


 Pierluigi Paganini
 April 30, 2020
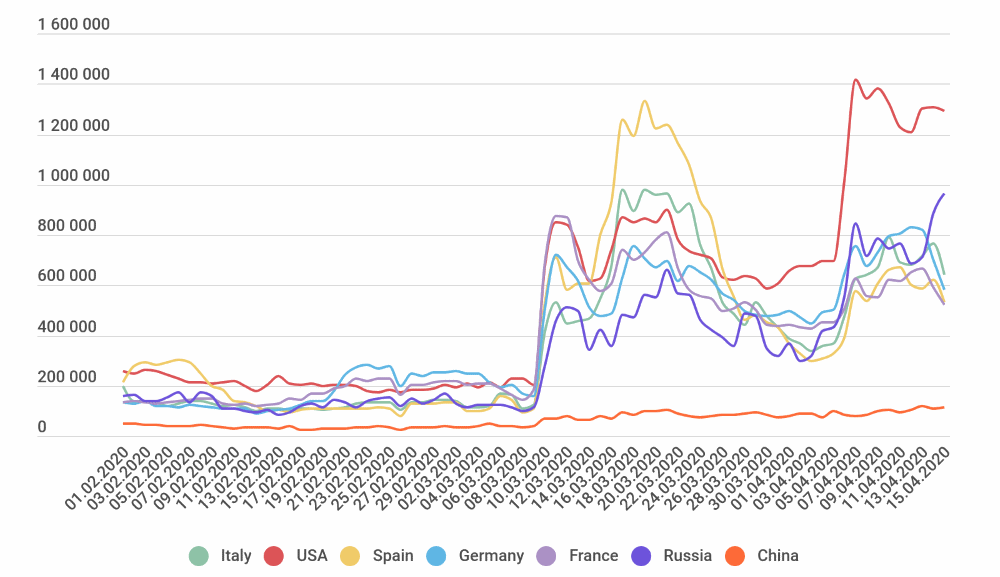
The number of RDP brute-force attacks is skyrocketing in mid-March due to remote working imposed during the COVID-19 pandemic. Researchers from Kaspersky Lab are observing a significant increase in the number of RDP brute-force attacks since the beginning of the COVID-19 pandemic. Earlier this month, researchers from Shodan reported a 41% increase in the number of RDP […]
 Pierluigi Paganini
April 29, 2020
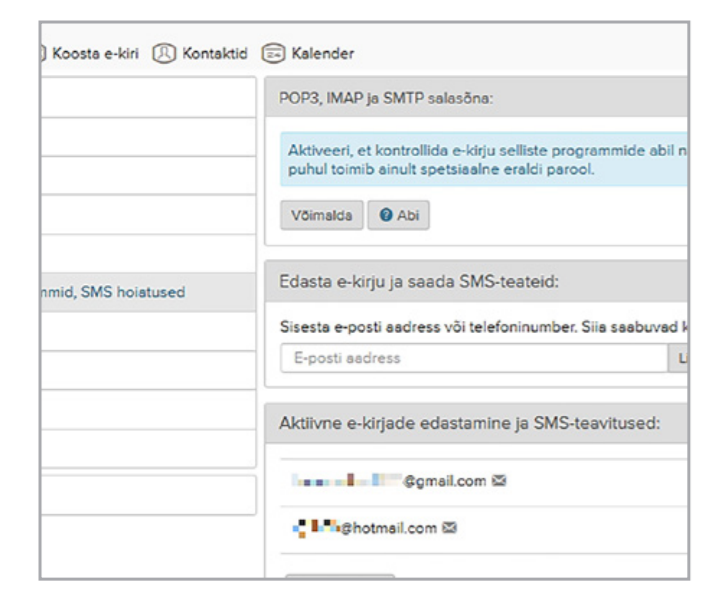
State-sponsored hackers have compromised a small number of accounts of the Estonian email provider Mail.ee belonging to high-profile people. Alleged state-sponsored hackers have hijacked a small number of accounts at the Estonian email provider Mail.ee, they exploited a zero-day vulnerability in the attack. According to the end-of-year report published this month by Estonian Internal Security […]
 Pierluigi Paganini
April 29, 2020
Google Project Zero white-hat hackers have disclosed zero-click vulnerabilities affecting multiple Apple operating systems. White-hat hackers at Google Project Zero team have discovered several zero-click vulnerabilities impacting multiple Apple’s multimedia processing components is several Apple operating systems. Multimedia processing components could be a privileges entry point for threat actos that attempt to hack into the […]
 Pierluigi Paganini
April 29, 2020
Adobe released security updates for Adobe Illustrator, Bridge, and Magento that fix several issues, including multiple remote code execution flaws. Adobe has released security updates that address multiple vulnerabilities in Adobe Illustrator, Bridge, and Magento, including some critical remote code execution flaws. The remote code execution flaws could be exploited by an attacker to execute commands […]
 Pierluigi Paganini
April 28, 2020
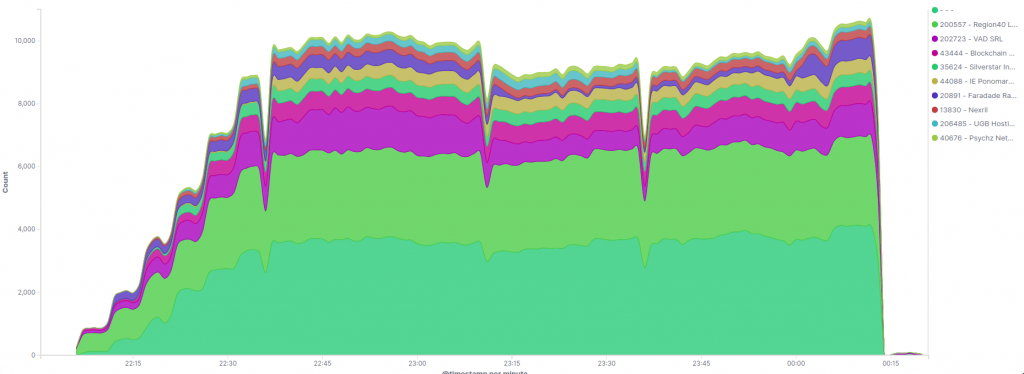
Timetv.live is the latest Azeri news site targeted by Denial of Service (DDoS) attacks launched by Sandman threat actor, the attack took place on March 21, 2020. Original Post by Qurium: *Qurium’s forensics report:* Sandman and Fineproxy behind the DDoSAttacks against TimeTV.Live https://www.qurium.org/alerts/azerbaijan/sandman-and-fineproxy-behind-the-ddos-attacks-against-timetv-live/ Timetv.live is the latest Azeri news site targeted by Denial of Service attacks. […]
 Pierluigi Paganini
April 28, 2020
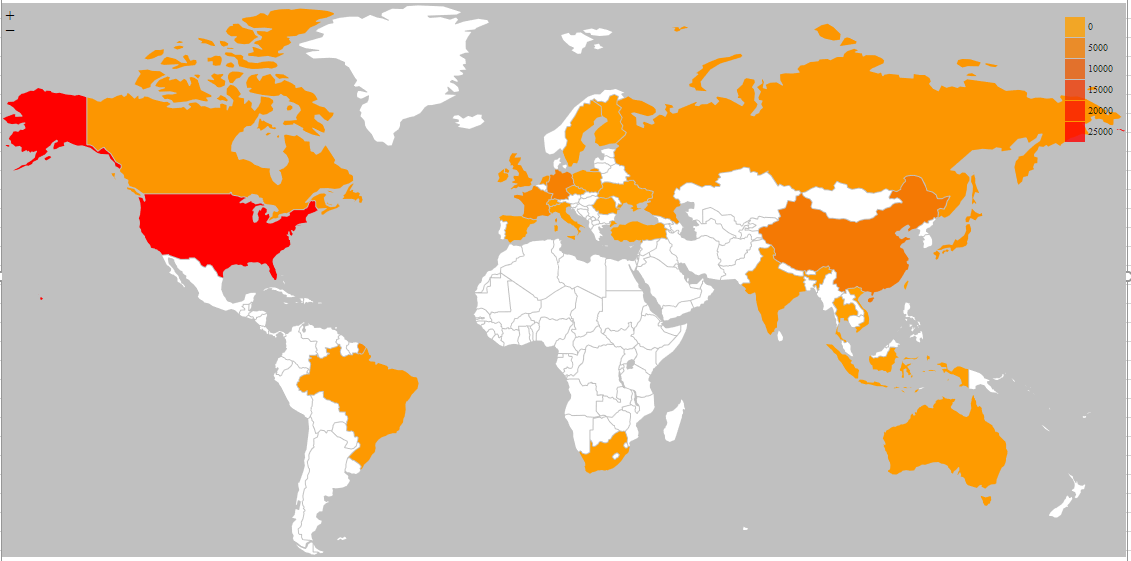
The Outlaw Hacking Group is back, malware researchers from Cybaze-Yoroi ZLab have uncovered a new botnet that is targeting European organizations Introduction During our daily monitoring activities, we intercepted a singular Linux malware trying to penetrate the network of some of our customers. The Linux malware is the well-known “Shellbot”, it is a crimetool belonging […]
 Pierluigi Paganini
April 28, 2020
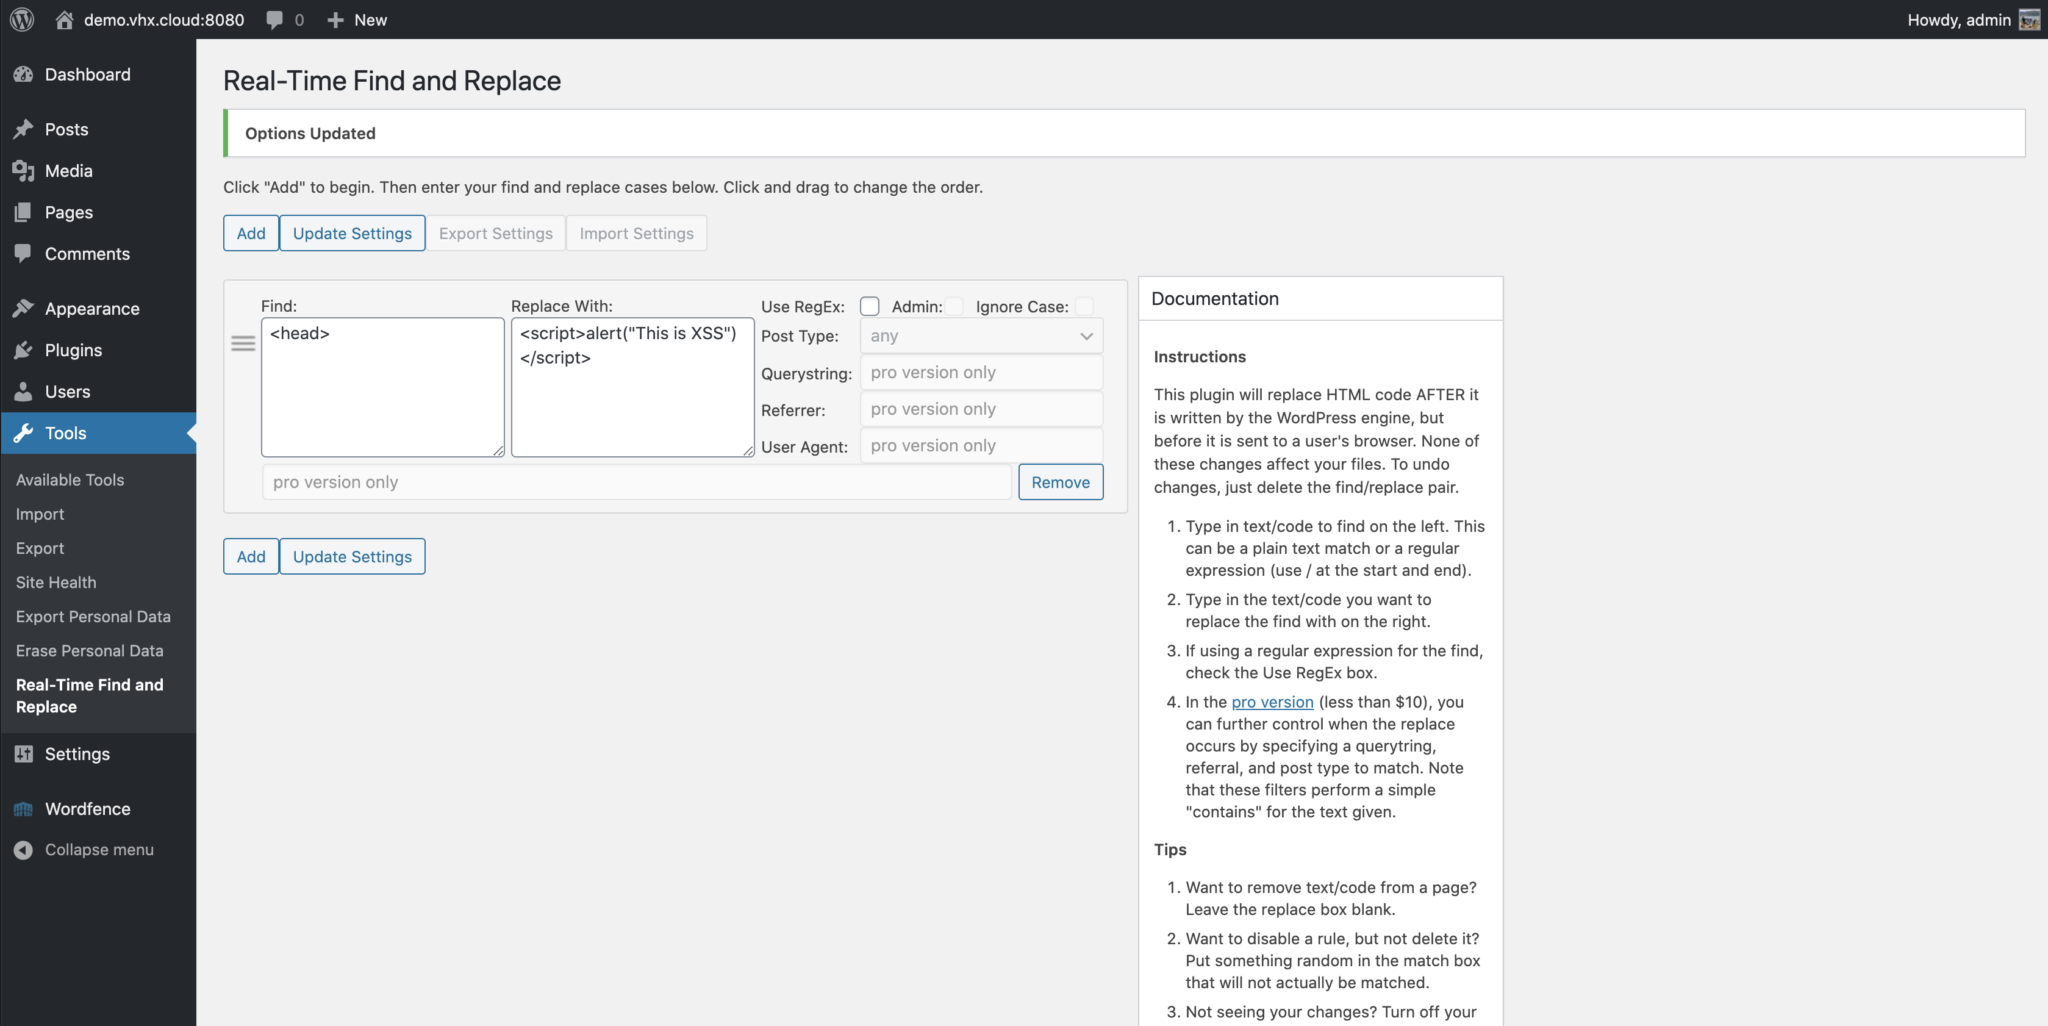
A bug in the Real-Time Find and Replace WordPress plugin could allow hackers to hackers to create rogue admin accounts on over 100,000 sites. A vulnerability in the Real-Time Find and Replace WordPress plugin could be exploited by attackers to create rogue admin accounts. The Real-Time Find and Replace WordPress plugin is currently installed on over 100,000 sites, it […]
 Pierluigi Paganini
April 27, 2020
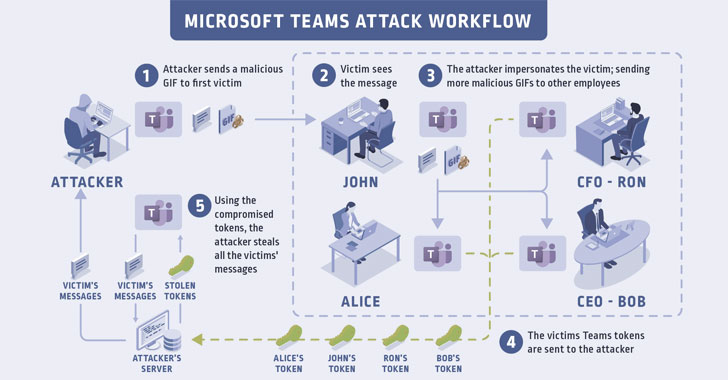
Experts discovered how to take over Microsoft Teams accounts by just sending recipients a regular GIF, it works for both desktop and web Teams versions. Microsoft has addressed a vulnerability in Teams workplace video chat and collaboration platform that could have allowed attackers to take Team accounts by sending participants a malicious link to an […]
 Pierluigi Paganini
April 27, 2020
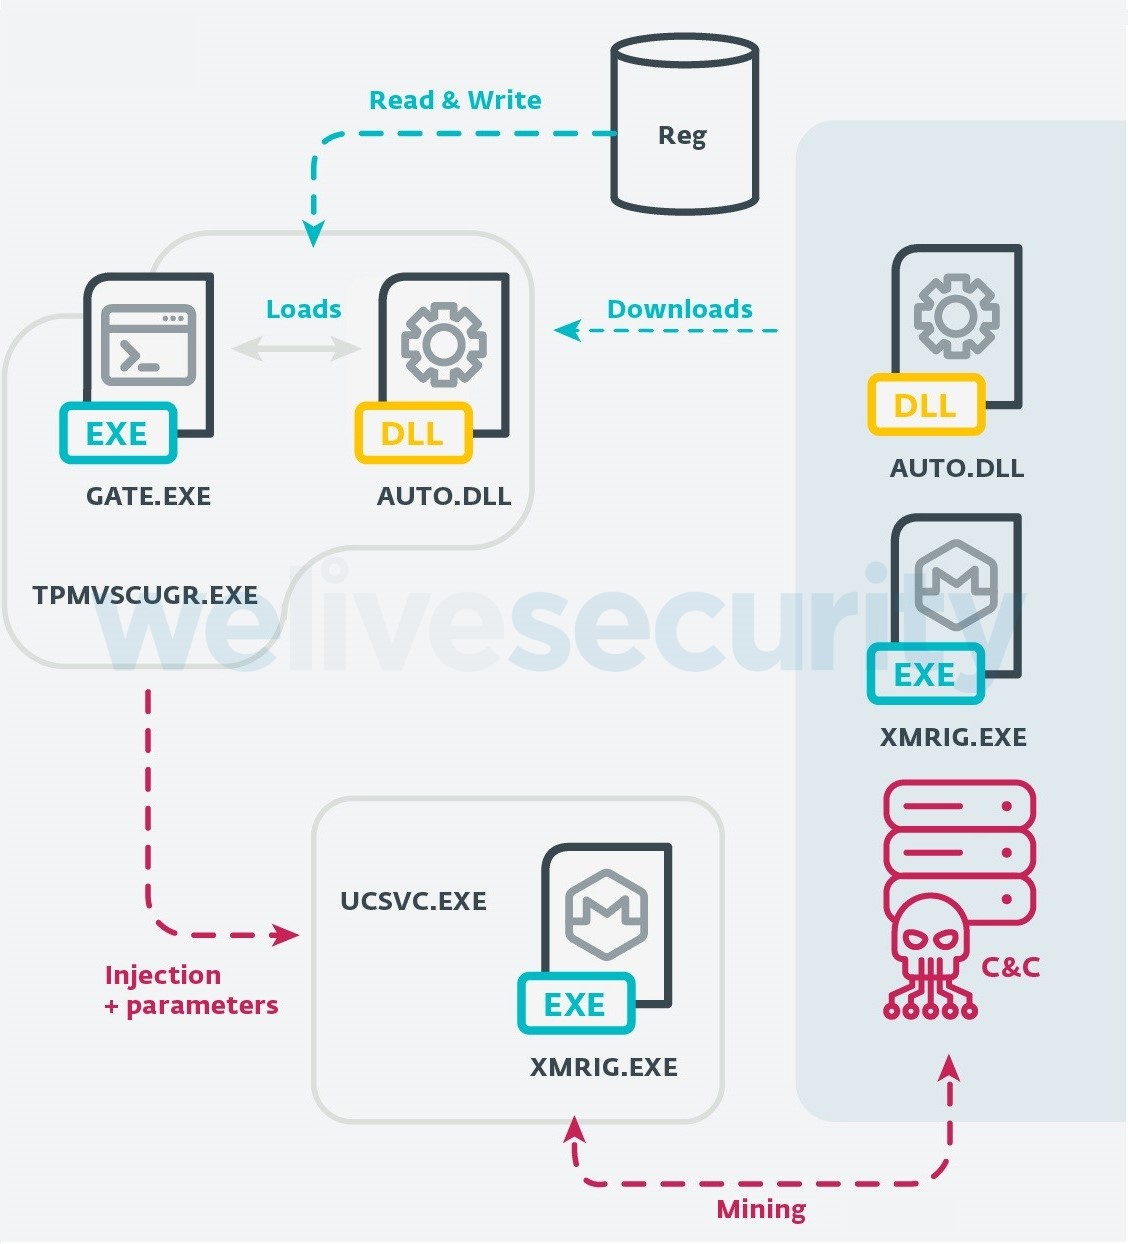
Experts managed to sinkhole several C2 servers of the VictoryGate botnet that already infected over 35,000 devices and propagates via infected USB devices. The VictoryGate botnet is active since at least May 2019, the botnet is more active in Latin America the most. More than 90% of the infected devices are located in Peru. Experts from […]
 Pierluigi Paganini
April 26, 2020
Cybersecurity firm Sophos releases an emergency patch to address an SQL injection flaw in its XG Firewall product that has been exploited in the wild. Cybersecurity firm Sophos has released an emergency patch to address an SQL injection zero-day vulnerability affecting its XG Firewall product that has been exploited in the wild. Sophos was informed […]



Security / September 15, 2026


