 Pierluigi Paganini
 December 20, 2019
Wawa convenience store chain disclosed a payment card breach that may have exposed debit and credit card data from thousands of customers. Wawa convenience store chain disclosed a payment card breach, its security team discovered a PoS malware on its payment processing systems. Wawa operates more than 860 convenience retail stores, this breach is potentially […]
 Pierluigi Paganini
December 19, 2019
The DoJ announced that the alleged member of the notorious hacker group The Dark Overlord has been extradited to the United States. The Department of Justice (DoJ) announced that the alleged member of The Dark Overlord hacking group has been extradited from the United Kingdom to the US. The man, Nathan Wyatt, 39, has been charged […]
 Pierluigi Paganini
December 19, 2019
Microsoft issues an out-of-band update to address SharePoint flaw, tracked as CVE-2019-1491, that could be exploited to obtain sensitive information. Microsoft issues an out-of-band update to fix an information disclosure vulnerability in SharePoint server, tracked as CVE-2019-1491, that could be exploited by an attacker to obtain sensitive information. “An information disclosure vulnerability exists in SharePoint […]
 Pierluigi Paganini
December 18, 2019
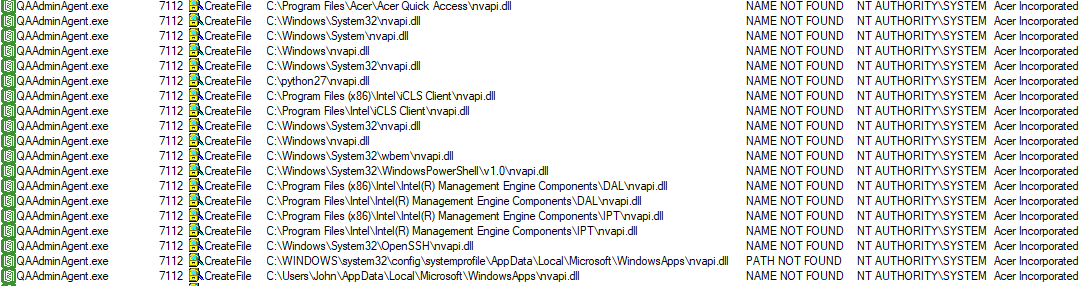
Experts found several flaws in Acer and ASUS software preinstalled on most of their PCs that could lead to privilege escalation and arbitrary code execution. SafeBreach experts discovered several vulnerabilities in Acer and ASUS software that comes pre-installed on most PCs from these vendors. The flaws could be exploited by attackers for privilege escalation and […]
 Pierluigi Paganini
December 18, 2019
Lab test provider LifeLabs has disclosed a data breach that exposed personal information for up to 15 million Canadians. Lab test provider LifeLabs announced that personal information for up to 15 million Canadians have been exposed after an unauthorized user gained access to their systems. LifeLabs notified its customers via letter, exposed data includes names, […]
 Pierluigi Paganini
December 18, 2019
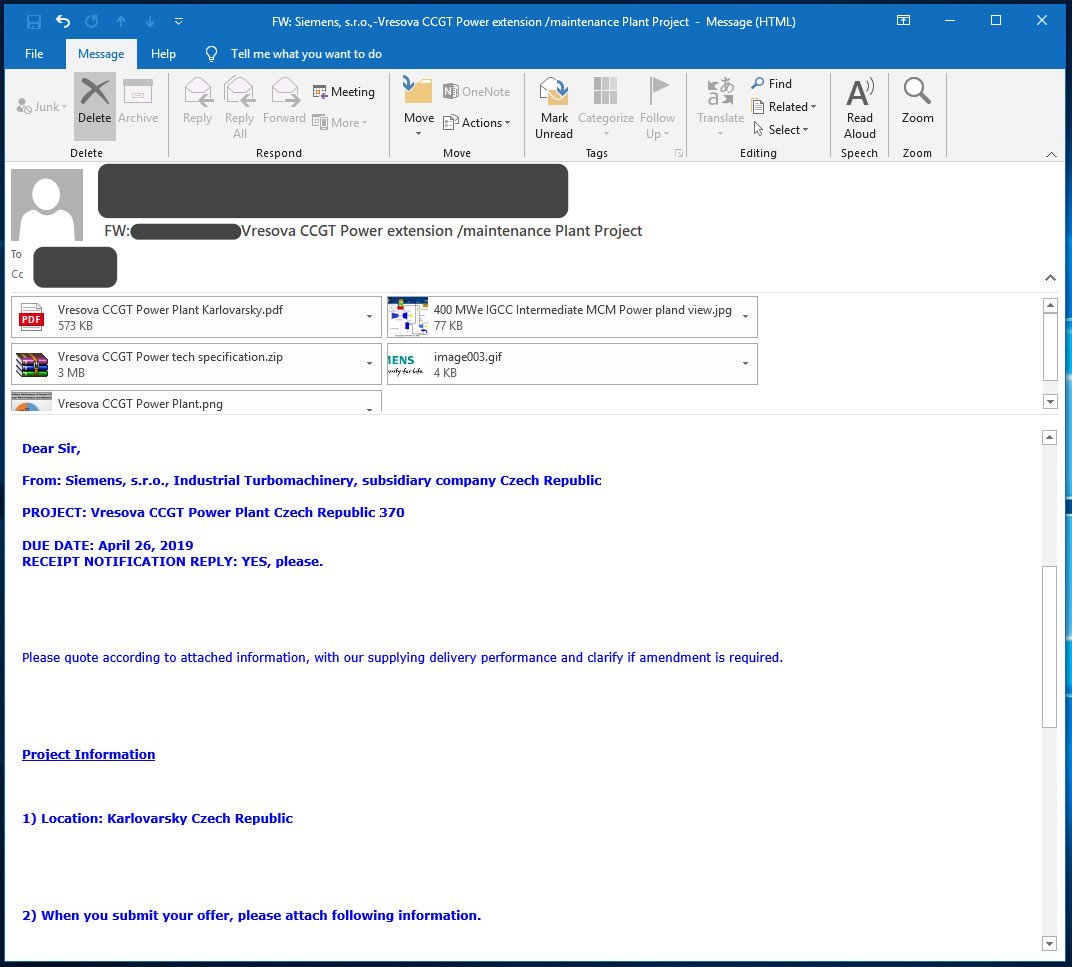
Experts discovered that at least 200 companies were the victims of a campaign, dubbed Gangnam Industrial Style, carried out by an advanced persistent threat (APT) group. Experts from the CyberX’s threat intelligence team Section 52 uncovered an ongoing cyberespionage campaign, tracked as Gangnam Industrial Style, that targeted industrial, engineering, and manufacturing organizations, most of them in South […]
 Pierluigi Paganini
December 17, 2019
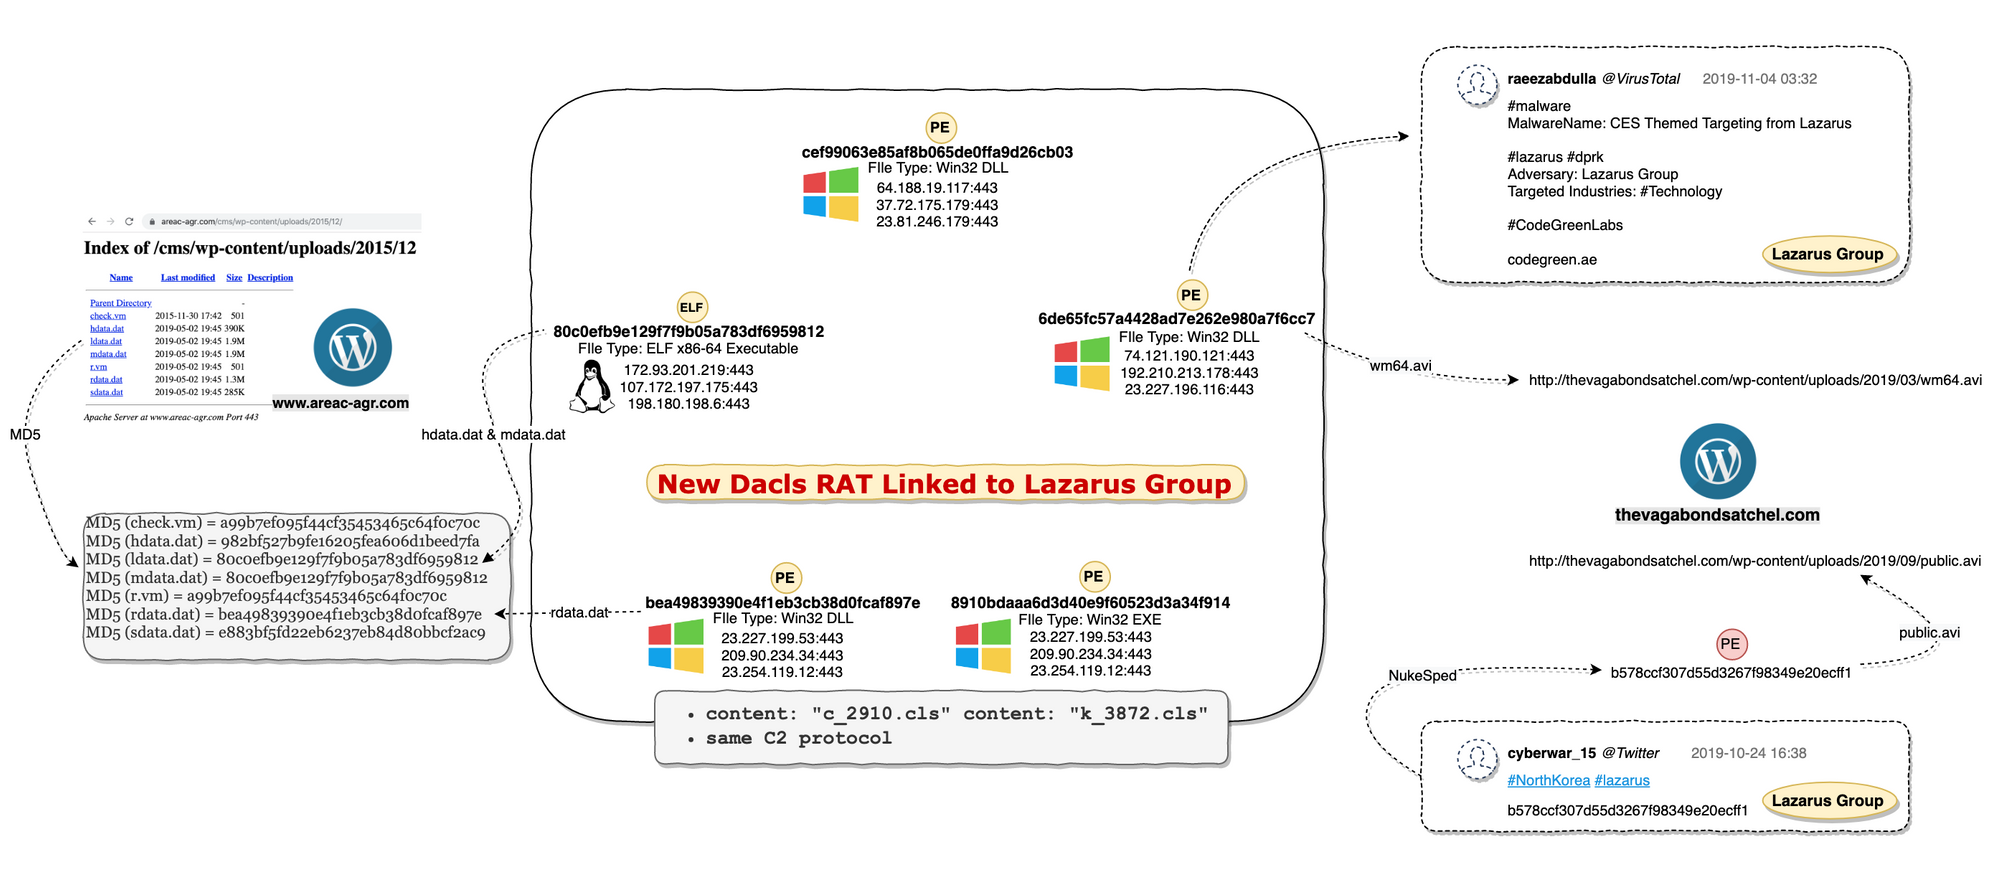
Researchers spotted a new Remote Access Trojan (RAT), dubbed Dacls, that was used by the Lazarus APT group to target both Windows and Linux devices. Experts at Qihoo 360 Netlab revealed that the North-Korea Lazarus APT group used a new Remote Access Trojan (RAT), dubbed Dacls, to target both Windows and Linux devices. The activity […]
 Pierluigi Paganini
December 17, 2019
TP-Link has addressed a critical vulnerability impacting some TP-Link Archer routers that could allow attackers to login without passwords. TP-Link addressed a critical zero-day vulnerability (CVE-2017-7405) in its TP-Link Archer routers that could be exploited by attackers to remotely take their control over LAN via a Telnet connection without authentication. “This is a zero-day flaw that was […]
 Pierluigi Paganini
December 17, 2019
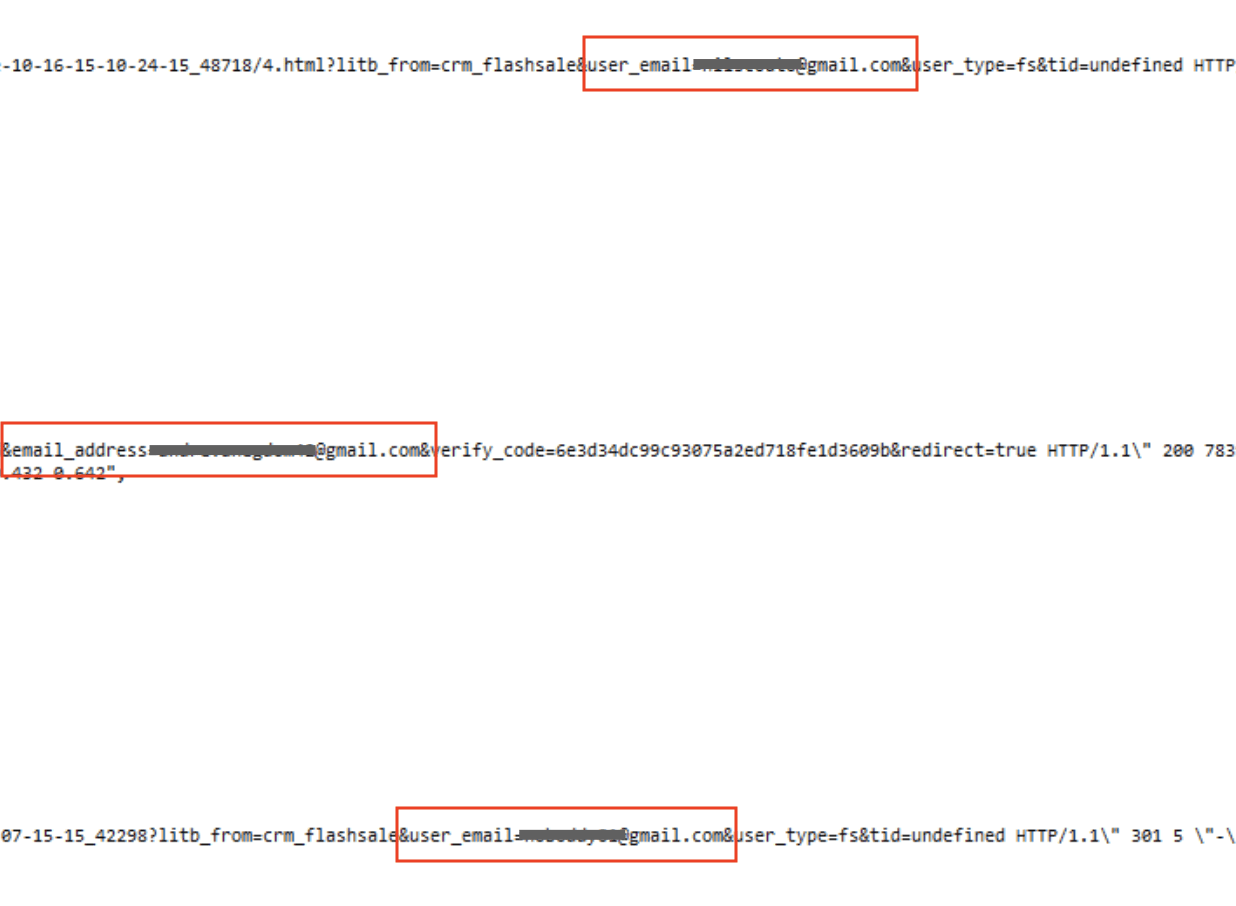
vpnMentor researchers discovered an unsecured server belonging to the Chinese e-store LightInTheBox.com containing 1.3TB of web server logs. Infosec researchers have uncovered an unsecured Elasticsearch database containing 1.3TB of web server log entries held by Chinese e-commerce website LightInTheBox.com. LightInTheBox is a Chinese online retailer trading on the New York Stock Exchange, most of its […]
 Pierluigi Paganini
December 17, 2019
Another year is ending and this is the right time to discover which are the worst passwords of 2019 by analyzing data leaked in various data breaches. Independent anonymous researchers, compiled and shared with security firm NordPass a list of 200 most popular passwords that were leaked in data breaches during 2019. The company collected […]