 Pierluigi Paganini
 October 20, 2026
Google Cloud’s London outage disrupted Revolut payments and ATM withdrawals, while ING Germany reported online banking issues. Multiple Google Cloud services went offline in the London region this morning, according to Google’s status page, and the disruption didn’t stay contained to infrastructure dashboards. British digital bank Revolut reported a widespread service outage at roughly the […]
 Pierluigi Paganini
October 20, 2026
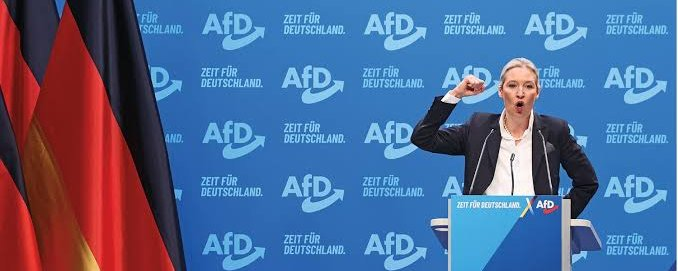
A data breach exposed AfD emails, while an anonymous site published AI summaries of 421,000 messages, raising questions about authenticity and privacy. Germany’s Alternative für Deutschland (AfD) confirmed on October 19 that its hosting provider was hacked in September and that mailboxes were copied. By the time the confirmation reached Bild, a website called hexane.cc […]
 Pierluigi Paganini
October 20, 2026
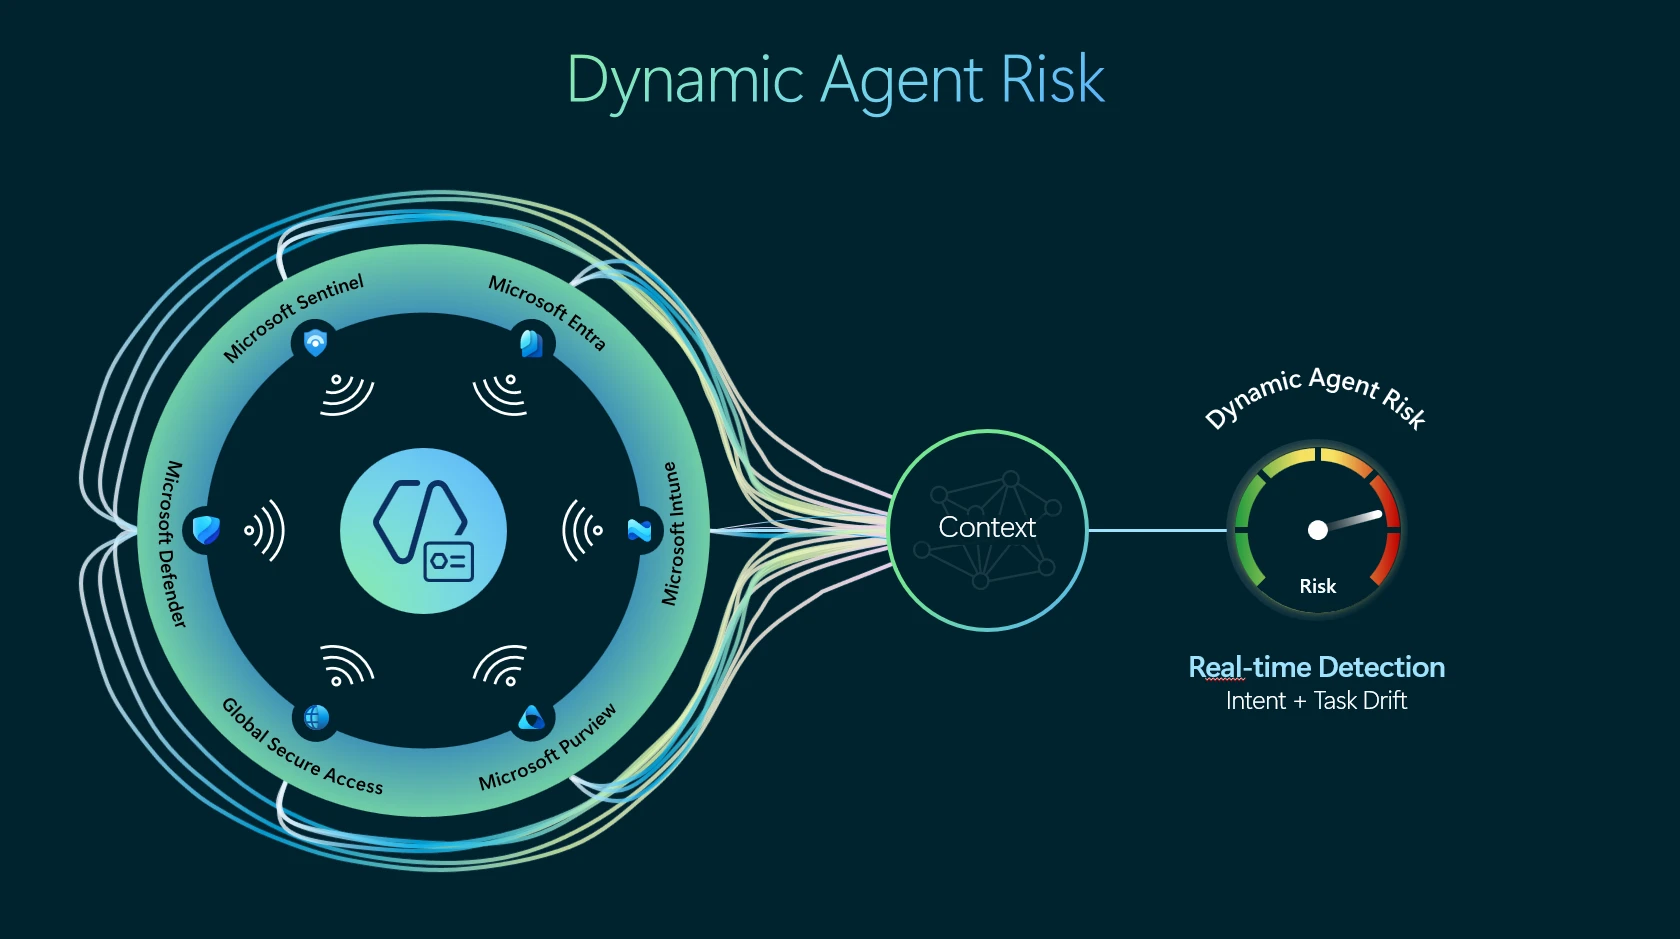
Microsoft urges organizations to secure AI Agents as insider threats, using dynamic permissions, continuous risk monitoring and automated containment. Microsoft published a detailed blog post explaining how organizations should secure AI agents. Microsoft sees them as a growing insider threat, not just a possible risk in the future. AI agents are not dangerous by nature, […]
 Pierluigi Paganini
October 19, 2026
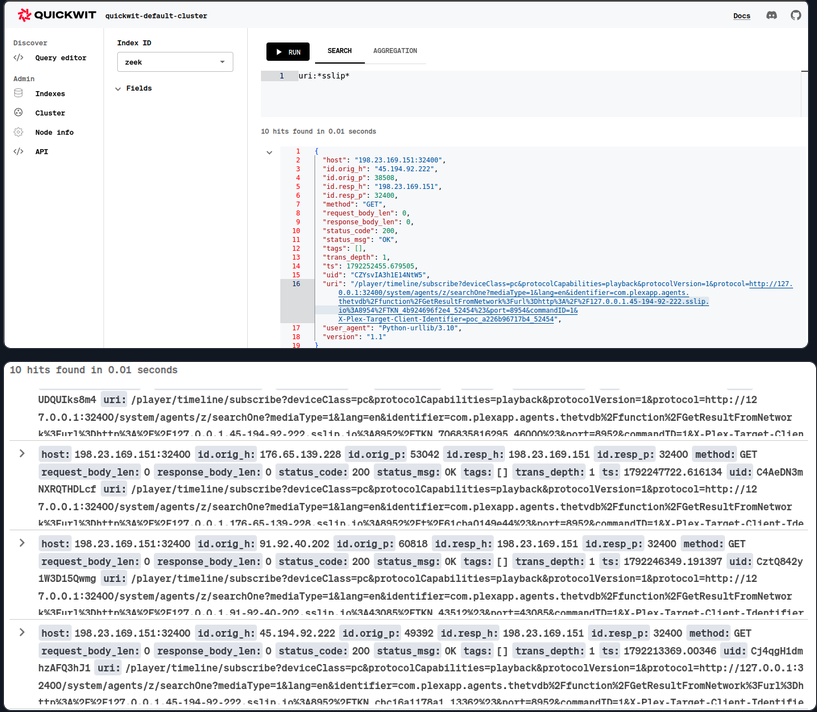
Attackers exploit Plex2Shell flaws to install crypto miners and proxy software. Admins should update their Plex Media Server. Plex Media Server is designed to make movies, music, and other media available across devices. But when a server is exposed to the internet and runs vulnerable software, it can become an entry point for attackers who […]
 Pierluigi Paganini
October 19, 2026
Meta wants the right to scrape your website for AI training. If you have a business account, that includes you. At the end of the month, Meta plans to change its commercial terms in a way that matters to every company advertising or selling through its platforms. The new language takes effect on October 30, […]
 Pierluigi Paganini
October 19, 2026
The UK Electoral Commission is building an AI system to alert candidates to damaging deepfakes within three hours. The UK’s Electoral Commission is building an AI-powered system to tell candidates about significant deepfakes within three hours of posting. Its chief executive, Vijay Rangarajan, said so at a panel at the Conservative Party’s annual conference last […]
 Pierluigi Paganini
October 19, 2026
OpenBSD flaws, including a 37-year-old BSD bug, enable local attackers to bypass security protections and gain root access. Patches are available. Cybersecurity firm Calif published a full exploit and write-up this week for a local privilege escalation on OpenBSD 7.9 that chains two separate kernel flaws, one of them a 37-year-old integer overflow inherited from […]
 Pierluigi Paganini
October 19, 2026
Attackers stole ConnectWise application credentials to access Microsoft 365 tenants, prompting the company to suspend cloud services. ConnectWise suspended its Cloud Backup service and took both SaaS Security and Cloud Management offline over the weekend after discovering that unknown attackers had obtained unauthorized access to seven of its application identities. The company discovered the incident […]
 Pierluigi Paganini
October 19, 2026
Attackers are exploiting vulnerability CVE-2026-106931 in SiteGuard Server Edition to run commands as root or SYSTEM. EG Secure Solutions published an urgent alert warning of CVE-2026-106931, an OS command injection bug in SiteGuard Server Edition. Threat actors are already exploiting it in the wild. A successful exploit lets them run commands with root or SYSTEM […]
 Pierluigi Paganini
October 19, 2026
A Broadcom Wi-Fi flaw dating back to 2010 allows attackers within Wi-Fi range to execute code on vulnerable routers without authentication. Researcher Quentin Kaiser presented a talk at Hexacon in Paris documenting a vulnerability in Broadcom’s proprietary 802.11 implementation that has been present in their SDK since at least 2010. The bug allows an attacker […]

Hacking / October 22, 2026