 Pierluigi Paganini
 October 10, 2019
Maintainers at the Tor Project have removed from its network more than 800 relay servers running outdated and EOL versions of the Tor software. Currently, the Tor network is composed of more than 6000 relays, some of them running outdated Tor software versions (in some cases back to the 0.2.4.x versions). Other relays are running […]
 Pierluigi Paganini
October 10, 2019
Security experts discovered a critical remote code execution vulnerability, tracked as CVE-2019-9535, in the GPL-licensed iTerm2 macOS terminal emulator app. Security experts at cybersecurity firm Radically Open Security (ROS) discovered a 7-year old critical remote code execution vulnerability in the GPL-licensed iTerm2 macOS terminal emulator app. The iTerm2 macOS terminal emulator app is one of the most […]
 Pierluigi Paganini
October 09, 2019
NSA is warning of multiple state-sponsored cyberespionage groups exploiting enterprise VPN Flaws Last week, the UK’s National Cyber Security Centre (NCSC) reported that advanced persistent threat (APT) groups have been exploiting recently disclosed VPN vulnerabilities in enterprise VPN products in attacks in the wild. Threat actors leverage VPN vulnerabilities in Fortinet, Palo Alto Networks and Pulse Secure, to […]
 Pierluigi Paganini
October 09, 2019
vBulletin has recently published a new security patch update that addresses three high-severity vulnerabilities in the popular forum software. vBulletin has recently published a new security patch update that addresses three high-severity flaws in vBulletin 5.5.4 and prior versions. The vulnerabilities could be exploited by remote attackers to take complete control over targeted web servers […]
 Pierluigi Paganini
October 09, 2019
Twitter admitted having “inadvertently” used phone numbers and email addresses, collected for security purposes, for advertising. Twitter apologized to have used phone numbers and email addresses, privided by the users for security purposes, for advertising. According to the social media company, data used for account authentication were also matched with advertisers’ database to improve the […]
 Pierluigi Paganini
October 09, 2019
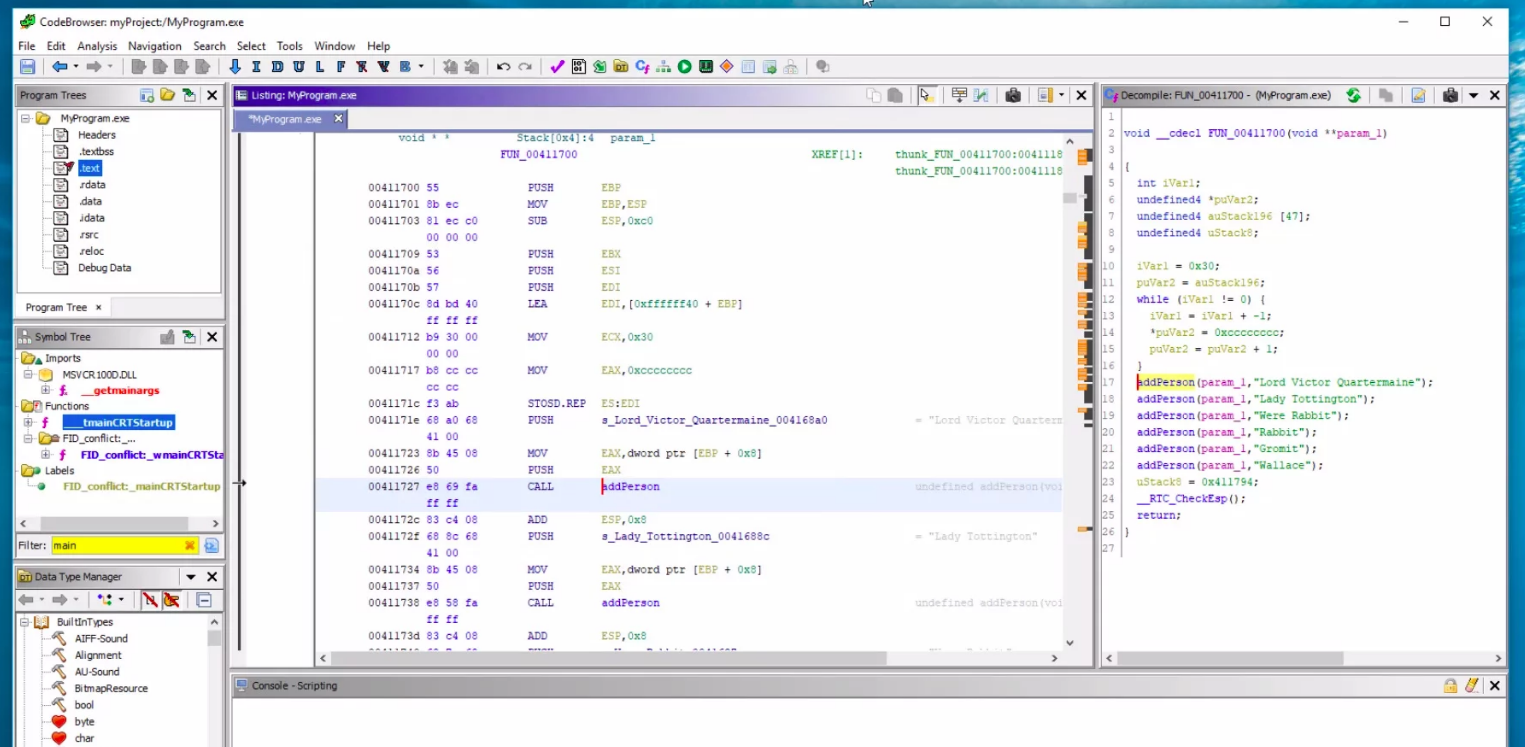
Security researchers discovered a code-execution vulnerability that affects versions through 9.0.4 of the Ghidra software reverse engineering (SRE) framework. GHIDRA is a multi-platform reverse engineering framework that runs on major OSs (Windows, macOS, and Linux). The framework was first mentioned in the CIA Vault 7 dump that was leaked in 2017. WikiLeaks obtained thousands of files allegedly originating from […]
 Pierluigi Paganini
October 08, 2019
One of the victims of the Muhstik ransomware gang who initially paid the ransomware, decided to hack back the crooks and released their decryption keys. Tobias Frömel, is a German software developer, who was a victim of the Muhstik ransomware. Frömel initially paid the ransom to decrypt his files, but later decided to get his […]
 Pierluigi Paganini
October 08, 2019
Patches for Internet Explorer Zero-Day Causing Problems for Many Users Microsoft released a new set of patches for a zero-day flaw in Internet Explorer recently fixed due to problems reported by users with the previous patch. On September 23, Microsoft released an out-of-band patch to address a zero-day memory corruption flaw in Internet Explorer (CVE-2019-1367) that […]
 Pierluigi Paganini
October 07, 2019
The United States and Baltic announced cooperation to protect the Baltic energy grid from cyber attacks as they disconnect from the Russian electricity grid. The US and Baltic agreed to cooperate to protect the Baltic energy grid from cyber attacks as they disconnect from the Russian electricity grid. US Energy Secretary Rick Perry and counterparts […]
 Pierluigi Paganini
October 07, 2019
The popular data breach notification service Have I Been Pwned? (HIBP) has added the stolen data from the StreetEasy and Sephora data incidents. Have I Been Pwned? (HIBP), the popular service that allows users to check whether their personal data has been compromised by data breaches has added the stolen data from the StreetEasy and Sephora data […]