


 Pierluigi Paganini
 November 10, 2026
A public iOS sandbox escape could expose wallet keys, Binance warns. No attacks are reported and no fix is confirmed. On 10 November, Binance warned users about a public iOS sandbox escape that lets one app read the files of other apps. Seed phrases, private keys and login credentials could be exposed to a malicious […]
 Pierluigi Paganini
November 05, 2026
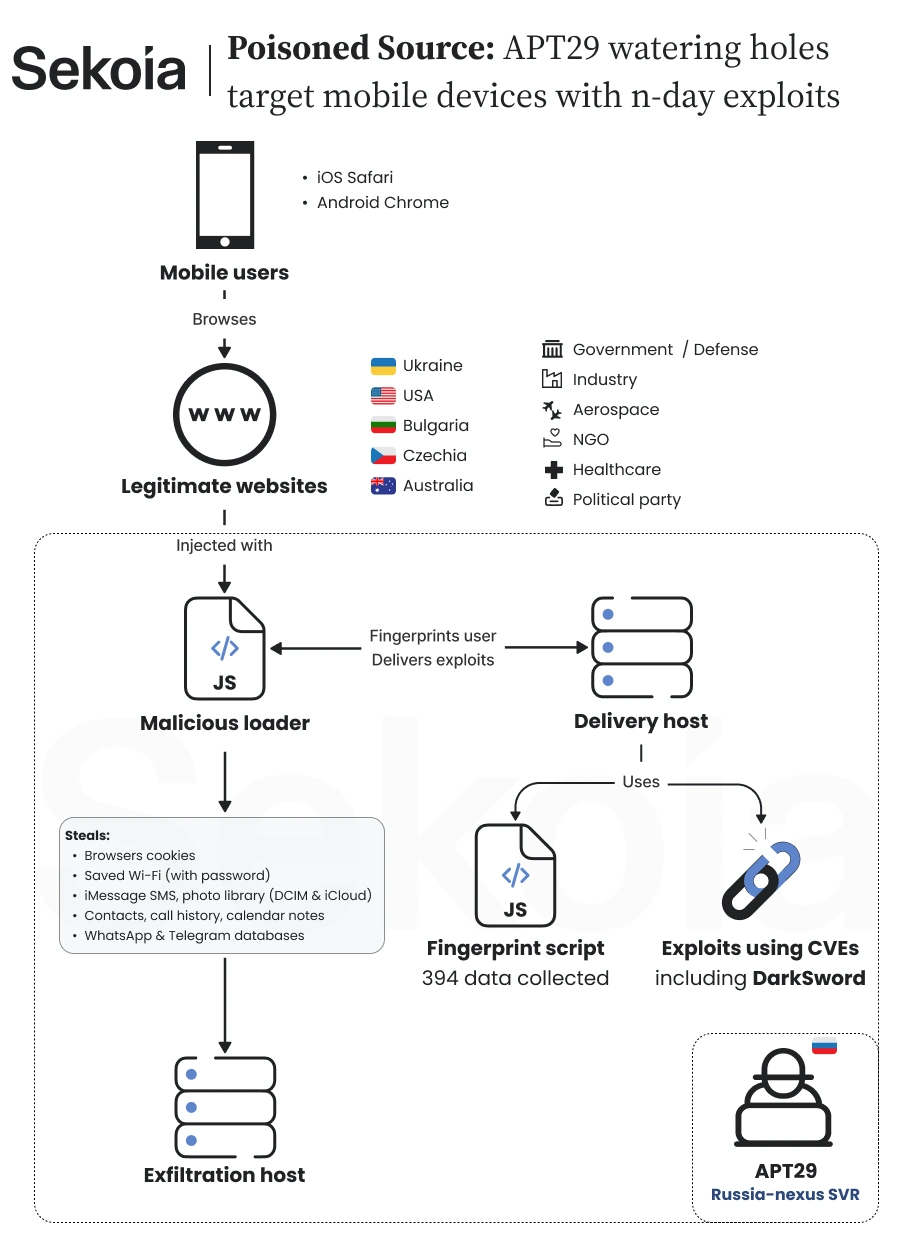
Russia-linked group APT29 targeted iOS and Android users through hijacked websites and a compromised analytics service. Sekoia says a large-scale watering hole campaign is going after iOS and Android users, and it links the campaign to APT29 (aka SVR group, Cozy Bear, Nobelium, BlueBravo, Midnight Blizzard, and The Dukes), the Russian group tied to the SVR foreign intelligence service. A watering hole […]
Pierluigi Paganini
March 26, 2026
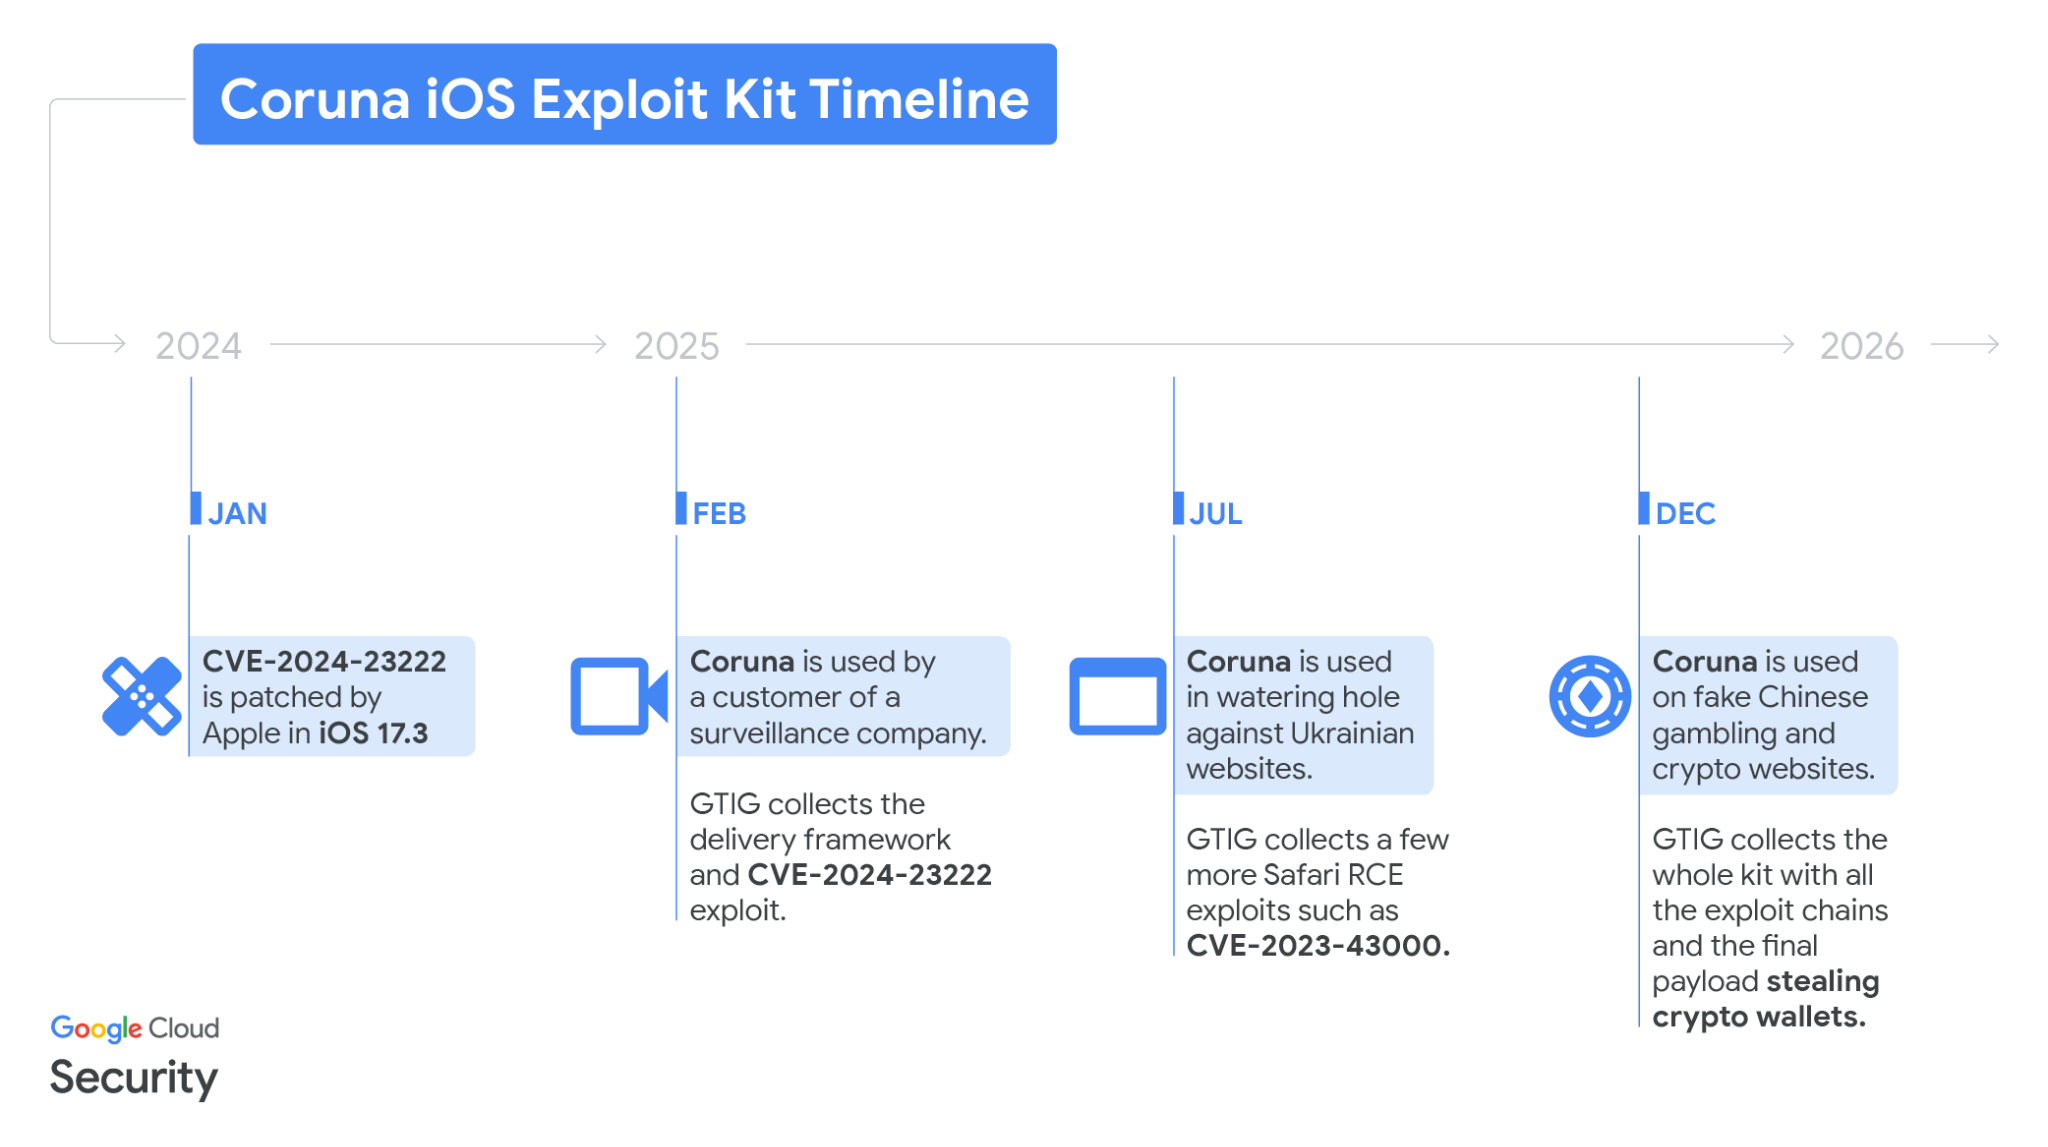
Kaspersky found Coruna iOS exploits reuse updated code from the 2023 Operation Triangulation attacks, suggesting a possible link. Kaspersky researchers discovered that the Coruna iOS exploit kit uses an updated version of the same kernel exploit seen in the 2023 Operation Triangulation campaign. While early evidence didn’t clearly link the two, the code similarities now […]
 Pierluigi Paganini
March 20, 2026
Apple warns that outdated iPhones are vulnerable to Coruna and DarkSword exploit kits and urges users to update iOS. Apple has warned that iPhones running outdated iOS versions are at risk from exploit kits like Coruna and DarkSword. These attacks use malicious web content to trigger infection chains that can steal sensitive data. Users are […]
 Pierluigi Paganini
March 19, 2026
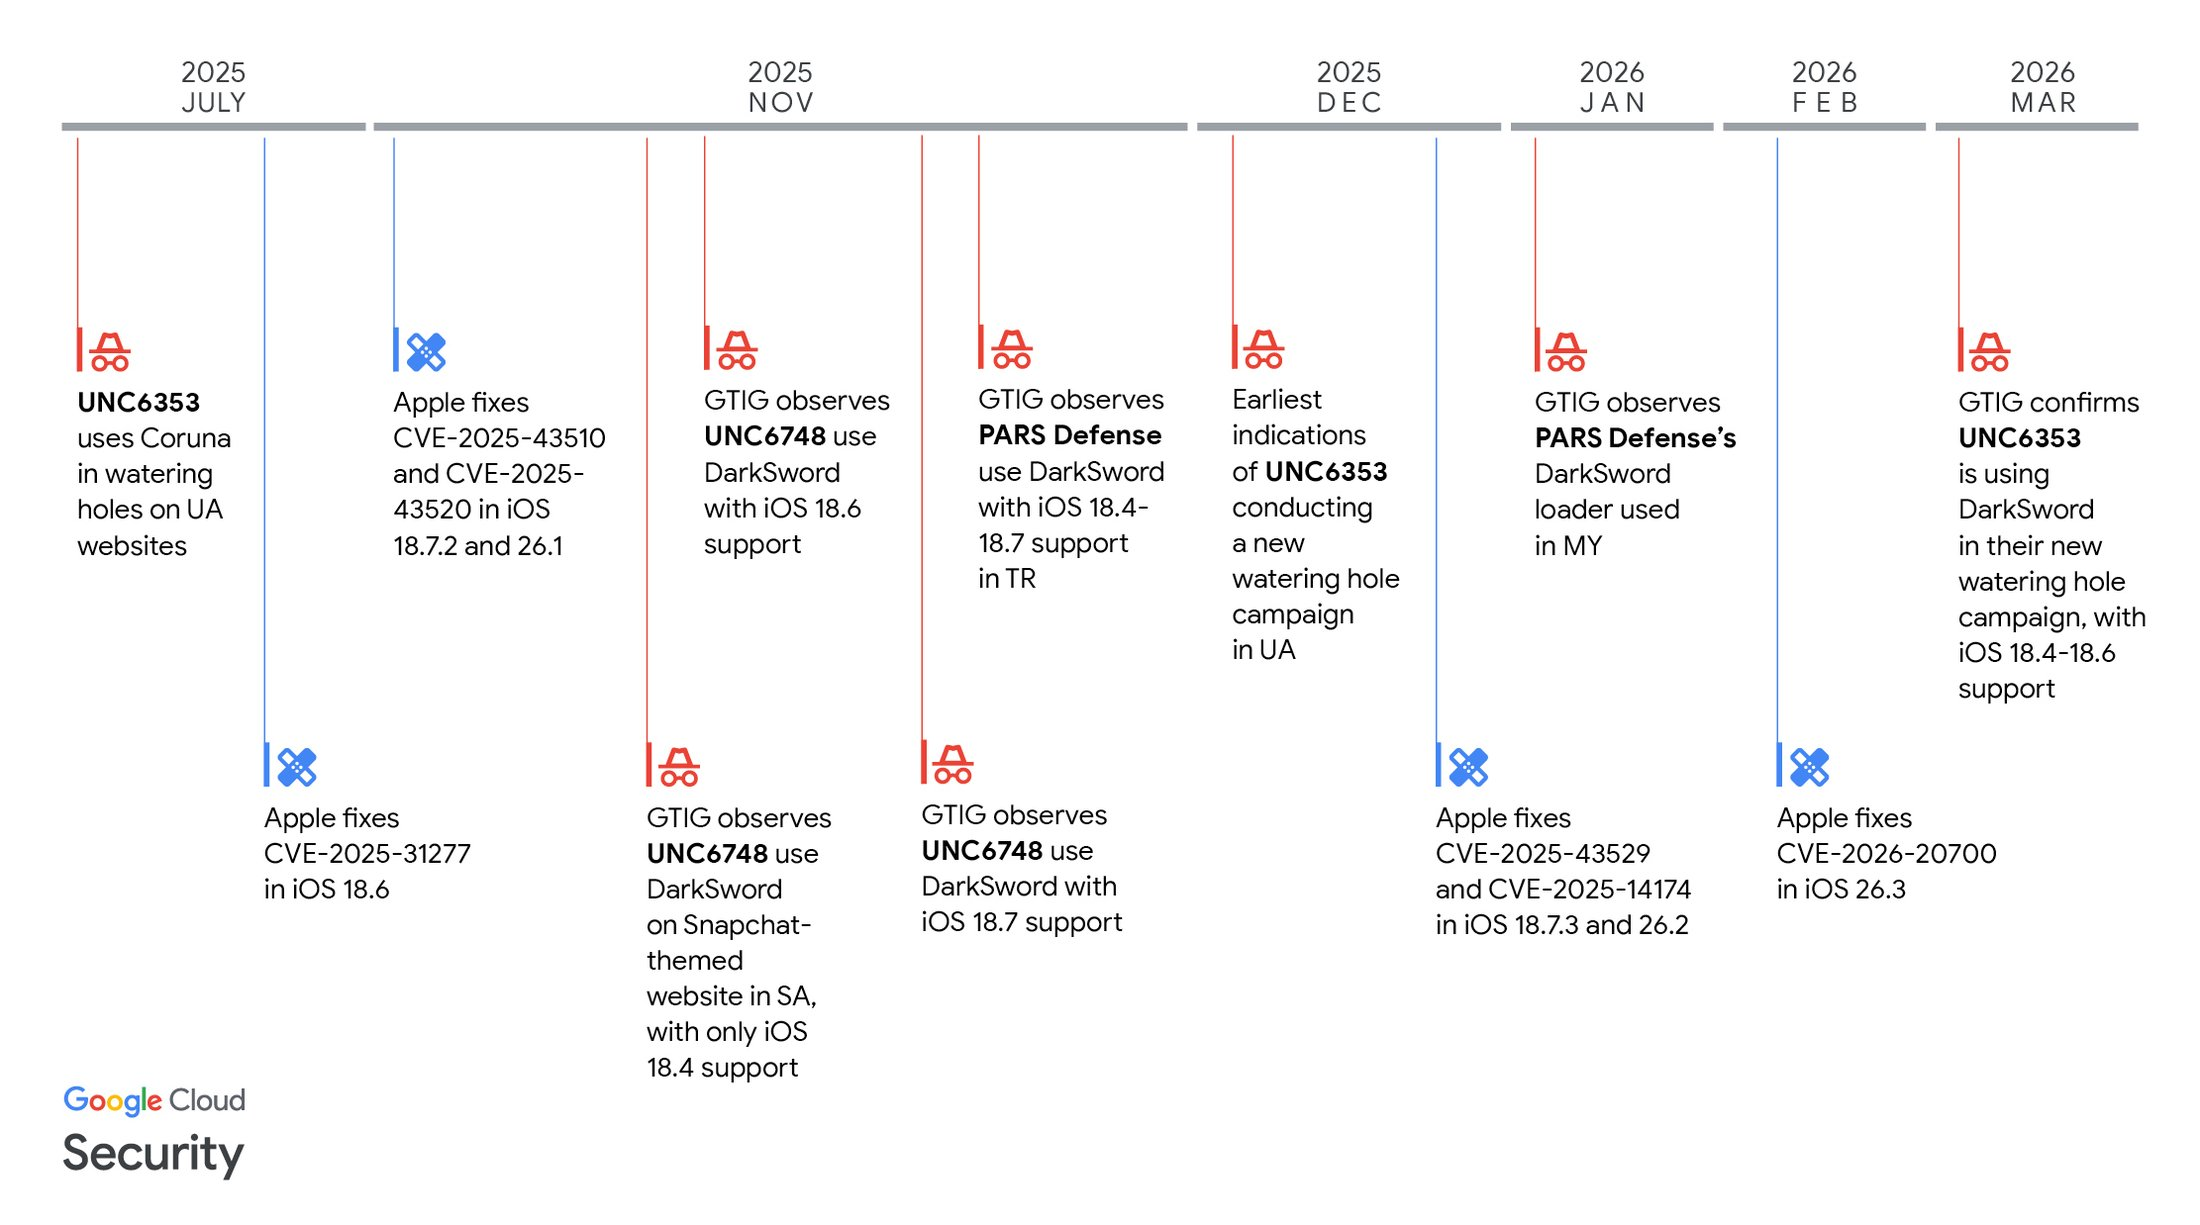
DarkSword, a new iOS exploit kit, is used by multiple actors to steal data in campaigns targeting Saudi Arabia, Turkey, Malaysia, and Ukraine. Lookout Threat Labs discovered a new iOS exploit kit called DarkSword that has been used since late 2025 by multiple threat actors, including surveillance vendors and likely nation-state actors. The toolkit enables […]
 Pierluigi Paganini
February 10, 2026
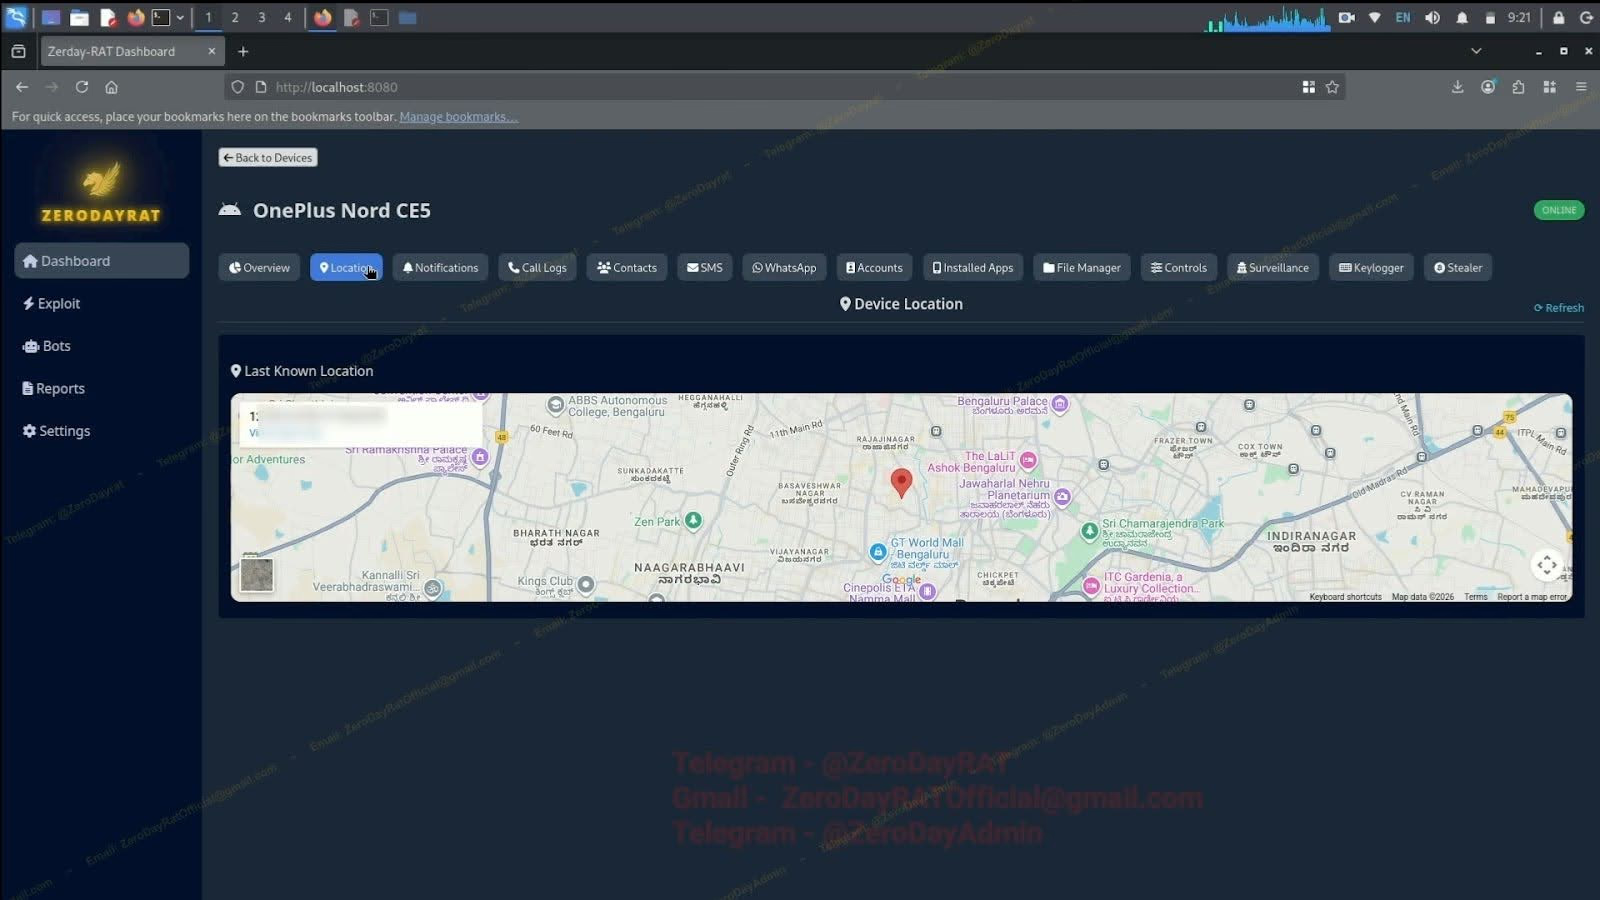
ZeroDayRAT is a commercial mobile spyware that grants full remote access to Android and iOS devices for spying and data theft. ZeroDayRAT is a newly discovered commercial mobile spyware toolkit that gives attackers full control over Android and iOS devices. It supports live camera access, keylogging, and theft of banking and crypto data. First spotted […]
Pierluigi Paganini
May 13, 2025
Apple released security updates to address easily exploitable vulnerabilities impacting iOS and macOS devices. Apple released urgent iOS and macOS security updates to patch critical flaws that could allow attackers to execute malicious code just by opening a crafted image, video, or website: Apple’s iOS 18.5 update addressed multiple critical flaws in AppleJPEG, CoreMedia, and […]
Pierluigi Paganini
April 17, 2025
Apple released emergency updates to fix iOS, iPadOS & macOS vulnerabilities actively exploited in sophisticated attacks. Apple released out‑of‑band security updates to address two vulnerabilities, tracked as CVE-2025-31200 and CVE-2025-31201, impacting iOS, iPadOS & macOS. The company confirmed that the flaws have been exploited in a small number of “extremely sophisticated” attacks against iOS targets. […]
Pierluigi Paganini
February 10, 2025
Apple released iOS and iPadOS updates to address a zero-day likely exploited in extremely sophisticated attacks targeting specific individuals. Apple released emergency security updates to address a zero-day vulnerability, tracked as CVE-2025-24200, that the company believes was exploited in “extremely sophisticated” targeted attacks. An attacker could have exploited the vulnerability to disable the USB Restricted […]
 Pierluigi Paganini
November 01, 2024
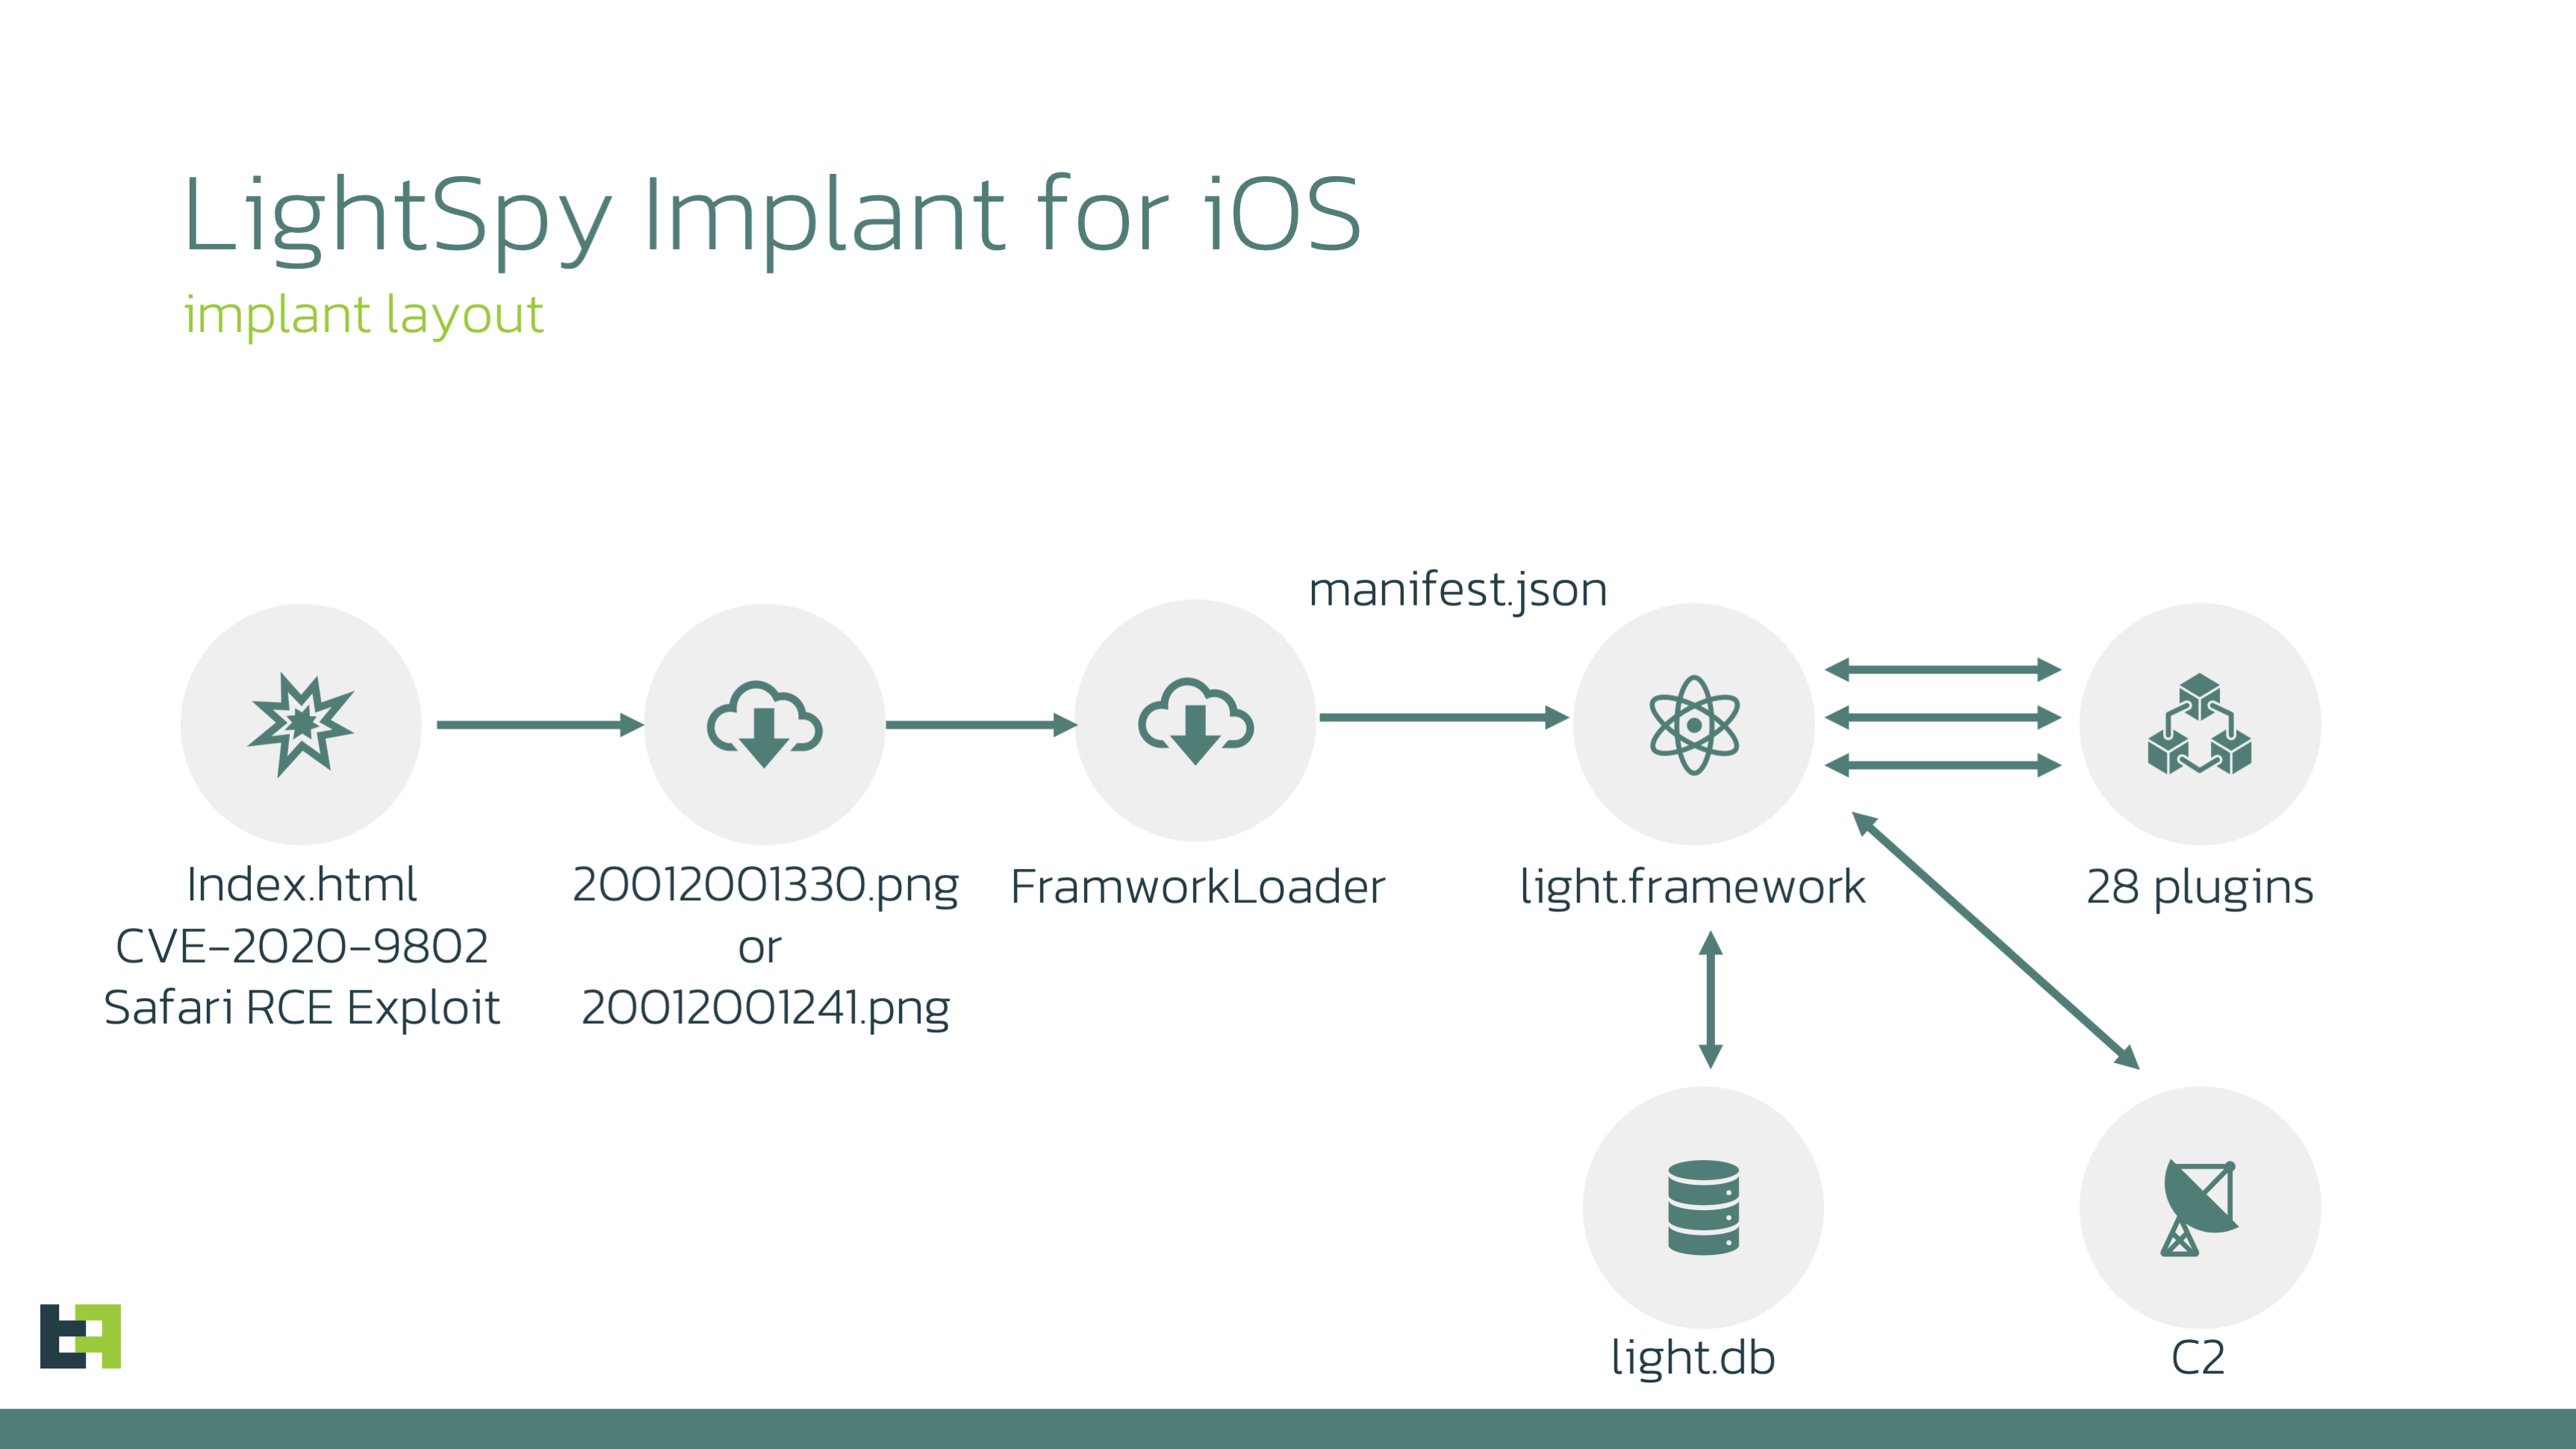
New LightSpy spyware targets iPhones supporting destructive features that can block compromised devices from booting up. In May 2024, ThreatFabric researchers discovered a macOS version of LightSpy spyware that has been active in the wild since at least January 2024. ThreatFabric observed threat actors using two publicly available exploits (CVE-2018-4233, CVE-2018-4404) to deliver macOS implants. The […]
Data Breach / November 17, 2026
Malware / November 17, 2026


