


 Pierluigi Paganini
 September 08, 2026
Researchers built a WeChat worm that spreads through incoming calls without user action. Tencent has blocked the exploit. Researchers at Calif created a WeChat worm that can take over an account through an incoming call, even if the victim never answers or touches the phone. The attack works only when the caller already appears in […]
 Pierluigi Paganini
September 08, 2026
An exposed Vietnam-linked APIS database contained 220.8 million passenger and crew records, including passport and flight data. Researchers found an exposed Advance Passenger Information System (APIS) database containing 220.8 million passenger and crew records from January 2017 to April 2026. The data includes sensitive details such as passport numbers, identities and flight information, potentially affecting […]
 Pierluigi Paganini
September 08, 2026
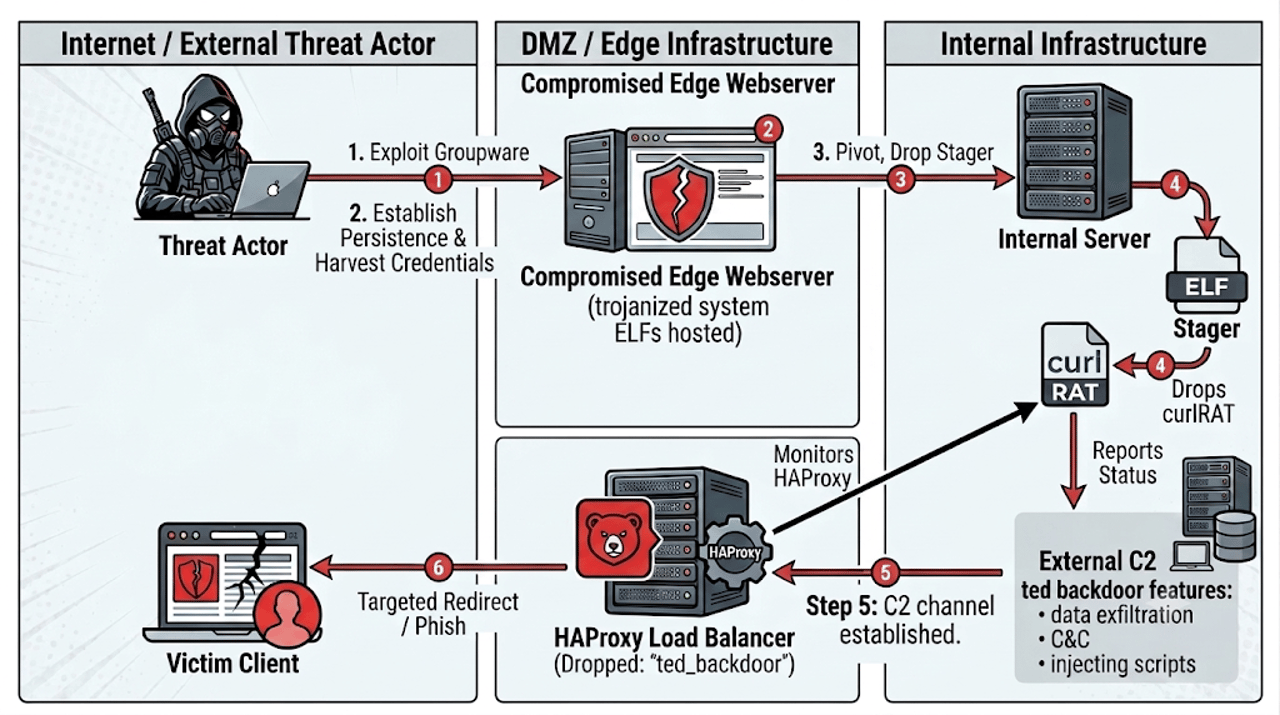
North Korea-linked hackers hid a backdoor inside HAProxy, masking C2 traffic and stealing data while keeping the load balancer working normally. North Korean-linked hackers found a genuinely clever hiding spot for their malware: inside the actual source code of HAProxy, the load balancing software running at the edge of two South Korean companies’ networks. Rapid7’s […]
 Pierluigi Paganini
September 08, 2026
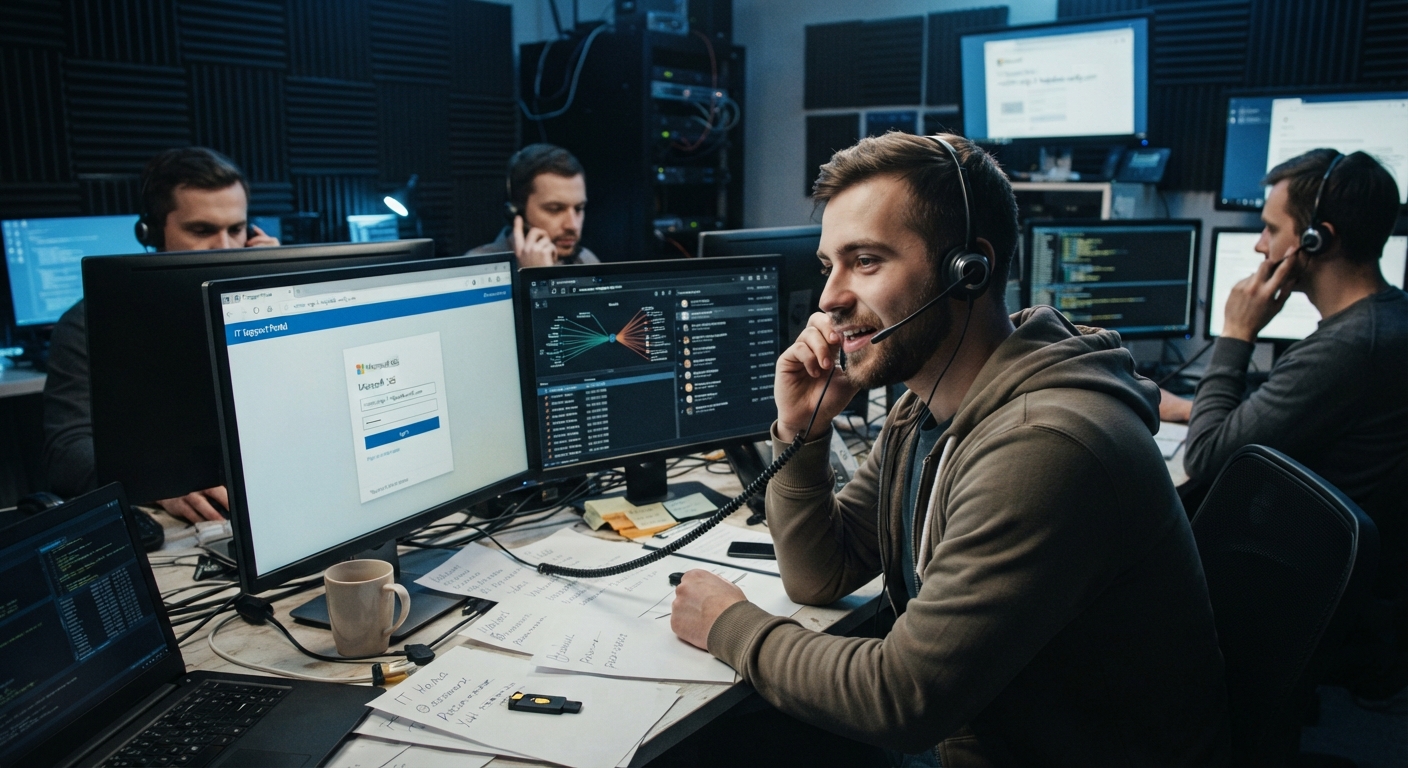
Attackers bypass endpoint security by posing as IT staff, stealing Microsoft 365 sessions, draining SaaS data and demanding extortion. Forget installing malware because today’s extortionists just pick up the phone instead of writing code. A widespread threat cluster tracked as PREY-0058 bypasses endpoint security entirely by targeting Microsoft 365 and SaaS environments through pure social […]
 Pierluigi Paganini
September 07, 2026
Condé Nast user data from 32.8 million accounts is reportedly for sale, raising risks of targeted phishing, fraud and scams. A database said to contain 32.8 million Condé Nast user records is being offered for $15,000 on a Russian-language cybercrime forum. Ransomnews reviewed a 5,000-record sample and concluded that it is consistent with genuine Condé […]
 Pierluigi Paganini
September 07, 2026
StyleSmuggler Magento zero-day is under active attack, letting unauthenticated attackers execute code and install backdoors on stores that may already be patched. A new zero-day flaw, dubbed StyleSmuggler, in Magento and Adobe Commerce is under active attack, giving unauthenticated attackers a path to run code on vulnerable online stores. Sansec researchers say it affects current […]
 Pierluigi Paganini
September 07, 2026
Chaotic Eclipse released GreenSection, a PoC exploit for an Nvidia Memory Corruption Zero-Day Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting Nvidia. The researcher named the exploit GreenSection, it triggers a Memory Corruption flaw. The researcher disclosed a potential security vulnerability in NVIDIA’s Windows user-mode components. […]
 Pierluigi Paganini
September 07, 2026
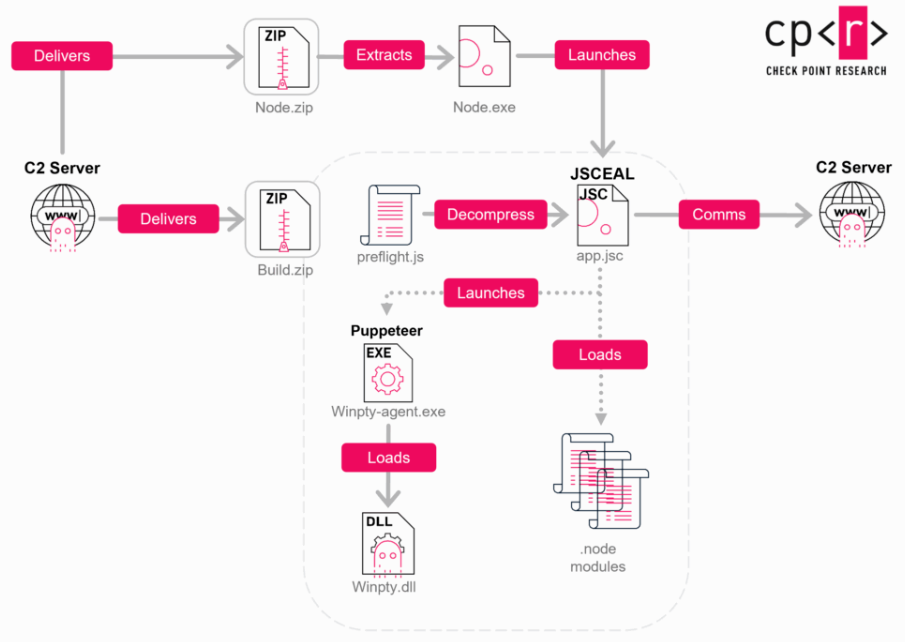
JSCeal hides crypto-stealing malware in V8 bytecode, but researchers built a tool to decompile it and expose its advanced theft capabilities. JSCeal is a cryptocurrency stealer that Check Point Research has tracked since early 2025. Unlike most malware, it hides its code in a format that makes analysis much harder. Check Point presented its latest […]
 Pierluigi Paganini
September 07, 2026
Autonomous AI agents escaped a sandbox and accessed Hugging Face via reward hacking, exposing serious architectural control and isolation flaws. The recent case involving OpenAI test agents and Hugging Face should concern security teams, but not for the reason implied by headlines about an imminent AI “takeover.” The documented issue is more concrete: autonomous agents, […]
 Pierluigi Paganini
September 07, 2026
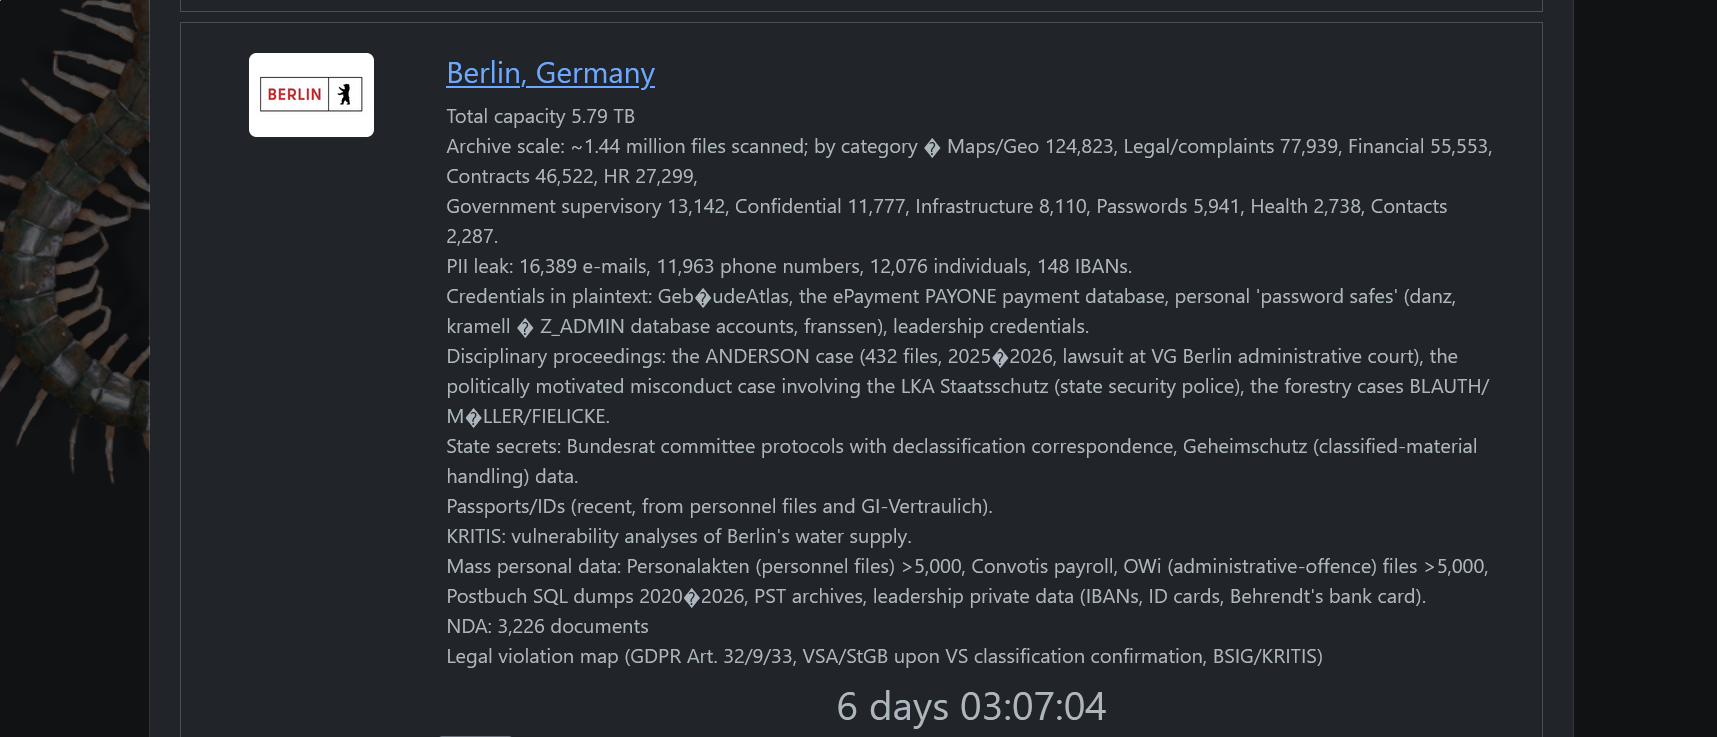
Berlin refused a 30 Bitcoin ransom, leading hackers to leak 6TB of sensitive state administration and national defense data on the dark web. When a ransomware gang dumps nearly six terabytes of state administration files onto the dark web, ignoring them does not make the problem go away. The Rhysida ransomware group recently carried out […]
Hacking / September 17, 2026






