 Pierluigi Paganini
 October 14, 2026
Ivanti VPN zero-days let attackers gain root access, steal credentials, evade detection, and prepare for wider network compromise. On October 5, Volexity started investigating suspicious activity at one of its monitoring customers and traced everything back to an Ivanti Connect Secure VPN appliance running version 22.8R2.4, the latest build available at the time. Three chained […]
 Pierluigi Paganini
April 07, 2025
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Ivanti Connect Secure, Policy Secure and ZTA Gateways flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an Apache Tomcat path equivalence vulnerability, tracked as CVE-2025-22457, to its Known Exploited Vulnerabilities (KEV) catalog. The vulnerability CVE-2025-22457 is a stack-based buffer overflow […]
 Pierluigi Paganini
January 16, 2024
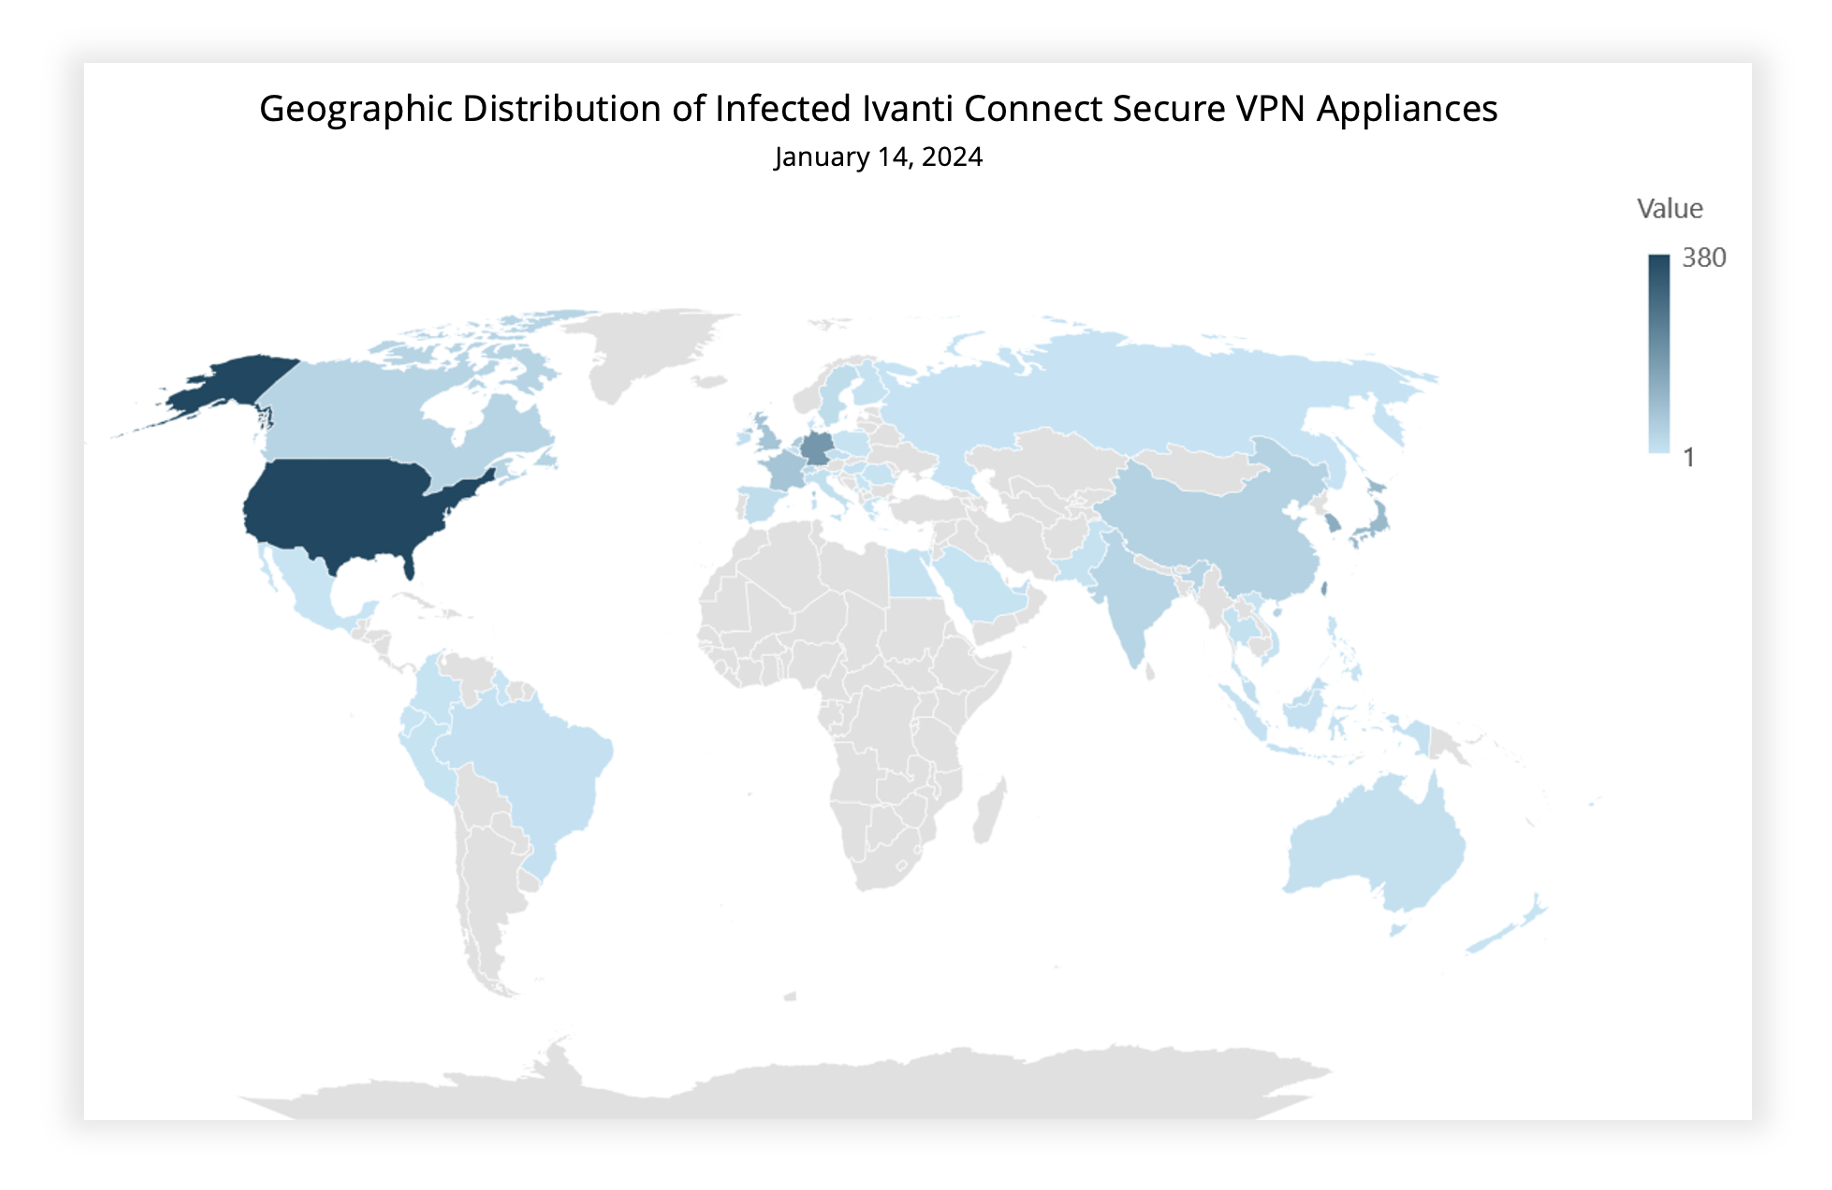
Experts warn that recently disclosed Ivanti Connect Secure VPN and Policy Secure vulnerabilities are massively exploited in the wild. Last week, software firm Ivanti reported that threat actors are exploiting two zero-day vulnerabilities (CVE-2023-46805, CVE-2024-21887) in Connect Secure (ICS) and Policy Secure to remotely execute arbitrary commands on targeted gateways. The flaw CVE-2023-46805 (CVSS score […]

Hacking / October 22, 2026