


 Pierluigi Paganini
 June 28, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. New FBI Alert: Russian Intelligence Uses Signal Recovery Keys to Access Messages Hospitality Sector Hit by […]
 Pierluigi Paganini
June 26, 2026
macOS.Gaslight: DPRK Rust implant for Mac with a prompt injection payload designed to fool AI-based malware analysts. SentinelLabs researchers spotted a Rust-based macOS implant, dubbed macOS.Gaslight, that surfaced in early June after an Apple XProtect update pointed to a VirusTotal sample uploaded on May 22. The binary was undetected by static engines at the time […]
 Pierluigi Paganini
June 25, 2026
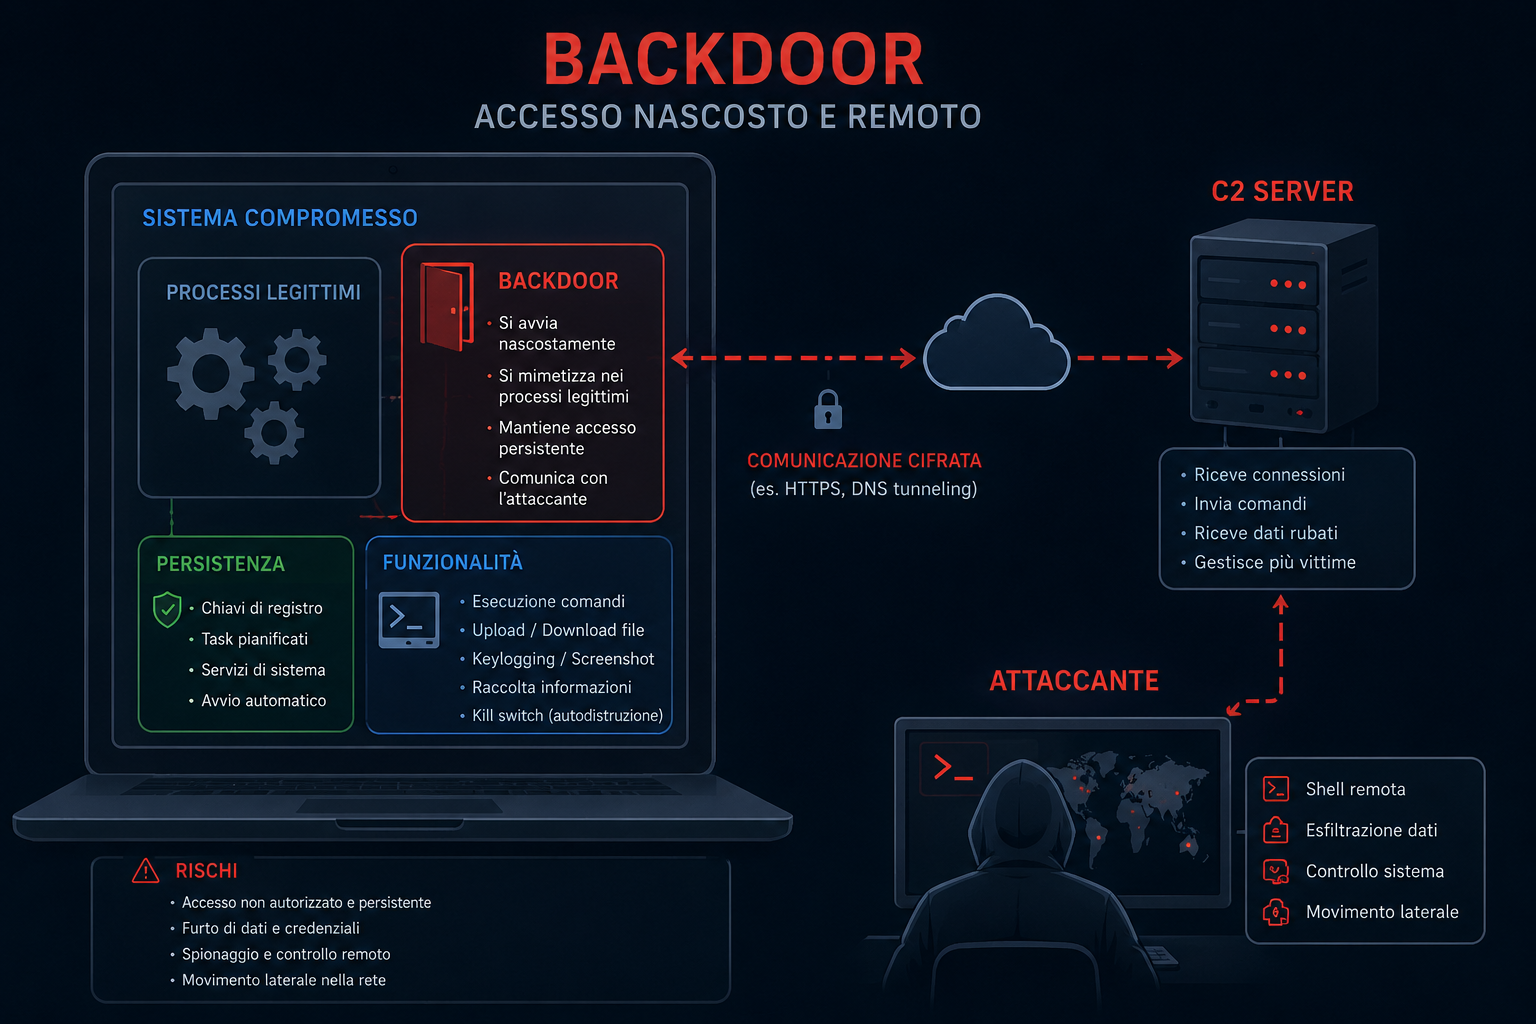
Mistic is a stealthy backdoor used by KongTuke-linked actors to keep long-term access in ransomware-targeted networks. Mistic is the kind of backdoor that tells you the operator wants time, not noise. Symantec security researchers say it has shown up in financially motivated attacks against insurance, education, IT, and professional services firms, and they link it […]
 Pierluigi Paganini
June 24, 2026
Operation Endgame disrupted malware services like StealC and Amadey that enable ransomware, fraud, and attacks on critical infrastructure. Between June 15 and 19, 2026, Europol coordinated a two-week law enforcement operation involving agencies from Canada, Denmark, Germany, the Netherlands, the UK, and the US, alongside private firms like Microsoft, Bitdefender, IBM X-Force, Proofpoint, Infoblox, Shadowserver, […]
 Pierluigi Paganini
June 23, 2026
Xsolis disclosed a breach affecting 1.4M people after a phishing attack exposed personal and health data from its hospital clients’ systems. Healthcare tech company Xsolis, Inc. has disclosed a data breach impacting nearly 1.4 million individuals. The Tennessee-based firm provides utilization management and revenue cycle solutions for healthcare providers. The company became aware of an […]
 Pierluigi Paganini
June 23, 2026
Attackers backdoored ShapedPlugin Pro updates, deploying malware that steals credentials, 2FA secrets, and grants full site access. If you installed a ShapedPlugin Pro plugin between April and June 2026 and kept it updated, your site may be compromised. Not because you did something wrong, but because the vendor’s own build and distribution pipeline was breached. […]
 Pierluigi Paganini
June 22, 2026
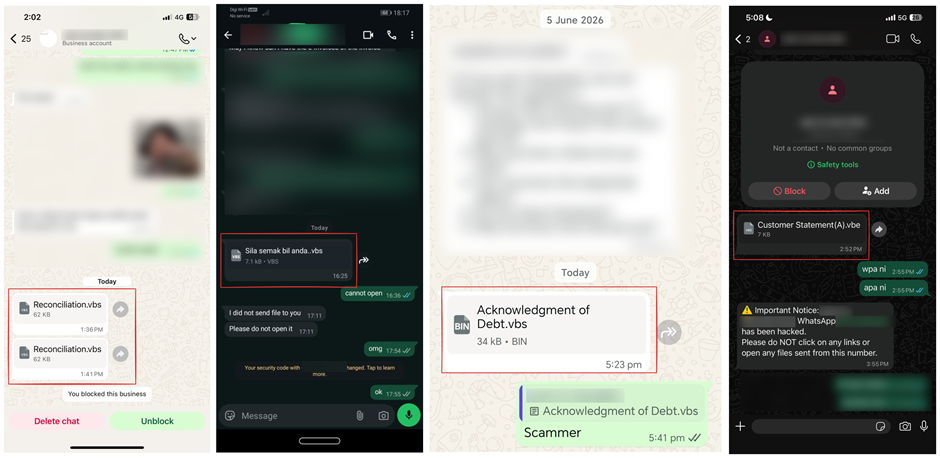
WhatsApp accounts were hijacked to spread fake debt notices that install remote access software, giving attackers control of victims’ PCs. Kaspersky published a technical analysis this week of an active malware campaign that spreads through WhatsApp messages and ends with a remote management tool silently installed on the victim’s machine. The campaign is still running […]
 Pierluigi Paganini
June 22, 2026
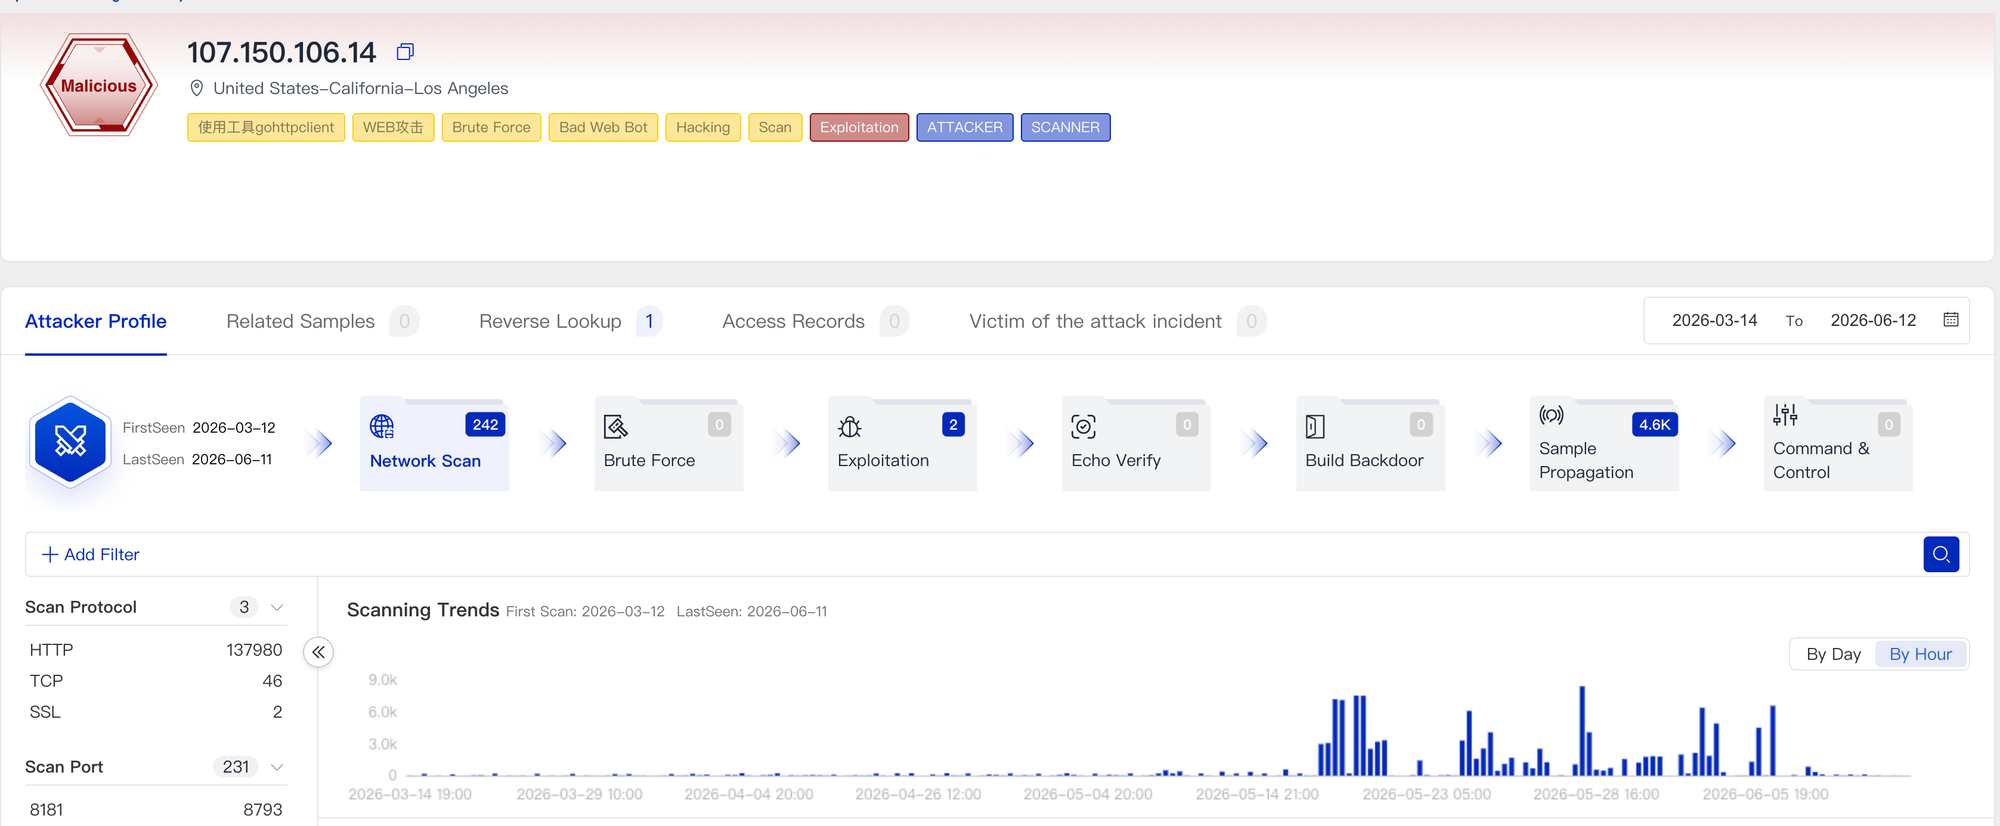
AryStinger hijacks outdated routers via old flaws, turning 4,300+ devices into a stealth network for reconnaissance and intrusion support. On March 12, 2026, QiAnXin’s XLab threat detection system flagged a single IP address, 107.150.106.14, spreading a Linux binary through two vulnerabilities that were disclosed in 2013 and 2016 respectively. The binary had zero detections on […]
 Pierluigi Paganini
June 21, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter OptinMonster supply chain attack hits 1.2 million sites Public and Private Medical Community Targeted by China-Nexus Threat Actor Pursuing Artificial Intelligence, Cyber, Medical, and National Defense Research Rokarolla : Android Banker with Complete Device […]
Pierluigi Paganini
June 21, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. Inside GentleKiller: The EDR-Killer Powering The Gentlemen FortiBleed Exposes Global Credential-Spraying Operation CISA Warns of Active […]







