 Pierluigi Paganini
 October 22, 2023
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs are free for you in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. A threat actor is selling access to Facebook and Instagram’s Police Portal Threat actors breached Okta […]
 Pierluigi Paganini
October 20, 2023
A joint international law enforcement investigation led to the arrest of a malware developer who was involved in the Ragnar Locker ransomware operation. Yesterday we became aware of a joint law enforcement operation that led to the seizure of the Ragnar Locker ransomware’s infrastructure. The police on Thursday seized the Tor negotiation and data leak sites, group’s […]
Pierluigi Paganini
October 19, 2023
An international law enforcement operation shuts down the infrastructure of the Ragnar Locker ransomware operation. Law enforcement from the US, Europe, Germany, France, Italy, Japan, Spain, Netherlands, Czech Republic, and Latvia conducted a joint operation that led to the seizure of the Ragnar Locker ransomware’s infrastructure. The police on Thursday seized the Tor negotiation and […]
 Pierluigi Paganini
October 19, 2023
I’m proud to announce the release of the 11th edition of the ENISA Threat Landscape (ETL) on the state of the cybersecurity threat landscape. The Europen Agency for cybersecurity ENISA releases its ENISA Threat Landscape 2023 (ETL) report, which is the annual analysis of the state of the cybersecurity threat landscape. This is the 11th edition of the […]
 Pierluigi Paganini
October 17, 2023
Threat actors exploited the recently disclosed zero-day flaw (CVE-2023-20198) in a large-scale hacking campaign on Cisco IOS XE devices. Threat actors have exploited the recently disclosed critical zero-day vulnerability (CVE-2023-20198) to compromise thousands of Cisco IOS XE devices, security firm VulnCheck warns. Cisco this week warned customers of a zero-day vulnerability, tracked as CVE-2023-20198 (CVSS score 10), […]
 Pierluigi Paganini
October 17, 2023
Russia-linked APT group Sandworm has hacked eleven telecommunication service providers in Ukraine between May and September 2023. The Russia-linked APT group Sandworm (UAC-0165) has compromised eleven telecommunication service providers in Ukraine between May and September 2023, reported the Ukraine’s Computer Emergency Response Team (CERT-UA). According to public sources, the threat actors targeted ICS of at […]
 Pierluigi Paganini
October 17, 2023
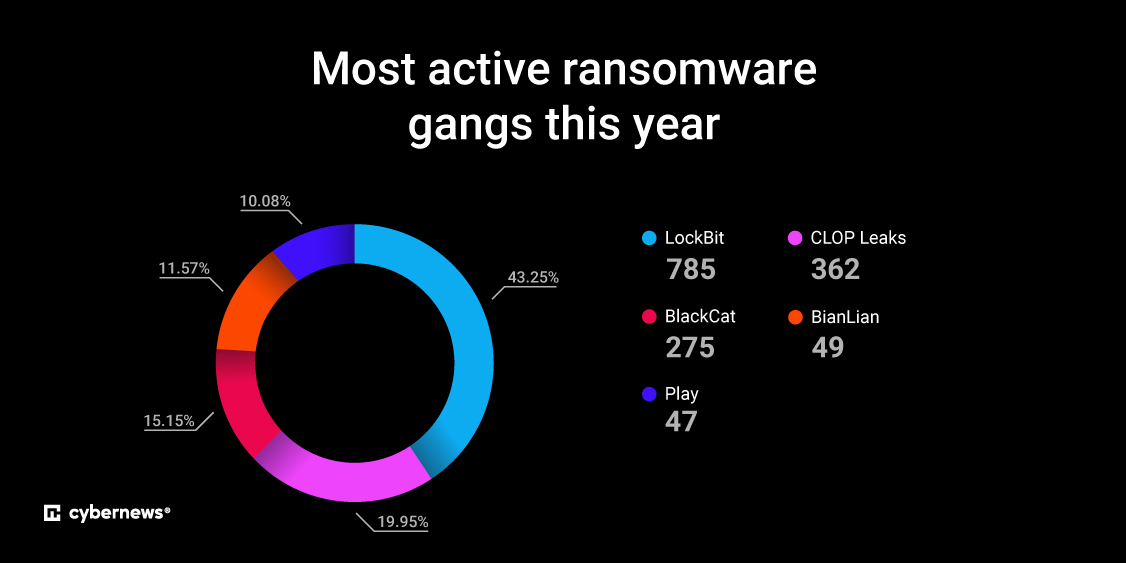
What is the impact of ransomware on organizations? One employee’s mistake can cost a company millions of dollars. Studies show that human error is the root cause of more than 80% of all cyber breaches, whether malicious or unintended. The recent debilitating cyberattacks on casino and resort giants MGM and Caesars are no exception. How […]
 Pierluigi Paganini
October 17, 2023
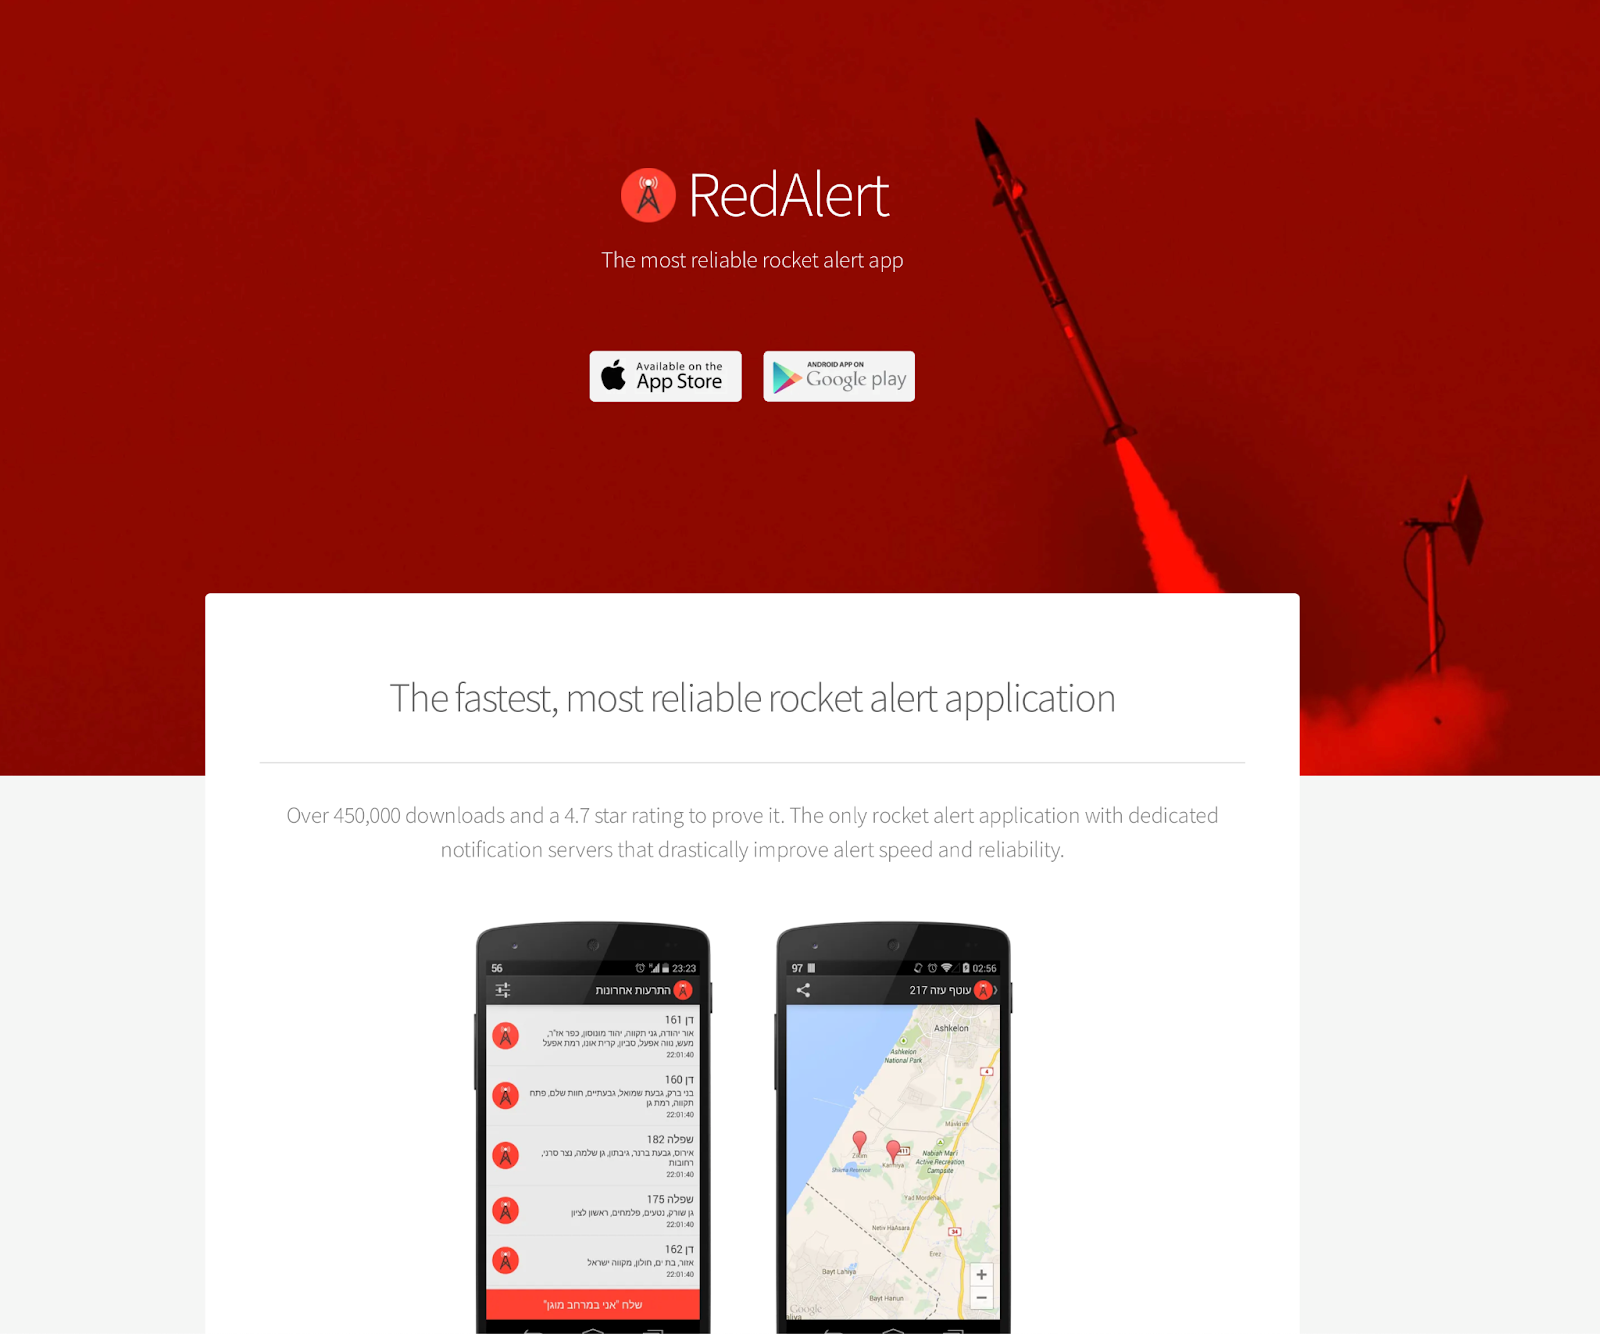
Threat actors are targeting Israeli Android users with a malicious version of the ‘RedAlert – Rocket Alerts’ that hide spyware. A threat actor is targeting Israeli Android users with a spyware-laced version of the ‘RedAlert – Rocket Alerts’ app, Cloudflare warns. RedAlert – Rocket Alerts is a mobile app that provides real-time alerts about incoming […]
 Pierluigi Paganini
October 16, 2023
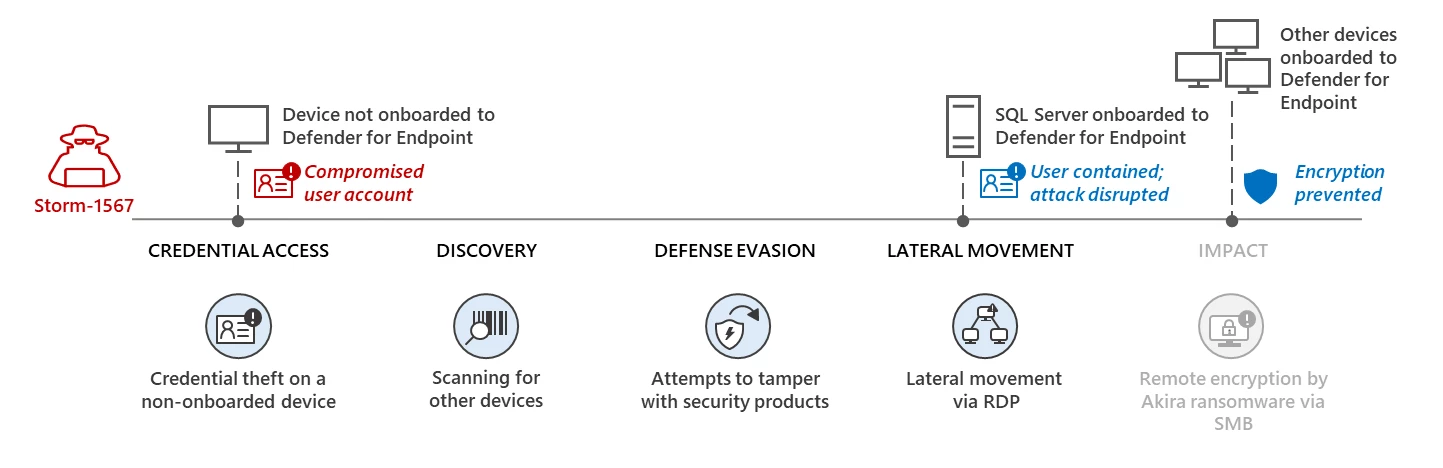
Microsoft thwarted a large-scale hacking campaign carried out by Akira ransomware operators targeting an unknown industrial organization. Microsoft announced that its Microsoft Defender for Endpoint helped to block a large-scale hacking campaign carried out by Akira ransomware operators (tracked by Microsoft as Storm-1567) The attack took place in early June 2023 and aimed at an industrial engineering […]
 Pierluigi Paganini
October 16, 2023
Researchers uncovered an ongoing campaign abusing popular messaging platforms Skype and Teams to distribute the DarkGate malware. From July to September, researchers from Trend Micro observed a malicious campaign DarkGate campaign abusing instant messaging platforms to deliver a VBA loader script to victims. The threat actors abused popular messaging platforms such as Skype and Teams […]