 Pierluigi Paganini
 May 23, 2023
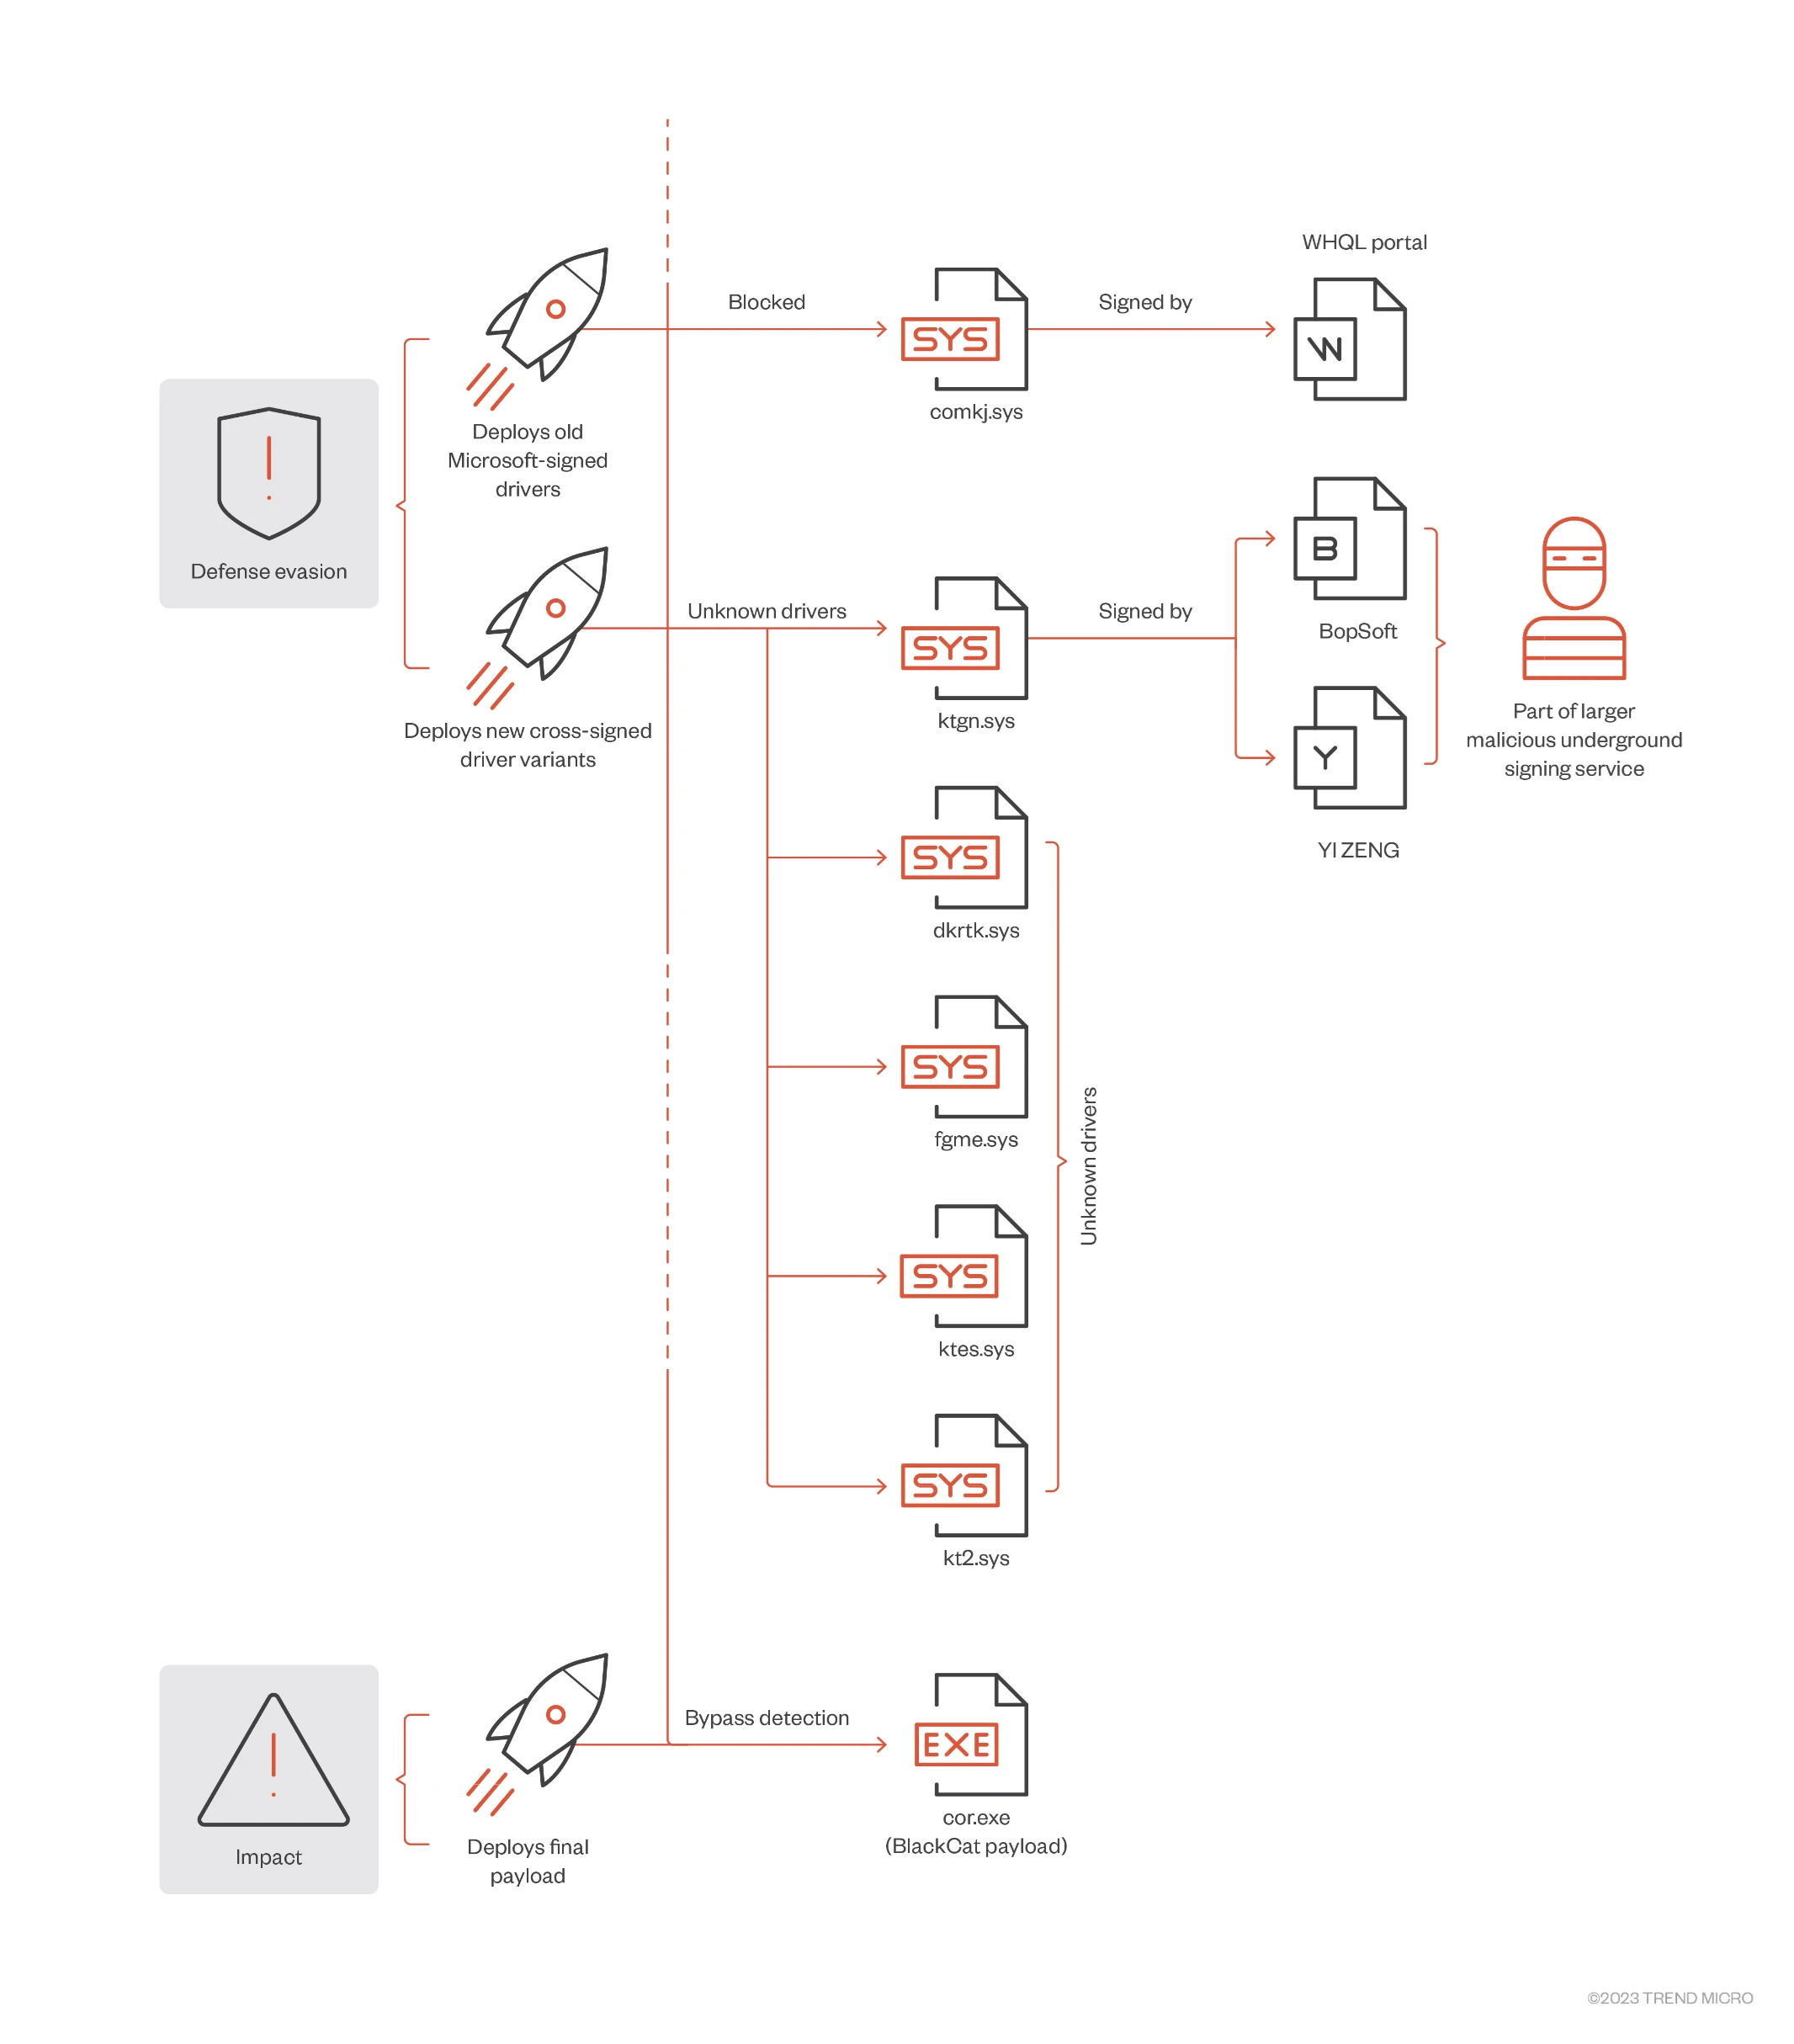
Experts spotted the ALPHV/BlackCat ransomware group using signed malicious Windows kernel drivers to evade detection. Trend Micro researchers shared details about ALPHV/BlackCat ransomware incident that took place on February 2023. A BlackCat affiliate employed signed malicious Windows kernel drivers to evade detection. Experts believe the driver is a new version of the malware reported in December 2022 […]
 Pierluigi Paganini
May 22, 2023
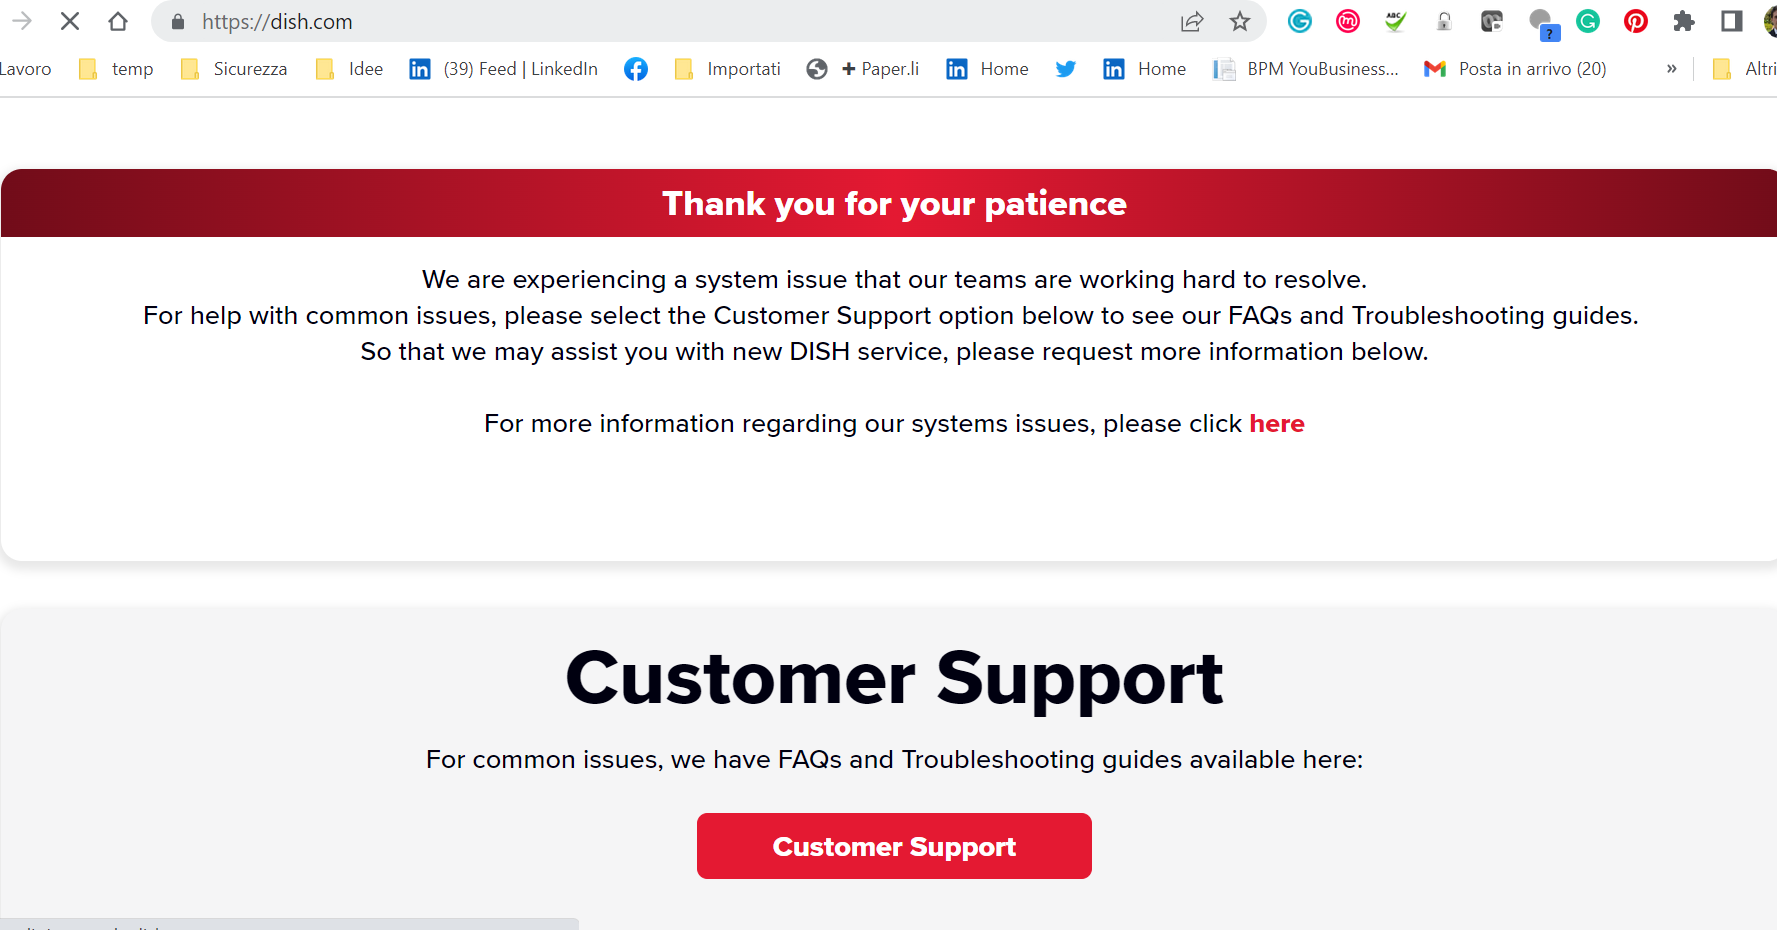
Satellite TV giant Dish Network disclosed a data breach after the February ransomware attack and started notifying impacted individuals. The American satellite broadcast provider Dish Network went offline on February 24, 2023, the outage impacted Dish.com, Dish Anywhere app, and many other services owned by the company. In early February, the company admitted that the outage was […]
 Pierluigi Paganini
May 21, 2023
The Python Package Index (PyPI) maintainers have temporarily disabled the sign up and package upload processes due to an ongoing attack. The maintainers of Python Package Index (PyPI), the Python software repository, have temporarily disabled the sign up and package upload processes due to an ongoing attack. The maintainers opted to disable the above functionalities […]
 Pierluigi Paganini
May 21, 2023
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs are free for you in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. We are in the final! Please vote for Security Affairs (https://securityaffairs.com/) as the best European Cybersecurity […]
 Pierluigi Paganini
May 20, 2023
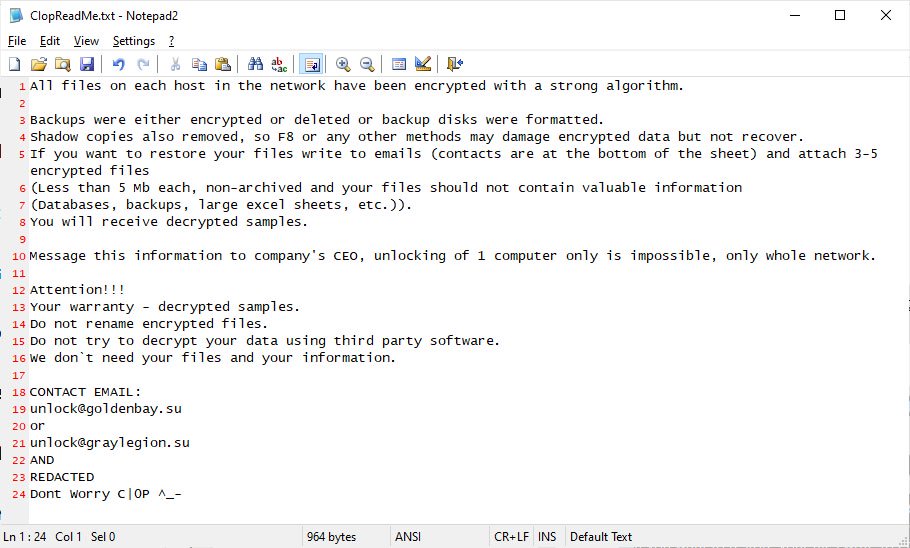
Cybercriminal gang FIN7 returned with a new wave of attacks aimed at deploying the Clop ransomware on victims’ networks. Researchers at Microsoft Security Intelligence team published a series of tweets to warn of a new wave of attacks aimed at distributing the Clop ransomware and linked it to the financially motivated cybercriminal group Sangria Tempest […]
 Pierluigi Paganini
May 19, 2023
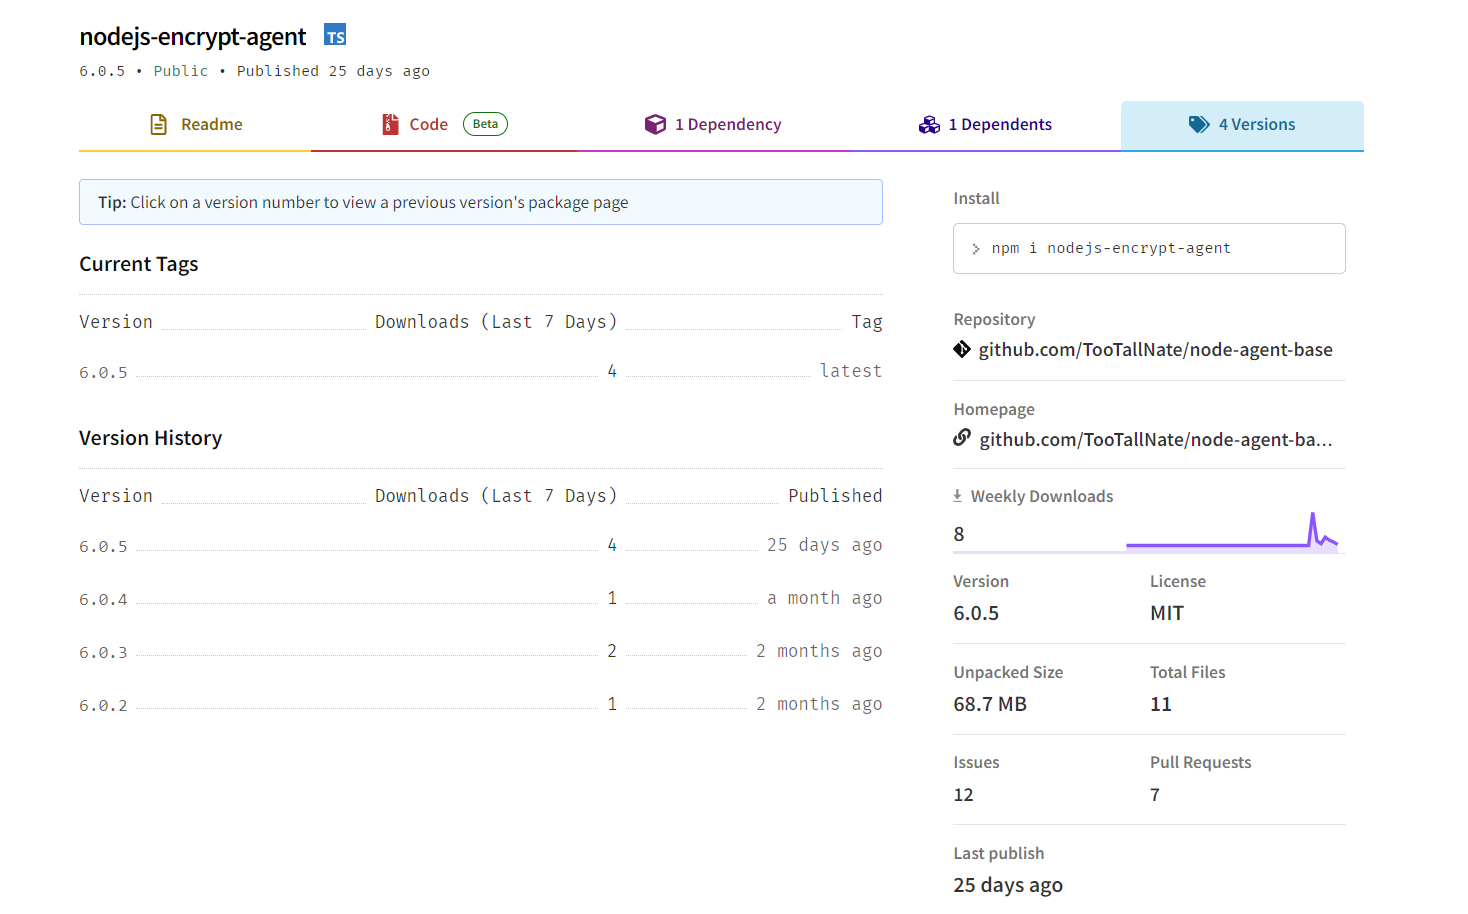
Experts discovered two malicious packages in the npm package repository, both were laced with an open-source info-stealer called TurkoRat. ReversingLabs discovered two malicious packages, respectively named nodejs-encrypt-agent and nodejs-cookie-proxy-agent, in the npm package repository containing an open-source info-stealer called TurkoRat. TurkoRat is an information-stealing malware that can obtain a broad range of data from the infected machine, […]
 Pierluigi Paganini
May 19, 2023
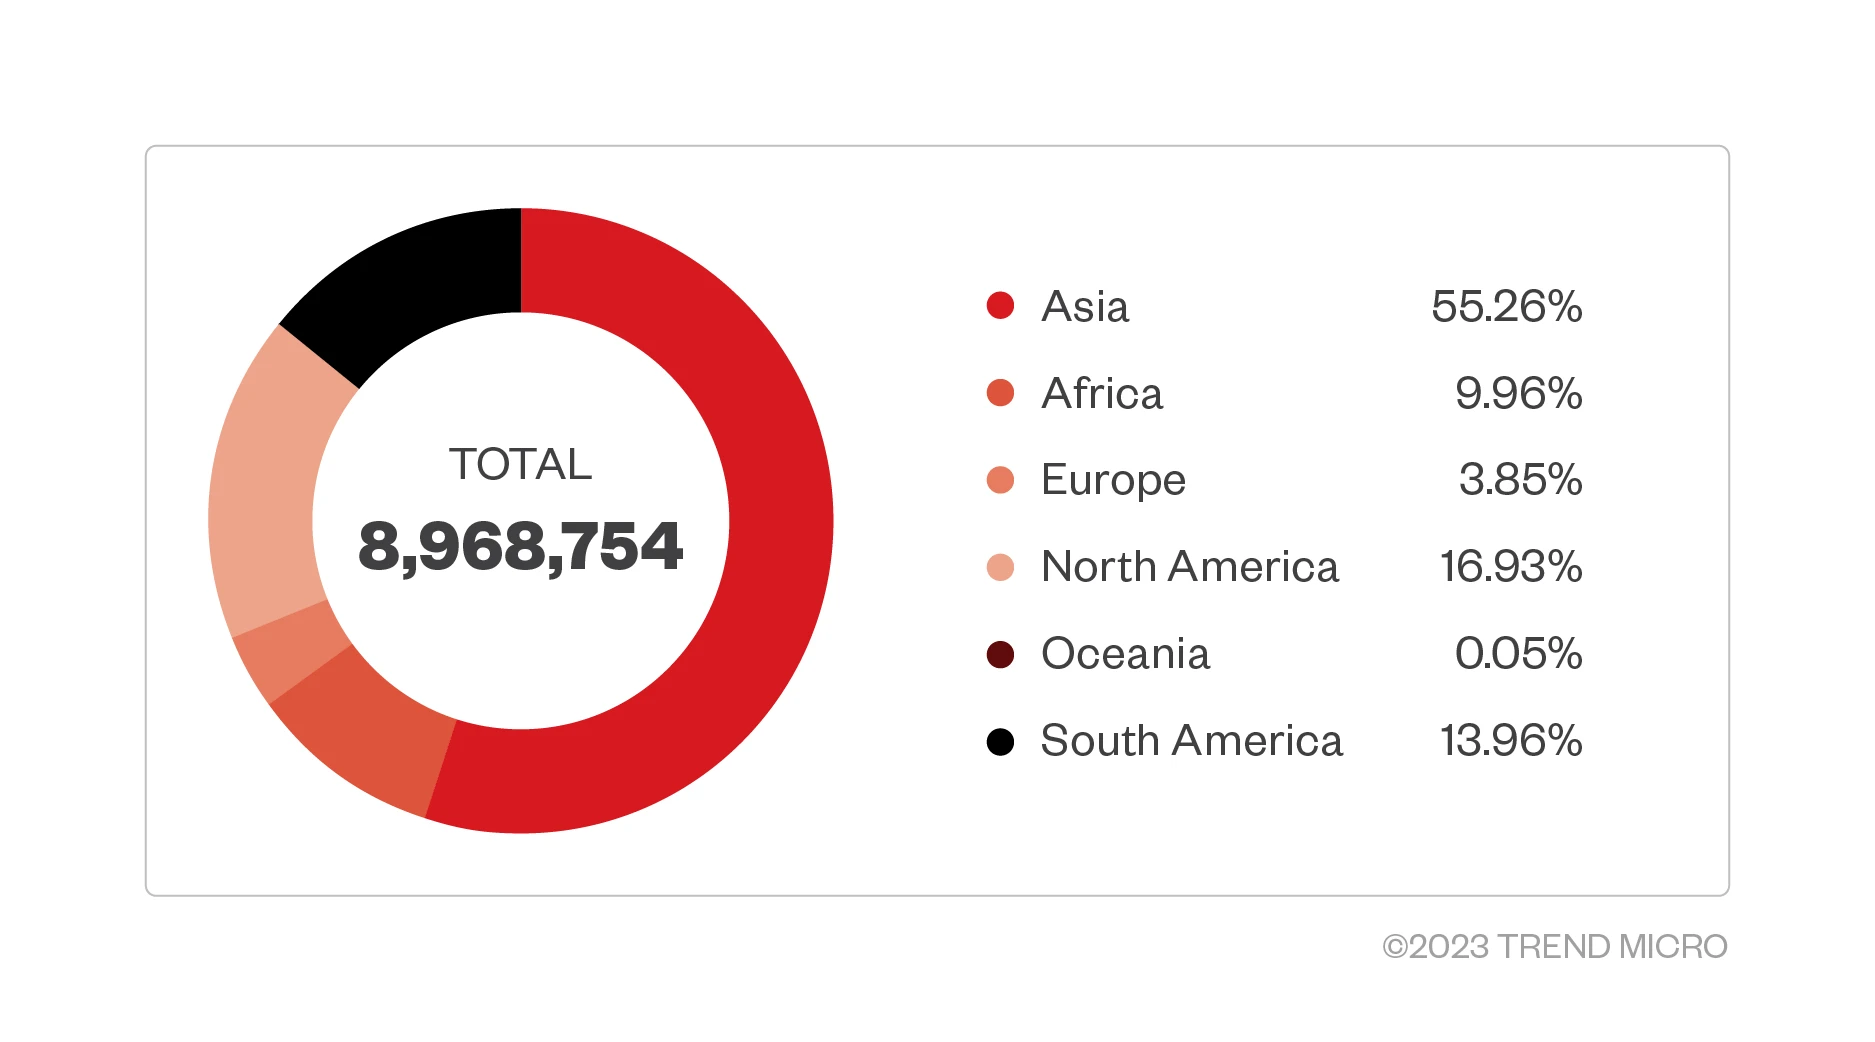
The Lemon Group cybercrime ring has reportedly pre-installed malware known as Guerilla on almost 9 million Android devices. A cybercrime group tracked has Lemon Group has reportedly pre-installed malware known as Guerilla on almost 9 million Android devices. Infected devices were used for multiple malicious activities, including traffic redirections through mobile proxies, info-stealing, click fraud, and […]
 Pierluigi Paganini
May 17, 2023
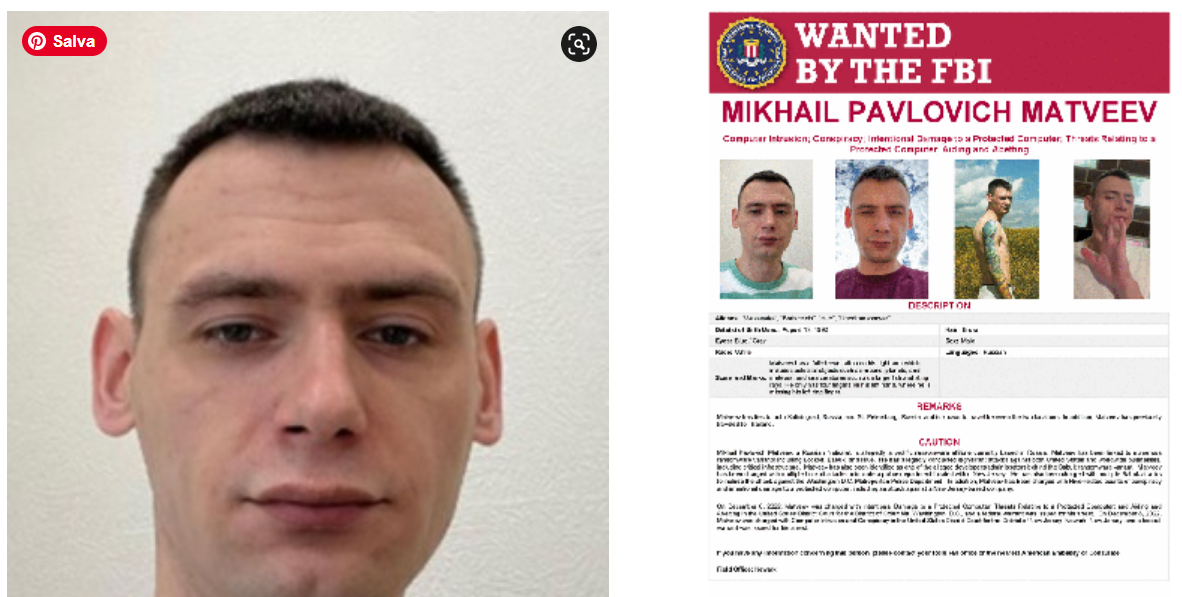
The US government is offering a $10M reward for Russian national Mikhail Pavlovich Matveev (30) charged for his role in ransomware attacks The US Justice Department charged Russian national Mikhail Pavlovich Matveev (30), aka Wazawaka, m1x, Boriselcin, and Uhodiransomwar, for his alleged role in multiple ransomware attacks. The DoJ unsealed two indictments charging the man […]
 Pierluigi Paganini
May 16, 2023
French electronics manufacturer Lacroix Group shut down three plants after a cyber attack, experts believe it was the victim of a ransomware attack. The French electronics manufacturer Lacroix Group shut down three facilities in France, Germany, and Tunisia in response to a cyber attack. The group designs and manufactures electronic equipment for its customers in […]
 Pierluigi Paganini
May 16, 2023
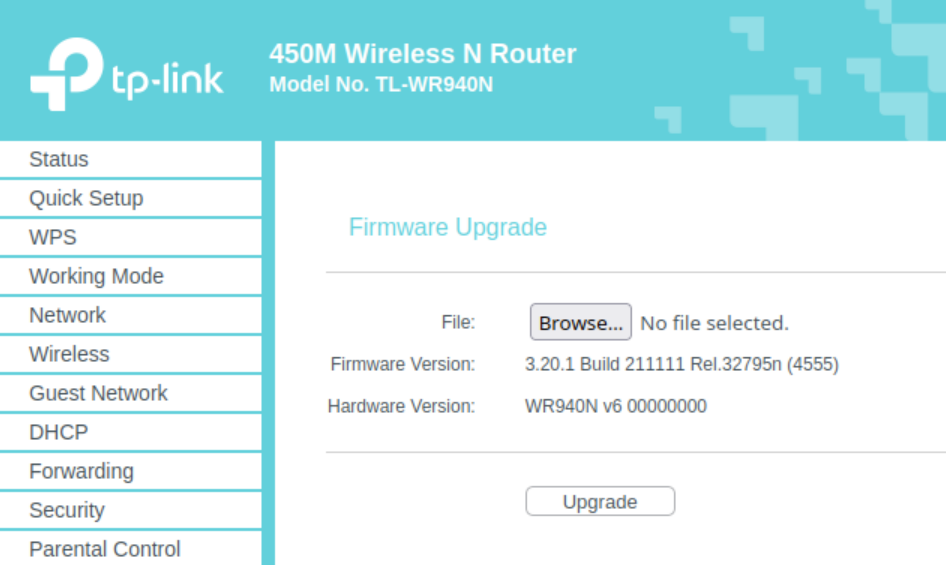
China-linked APT group Mustang Panda employed a custom firmware implant targeting TP-Link routers in targeted attacks since January 2023. Since January 2023, Check Point Research monitored a series of targeted attacks aimed at European foreign affairs entities that have been linked to the China-linked cyberespionage group Mustang Panda (aka Camaro Dragon, RedDelta or “Bronze President). MustangPanda […]
Artificial Intelligence / September 30, 2026


Security / September 30, 2026