


 Pierluigi Paganini
 February 20, 2023
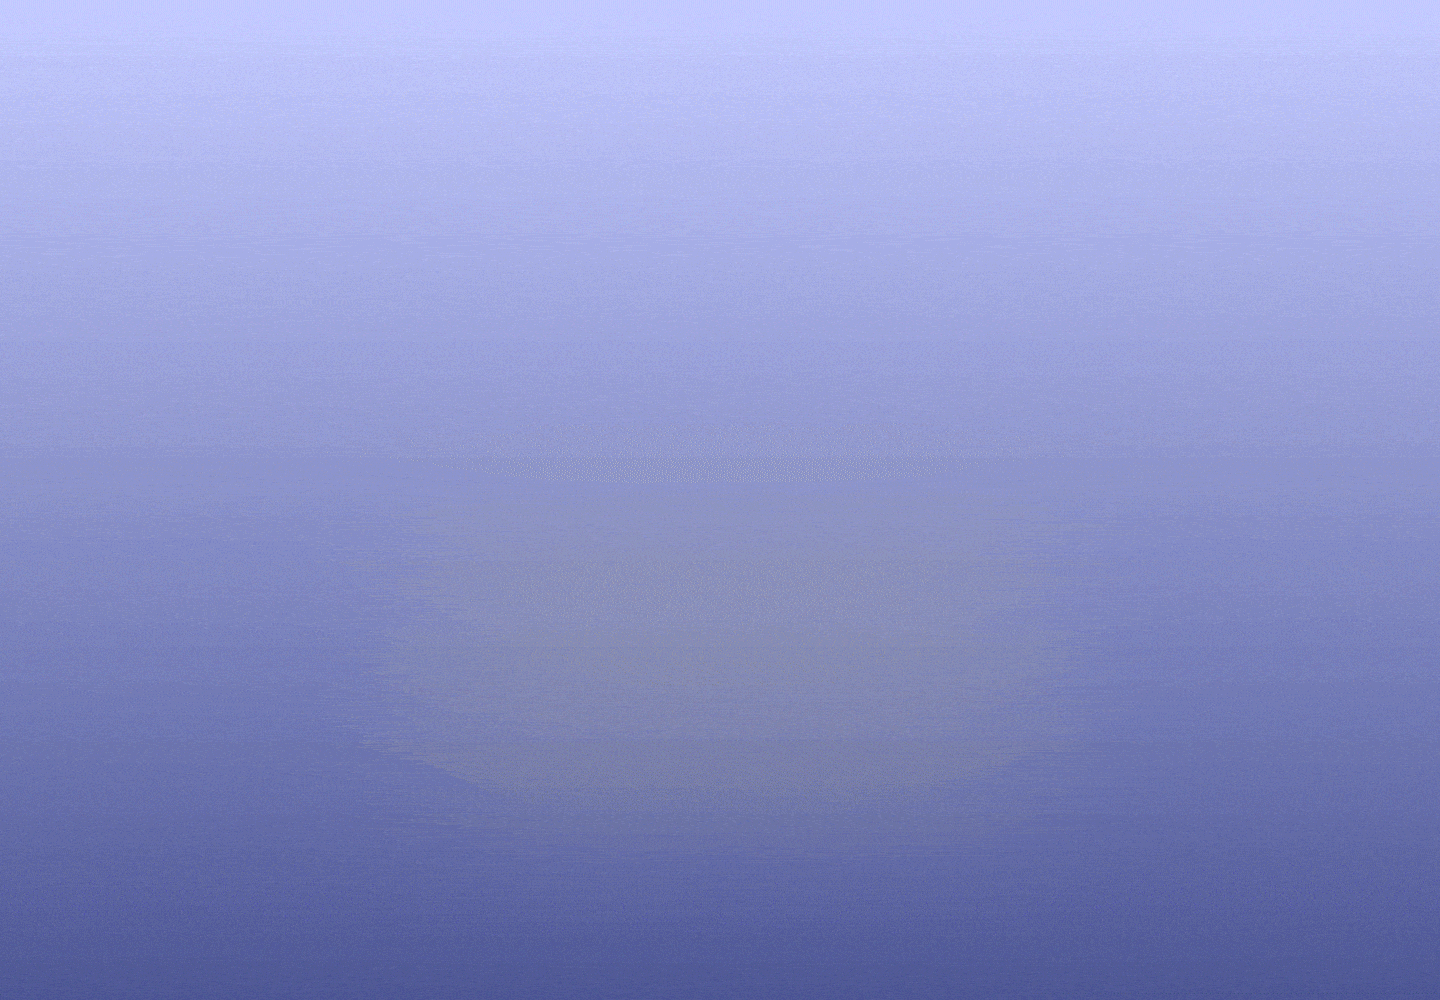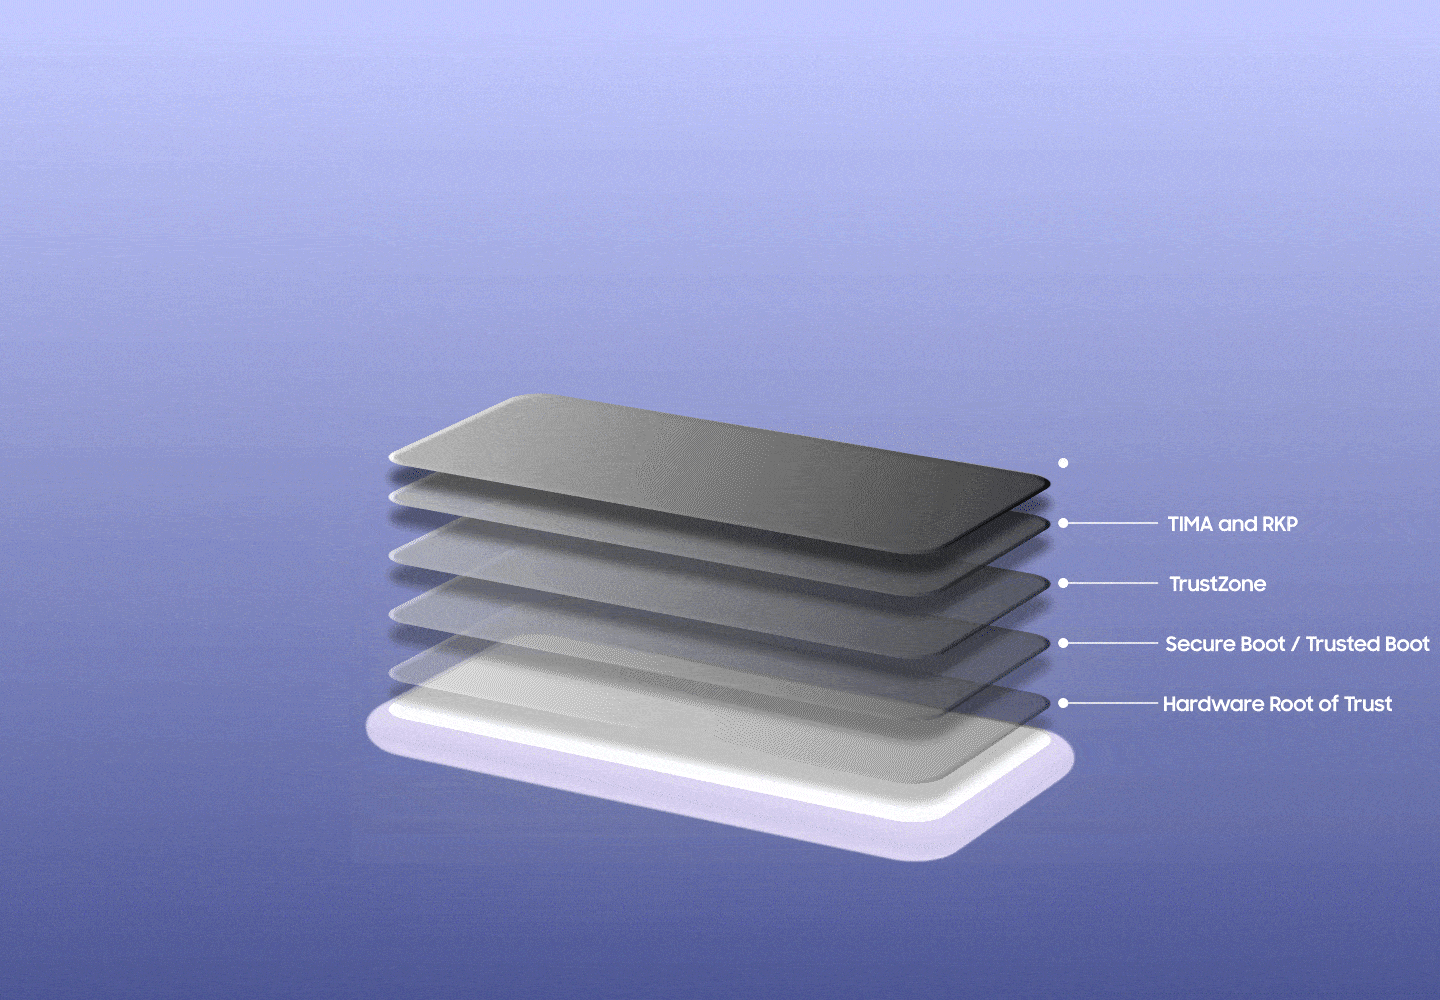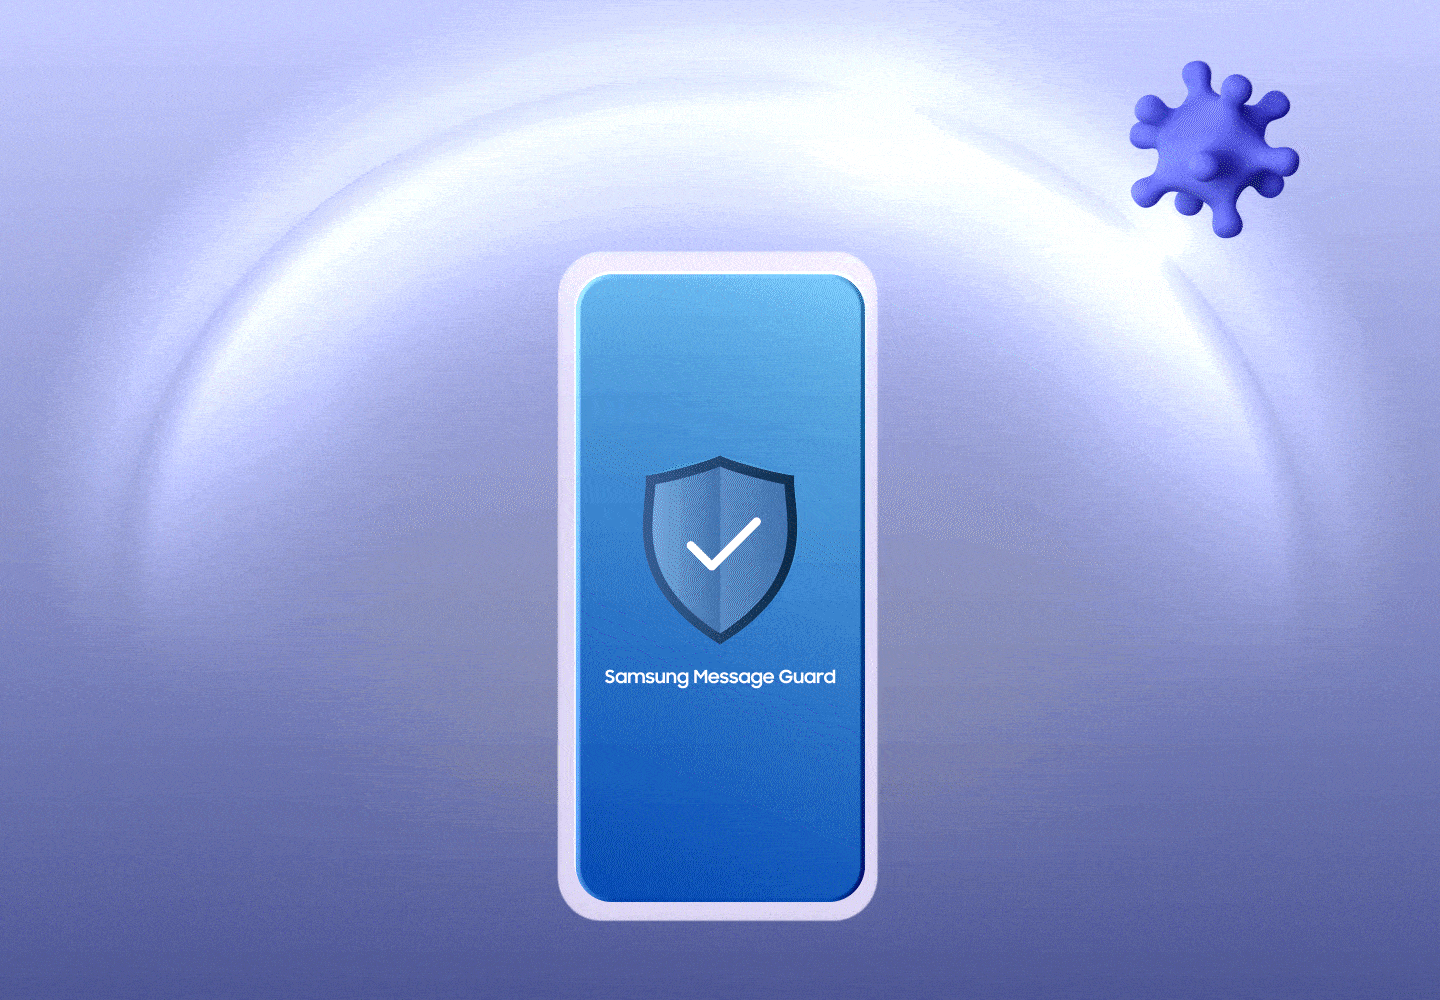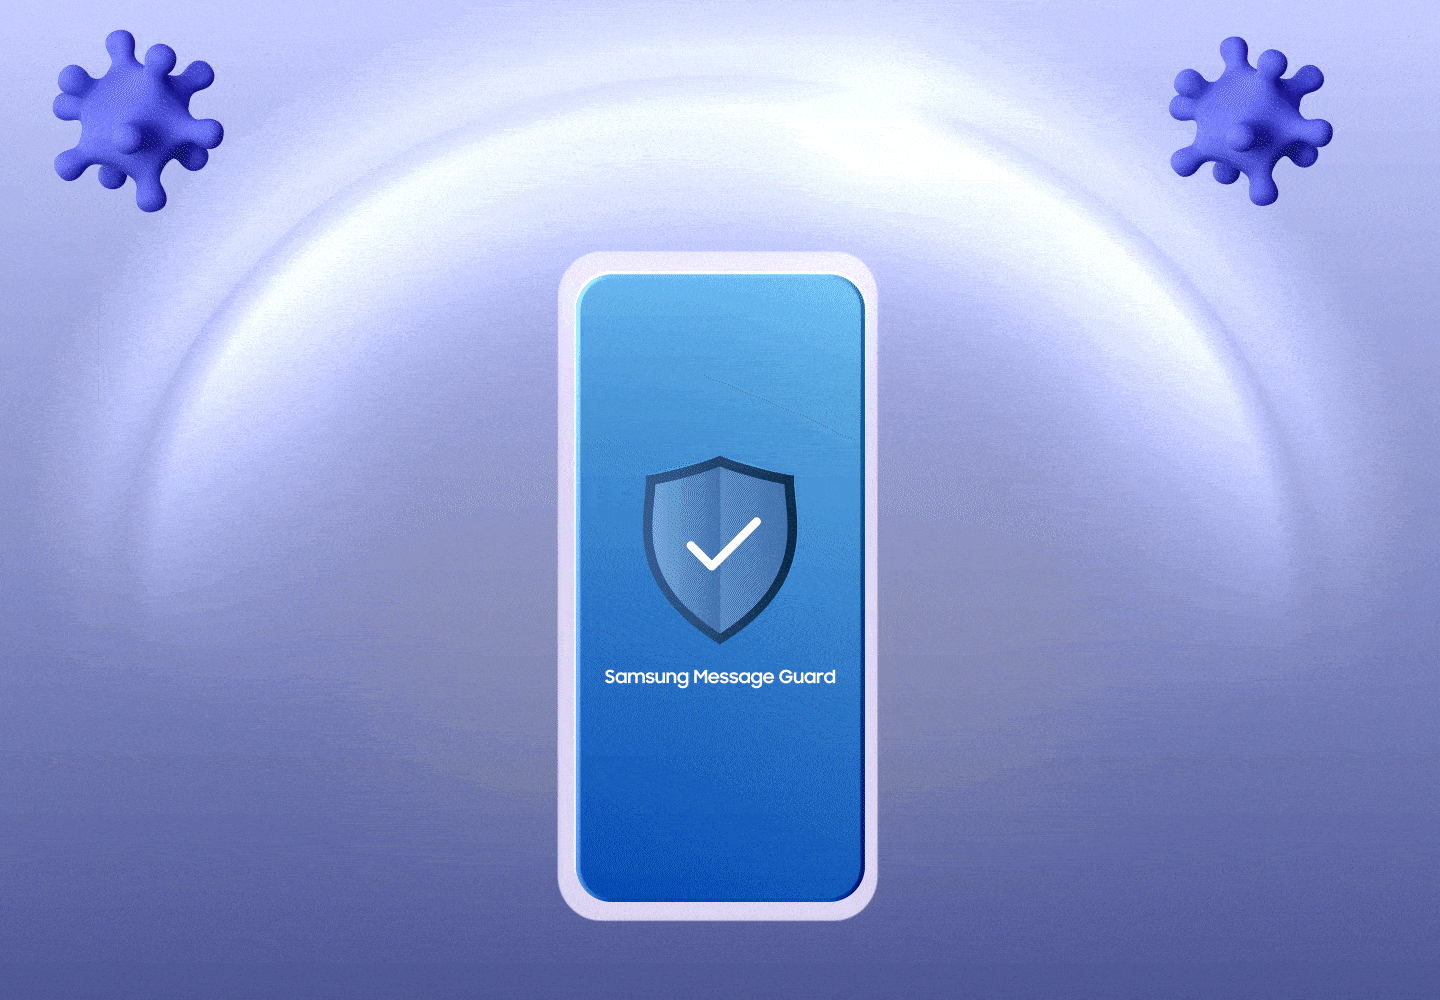
Samsung introduces a new protection feature called Message Guard to protect users from zero-click malware attacks. Samsung announced the implementation of a new security feature called Message Guard that aims at protecting users from malicious code that can be installed via zero-click attacks. Zero-click exploits allow attackers to compromise the target device without any user interaction, for example, a […]
 Pierluigi Paganini
February 20, 2023
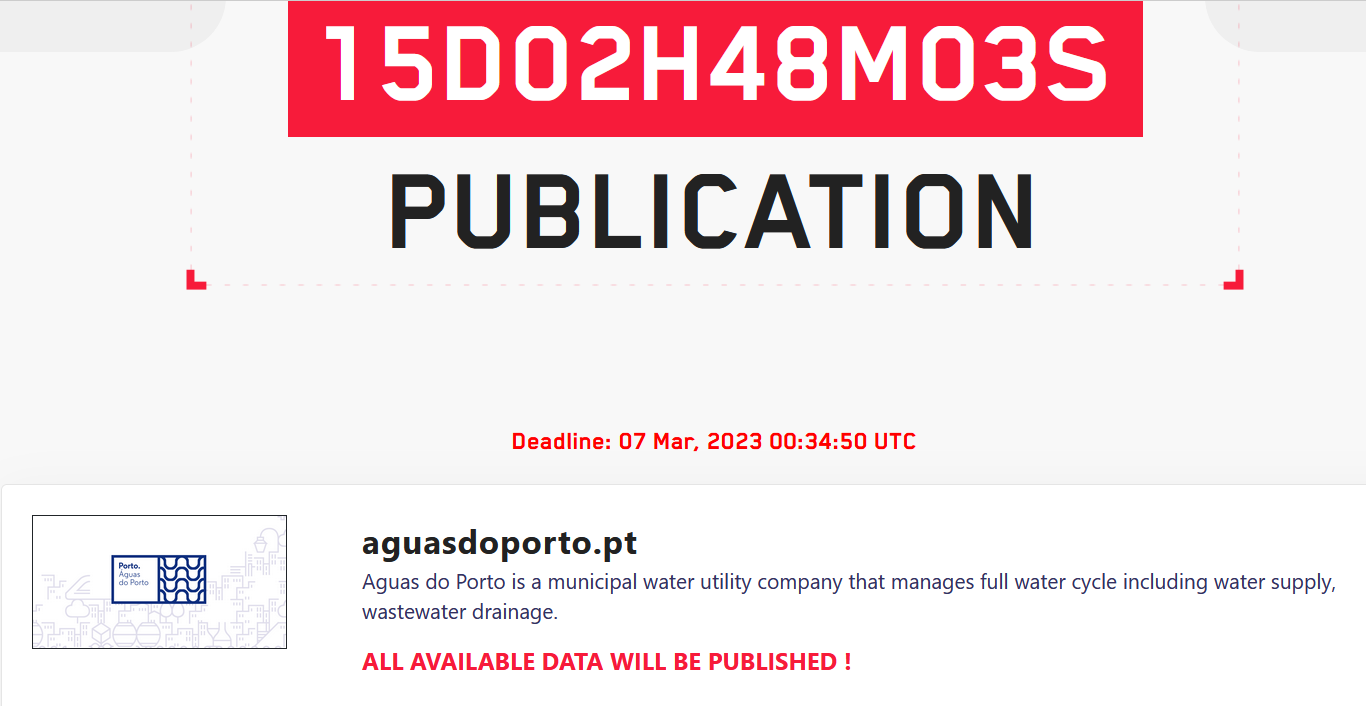
The LockBit ransomware gang claims to have hacked Aguas do Porto, a Portuguese municipal water utility company. The LockBit ransomware gang claims to have hacked Aguas do Porto, a Portuguese municipal water utility company, and is threatening to leak the stolen data. Aguas do Porto is a municipal water utility company that manages the full […]
 Pierluigi Paganini
February 19, 2023
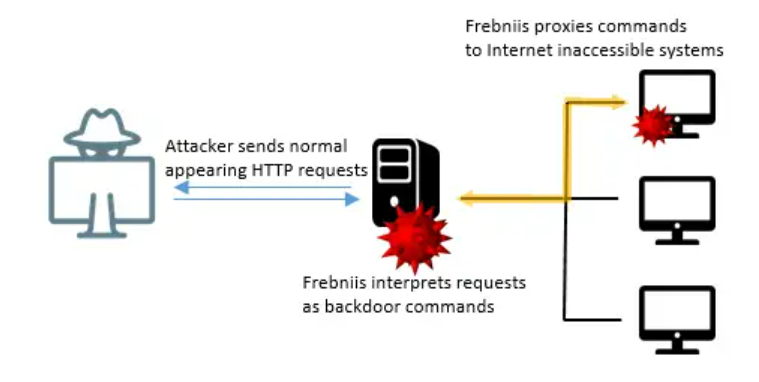
Experts spotted a malware dubbed Frebniis that abuses a Microsoft IIS feature to deploy a backdoor and monitor all HTTP traffic to the system. Broadcom Symantec researchers have spotted a new malware, tracked as Frebniis, that abuses Microsoft Internet Information Services (IIS) to deploy a backdoor and monitor all HTTP traffic to the infected system, […]
 Pierluigi Paganini
February 19, 2023
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs are free for you in your email box. If you want to also receive for free the newsletter with the international press subscribe here. Twitter will allow using the SMS-based two-factor authentication (2FA) only to its Blue subscribers GoDaddy […]
 Pierluigi Paganini
February 16, 2023
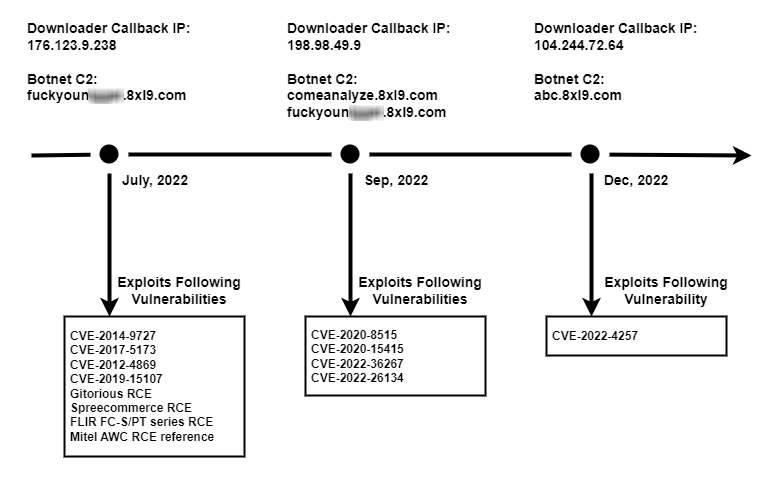
During the second half of 2022, a variant of the Mirai bot, tracked as V3G4, targeted IoT devices by exploiting tens of flaws. Palo Alto Networks Unit 42 researchers reported that a Mirai variant called V3G4 was attempting to exploit several flaws to infect IoT devices from July to December 2022. Below is the list […]
 Pierluigi Paganini
February 16, 2023
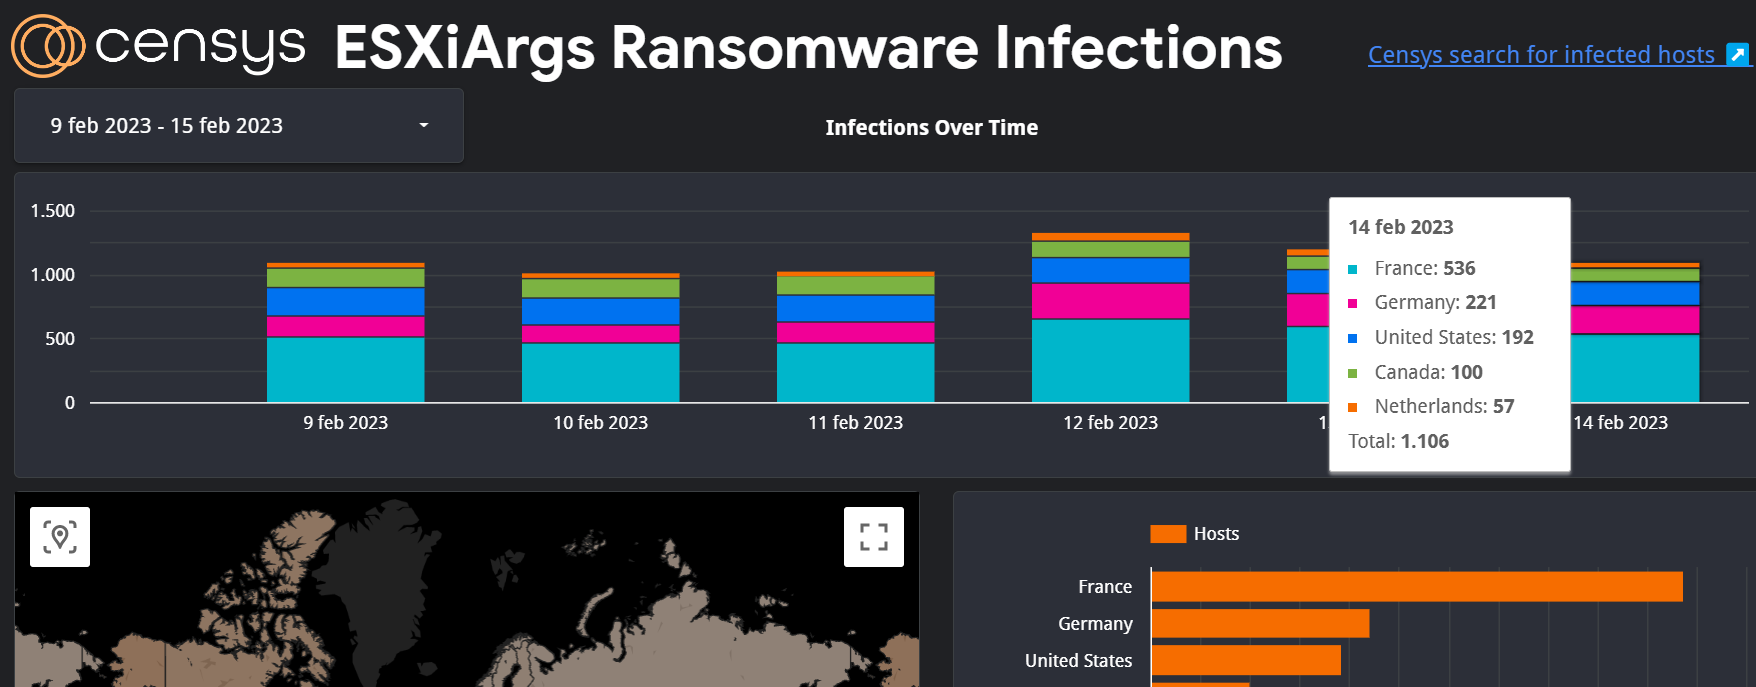
ESXiArgs ransomware continues to spread in Europe, most of the recent infections were observed in France, Germany, the Netherlands, the UK, and Ukraine Researchers from Censys reported that more than 500 hosts have been infected in a new wave of ESXiArgs ransomware attacks, most of which are in France, Germany, the Netherlands, and the U.K.. […]
 Pierluigi Paganini
February 16, 2023
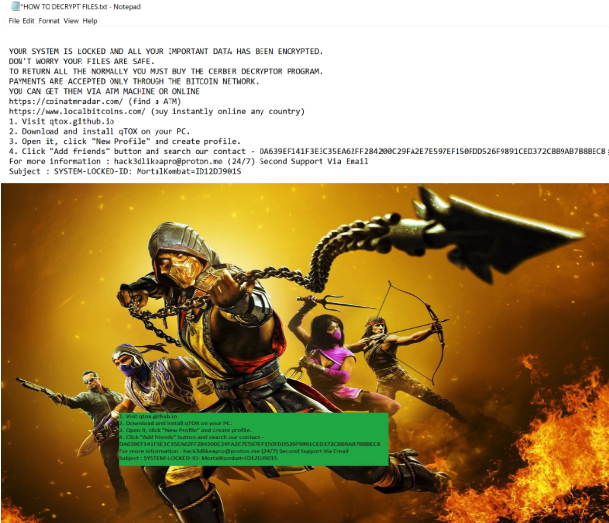
Talos researchers observed a financially motivated threat actor using a new ransomware dubbed MortalKombat and a clipper malware named Laplas. Since December 2022, Cisco Talos researchers have been observing an unidentified financially motivated threat actor deploying two new malware, the recently discovered MortalKombat ransomware and a GO variant of the Laplas Clipper malware. The threat actor […]
 Pierluigi Paganini
February 16, 2023
Hyundai and Kia car makers are releasing an emergency software update to fix a flaw that can allow stealing a car with a USB cable. Carmakers Hyundai and KIA are rolling out an emergency update for the software shipped with several car models. The update addresses a bug that can be exploited by thieves to […]
 Pierluigi Paganini
February 15, 2023
The City of Oakland has declared a local state of emergency due to the effect of the ransomware attack that hit the city on February 8, 2023. The City of Oakland disclosed last week a ransomware attack, the security breach began on February 8, 2023. In an abundance of caution, the City of Oakland has […]
 Pierluigi Paganini
February 15, 2023
Experts detected a new evasive malware dubbed Beep, it implements many anti-debugging and anti-sandbox techniques. Researchers from Minerva recently discovered a new evasive malware dubbed Beep, which implements many anti-debugging and anti-sandbox techniques. The name Beep comes from the use of techniques involved in delaying the execution through the use of the Beep API function. The experts […]
Security / September 30, 2026
Artificial Intelligence / September 30, 2026


Security / September 30, 2026


