 Pierluigi Paganini
 September 25, 2026
CARBONATO exploits exposed Docker daemons, installs an AI agent, steals API keys and spreads across networks with autonomous command execution. CARBONATO is a Docker-based botnet that has been active since at least October 2024. ThreatDown discovered the operation after finding an unauthenticated container registry exposed to the internet. The registry contained the attackers’ entire toolchain […]
 Pierluigi Paganini
September 24, 2026
Ryuk member Karen Vardanyan was sentenced to 24 months in U.S. prison after extradition from Ukraine and ordered to pay $1.2M in restitution. Karen Vardanyan, a 35-year-old Armenian citizen who went by “Maneeken” and, oddly, “Karl Lagerfeld” online, was extradited from Ukraine and sentenced to 24 months in federal prison plus three years of supervised […]
 Pierluigi Paganini
September 24, 2026
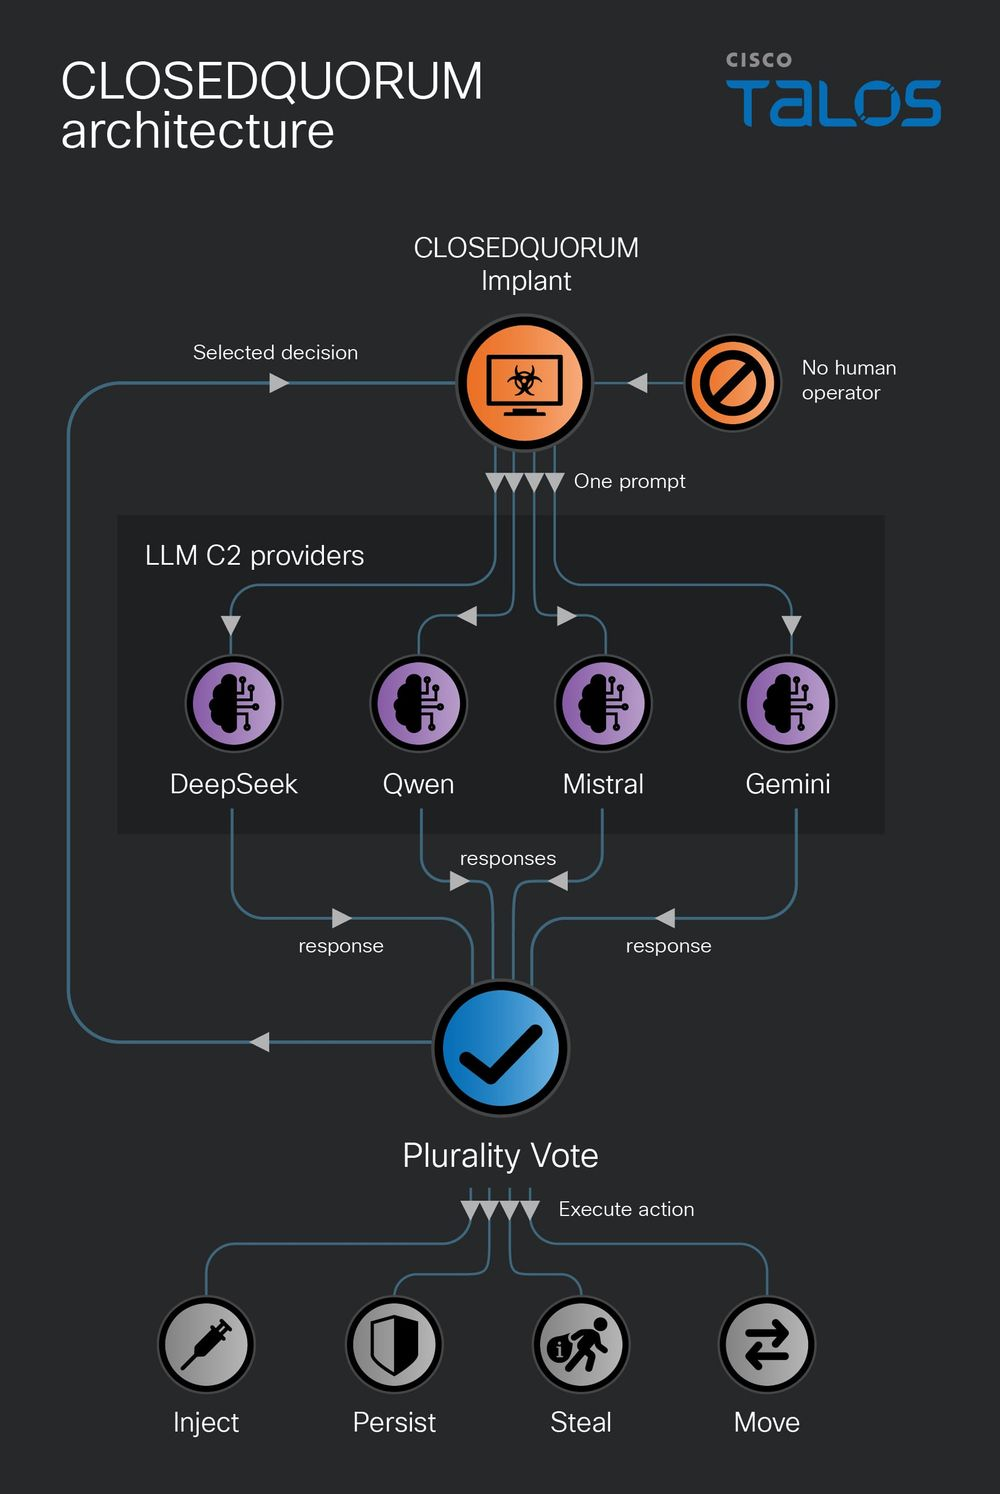
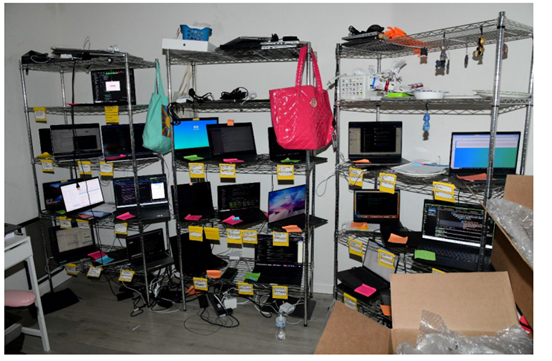
Cisco Talos finds CLOSEDQUORUM, malware that lets four commercial AI models vote on its next move, with no human operator required. Cisco Talos found malware, dubbed CLOSEDQUORUM, that holds a vote before deciding what to steal from you. Four AI models vote on its next move, without any human interaction. CLOSEDQUORUM is the first Windows […]
 Pierluigi Paganini
September 23, 2026
Attackers spoofed LastPass on GitHub, used a Microsoft-signed driver to disable 145 security products, then deployed an infostealer. Someone impersonated LastPass on GitHub, got users to download a fake authenticator, and ended up killing 145 different antivirus and EDR products using a driver that Microsoft itself had signed. That last part is the one worth […]
 Pierluigi Paganini
September 22, 2026
North Korea-linked WaterPlum runs the Contagious Interview campaign, infecting over 30,000 devices using a fake job interview. On September 18, Japan’s National Police Agency, the FBI, the US Department of Defense’s Cyber Crime Center, and intelligence agencies from Australia and Germany published a joint advisory about a group called WaterPlum, better known as Contagious Interview. […]
 Pierluigi Paganini
September 20, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Gray Rabbits and the Tale of a One-Click Backdoor Red Heron exploits Gitea n-day flaw in multinational campaign, exposing new Linux rootkit Malicious Twitch Browser Extension Exposes 30,000 Users’ OAuth Tokens to Russian Bot […]
 Pierluigi Paganini
September 20, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. Google Gemini also Broke Out of Its Test Environment AI Helps Hackers Hijack OpenAI Staff Accounts Through […]
 Pierluigi Paganini
September 18, 2026
A Brevo supply-chain attack used compromised Cloudflare access to inject malware into websites, potentially affecting over 100,000 sites. Brevo, formerly known as Sendinblue, is a French cloud-based marketing and customer communication platform whose clients include eBay, Louis Vuitton and Michelin. The company was first compromised on September 10, when attackers exploited a vulnerability in its […]
 Pierluigi Paganini
September 18, 2026
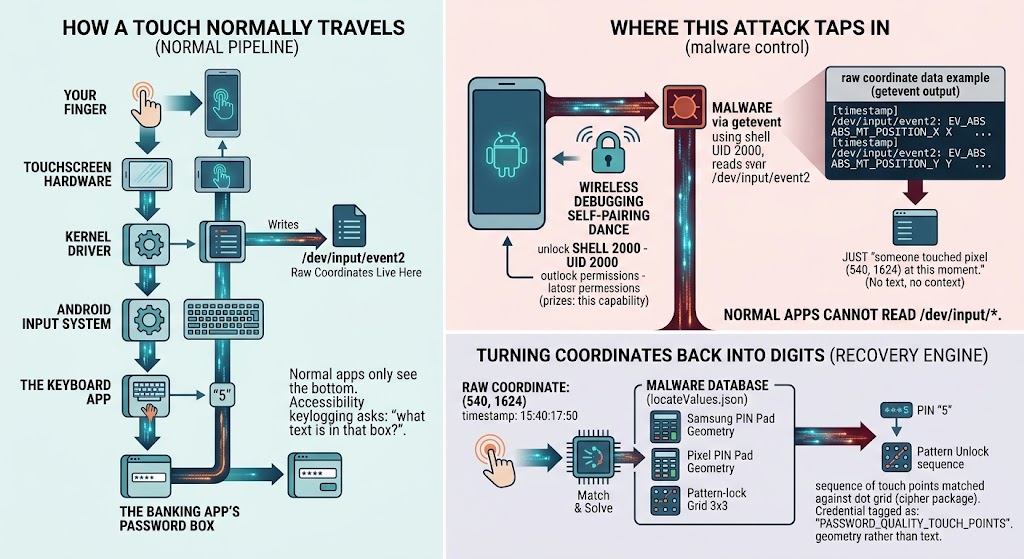
RatHat combines AI-driven screen control, Android debugging abuse and advanced credential theft to give attackers deep control of infected phones. RatHat is the new Android trojan you should know about. Zimperium researchers just published a breakdown of a strain they’ve traced to China-based operators, and what makes it different isn’t the credential theft, which is […]
 Pierluigi Paganini
September 17, 2026
UK, US, and Dutch agencies expose Chosen Brick, Iranian malware used to track and harass dissidents, journalists, and activists via Telegram. The UK, the US, and the Netherlands published a joint advisory warning about a Windows malware family, dubbed Chosen Brick, that Iran’s intelligence services use to track down dissidents, journalists, and activists, and the […]