 Pierluigi Paganini
 June 03, 2017
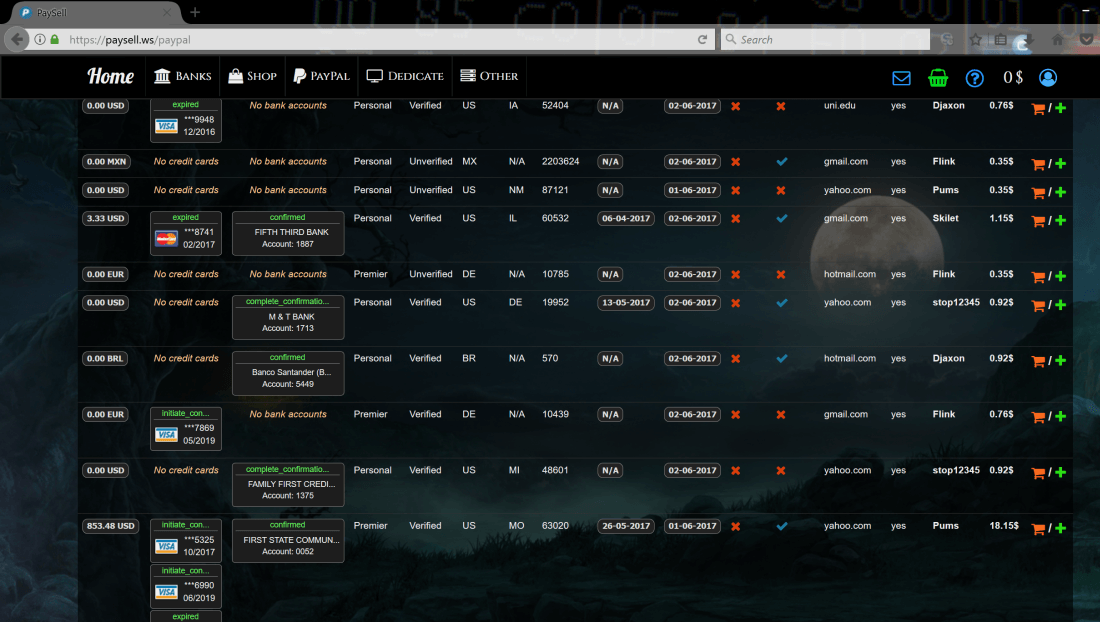
Security researchers linked Jaff ransomware campaigns to the backend infrastructure used by operators behind a black market. Security researchers at Heimdal Security who are investigating a new strain of Jaff ransomware discovered that the malware is sharing the backend infrastructure with a black market offering for sale stolen card data and account information. The black […]
 Pierluigi Paganini
June 03, 2017
Security Experts are observing a significant increase in the number of malware and hacking tools leveraging the ETERNALBLUE NSA exploit. ETERNALBLUE is the alleged NSA exploit that made the headlines with DOUBLEPULSAR in the WannaCry attack. ETERNALBLUE targets the SMBv1 protocol and it has become widely adopted in the community of malware developers. Investigations on WannaCry […]
 Pierluigi Paganini
June 02, 2017
Crowdfunding initiative aims to buy Shadow Brokers leak before threat actors will start using the hacking tools and exploits in the wild. The Shadow Brokers hacker group is going to launch a monthly subscription model for its data dumps, 0-Day Exploit Subscriptions goes for (100 Zcash), approximately $24,450 per month. The hacking tools and exploits that will […]
 Pierluigi Paganini
June 02, 2017
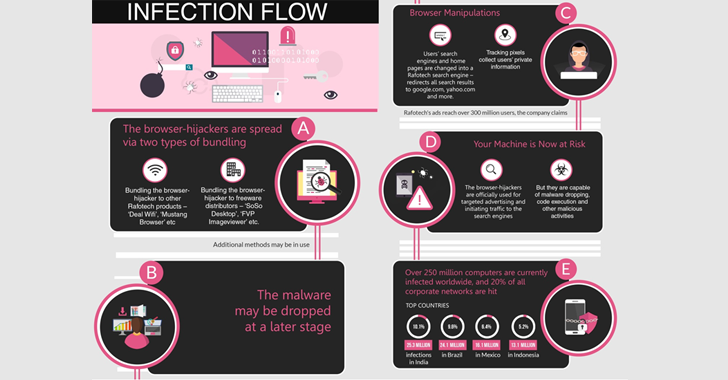
Check Point have discovered a massive malware campaign spreading the Fireball malware, it has already infected more than 250 million computers worldwide Security researchers at Check Point have discovered a massive malware campaign spreading the Fireball malware. The malicious code has already infected more than 250 million computers worldwide running both Windows and Mac OS. […]
 Pierluigi Paganini
May 30, 2017
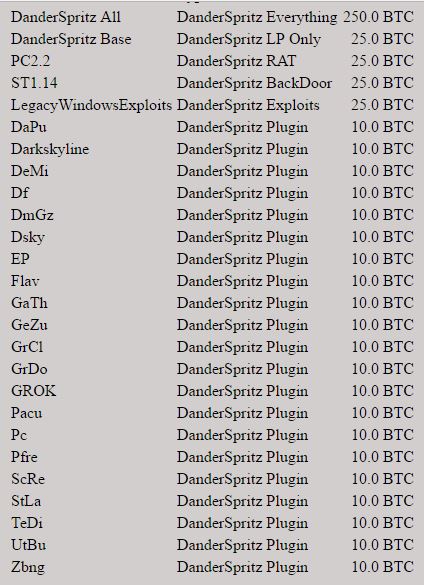
Shadow Brokers is going to launch a monthly subscription model for its data dumps, 0-Day Exploit Subscriptions goes for $21,000 per month. A couple of weeks ago, while security experts were debating about WannaCry ransomware and the NSA exploits it used, the Shadow Brokers group revealed its plan to sell off new exploits every month starting from June. […]
 Pierluigi Paganini
May 26, 2017
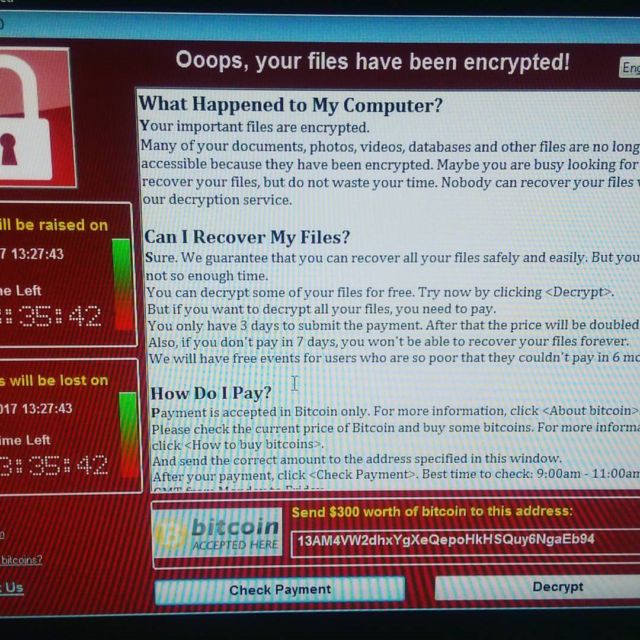
Security experts at threat intelligence firm Flashpoint conducted a linguistic analysis of dozens of ransom notes displayed by the WannaCry ransomware. Malware researchers at threat intelligence firm Flashpoint conducted a linguistic analysis of 28 ransom notes displayed by the WannaCry ransomware. Flashpoint analyzed 28 WannaCry ransom notes written in various language including Chinese (both simplified and […]
 Pierluigi Paganini
May 25, 2017
Researchers at ESET security firm have discovered that someone has released 200 master keys for the latest variants of the prominent Crysis ransomware. While security experts continue to investigate the WannaCry attack, someone has released 200 master keys for the latest variants of the prominent Crysis ransomware. The file encrypted by this version have the .wallet and […]
 Pierluigi Paganini
May 24, 2017
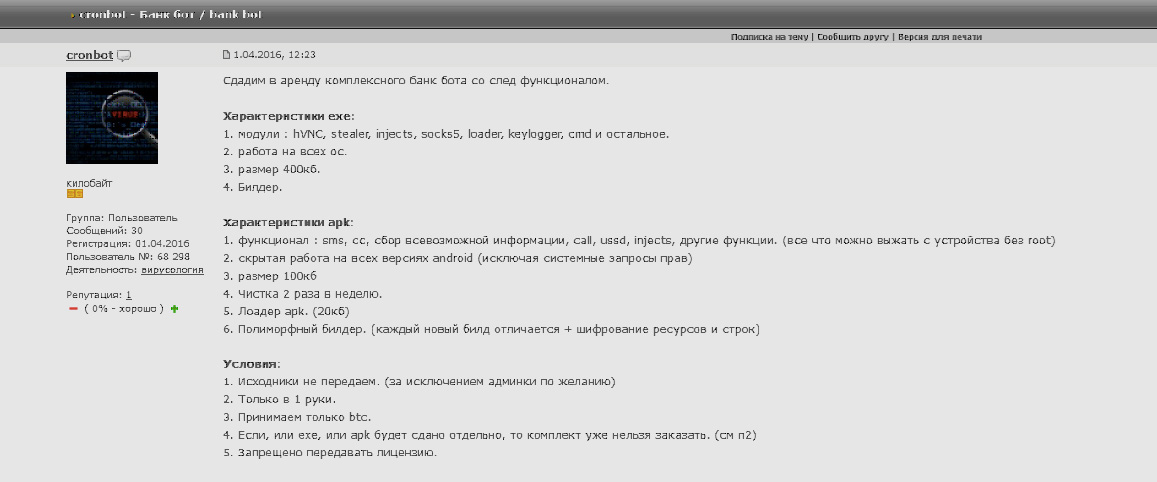
Russian authorities with the support of the security firm Group-IB dismantled the operations of the Cron gang that infected more than 1 million smartphones. Russian authorities dismantled a major criminal ring that was targeting bank accounts by using an Android malware, dubbed ‘Cron,’ that compromised more than one million Android smartphones. According to the Russian Interior […]
 Pierluigi Paganini
May 23, 2017
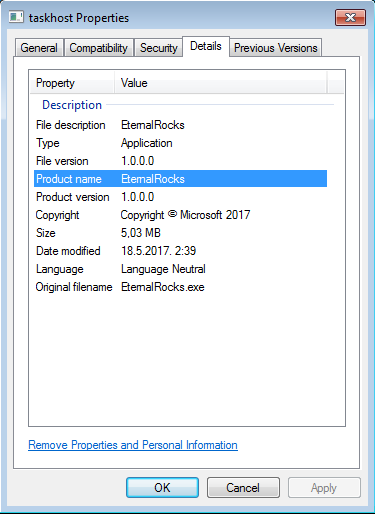
A security expert discovered a new worm, dubbed EternalRocks, that exploits the EternalBlue flaw to spread itself like WannaCry ransomware. The security expert Miroslav Stampar, a member of the Croatian Government CERT, has discovered a new worm, dubbed EternalRocks, that exploits the EternalBlue flaw in the SMB protocol to spread itself like the popular WannaCry ransomware. […]
 Pierluigi Paganini
May 22, 2017
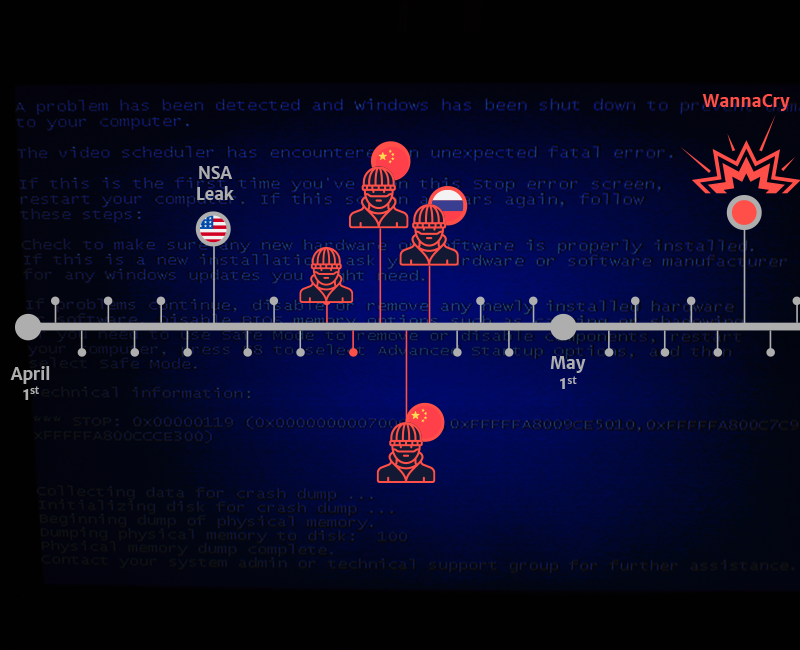
At least 3 different groups have been leveraging the NSA EternalBlue exploit weeks before the WannaCry attacks, here’s the evidence. In the last days, security experts discovered numerous attacks that have been leveraging the same EternalBlue exploit used by the notorious WannaCry ransomware. The Shadow Brokers hacker group revealed the exploit for the SMB vulnerability in April, but […]