 Pierluigi Paganini
 May 22, 2017
Experts from Talos Team discovered changes made to the Terror exploit kit (EK) that allow it to fingerprint victims and target specific vulnerabilities. Recent changes made to the Terror exploit kit (EK) allow it to fingerprint victims and target specific vulnerabilities instead of carpet bombing the victims with many exploits at the same time, Talos […]
 Pierluigi Paganini
May 21, 2017
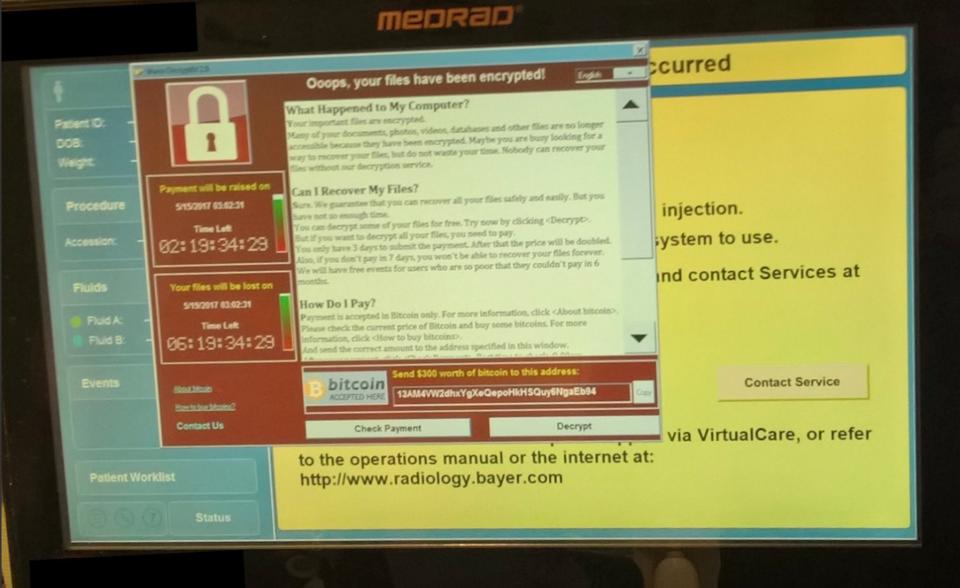
According to Forbes, the dreaded WannaCry ransomware has infected medical devices in at least two hospitals in the United States. WannaCry infected 200,000 computers across 150 countries in a matter of hours last week, it took advantage of a tool named “Eternal Blue”, originally created by the NSA, which exploited a vulnerability present inside the earlier […]
 Pierluigi Paganini
May 20, 2017
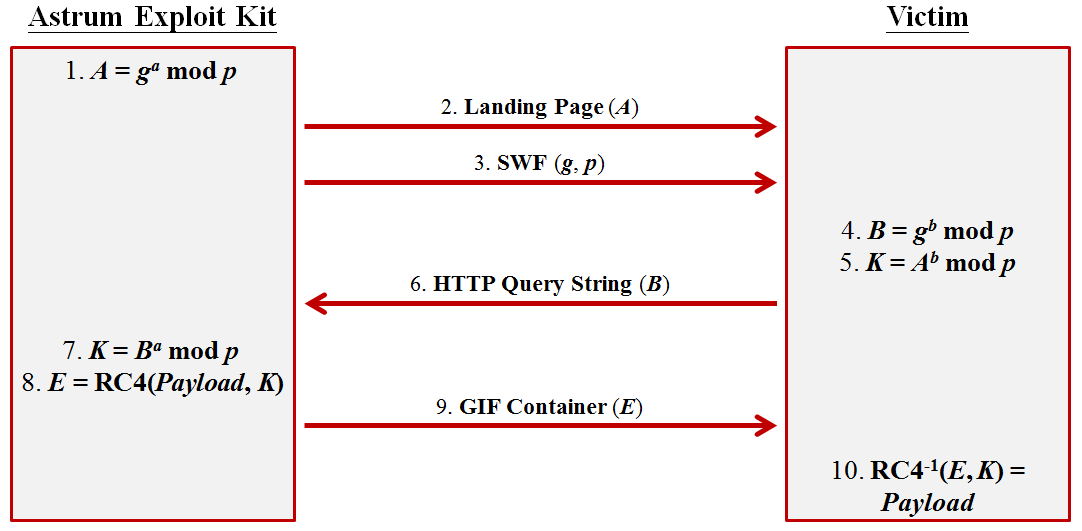
The Stegano exploit kit, also known as Astrum, continues to evolve, recently its authors adopted the Diffie-Hellman algorithm to hinder analysis. The Stegano exploit kit made was associated in the past with a massive AdGholas malvertising campaign that delivered malware, mostly Gozi and RAMNIT trojans. Experts at TrendMicro also observed the exploit kit in the Seamless malvertising campaign. “Astrum’s […]
 Pierluigi Paganini
May 20, 2017
A wave of cyber attacks against the Baltic energy networks raised concerns that foreign states could disable them in the region. A wave of “exploratory” cyber attacks targeted energy networks of the Baltic states, the NATO alliance is following with apprehension the events. Baltic attacks raised concerns that foreign states could disable the energy networks in the […]
 Pierluigi Paganini
May 20, 2017
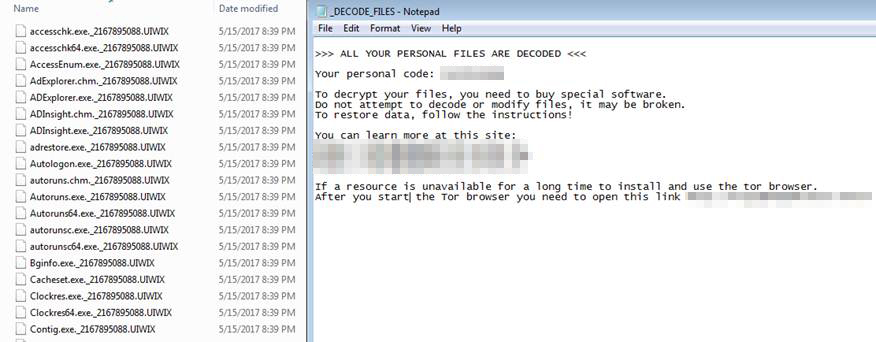
Security experts discovered a new ransomware family, dubbed UIWIX, that uses the NSA-linked EternalBlue exploit for distribution The effects of the militarization of the cyberspace are dangerous and unpredictable. A malicious code developed by a government could create serious problems for the Internet users, the recent WannaCry massive attack demonstrates it that used the EternalBlue Exploit to […]
 Pierluigi Paganini
May 19, 2017
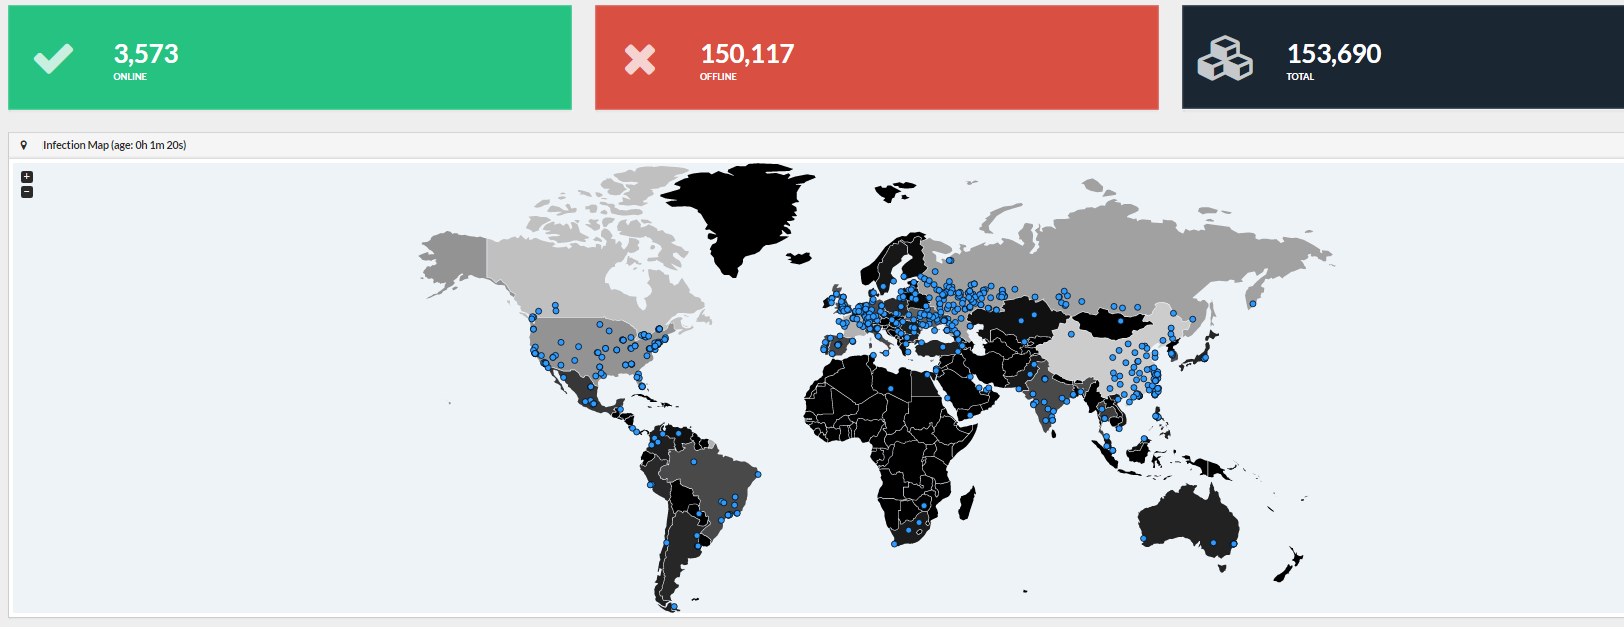
A security researcher developed a tool called wanadecrypt to restore encrypted files from Windows XP PCs infected by the WannaCry ransomware. The WannaCry ransomware made the headlines with the massive attack that hit systems worldwide during the weekend. The malicious code infected more than 200,000 computers across 150 countries in a matter of hours, it leverages the Windows […]
 Pierluigi Paganini
May 17, 2017
The tech giant Cisco announced an investigating on the potential impact of WannaCry malware on its products. Recent massive WannaCry ransomware attack highlighted the importance of patch management for any organization and Internet users. Another Tech giant, Cisco announced it is investigating the potential impact of WannaCry malware on its products, especially on its solutions that […]
 Pierluigi Paganini
May 17, 2017
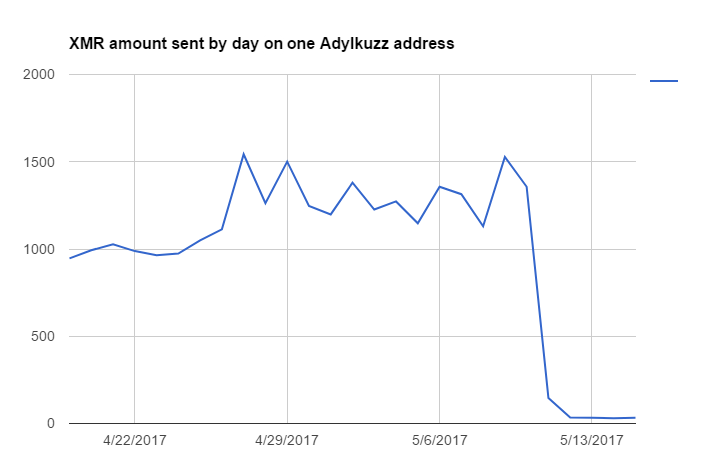
Security experts at ProofPoint security discovered that many machines can’t be infected by WannaCry because they have been already infected by Adylkuzz. The recent WannaCry ransomware attack wasn’t the first to use the NSA-linked EternalBlue and DoublePulsar hacking tools. Proofpoint researchers have discovered that the cryptocurrency miner Adylkuzz, was the first threat that used the EternalBlue exploit to trigger […]
 Pierluigi Paganini
May 16, 2017
Last Friday, a weaponized version of an NSA exploit was used to infect over two hundred thousand computers in over 150 countries with the WannaCry ransomware. In addition to government ministries and transportation infrastructure, the British National Health Service (NHS) was crippled, disrupting treatment and care for thousands of patients, and putting countless lives at […]
 Pierluigi Paganini
May 16, 2017
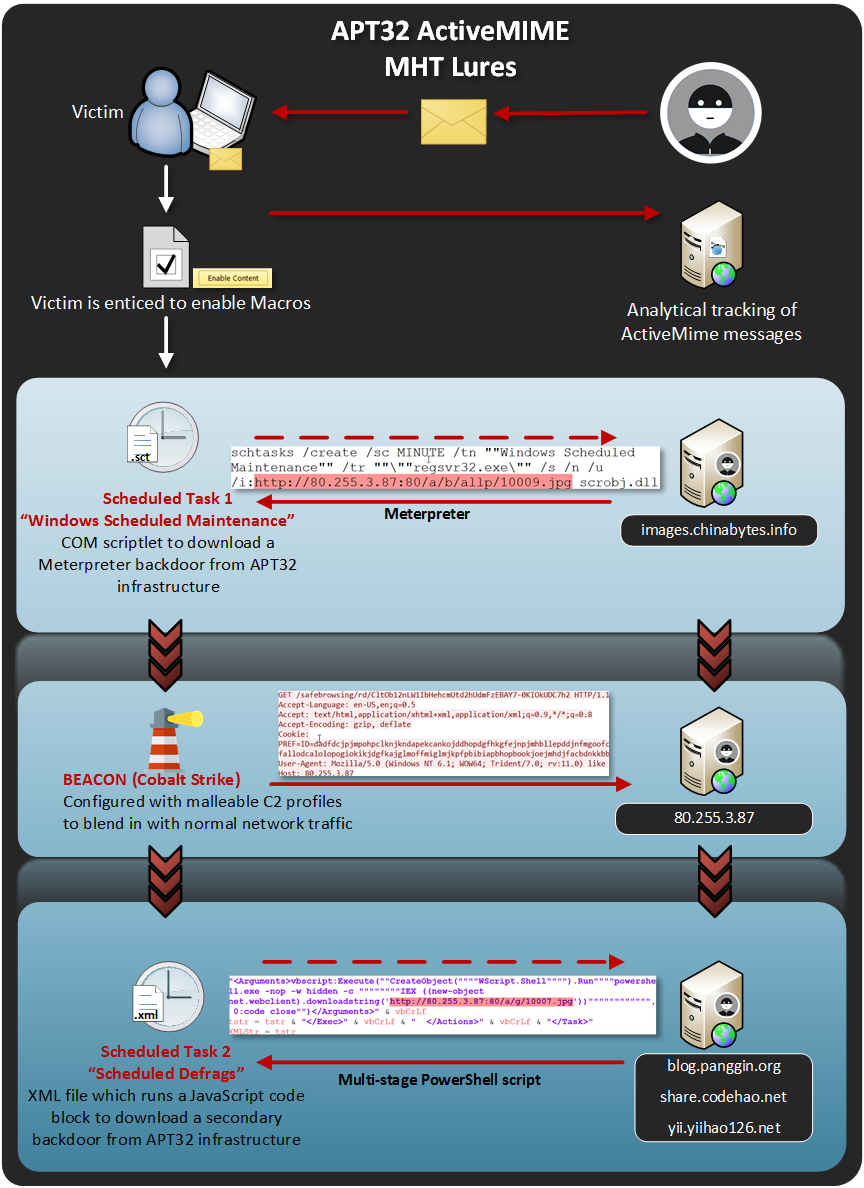
APT32 is a new APT group discovered by security experts at FireEye that is targeting Vietnamese interests around the globe. The APT32 group, also known as OceanLotus Group, has been active since at least 2013, according to the experts it is a state-sponsored hacking group. The hackers targeting organizations across multiple industries and have also targeted foreign governments, […]