 Pierluigi Paganini
 November 05, 2015
Rafael Salema Marques, a Brazilian researcher, published a PoC about the existence of Mabouia ransomware, the first ransomware that targets MAC OS X. Imagine this scenario: You received a ransom warning on your computer stating that all your personal files had been locked. In order to unlock the files, you would have to pay $500. […]
 Pierluigi Paganini
November 05, 2015
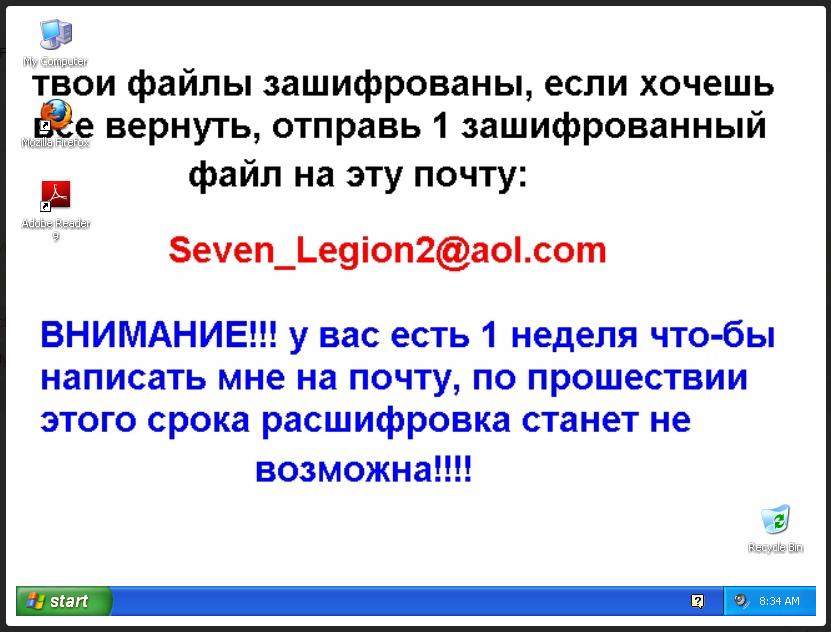
Malware researchers at Check Point Technologies have discovered a new offline ransomware that is targeting mainly Russian users. Malware researchers at Check Point Technologies have spotted a new “offline” ransomware that is targeting Russian users. The principal characteristic of this strain of malware is that it doesn’t need to communicate with a command and control […]
 Pierluigi Paganini
November 05, 2015
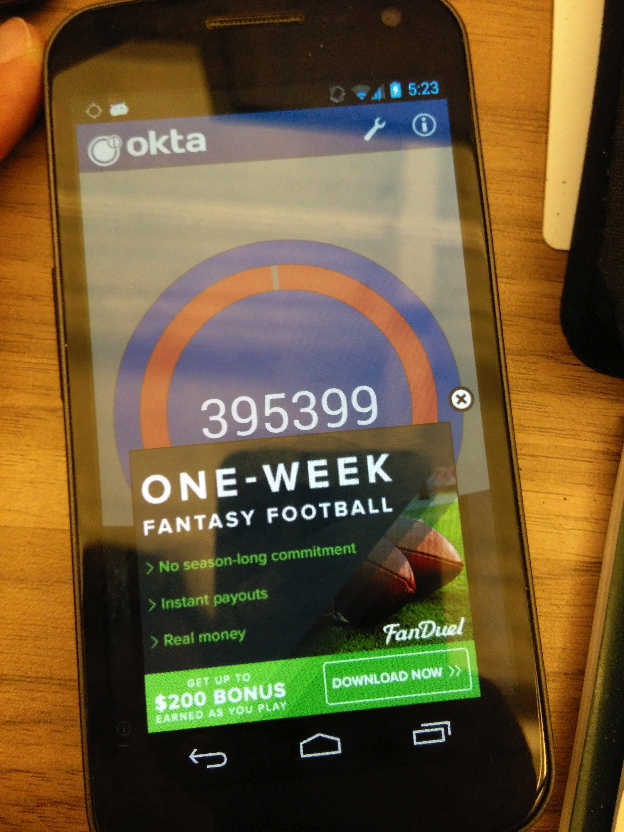
Researchers at Lookout firm have come across a new malicious adware family distributed via trojanized versions of popular Android applications. Researchers at mobile security firm Lookout have come across a new malicious adware family distributed via trojanized versions of popular Android applications. Security experts at Lookout have discovered a new strain of adware dubbed Shuanet, which is distributed via […]
 Pierluigi Paganini
November 04, 2015
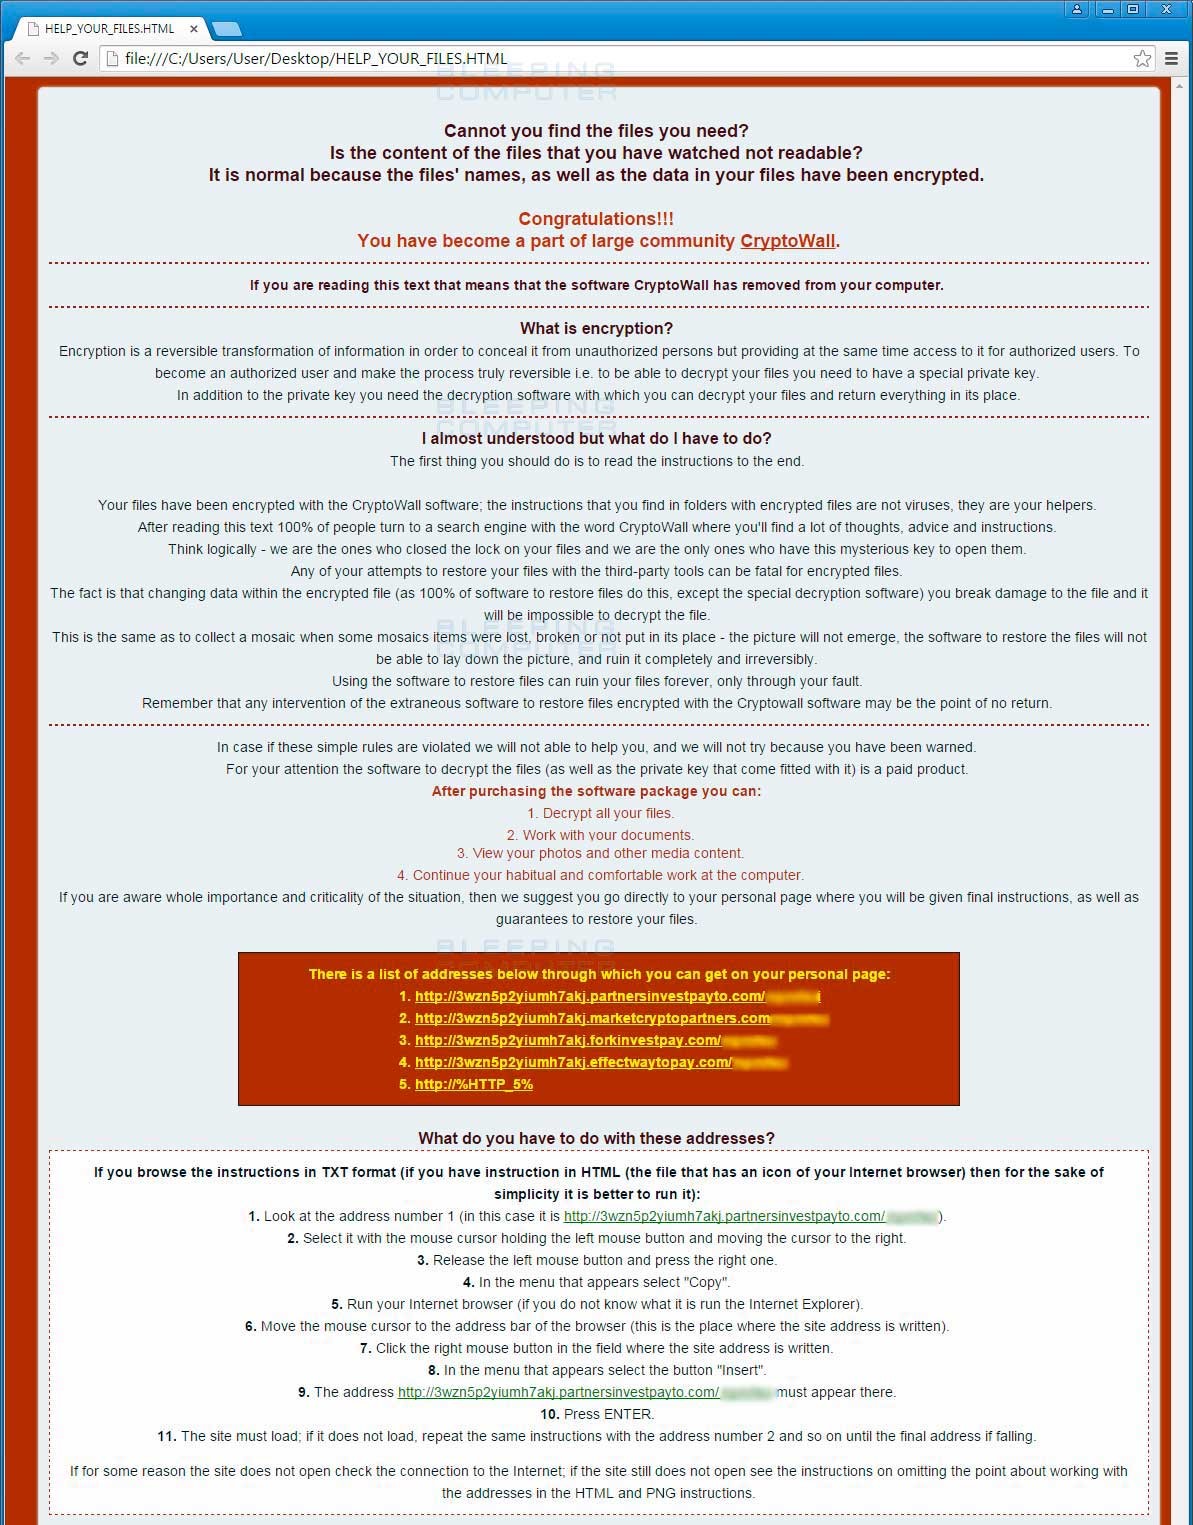
The fourth member of the CryptoWall family of ransomware, CryptoWall 4.0, has just been released, complete with new features and a brand new look. We recently reported that CryptoWall 3.0 has allegedly caused over $325 million in annual damages. CryptoWall first emerged in April 2014. Its first major upgrade was dubbed CryptoWall 2.0, and first emerged in October […]
 Pierluigi Paganini
November 04, 2015
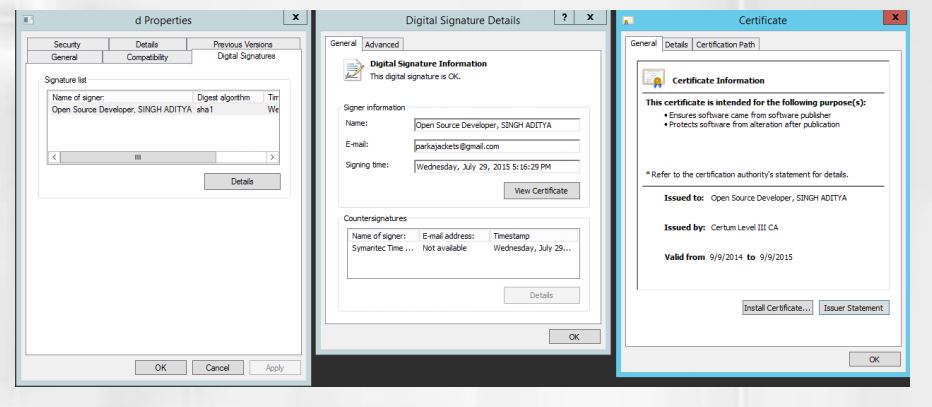
Security Experts at InfoArmor discovered GovRAT, a malware-signing-as-a-service platform that is offered to APT groups in the underground. In the past, I have explained why digital certificates are so attractive for crooks and intelligence agencies, one of the most interesting uses is the signature of malware code in order to fool antivirus. Naturally, digital certificates […]
 Pierluigi Paganini
November 03, 2015
According to a German website, there is a new strain of ransomware dubbed Chimera that also threatens to publish personal data on the Internet. A new strain of ransomware is targeting German companies, it is named Chimera and this time crooks don’t limit their extortion scheme to the file encrypting, they are also threatening victims […]
 Pierluigi Paganini
October 31, 2015
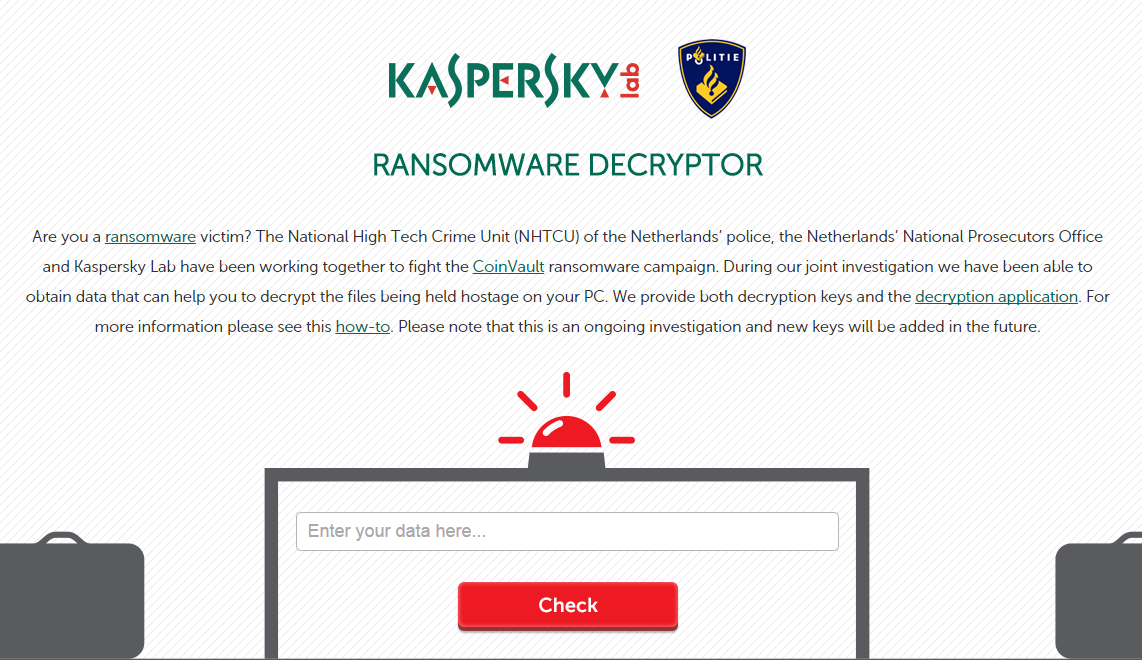
Victims of CoinVault ransomware can now rely on a new set of encryption keys added to the free CoinVault Ransomware Decryptor tool to recover their files. Every day, dozens of users ask me how to decrypt their data locked by various ransomware such as CoinVault or Bitcryptor? Now I have a good news for them, […]
 Pierluigi Paganini
October 29, 2015
Experts at Symantec have discovered a new variant of the Chikdos DDoS-Trojan that is targeting MySQL servers worldwide. There is a malware in the wild that abuses MySQL Servers for DDoS Attacks, the experts named it Chikdos. The threat was detected for the first time by the Polland CERT and according to the experts it has […]
 Pierluigi Paganini
October 27, 2015
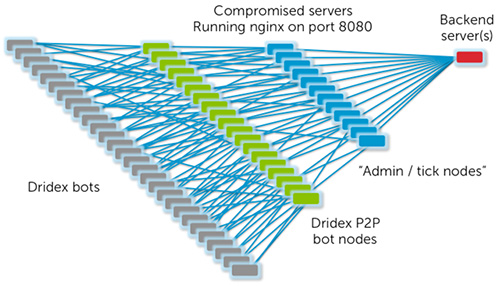
The Dridex Banking Trojan has risen again despite the recent operation conducted by law enforcement on a global scale. Spam campaign relying on the Dridex malware continues to threaten banking users across the world despite the operations conducted by law enforcement on a global scale. We left Dridex malware spreading across the Europe, in particular targeting […]
 Pierluigi Paganini
October 27, 2015
Researchers at Symantec uncovered bad actors that have been using a backdoor Trojan dubbed Duuzer to target organizations in South Korea and elsewhere. According to Symantec, threat actors have been using a data stealer Trojan dubbed Duuzer to target organizations mainly located in South Korea. The bad actors conducted targeted attacks against organizations in the manufacturing […]