 Pierluigi Paganini
 October 05, 2015
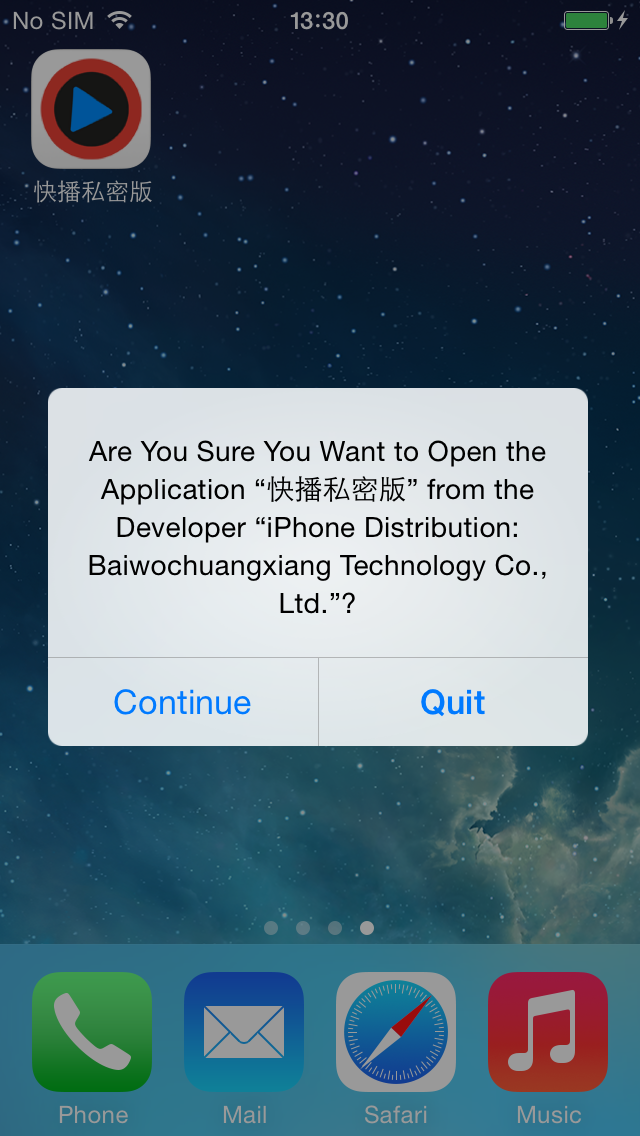
Experts at Paloalto Networks discovered a strain of Apple iOS malware dubbed YiSpecter that is able to infect both jailbroken and non-jailbroken devices. The recent XCodeGhost attack suffered by Apple demonstrated that nobody is completely secure from malware-based attacks. Now security researchers at PaloAlto Networks have discovered a new malware dubbed YiSpecter that they sustain is able to […]
 Pierluigi Paganini
October 04, 2015
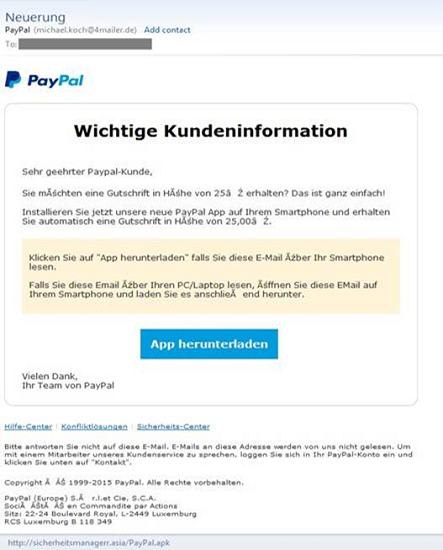
Security experts at Trend Micro have uncovered a spam campaign spreading a bogus PayPal app to steal German users’ banking credentials. A spam campaign is targeting German Andoird users, the malicious emails impersonate PayPal trying to trick the recipient into downloading a bogus PayPal app update that hides a banking Trojan. “Mobile banking is now used by […]
 Pierluigi Paganini
October 02, 2015
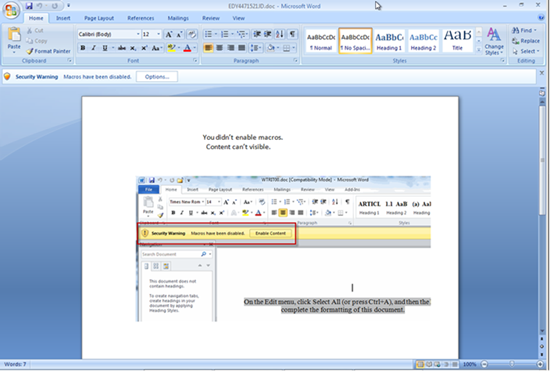
The Dridex Banking Malware is risen, security experts at Palo Alto intelligence discovered a still ongoing large phishing campaign. Once against the Dridex banking Trojan is in the headlines, this week security experts at Palo Alto intelligence discovered a still ongoing large phishing campaign. The phishing campaign is targeting victims mainly in the UK, the malicious messages […]
 Pierluigi Paganini
October 02, 2015
A new strain of malware identified by Symantec as the Vigilante malware, aka Wifatch, has infected tens of thousands of IoT devices across the world. Who is infecting thousands of IoT devices across the world, and why? A new strain of malware, identified by Symantec as Linux.Wifatch has infected tens of thousands of IoT devices across the […]
 Pierluigi Paganini
October 01, 2015
Patrick Wardle, director of research at Synack has already demonstrated another method, called Apple dylib hijacking, to bypass Apple GateKeeper. Since the introduction of the Apple Gatekeeper by MAC OSX, many researchers have focused their attention in trying to find flaws affecting it due to bypass Apple security and gain control of a device. Patrick […]
 Pierluigi Paganini
September 29, 2015
The researchers at Security Intelligence announced that Shifu banking trojan is officially spreading to the UK targeting Banks and Wealth Management Firms. A few weeks ago researchers at Security Intelligence announced the discovery of the sophisticated banking Trojan Shifu, the malicious code has been used to target the customers of more than a dozen Japanese […]
 Pierluigi Paganini
September 24, 2015
Trend Micro published a report that explains the dynamics triggered by data breaches, following data from the incidents to their offer in the Dark Web. Trend Micro published a report that explains the dynamics triggered by data breaches, following data from the incidents to their offer in the Dark Web. Stolen data is a precious commodity […]
 Pierluigi Paganini
September 19, 2015
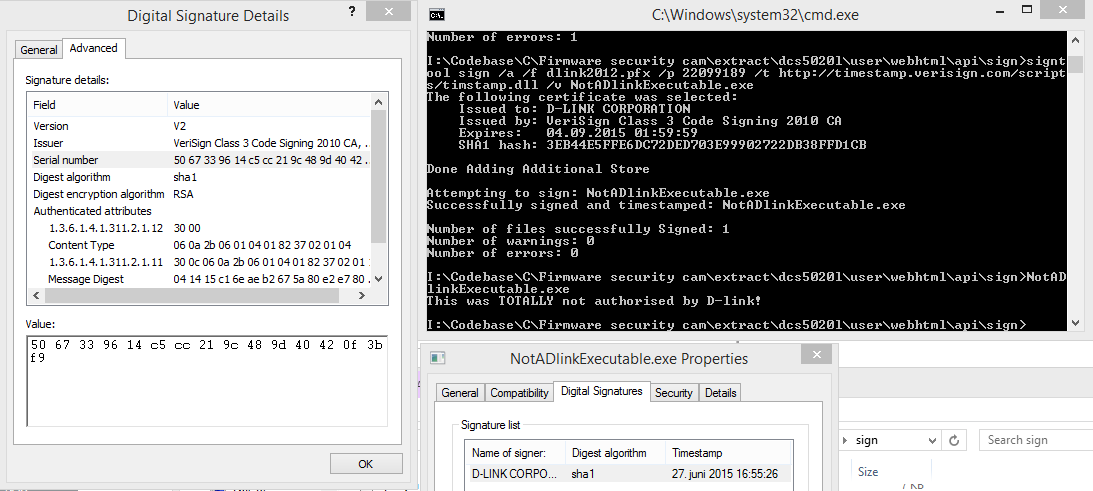
The Taiwanese networking equipment manufacturer D-Link has accidentally published its private code signing keys in the source of one of its firmware update. According to the Dutch news site Tweakers, the Taiwan-based networking equipment manufacturer D-Link accidently published its private code signing keys inside its open source firmware packages. One of the readers of the Dutch news […]
 Pierluigi Paganini
September 18, 2015
Sucuri has noticed a spike in the number of compromised websites as part of a malware campaign which relies on thousands of compromised WordPress sites. According to security experts at Sucuri, threat actors have hijacked thousands of websites running the WordPress CMS to serve malware. The technique is not new, legitimate compromised websites host malicious […]
 Pierluigi Paganini
September 18, 2015
Security experts at Doctor Web have discovered a new PoS Trojan dubbed MWZLesson that borrows code from other popular malicious software. Security experts at Dr. Web have discovered a new PoS Trojan that was designed by mixing code from other malware. The new PoS Trojan, dubbed Trojan.MWZLesson, was designed reusing the code of other popular malware, including the Dexter PoS […]