


 Pierluigi Paganini
 April 02, 2014
A security researcher reported to Tesla company a series of security issues related with S model that could be exploited to locate and unlock the vehicles. Hackers are able to remotely locate or unlock the Tesla Motors electric vehicles, the news is curious but it isn’t a novelty. Car hacking was largely discussed in the last […]
 Pierluigi Paganini
April 01, 2014
Israeli researcher Danor Cohen has discovered a security flaw in WinRAR, IntelCrawler confirmed was exploited in cyber espionage campaign. WinRAR is a popular shareware file archiver and data compression utility, as usual these applications are targeted by hackers because their penetration level. Recently the Israeli researcher Danor Cohen has discovered that a security flaw in WinRAR is being exploited in a series […]
 Pierluigi Paganini
March 30, 2014
GCHQ infiltrated German firms while NSA obtained a court order to spy on Germany and collected information about the chancellor in a special database. A new report published by Der Spiegel agency based on the document leaked by Edward Snowden has revealed that the National Security Agency (NSA) and the British Government Communications Headquarters (GCHQ) spied on private […]
 Pierluigi Paganini
March 30, 2014
Experts at Lookout Mobile Security have discovered that cyber criminals are spreading Coinkrypt malware to use victim’s mobile to mine digital currencies. Security experts at Lookout Mobile Security firm have discovered that cyber criminals are adopting Coinkrypt malware to use victim’s mobile phone to mine digital currencies. In many cases we discussed of the raise for criminal activities that […]
 Pierluigi Paganini
March 29, 2014
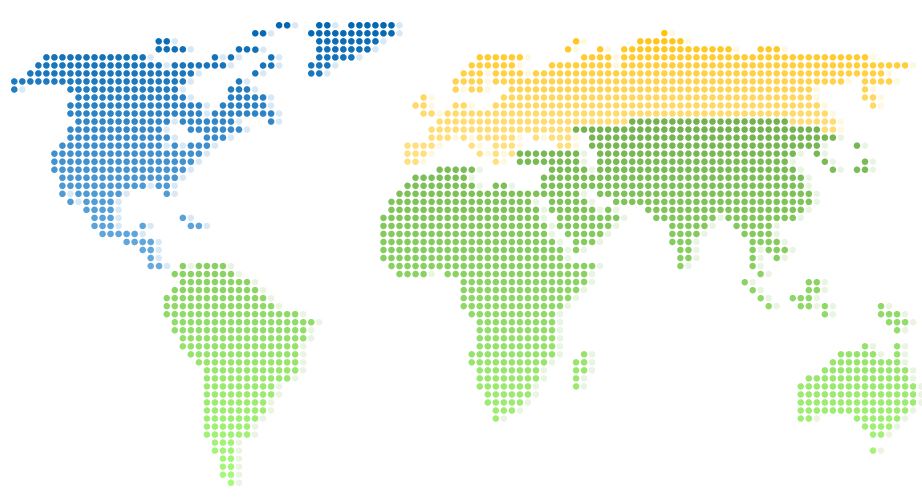
The Global Threat Intelligence Report (GTIR) addresses the security challenges of organizations globally analyzing 3 billion worldwide attacks occurred in 2013. The NTT Innovation Institute has released the new Global Threat Intelligence Report (GTIR), a document structured to raise awareness of the rapidly evolving global threat landscape. The GTIR was based on threat intelligence and attack data from […]
 Pierluigi Paganini
March 28, 2014
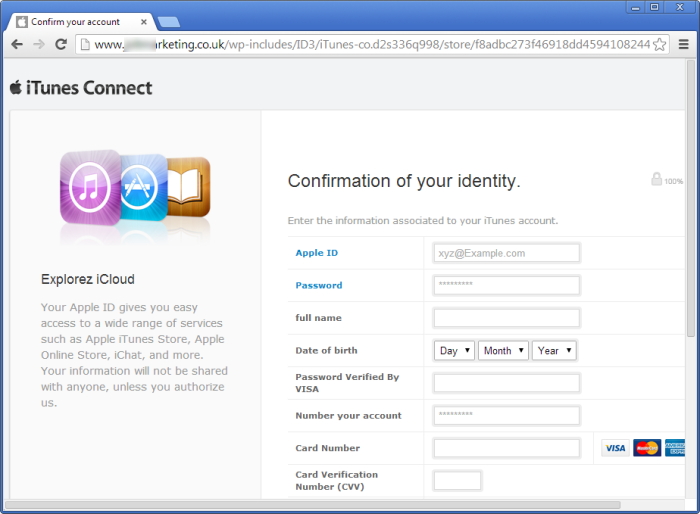
More than 12,000 phishing sites analyzed by Netcraft are hosted on compromised WordPress installations, the websites were used also to serve malicious code. Netcraft internet services company published a statistic which shows that nearly 12,000 WordPress instances were compromised in February, the attackers used the popular CMS to conduct phishing campaigns against targeted family of users, […]
 Pierluigi Paganini
March 27, 2014
Security experts at F-Secure have detected a new variant of Gameover ZeuS financial Trojan which is targeting recruitment websites. Zeus Trojan is probably one of the most prolific and long-lived malware, security firms have discovered in the last years numerous variant even more sophisticated. After the public release of it source code, principal security firms have […]
 Pierluigi Paganini
March 22, 2014
Security analysts at SenceCy which are monitoring the advancement of a new Zorenium Bot discovered that it is able to infect also iOS devices. Security analysts at SenceCy are monitoring the evolution for the Zorenium Bot, a new and unknown malware which has been advertised in the underground since January 2014. This is the third […]
 Pierluigi Paganini
March 20, 2014
Danchev profiling a service which proposes more than 5M harvested mobile phone numbers has discovered a fraudulent architecture used for illicit purposes. Cybercrime has targeted mobile industry more than ever, the number of attacks is on the rise and the proposal in the underground of tools and services for mobile market is rapidly growing. The […]
 Pierluigi Paganini
March 20, 2014
FireEye experts investigating on a spear-phishing campaign on an US-based financial institution discovered that common WinSpy RAT was adapted to hit Android devices. FireEye Security Researchers have recently identified a new variant of Winspy RAT that can infect users’ PC and also their Android Devices during synchronization operations. We have a long discussed about the increment for […]







