 Pierluigi Paganini
 October 11, 2022
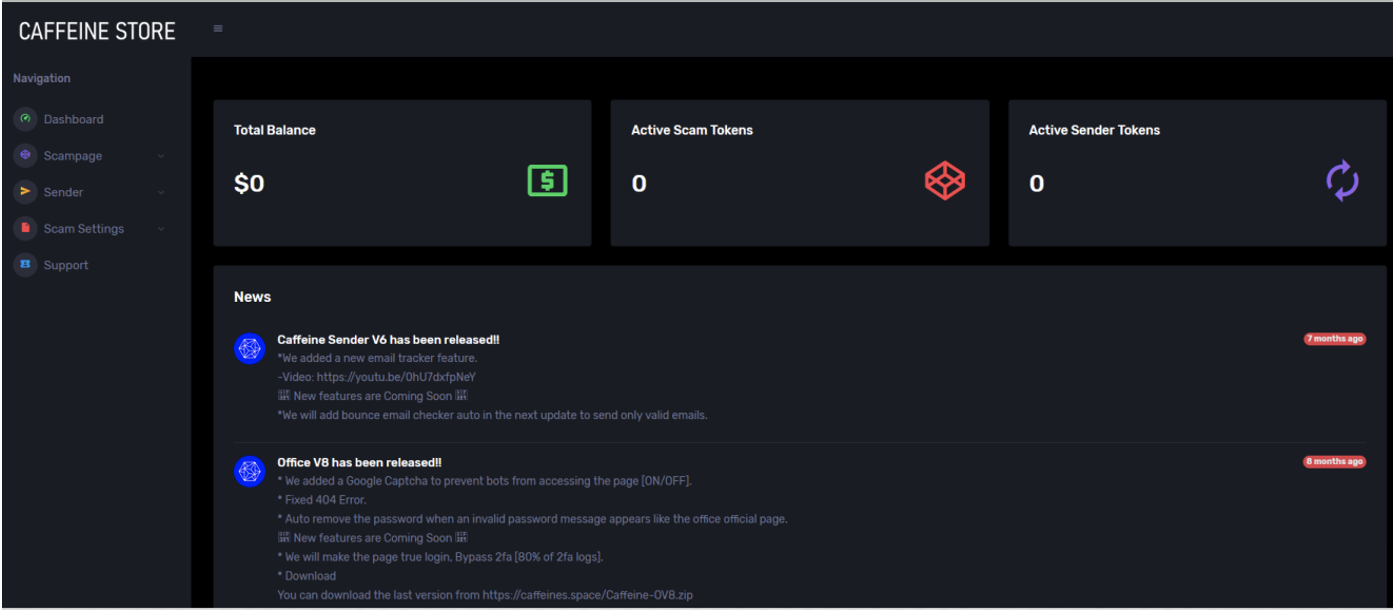
Researchers warn of a new phishing-as-a-service (PhaaS) toolkit, called Caffeine, which is being used by cybercriminals. In March 2022, Mandiant researchers discovered threat actors using a shared Phishing-as-a-Service (PhaaS) platform called Caffeine. The experts noticed that the toolkit has an intuitive interface and supports multiple features that allow customers to easily arrange phishing campaigns. The service […]
 Pierluigi Paganini
September 23, 2021
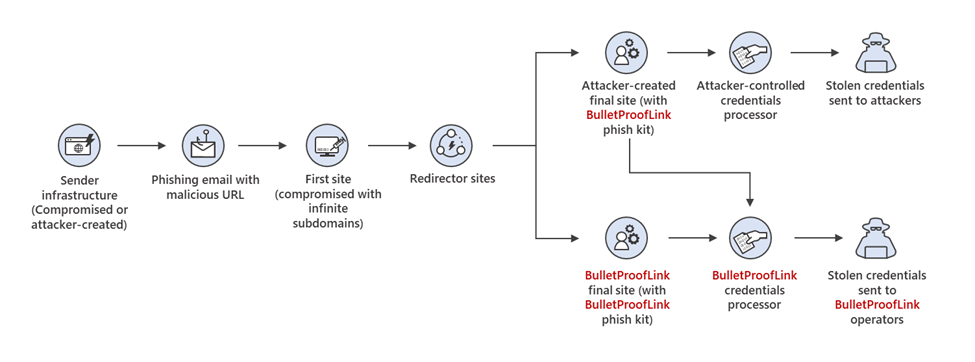
Microsoft uncovered a large-scale phishing-as-a-service operation, dubbed BulletProofLink, that enabled threat actors to easily carry out malicious campaigns. Microsoft researchers have uncovered a large-scale phishing-as-a-service (PHaaS) operation, dubbed BulletProofLink (aka Anthrax), that offers to its customers phishing kits, email templates, and hosting and automated services to carry out phishing attacks. BulletProofLink service was very cheap […]
 Pierluigi Paganini
July 16, 2017
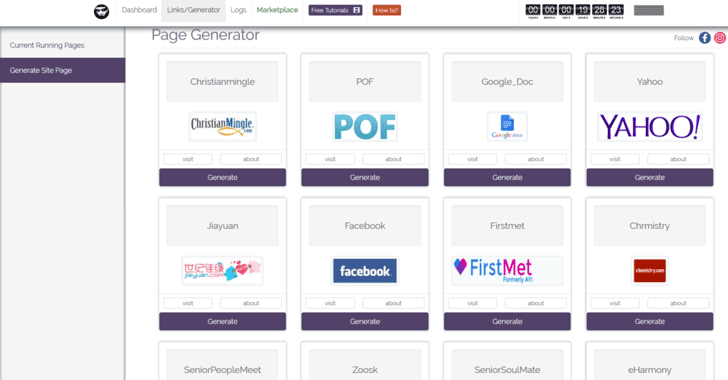
The experts from Netskope Threat Research Labs discovered the Hackshit PhaaS platform, another interesting case of crimeware-as-a-service. A few days ago, we discussed the Katyusha scanner,a powerful and fully automated SQLi vulnerability scanner discovered by researchers at security firm Recorded Future that was available for $500 in the cyber crime underground. The Katyusha scanner is just one […]