


 Pierluigi Paganini
 December 10, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. Once again thank you! · Halloware Ransomware, a new malware offered for sale on the Dark Web for Only $40 · PayPal-owned company TIO Networks data breach affects 1.6 million customers · Security Affairs newsletter Round 139 […]
 Pierluigi Paganini
December 08, 2017
#OpUSA – OpIsrael – The hacker collective Anonymous threatens cyber attacks on US Government and launched the offensive against the Israeli targets. In the last hours, the hacktivists leaked online names, emails, and passwords of Israeli public employees and shared a list of US government sites to target, calling on action against them. Anonymous leaked data belonging to only a […]
Pierluigi Paganini
December 03, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. Once again thank you! · A new Mirai variant is rapidly spreading, around 100,000 IPs running the scans in the past 60 hours · Security Affairs newsletter Round 138 – News of the week · The Cobalt […]
Pierluigi Paganini
November 26, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. Once again thank you! · A second variant of the new Cryptomix Ransomware released in a few days · Cash Converters suffered a data breach, users of the old webshop are at risk · De-authentication attack on […]
 Pierluigi Paganini
November 21, 2017
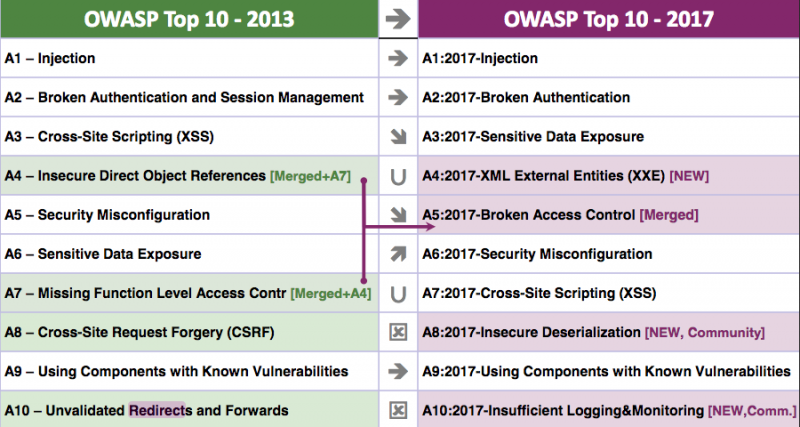
The Open Web Application Security Project (OWASP) presented the final release for the 2017 OWASP Top 10. The Open Web Application Security Project (OWASP) published the final version of the 2017 OWASP Top 10. In April, the OWASP announced the first release candidate for the 2017 OWASP Top 10, the main novelty was represented by the presence […]
Pierluigi Paganini
November 19, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. Once again thank you! · Avira spotted a new strain of the dreaded Locky Ransomware in the wild · Google introduces updates in Chrome to prevent unexpected redirects and unwanted content · Microsoft president urges a digital […]
 Pierluigi Paganini
November 15, 2017
The US clothes retailer FOREVER 21 announced it has suffered a security breach, hackers stole payment card data at some locations. Another data breach made the headlines, this time the victim is the US clothes retailer Forever 21 which announced it has suffered a security breach. According to the company, unknown hackers gain unauthorized access […]
Pierluigi Paganini
November 12, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. Once again thank you! · Flaws in IEEE P1735 electronics standard expose intellectual property · Popular Anime crunchyroll.com hijacked to distribute a keylogger · Security Affairs newsletter Round 135 – News of the week · The NIC Asia Bank […]
 Pierluigi Paganini
November 08, 2017
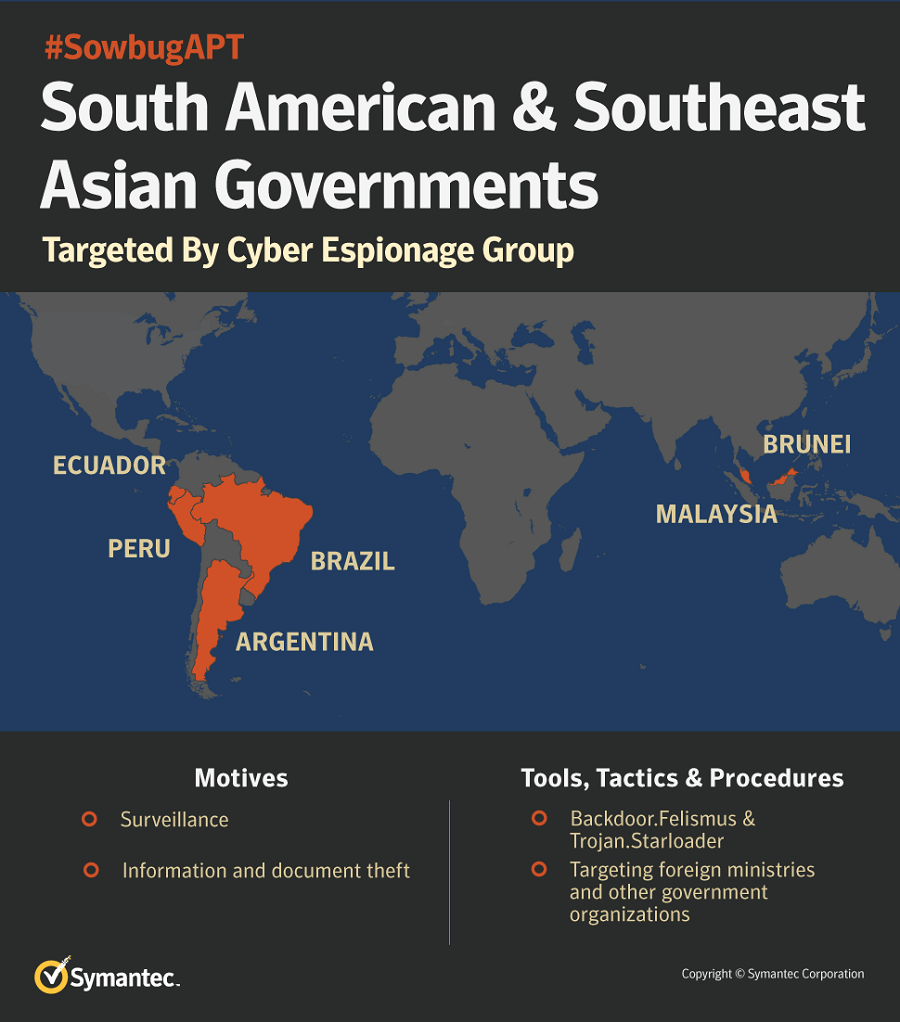
Malware researchers from Symantec have spotted a new cyber espionage APT dubbed Sowbug group that has been active at least since 2015. A new cyber espionage group dubbed Sowbug appeared in the threat landscape, according to the experts it has been active since 2015 and was involved in highly targeted attacks against a host of government organizations in […]
 Pierluigi Paganini
November 06, 2017
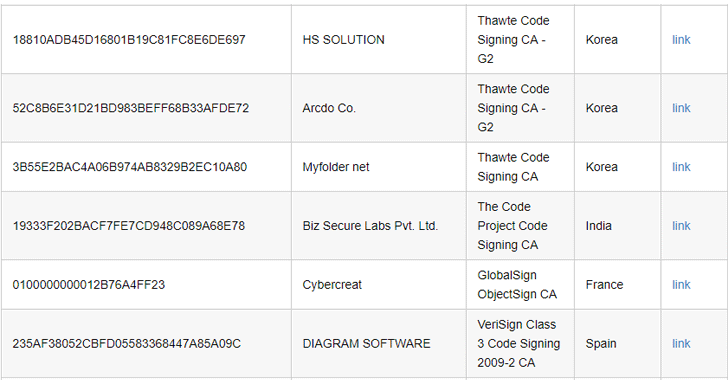
A group of researchers demonstrated that malware signed with stolen Digital code-signing certificates continues to bypass security software. A recent study conducted by the Cyber Security Research Institute (CSRI) revealed that stolen digital code-signing certificates are available for sale for anyone to purchase on the dark web for up to $1,200. Digital code-signing certificates are a precious […]



Artificial Intelligence / September 14, 2026


