


 Pierluigi Paganini
 November 05, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. Once again thank you! IOActive disclosed 2 critical flaws in global satellite telecommunications Inmarsats SATCOM systems Matrix Ransomware being distributed through malvertising Security Affairs newsletter Round 134 – News of the week Hashcat 4.0.0 now can crack […]
Pierluigi Paganini
October 29, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. Once again thank you! · A leaked document raises a doubt about NSA knew the #Krack attack since 2010 · APT28 group is rushing to exploit recent CVE-2017-11292 Flash 0-Day before users apply the patches · DHS […]
Pierluigi Paganini
October 22, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. Once again thank you! · ENISA – CTI – EU | Bonding EU Cyber Threat Intelligence · Flaws in Siemens Building Automation Controllers open to hack. Fix them asap · Hacker interview – Speaking with ICEMAN: Banks […]
 Pierluigi Paganini
October 04, 2017
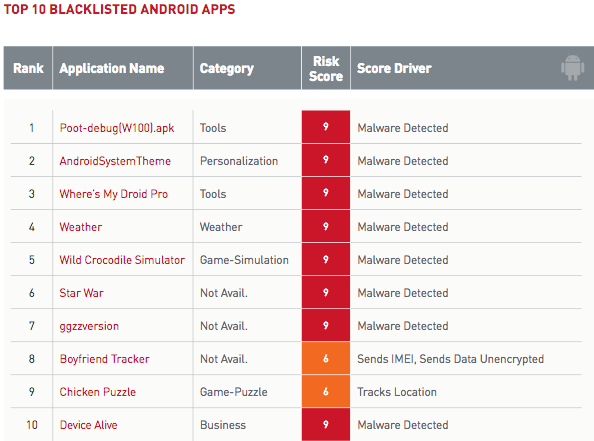
Mobile security firm Appthority published an interesting report that revealed which Android and iOS applications are most frequently blacklisted by enterprises. The company Appthority has published an interesting report that reveals which mobile apps, both Android and iOS, are most frequently blacklisted by enterprises. “The mobile ecosystem in an enterprise comprises apps from managed devices, BYOD and COPE. Appthority compiled […]
Pierluigi Paganini
October 01, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. Once again thank you! · Authors of Locky Ransomware are big fans Game of Thrones series · Massive HerbaLife spam campaign spreads a variant of Locky ransomware · Passwords and much more for 540,000 SVR Tracking accounts […]
Pierluigi Paganini
September 24, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. Once again thank you! · 400,000 UK consumers at risk after the Equifax data breach · Chrome will label Resources delivered via FTP as Not Secure · MAGENTO 2.0.16 and 2.1.9 security update fixes critical flaw in […]
Pierluigi Paganini
September 17, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. · Crooks leverage Facebook CDN servers to bypass security solutions · Mexican tax refund MoneyBack site exposed 400GB of sensitive customer data · Security Affairs newsletter Round 127 – News of the week · Apache Foundation rejects […]
 Pierluigi Paganini
September 15, 2017
Around 200,000 WordPress websites using the Display Widgets Plugin were impacted after it was updated to include malicious code. According to security firm Wordfence, roughly 200,000 WordPress websites were impacted after a plugin they were using was updated to include a backdoor. “If you have a plugin called “Display Widgets” on your WordPress website, remove it […]
 Pierluigi Paganini
September 14, 2017
The company ZERODIUM announced it will pay up to $1 million for fully working zero day exploits for Tor Browser on Tails Linux and Windows OSs. The zero-day broker Zerodium offers $1 million for Tor Browser exploits with the intent to unmask Tor users. The controversial firm will then resell the zero-day exploit for Tor […]
 Pierluigi Paganini
September 10, 2017
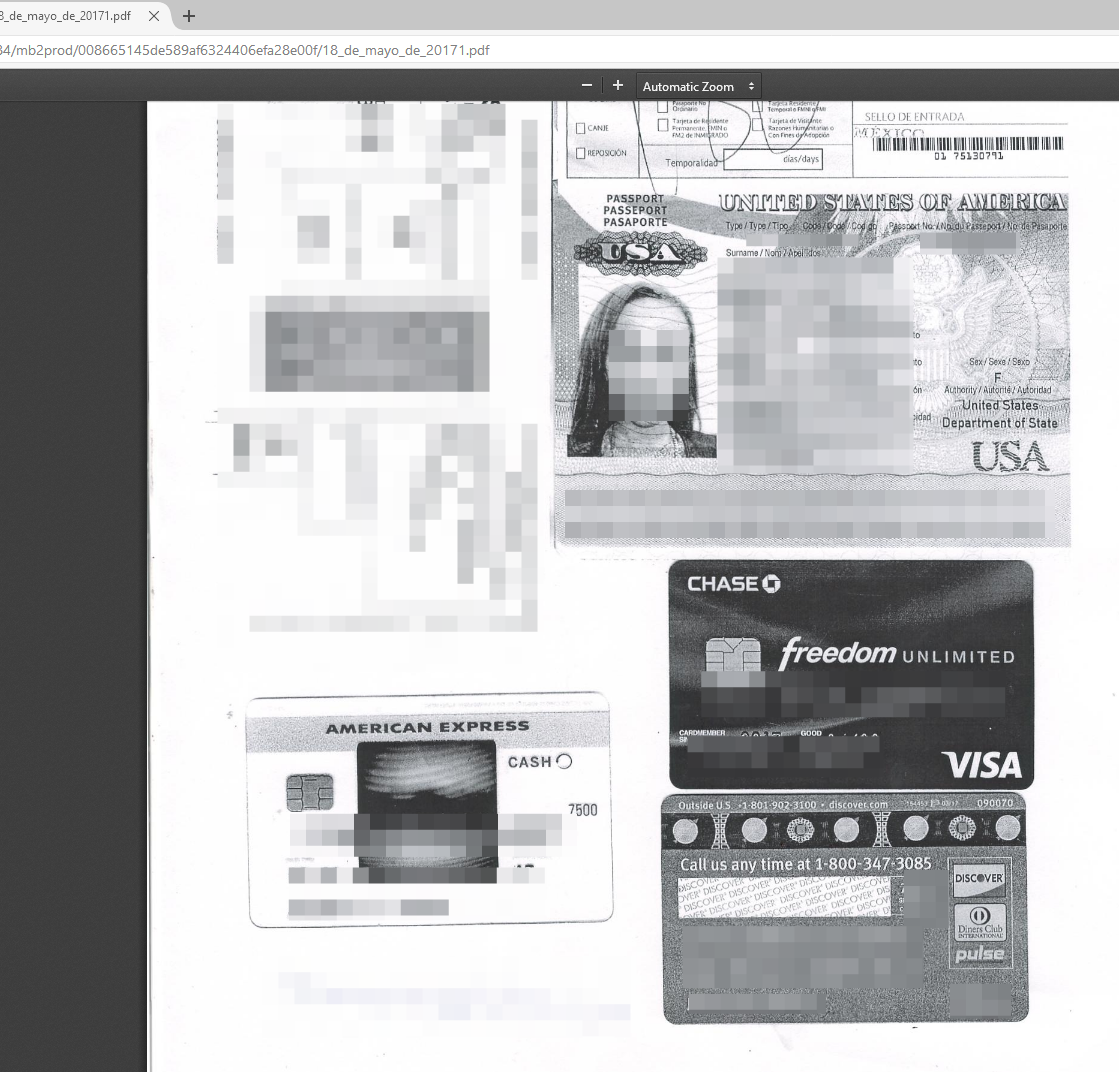
Experts from security firm Kromtech discovered the Mexican VAT refund site MoneyBack exposed 400GB of sensitive information. Another huge data leak made the headlines, experts from security firm Kromtech discovered the Mexican VAT refund site MoneyBack exposed sensitive customer information online. because of a misconfigured database. Kromtech discovered the unsecured CouchDB during a routine security audit. The Mexican VAT refund […]



Artificial Intelligence / September 14, 2026


