 Pierluigi Paganini
 June 04, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. · British Airways cancels thousands of flights, there is no evidence of cyber-attacks · Security Affairs newsletter Round 112 – News of the week · Tainted Leaks – Widespead Russias disinformation campaign hit 39 Countries · Austrian […]
Pierluigi Paganini
May 28, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. · Google is rolling out Google Play Protect, a machine-learning system to protect Android users · Medical Devices infected by WannaCry Ransomware in US hospitals · Researchers found a link between the APT3 Threat Group and the Chinese […]
 Pierluigi Paganini
May 28, 2017
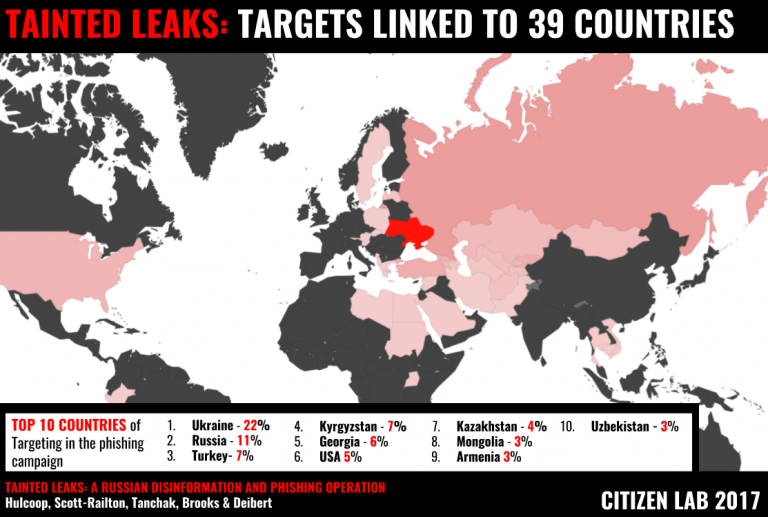
Researchers at Citizen Lab documented a Russia’s campaign of cyberespionage and disinformation that leveraged tainted leaks. According to the researchers at the Citizen Lab at the University of Toronto, a Russian disinformation campaign targeted 39 countries. The cyber attacks against the DNC were part of a larger campaign orchestrated by a nation state actor against government, […]
 Pierluigi Paganini
May 25, 2017
Researchers at ESET security firm have discovered that someone has released 200 master keys for the latest variants of the prominent Crysis ransomware. While security experts continue to investigate the WannaCry attack, someone has released 200 master keys for the latest variants of the prominent Crysis ransomware. The file encrypted by this version have the .wallet and […]
 Pierluigi Paganini
May 24, 2017
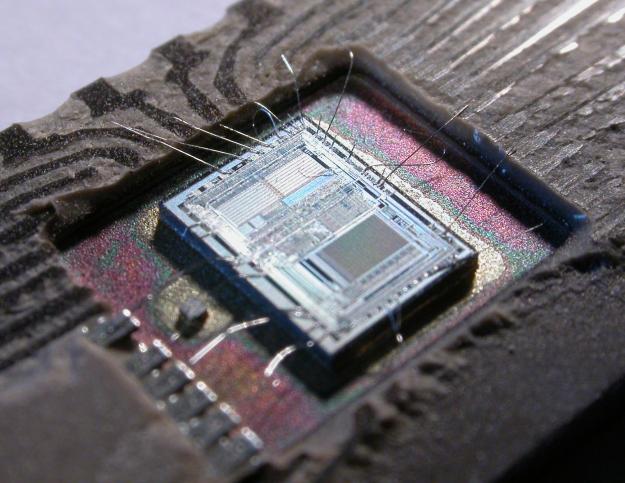
Experts found that NAND Data Storage Chips are vulnerable to malicious programs which can corrupt data and even destroy them over time. Researchers at Carnegie Mellon University, Seagate Technology and Swiss Federal Institute of Technology in Zürich have uncovered a potential flaw in the storage devices that power most cell phones, computers and big data […]
Pierluigi Paganini
May 21, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. First of all, let me inform you that at the #infosec16 SecurityAffairs was awarded as The Best European Personal Security Blog http://securityaffairs.co/wordpress/48202/breaking-news/securityaffairs-best-european-personal-security-blog.html · Experts at RedSocks analyzed the massive WannaCry Ransomware attack · Security Affairs newsletter Round 110 – […]
 Pierluigi Paganini
May 21, 2017
Security experts at threat intelligence firm Record Future have found a clear link between APT3 cyber threat group and China’s Ministry of State Security. The curtain has been pulled back a little on the Chinese Intelligence Agency intelligence gathering structure — and it includes private security contractors and the network vendor supply chain. In 2010, […]
 Pierluigi Paganini
May 17, 2017
The tech giant Cisco announced an investigating on the potential impact of WannaCry malware on its products. Recent massive WannaCry ransomware attack highlighted the importance of patch management for any organization and Internet users. Another Tech giant, Cisco announced it is investigating the potential impact of WannaCry malware on its products, especially on its solutions that […]
 Pierluigi Paganini
May 17, 2017
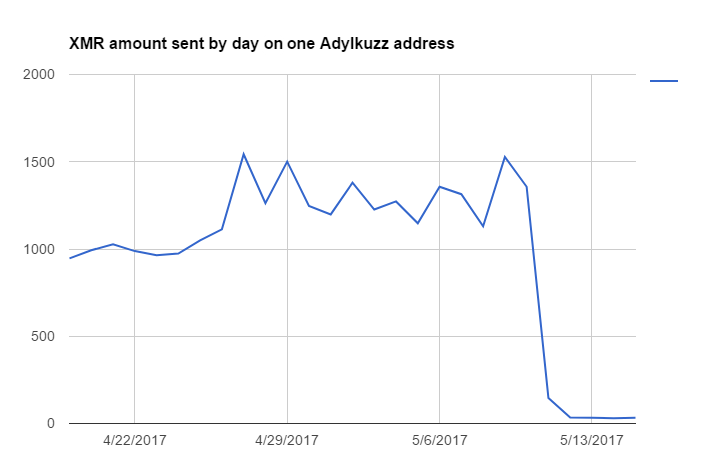
Security experts at ProofPoint security discovered that many machines can’t be infected by WannaCry because they have been already infected by Adylkuzz. The recent WannaCry ransomware attack wasn’t the first to use the NSA-linked EternalBlue and DoublePulsar hacking tools. Proofpoint researchers have discovered that the cryptocurrency miner Adylkuzz, was the first threat that used the EternalBlue exploit to trigger […]
 Pierluigi Paganini
May 16, 2017
Last Friday, a weaponized version of an NSA exploit was used to infect over two hundred thousand computers in over 150 countries with the WannaCry ransomware. In addition to government ministries and transportation infrastructure, the British National Health Service (NHS) was crippled, disrupting treatment and care for thousands of patients, and putting countless lives at […]

Security / September 15, 2026