 Pierluigi Paganini
 May 16, 2017
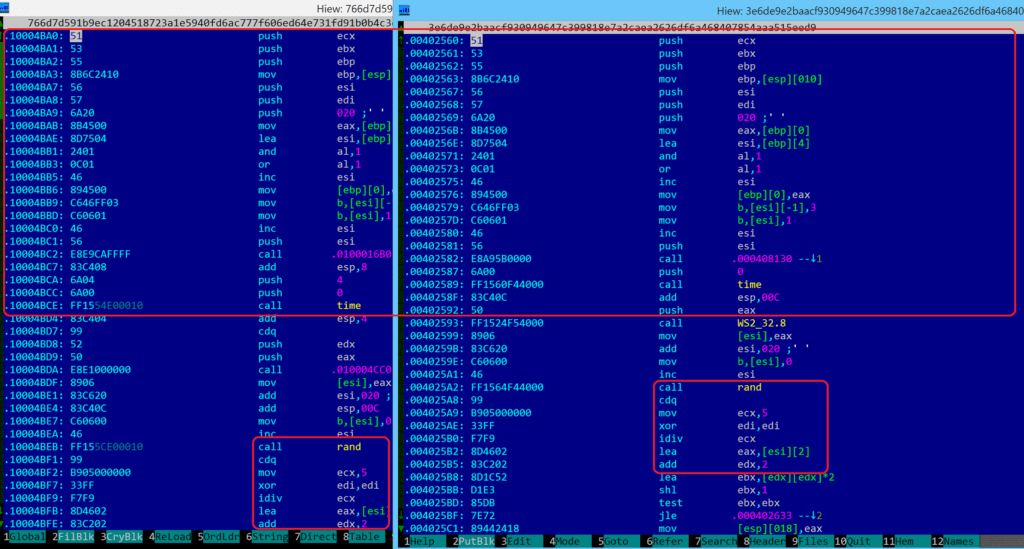
In the IT security community several experts start linking the WannaCry ransomware to the Lazarus Group due to similarities in the attack codes. The security researcher at Google Neel Mehta published a mysterious tweet using the #WannaCryptAttribution hashtag. What did he mean? 9c7c7149387a1c79679a87dd1ba755bc @ 0x402560, 0x40F598ac21c8ad899727137c4b94458d7aa8d8 @ 0x10004ba0, 0x10012AA4#WannaCryptAttribution — Neel Mehta (@neelmehta) May 15, 2017 According […]
 Pierluigi Paganini
May 14, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. First of all, let me inform you that at the #infosec16 SecurityAffairs was awarded as The Best European Personal Security Blog http://securityaffairs.co/wordpress/48202/breaking-news/securityaffairs-best-european-personal-security-blog.html · Business email compromise (BEC), the 5 billion dollar scam · European law enforcement takes down Darknet […]
 Pierluigi Paganini
May 08, 2017
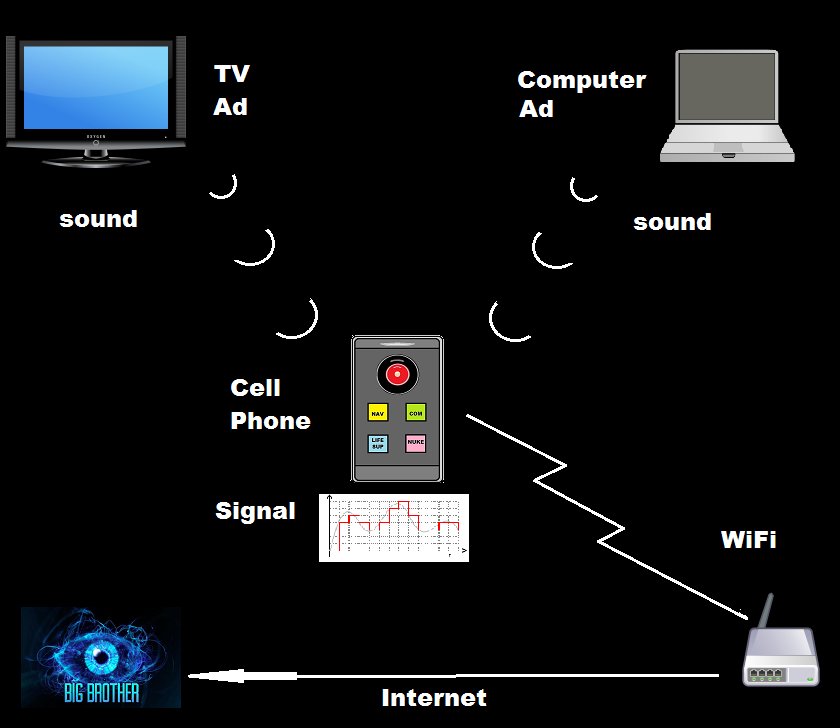
Researchers at Technische Universitat Braunschweig published a study on 200+ Android mobile apps that are listening to your life through ultrasonic beacons. Researchers at Technische Universitat Braunschweig in Germany recently published a finding that over 200 Android mobile applications are listening to your life through ultrasonic beacons. Like digital electronic vampire bats, these apps are checking […]
Pierluigi Paganini
May 07, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. First of all, let me inform you that at the #infosec16 SecurityAffairs was awarded as The Best European Personal Security Blog http://securityaffairs.co/wordpress/48202/breaking-news/securityaffairs-best-european-personal-security-blog.html · Hacker holds Netflix to ransom over new episodes of Orange Is The New Black · Lenovo […]
 Pierluigi Paganini
May 06, 2017
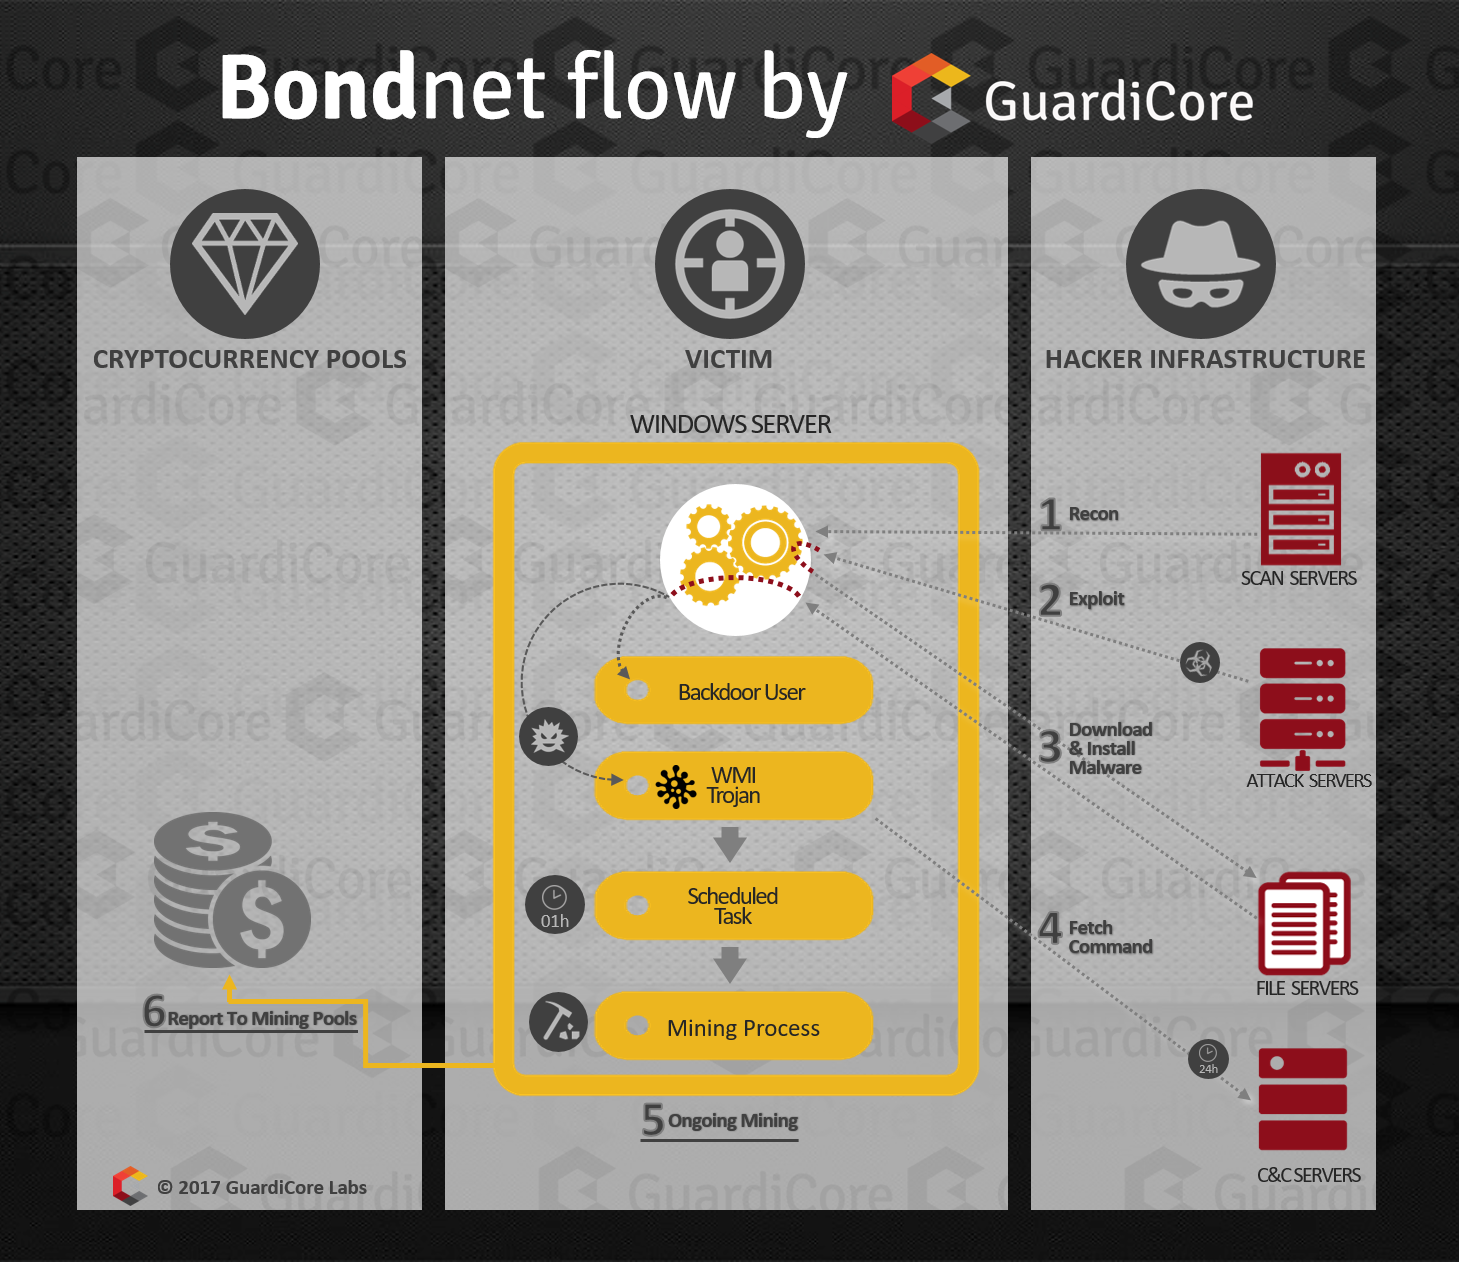
The new Bondnet botnet “Bond007.01” recently discovered coming out of China and it has infected an estimated 15,000 Windows server computers world-wide. There’s a new botnet in town and it’s named after the spy with a license to kill – James Bond. The new Bondnet botnet “Bond007.01” was discovered coming out of China by researchers […]
 Pierluigi Paganini
May 03, 2017
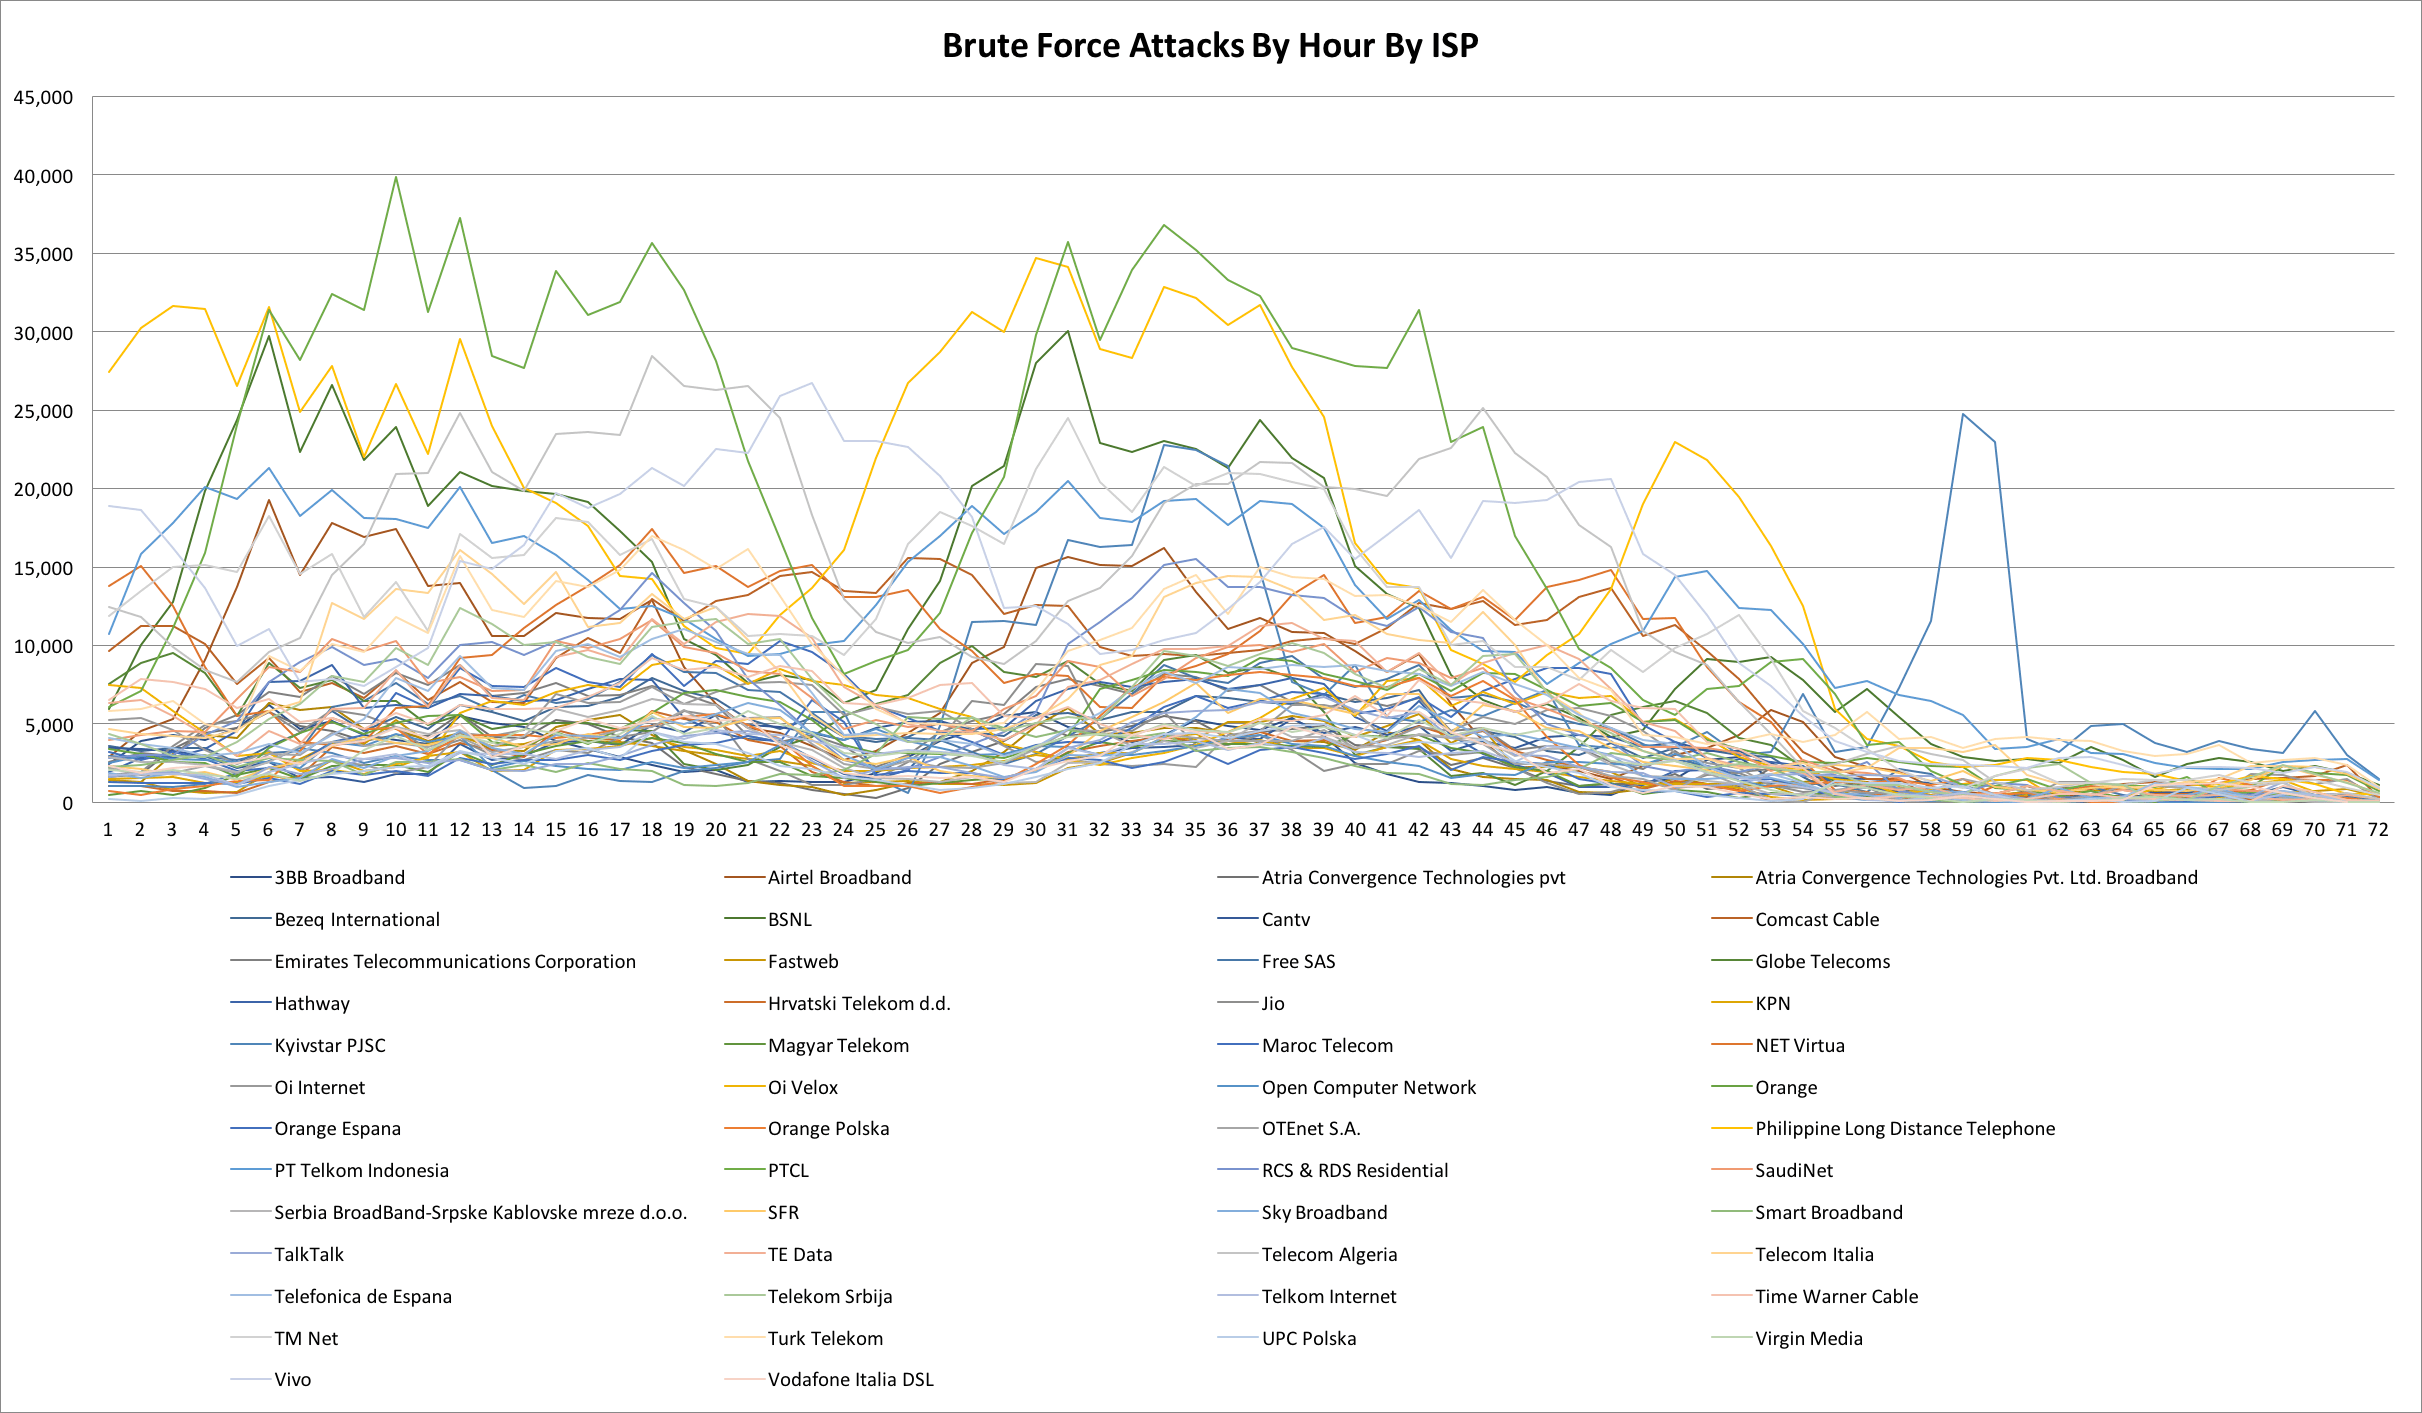
Experts from security firm WordFence reported a rapid reduction of WordPress attacks originating from hundreds of ISPs worldwide. Experts at the security firm Wordfence a few weeks ago reported that tens of thousands of flawed routers from dozens of ISPs worldwide were recruited in a botnet used to power several types of attacks against WordPress […]
 Pierluigi Paganini
May 02, 2017
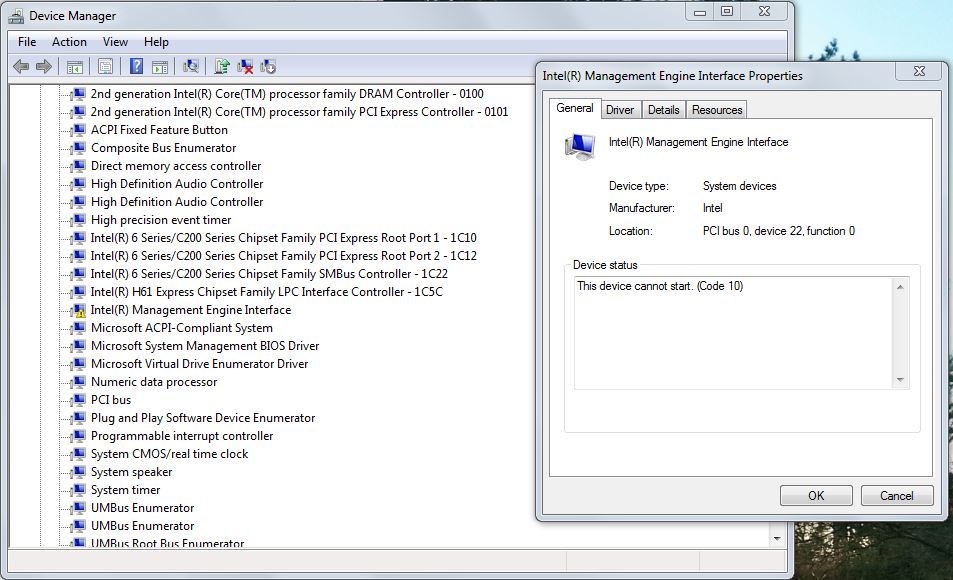
A critical remote code execution vulnerability tracked as CVE-2017-5689 in Intel Management Engine affects Intel enterprise PCs dates back 9 years. A critical remote code execution (RCE) vulnerability tracked as CVE-2017-5689 has been discovered in the remote management features implemented on computers shipped with Intel Chipset in past 9 years. The vulnerability affects the Intel Management […]
 Pierluigi Paganini
April 29, 2017
Security expert Chris Vickery reported a data breach at online trading firm AMP that exposed customer credit reports, and Social Security numbers. The popular security expert Chris Vickery has discovered a new data breach that affected the AMP online trading firm that exposed thousands of files, including credit reports, passport scans, and customer chat logs. This specific […]
 Pierluigi Paganini
April 28, 2017
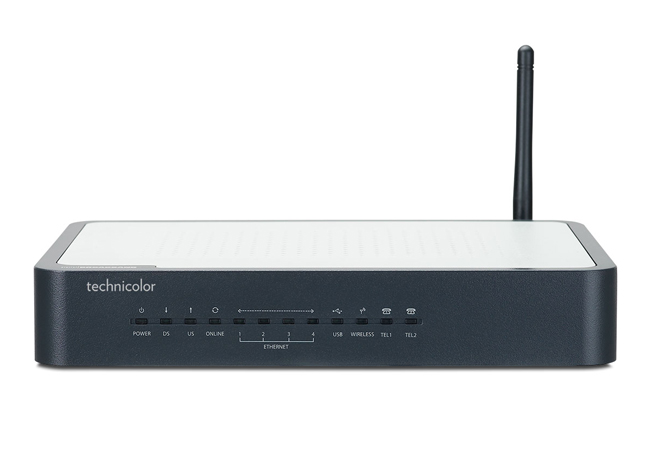
Security researchers discovered an SNMP flaw dubbed StringBleed that affects several models of Internet-connected devices. Simple Network Management Protocol (SNMP) authentication bypass affects several IoT devices, hackers could exploit the issue by simply sending random values in specific requests. The problem, dubbed StringBleed and tracked as CVE 2017-5135, was reported by the security researchers Ezequiel Fernandez and Bertin Bervis. The SNMP […]
 Pierluigi Paganini
April 27, 2017
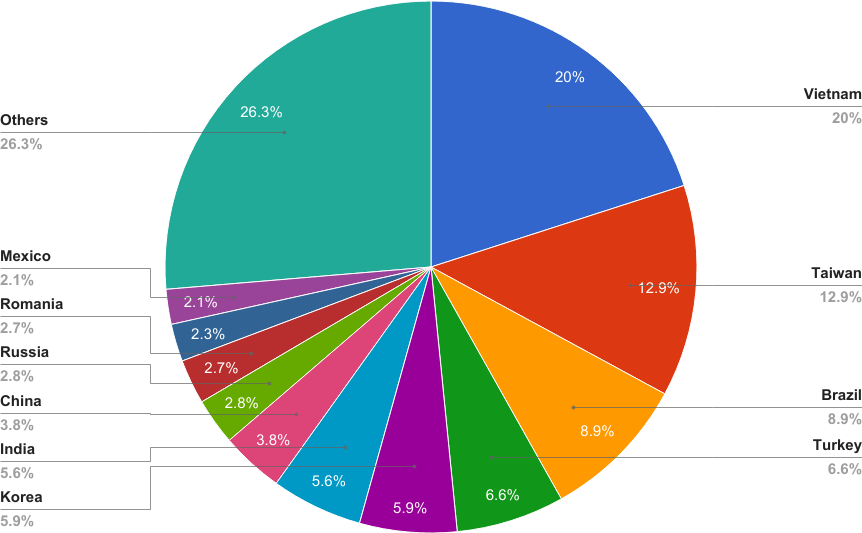
The mysterious Hajime Botnet continues to grow and reached 300,000 IoT Devices, the author also implemented a new attack method. Recently experts from Symantec spotted a new IoT botnet dubbed Hajime that is spreading quickly in the last months, mostly in Brazil and Iran. The Hajime malware was first spotted in October 2016, it implements the same mechanism […]

Security / September 15, 2026