 Pierluigi Paganini
 September 16, 2026
CenterPoint Energy confirmed a customer data breach after a hacker claimed to leak 7.49M records, including personal and billing information. CenterPoint Energy admitted on Monday that an intruder stole personal information belonging to some of its customers. The Houston-based utility, which supplies electricity and gas to about 7 million accounts across Texas, Indiana, Minnesota and […]
 Pierluigi Paganini
September 15, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Cisco Secure Email Gateway flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Cisco Secure Email Gateway flaw, tracked as CVE-2026-76461 (CVSS score of 9,8), to its Known Exploited Vulnerabilities (KEV) catalog. Cisco disclosed a critical zero-day CVE-2026-76461 this week; […]
 Pierluigi Paganini
September 15, 2026
Cisco warns of a critical zero-day in Secure Email Gateway, exploited in the wild to gain root access through malicious emails. Cisco disclosed a critical zero-day, tracked as CVE-2026-76461 (CVSS score of 9.8), affecting Secure Email Gateway appliances. The flaw can be exploited remotely without authentication. Attackers can send specially crafted emails containing malicious SQL […]
 Pierluigi Paganini
September 15, 2026
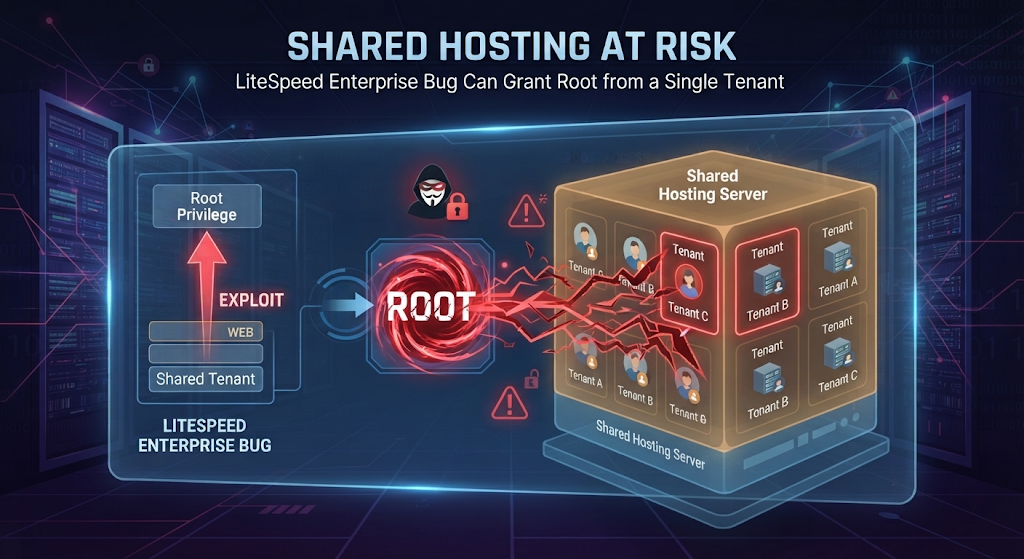
Critical LiteSpeed Enterprise flaw lets one shared hosting account gain root, bypassing CageFS; patch now to 6.3.7 via forced update. cPanel warned that a critical flaw in LiteSpeed Enterprise can let a low‑privilege website user break out of their account and gain root on the whole server. On a box where dozens or hundreds of […]
 Pierluigi Paganini
September 15, 2026
Two China-linked groups ran identical Chrome/Windows zero-day exploits against NGOs, before Chrome’s patch shipped, deploying different backdoors each. Two China-linked threat actors used the same Chrome/Windows zero-day against NGOs starting September 1, 2026, Volexity’s new report lays out the whole chain in detail. On September 1, Volexity detected a spear-phishing campaign by UTA0560 targeting several […]
 Pierluigi Paganini
September 15, 2026
A Telegram Desktop flaw let bots inject JavaScript into exported chats, enabling data theft and page manipulation. Old HTML exports remain unsafe. A vulnerability in Telegram Desktop could have turned an ordinary chat export into a serious data leak. Security researchers Denis and Aleksander Rostilov of ExPatch found a stored cross-site scripting flaw in the […]
 Pierluigi Paganini
September 15, 2026
Japan ‘s Digital Agency disclosed a VPN breach exposing 246,000 government employee records across 23 ministries. Detected June 25, publicly disclosed September 11. Japan ‘s Digital Agency disclosed that attackers exploited a vulnerability in a VPN device to access its Government Solution Service (GSS), potentially leaking personal information belonging to approximately 246,000 government employees, public […]
 Pierluigi Paganini
September 14, 2026
Frontier AI is compressing the attack lifecycle from vulnerability discovery to exploitation, forcing defenders to detect, patch and respond at machine speed. Cybersecurity has always been a race between attackers and defenders. ENISA’s latest assessment suggests that frontier AI is changing the speed of that race, and the gap between discovering a vulnerability and exploiting […]
 Pierluigi Paganini
September 14, 2026
China rejects Amodei’s AI slowdown proposal, calling it fearmongering and a US attempt to contain China’s technology sector. The debate over whether the world should slow down the development of advanced AI has quickly turned into something bigger than a technology argument. Dario Amodei, CEO of Anthropic, has called for a slower pace of development, […]
Pierluigi Paganini
September 14, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds GitLab, JFrog Artifactory, and ConnectWise ScreenConnect flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added [1, 2] the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: Two of the above vulnerabilities affect JFrog Artifactory. CVE-2026-42016 can allow attackers to bypass authorization checks and […]