 Pierluigi Paganini
 March 30, 2020
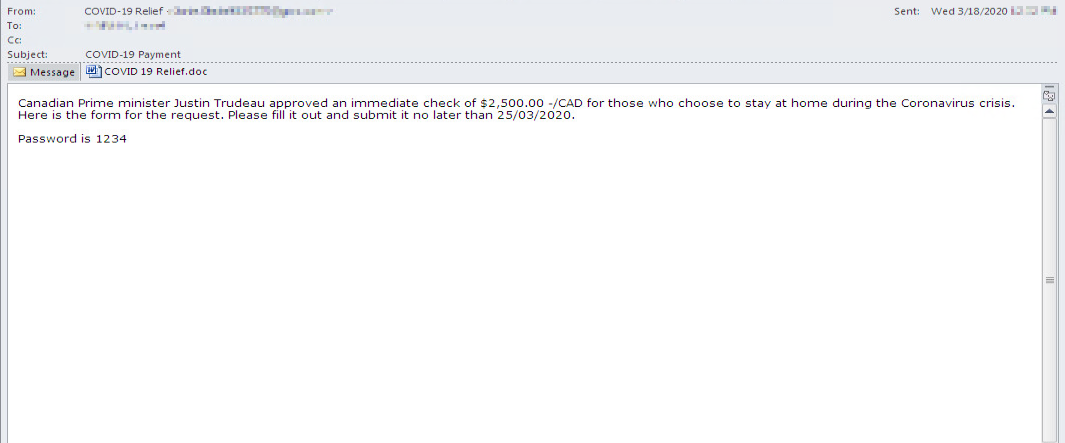
The Zeus Sphinx malware is back, operators are now spreading it exploiting the interest in the Coronavirus outbreak. The Zeus Sphinx malware is back, it was observed in a new wave of attacks attempting to exploit the interest in the Coronavirus outbreak. Experts from IBM X-Force uncovered a hacking campaign employing the Zeus Sphinx malware, […]
 Pierluigi Paganini
March 30, 2020
Voter information for 4,934,863 Georgians has been published on a hacker forum over the weekend. According to the data breach notification service Under the Breach, on Saturday a file containing voter information for more than 4.9 million Georgians, including deceased citizens, has been published on a hacking forum. Georgia has 3.7 million citizens, but the voting […]
 Pierluigi Paganini
March 30, 2020
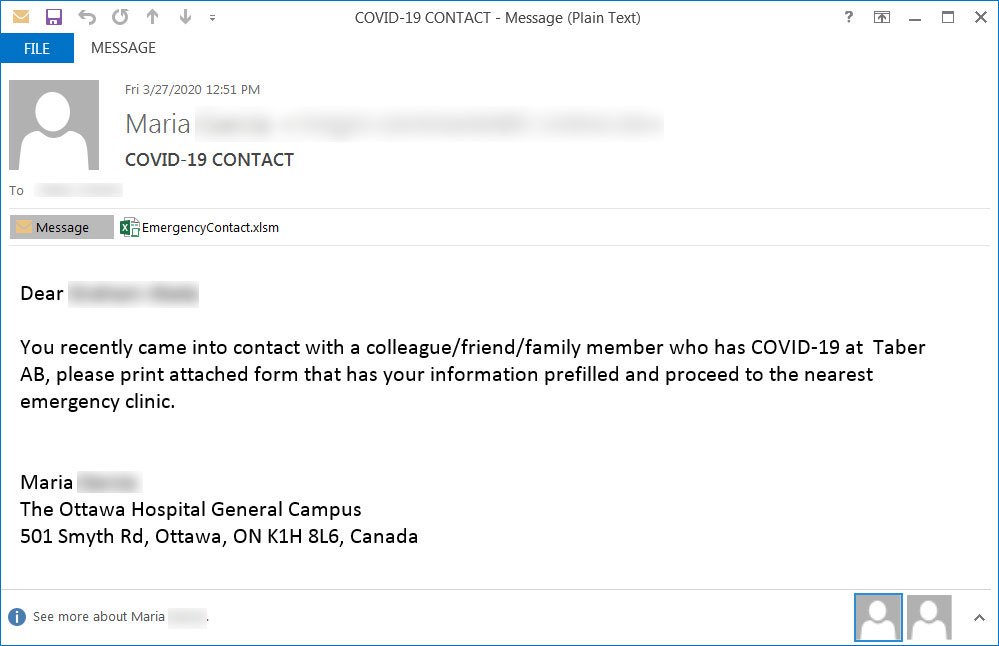
Security experts uncovered a new Coronavirus-themed phishing campaign, the messages inform recipients that they have been exposed to the virus. Experts continue to spot Coronavirus-themed attack, a new phishing campaign uses messages that pretend to be from a local hospital informing the victims they have been exposed to the virus and that they need urgently […]
 Pierluigi Paganini
March 29, 2020
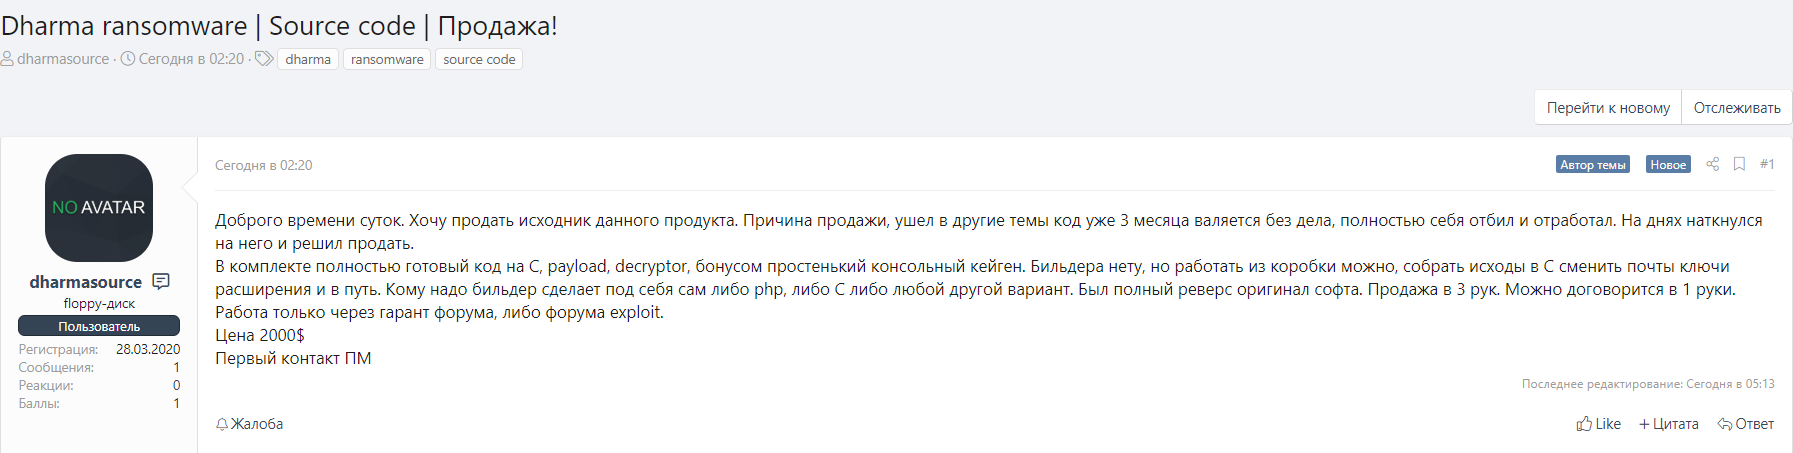
The source code of the infamous Dharma ransomware is now available for sale on two Russian-language hacking forums. The source code of one of the most profitable ransomware families, the Dharma ransomware, is up for sale on two Russian-language hacking forums. The Dharma ransomware first appeared on the threat landscape in February 2016, at the […]
 Pierluigi Paganini
March 29, 2020
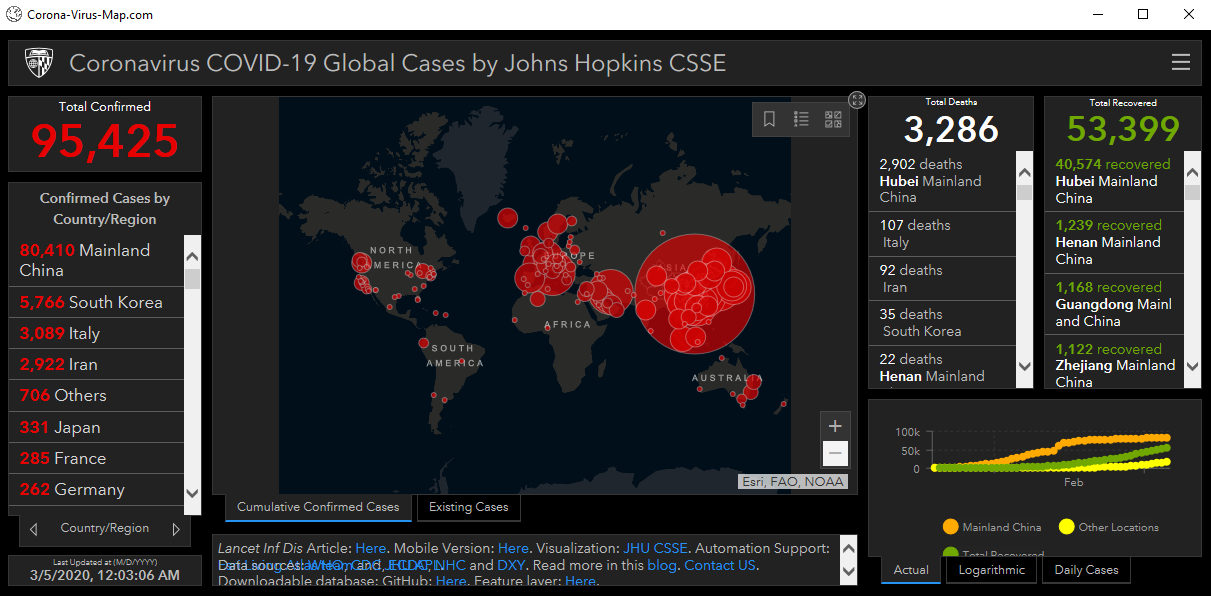
In this post, I decided to share the details of the Coronavirus-themed attacks launched from March 22 to March 28, 2020. Threat actors exploit the interest in the COVID19 outbreak while infections increase worldwide, experts are observing new campaigns on a daily bases. Below a list of attacks detected this week. March 23 – COVID19-themed […]
 Pierluigi Paganini
March 29, 2020
A new round of the weekly newsletter arrived! The best news of the week with Security Affairs Coronavirus-themed attacks March 15 – March 21, 2020 Google addresses high severity bugs in Chrome Keepnet Labs accidentally exposed an unprotected database with 5 Billion previously leaked records Security firm accidentally exposed an unprotected database with 5 Billion […]
 Pierluigi Paganini
March 29, 2020
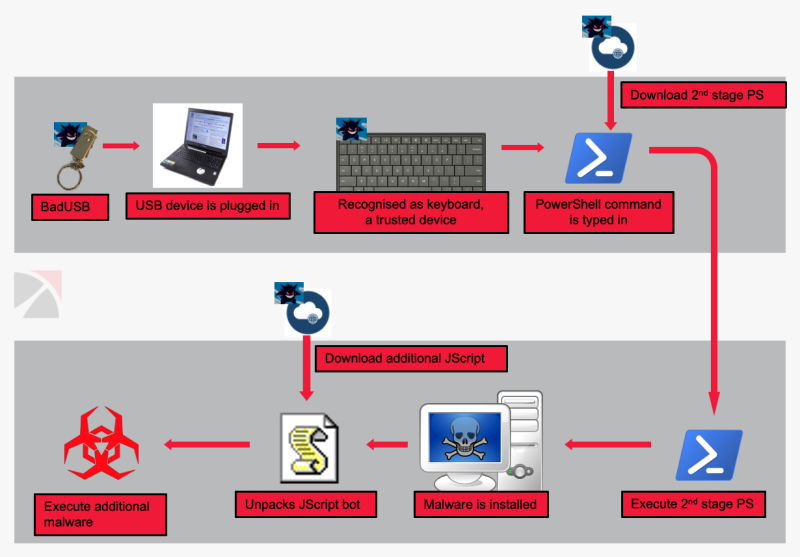
The FIN7 APT group has been targeting businesses with malicious USB drives and Teddy Bears sent to the victims, the FBI warns. The FBI is warning of a new wave of attacks carried out by the FIN7 APT group that is sending to the victims devices acting as a keyboard (HID Emulator USB) when plugged […]
 Pierluigi Paganini
March 28, 2020
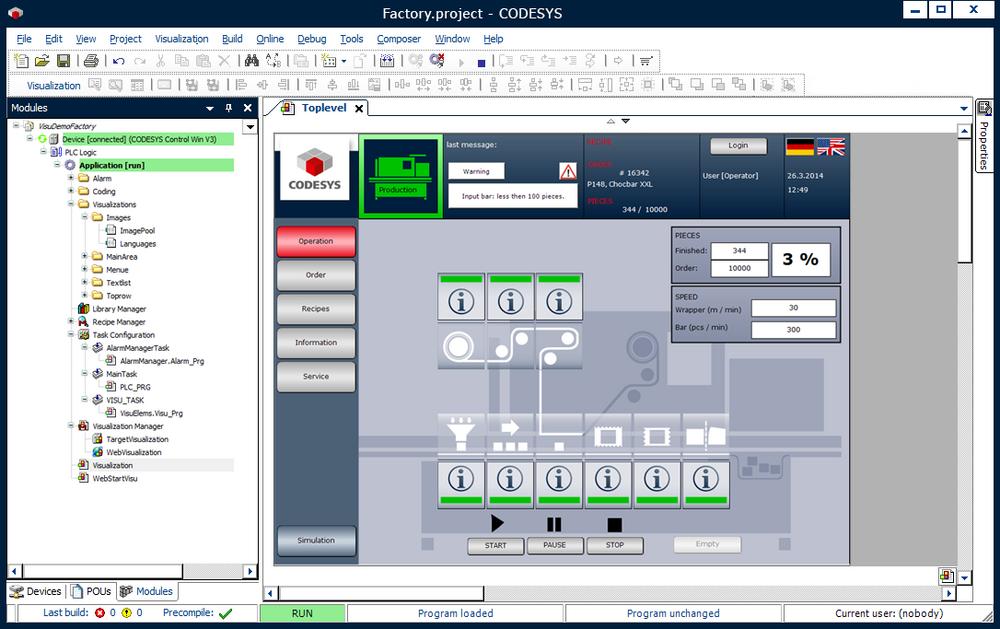
Experts discovered an easily exploitable heap-based buffer overflow flaw, tracked as CVE-2020-10245, that exists in the CODESYS web server. A critical heap-based buffer overflow flaw in a web server for the CODESYS automation software for engineering control systems could be exploited by a remote, unauthenticated attacker to crash a server or execute arbitrary code. CODESYS […]
 Pierluigi Paganini
March 28, 2020
Experts from Qihoo 360’s NetLab recently spotted two zero-day campaigns targeting DrayTek enterprise-grade networking devices. Since December 2019, researchers from Qihoo 360 observed two different attack groups that are employing two zero-days exploits to take over DrayTek enterprise routers to eavesdrop on FTP and email traffic inside corporate networks. While Netlab360 has found about ~100,000 devices […]
 Pierluigi Paganini
March 28, 2020
AMD admitted that a hacker has stolen files related to some of its graphics products, but it downplayed the potential impact of the hack. AMD admitted that a hacker that goes online with the moniker “Palesa” has stolen source code files related to some of its graphics products, but it downplayed the potential impact of […]
Uncategorized / September 21, 2026

Security / September 20, 2026