Pierluigi Paganini
 October 08, 2026
MonsterCloud owner Zohar Pinhasi allegedly paid ransomware demands behind clients’ backs, then charged them millions for the supposed recovery. Zohar Pinhasi, the owner of Florida-based MonsterCloud, was charged this week with wire fraud. Federal prosecutors say his clients were scammed twice during the same ransomware crisis. Pinhasi (50) also used the names “Zack Silver” and […]
 Pierluigi Paganini
October 01, 2026
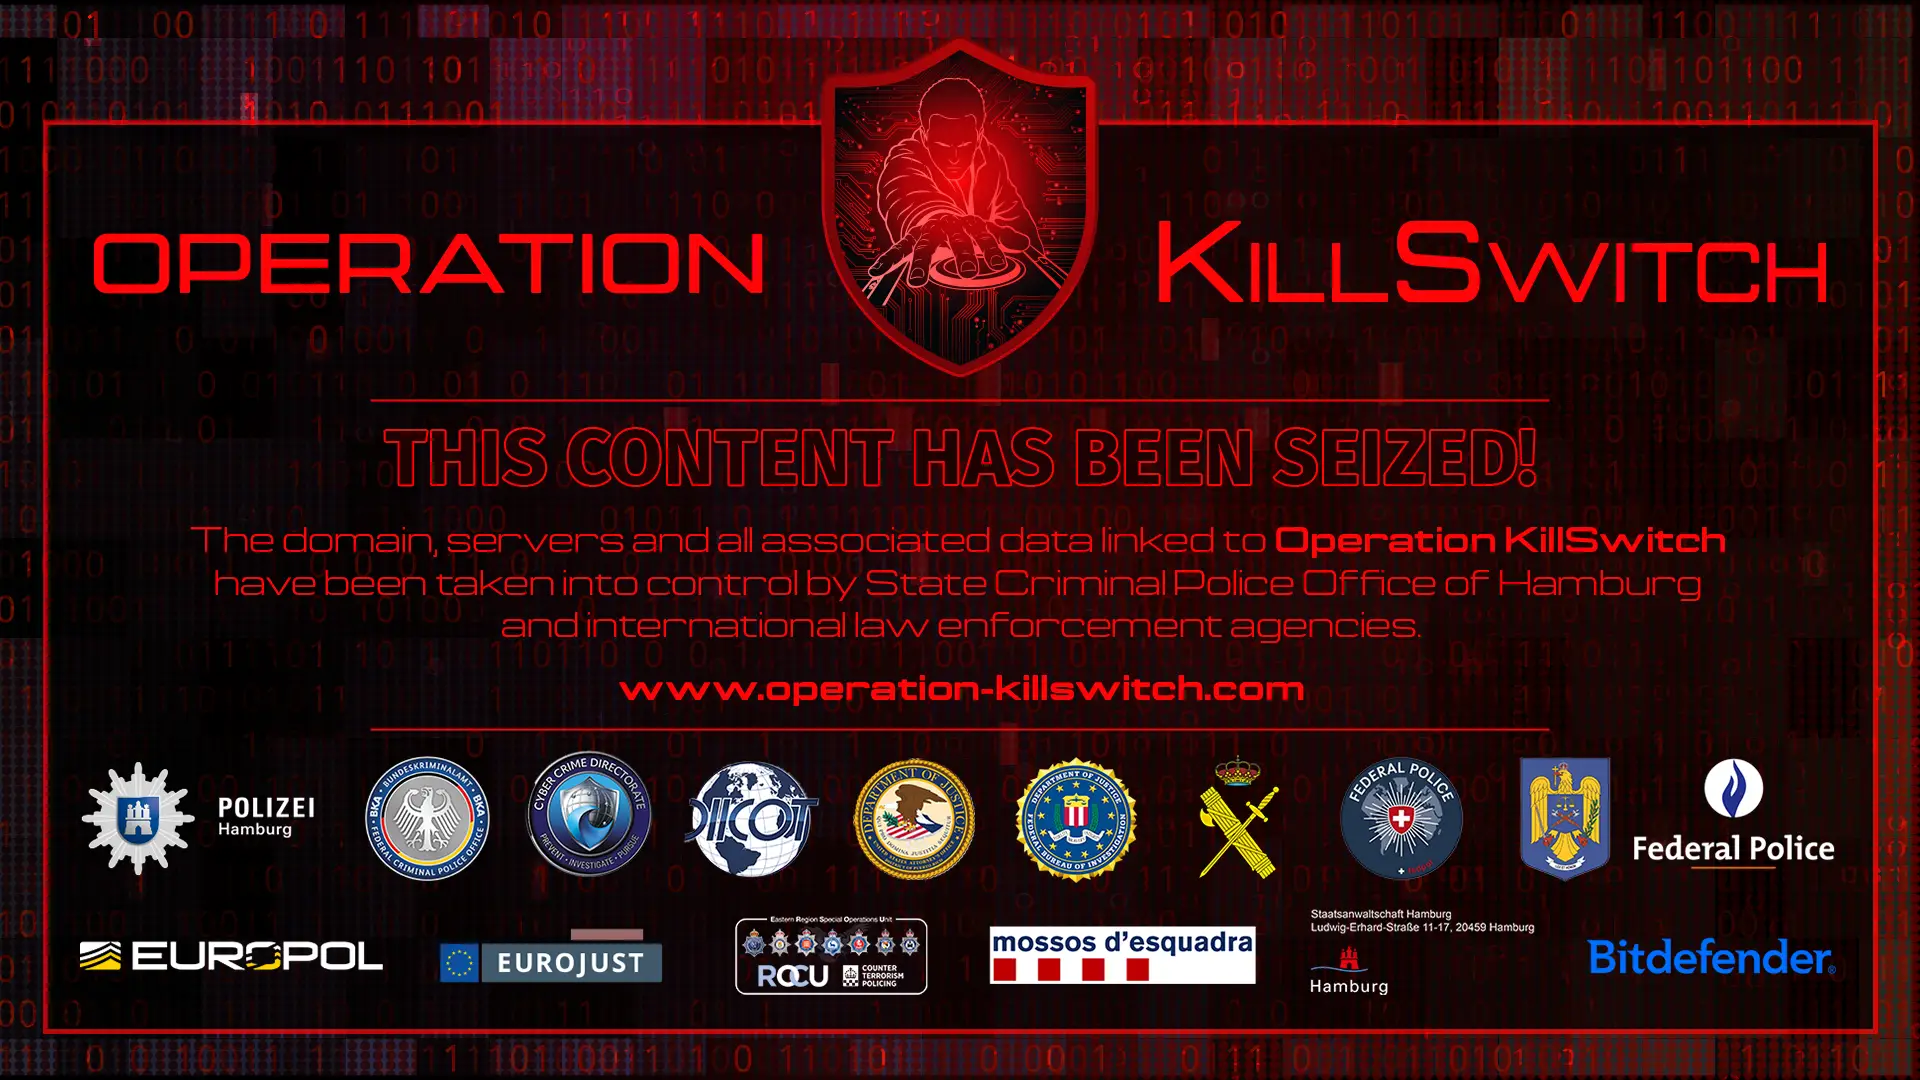
Operation KillSwitch: Europol says the KillSec ransomware group, allegedly led by a 16-year-old, was dismantled after attacks on about 1,000 victims. Law enforcement seized control of KillSec ‘s dark web leak site, the Tor website the group used to threaten victims with publishing stolen files unless they paid up. That single action locked down more […]
 Pierluigi Paganini
September 28, 2026
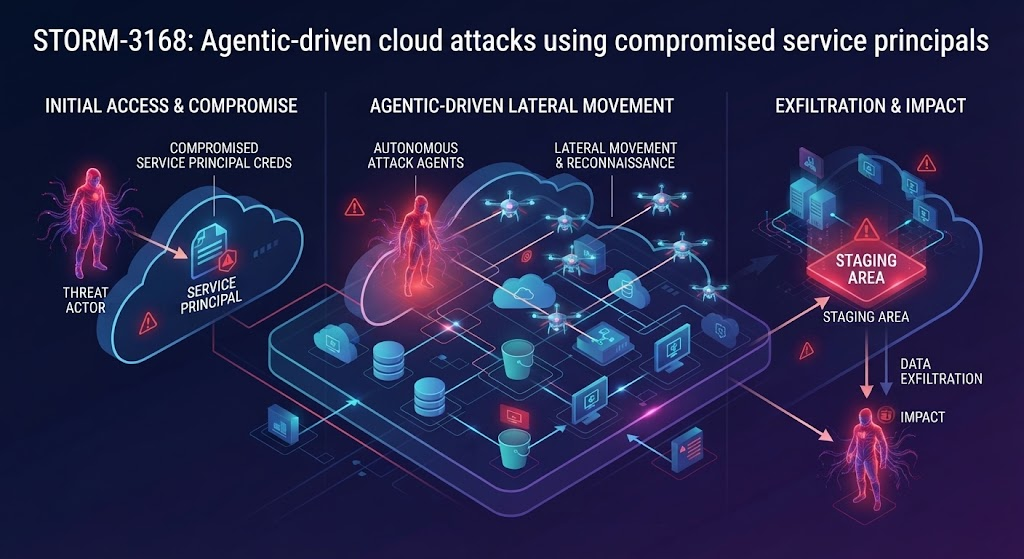
Microsoft details Storm-3168, the JADEPUFFER-linked actor that used stolen service principals to delete Azure storage in minutes and harvest keys. Microsoft just published the first detailed look at what JADEPUFFER does inside Azure. Sysdig first spotted the group’s activity in July 2026 and called it the first documented agentic ransomware operation. Microsoft tracks the same […]
Pierluigi Paganini
September 24, 2026
Ryuk member Karen Vardanyan was sentenced to 24 months in U.S. prison after extradition from Ukraine and ordered to pay $1.2M in restitution. Karen Vardanyan, a 35-year-old Armenian citizen who went by “Maneeken” and, oddly, “Karl Lagerfeld” online, was extradited from Ukraine and sentenced to 24 months in federal prison plus three years of supervised […]
 Pierluigi Paganini
August 13, 2026
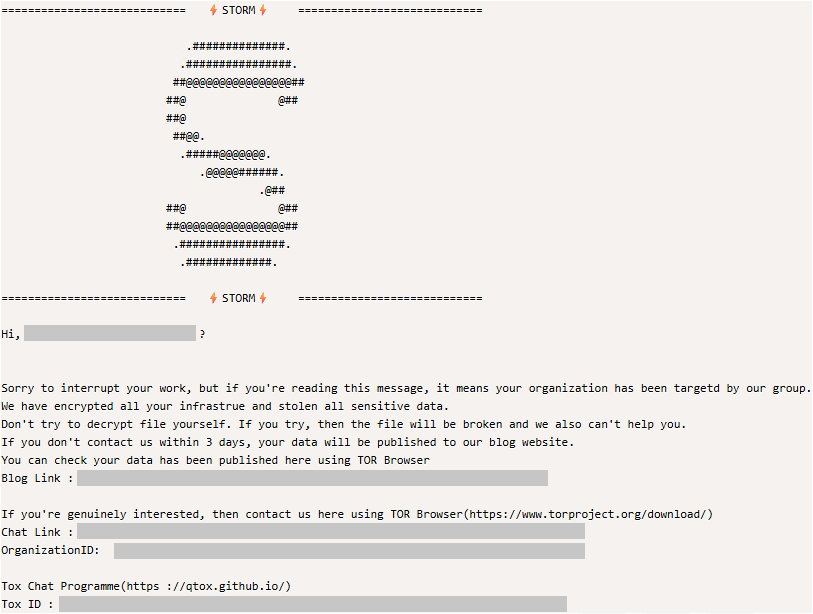
Microsoft says China-linked Storm-1175 is using a new ransomware called StormEncryptor, replacing Medusa in its latest attacks. Microsoft says China-linked, financially motivated threat actor Storm-1175 has begun using a new ransomware strain called StormEncryptor. The group previously relied on Medusa ransomware. StormEncryptor is written in C++ and encrypts files and adds the .encrypted extension, then […]
Pierluigi Paganini
August 06, 2026
A U.S. court sentenced Ransom Cartel founder Maksim Silnikau to 16 years for running a ransomware-as-a-service operation. Maksim Silnikau (aka “J.P. Morgan,” “lansky,” and “xxx,”) built a ransomware business the way a franchise owner builds a chain: he never had to touch most of the crime scenes himself. This week, a federal judge in Virginia […]
 Pierluigi Paganini
August 03, 2026
River Bank says hackers deleted data stolen in its June ransomware attack, though the investigation into the incident is still ongoing. River Financial Corporation, the parent company of River Bank & Trust, says hackers deleted data stolen during a ransomware attack that hit parts of its server environment in June. The breach began on June […]
 Pierluigi Paganini
July 27, 2026
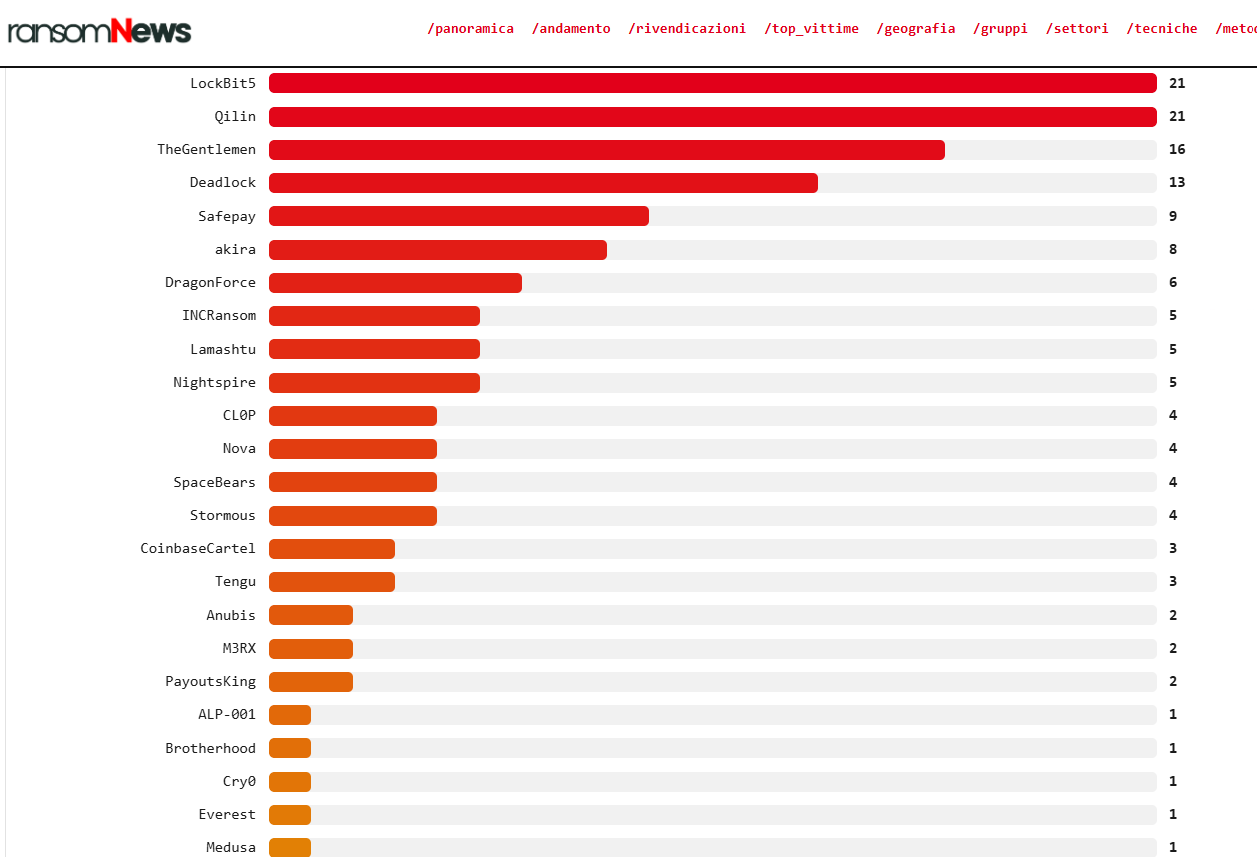
A new report links 148 ransomware attacks to Italian organizations in H1 2026, with manufacturing the most targeted sector. Six months, 148 confirmed ransomware claims against Italian targets, and one sector taking the brunt of it. That’s the headline number from a new semi-annual tracker compiled by ransomNews under its RedACT project, which pulls together […]
 Pierluigi Paganini
July 21, 2026
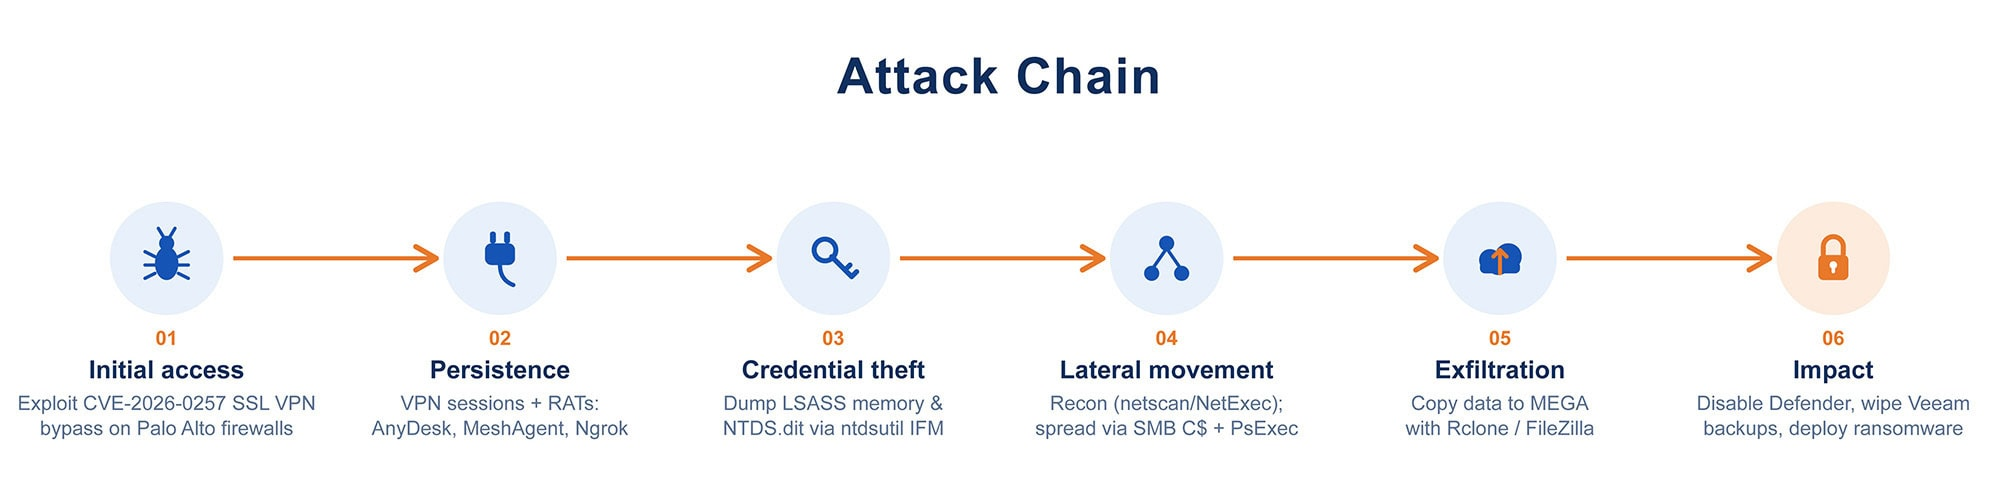
Qilin ransomware exploits the PAN-OS GlobalProtect flaw CVE-2026-0257 to gain unauthorized VPN access to unpatched networks. Arctic Wolf researchers warn that the Qilin ransomware gang is exploiting the critical PAN-OS GlobalProtect vulnerability CVE-2026-0257 to compromise corporate networks. CVE-2026-0257 is a PAN-OS authentication bypass vulnerability affecting GlobalProtect portals and gateways. Palo Alto Networks addressed the vulnerability on May […]
 Pierluigi Paganini
July 14, 2026
U.S. sanctions hit VPN provider 1VPNS and a cryptor seller for enabling ransomware gangs behind billions in losses to critical infrastructure. The U.S. Treasury’s Office of Foreign Assets Control sanctioned two individuals and one entity on July 13 for supplying tools and infrastructure to ransomware groups that have caused billions of dollars in losses to […]