 Pierluigi Paganini
 February 19, 2016
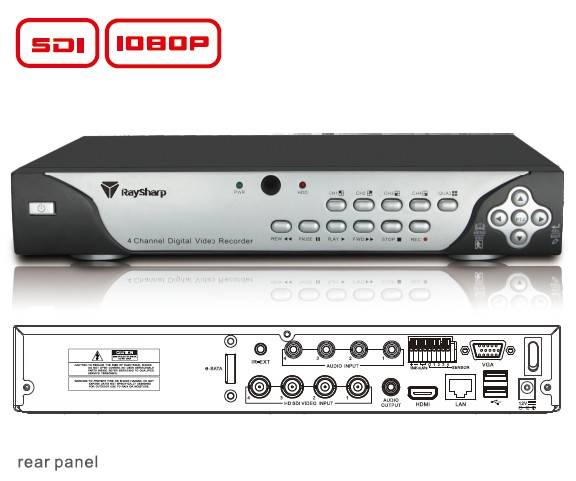
According to a report published by Risk Based Security more than tens of thousands of DVRs are exposed on the Internet with a hardcoded password. According to a report published by Risk Based Security (RBS), the firmware of DVRs manufactured by China-based Zhuhai RaySharp contains hardcoded credentials that could be used by a remote hacker […]
 Pierluigi Paganini
February 18, 2016
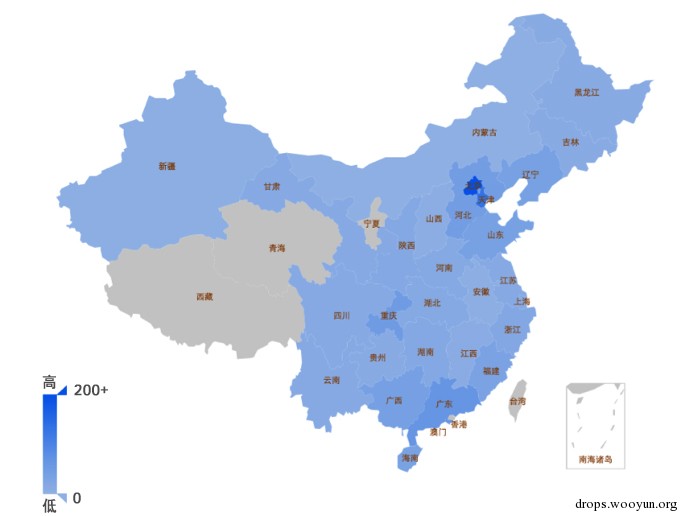
In May 2015, the Chinese security firm Qihoo 360 published a report on a Trojan called OceanLotus that was being used since 2012 for APT attacks in the Chinese market. The APT attacks based on the OceanLotus focused on government organizations, research institutes, maritime agencies, and companies specializing in other activities. At the time were […]
 Pierluigi Paganini
February 17, 2016
A group of researchers discovered that roughly 1,000 brain wallets have been drained by cyber criminals that have stolen $103,000 The term brainwallet refers to the concept of storing Bitcoins in one’s own mind by memorization of a passphrase. The phrase is converted into a 256-bit private key with a hashing or key derivation algorithm (example: SHA256). That […]
 Pierluigi Paganini
February 14, 2016
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs Google patched Nexus devices, including a critical Wi-Fi flaw How to thwart the passcode lock screen on iOS 8 and 9? Security Affairs newsletter Round 46 – News of the week Dyre crackdown, the biggest effort to […]
 Pierluigi Paganini
February 05, 2016
According to the NSW Government Department of Resources and Energy Chinese hackers have launched a malware-based attack on its network in December. The Australian NSW Government Department of Resources and Energy revealed that in December 2015 unknown hackers targeted its systems. In the same period, the organization was launching a number of important projects, including […]
 Pierluigi Paganini
February 03, 2016
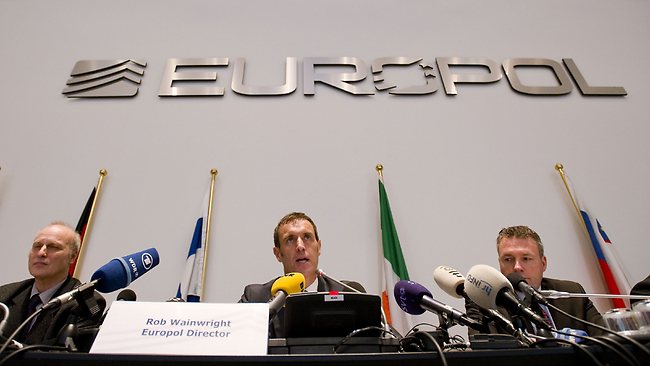
The Europol is increasing its efforts against terrorism, it has joined forces with EU to fight terrorist financing and money laundering. Since 1 January 2016, Europol has increased the level of integration among the nodes of the decentralised computer network of the European Union Member States’ Financial Intelligence Units (FIUs), the FIU.net. “FIU.NET is a decentralised computer network […]
 Pierluigi Paganini
February 03, 2016
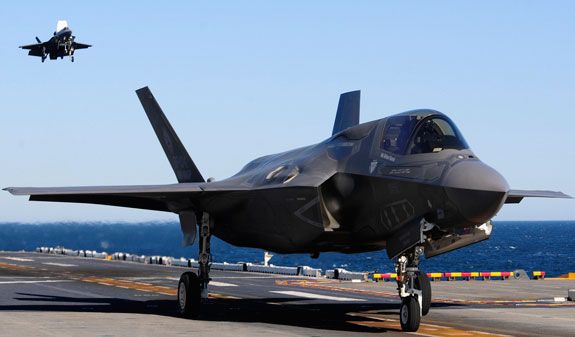
Cybersecurity Operational Tests And Assessments conducted by the US Defence are essential to improve overall security … and discover that US Govt can’t check F-35 data due to insecure systems. It is difficult to understand the importance of concept like information sharing when dealing with daily work, but officers at the Pentagon are learning at […]
 Pierluigi Paganini
January 31, 2016
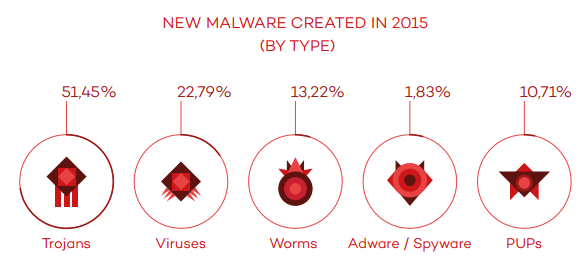
According to a new report from Panda Security more than 84 million new malware samples were detected over the 2015, 27% of all malware of ever. In 2015, security experts have detected the a record number of new malware, according to a report published by Panda Security more than 84 million new malware samples were collected. […]
Pierluigi Paganini
January 31, 2016
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs Shodan implements a feature to browse vulnerable webcams Europol, a new EU counter terrorism centre opening this month Security Affairs newsletter Round 44 – News of the week Skype – IP will now be hidden by default […]
 Pierluigi Paganini
January 29, 2016
Security Experts at FireEye discovered a new strain of POS malware dubbed CenterPOS that is threatening the retail systems. In the last 2/3 years, we have seen a significant increase in the number of POS malware, their diffusion is becoming even more worrying. We read about many high-profile breaches that involved high-complex malware targeting payment systems […]