 Pierluigi Paganini
 March 10, 2015
A new interesting report published by The Intercept details the effort spent by the US intelligence to compromise the security of Apple devices. The Intercept published another disconcerting post on the US Intelligence campaign aimed to steal the secrets of the IT giant Apple. According to top-secret documents disclosed by The Intercept a team of researchers working with the Central […]
 Pierluigi Paganini
February 18, 2015
Bio hacking – technology and humans have never been so close, they complement each other. But what are the security and privacy risks? IS BIOHACKING A SECURITY RISK? Imagine a world where our day to day activities like door locking, supermarket purchases, credit card swipes and smartphone usage are replaced by just one chip embedded […]
 Pierluigi Paganini
February 11, 2015
A serious vulnerability in the FancyBox WordPress plugin makes it easy for a hacker to compromise any website based on the popular CMS. Last week SecurityWeek reported about another a zero-day flaw found in a WordPress plugin. This time, a new vulnerability found in the popular FancyBox for WordPress plugin could be exploited to inject […]
 Pierluigi Paganini
February 11, 2015
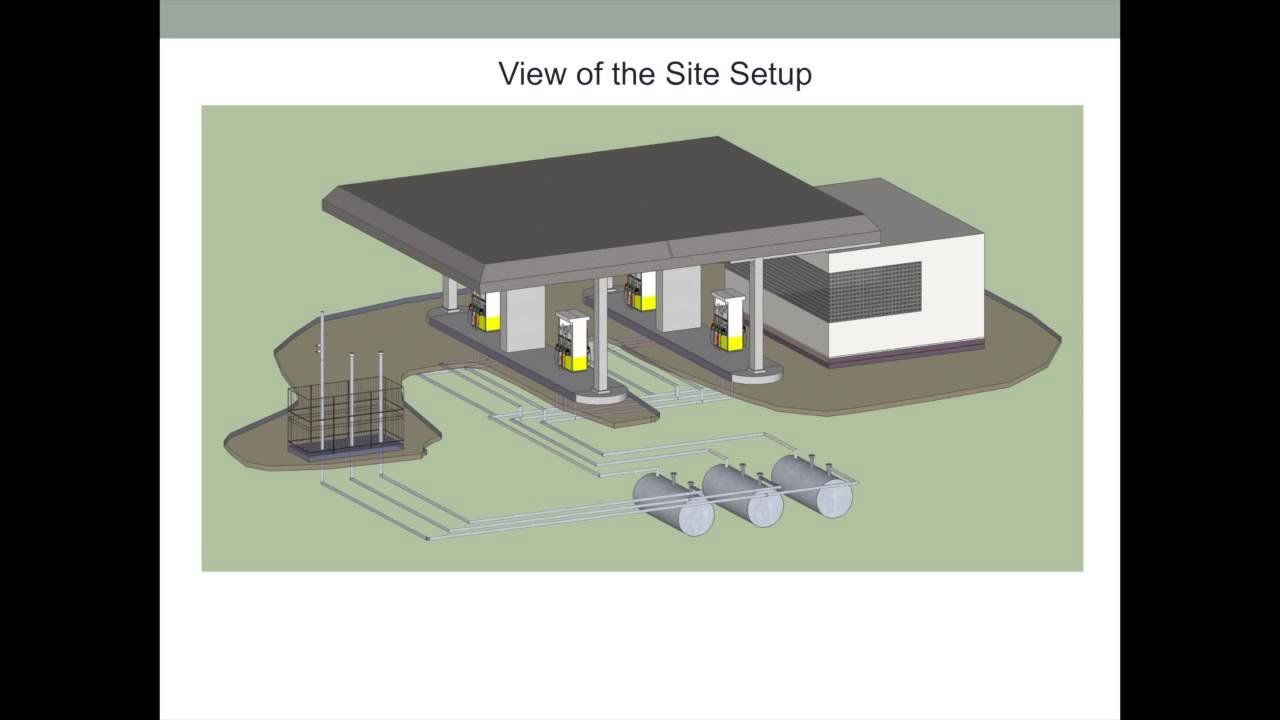
Researchers from Trend Micro discovered that unknown hackers have compromised Gas Pump Monitoring Systems in the US … it’s security emergency. Researchers at Trend Micro and many other security firms have observed a significant increase in the number of cyber attacks against systems in oil and energy industries. Another worrying trend observed by the experts is […]
 Pierluigi Paganini
February 05, 2015
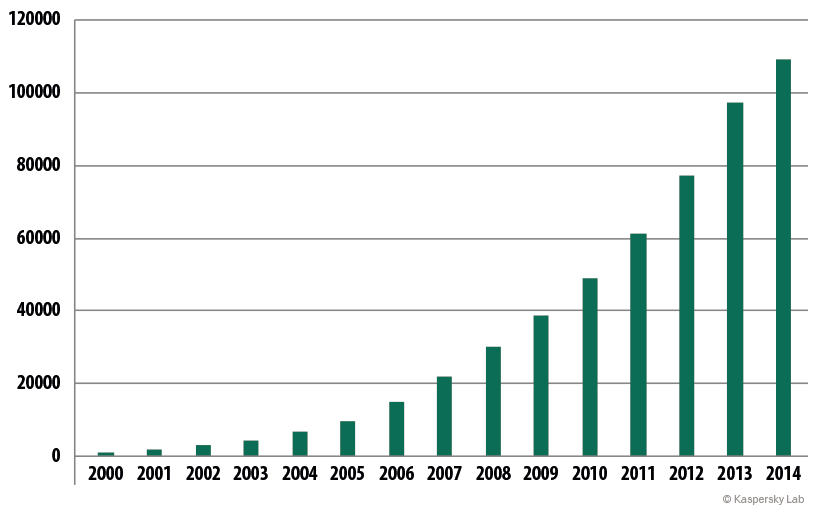
A recent report published by experts at Kaspersky Lab revealed that the number of abuses for digital certificates is in constant increase. According to a recent report published by Kaspersky Lab the number of untrusted certificates used to sign malicious code is doubled in the last year. The reason is that there is the wrong […]
 Pierluigi Paganini
January 29, 2015
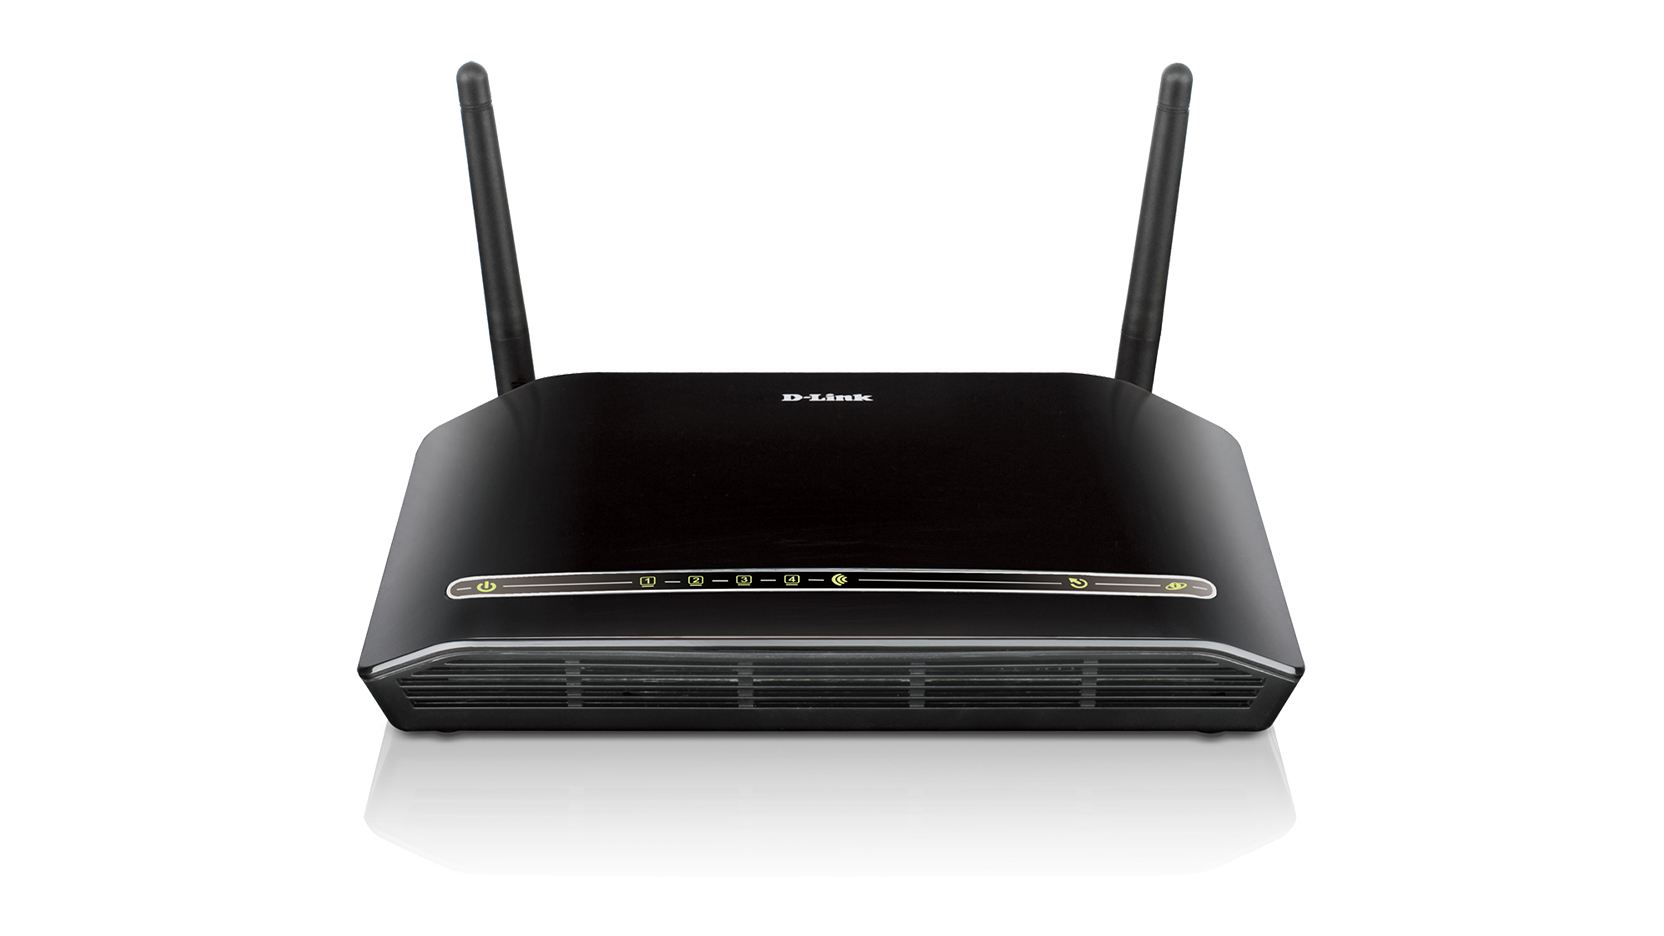
Critical DNS hijacking flaw affects D-Link DSL router, the flaw affects the ZynOS firmware that is used also by other vendors, including TP-Link and ZTE. A security vulnerability affects DSL router model from D-Link, the flaw could be exploited by a remote attacker to change device DNS settings and hijack users’ traffic. The Bulgarian security […]
 Pierluigi Paganini
January 28, 2015
According to a new series of reports published by Secunia firm, Oracle Java poses the biggest security risks to Desktop machines in the US. According to the a new report published by Secunia security vendor, Oracle Java software represents the principal source of problems for private US desktops, followed by Apple Quicktime 7.x. Oracle Java is […]
 Pierluigi Paganini
January 28, 2015
The CYBERPOL announced a series of training programs that aim to educate both law-enforcement and cyber security officers (CSO). CYBERPOL announced today that it has refined CYBERPOL’s focus arena and will be focusing on three main areas of cyber analytical research namely, Cyber Crime, Cyber threats and Cyber Intelligence CYBINT. The collective goal is to […]
 Pierluigi Paganini
January 26, 2015
Topface, the Russian-based dating site, has been hacked, User names and e-mail addresses of 20 million visitors are offered for sale online. Nearly 20 Million User names and e-mail addresses of visitors to the Russian-based dating website Topface have been available for sale online, the news first reported by Bloomberg. According to Daniel Ingevaldson, chief technology […]
 Pierluigi Paganini
January 23, 2015
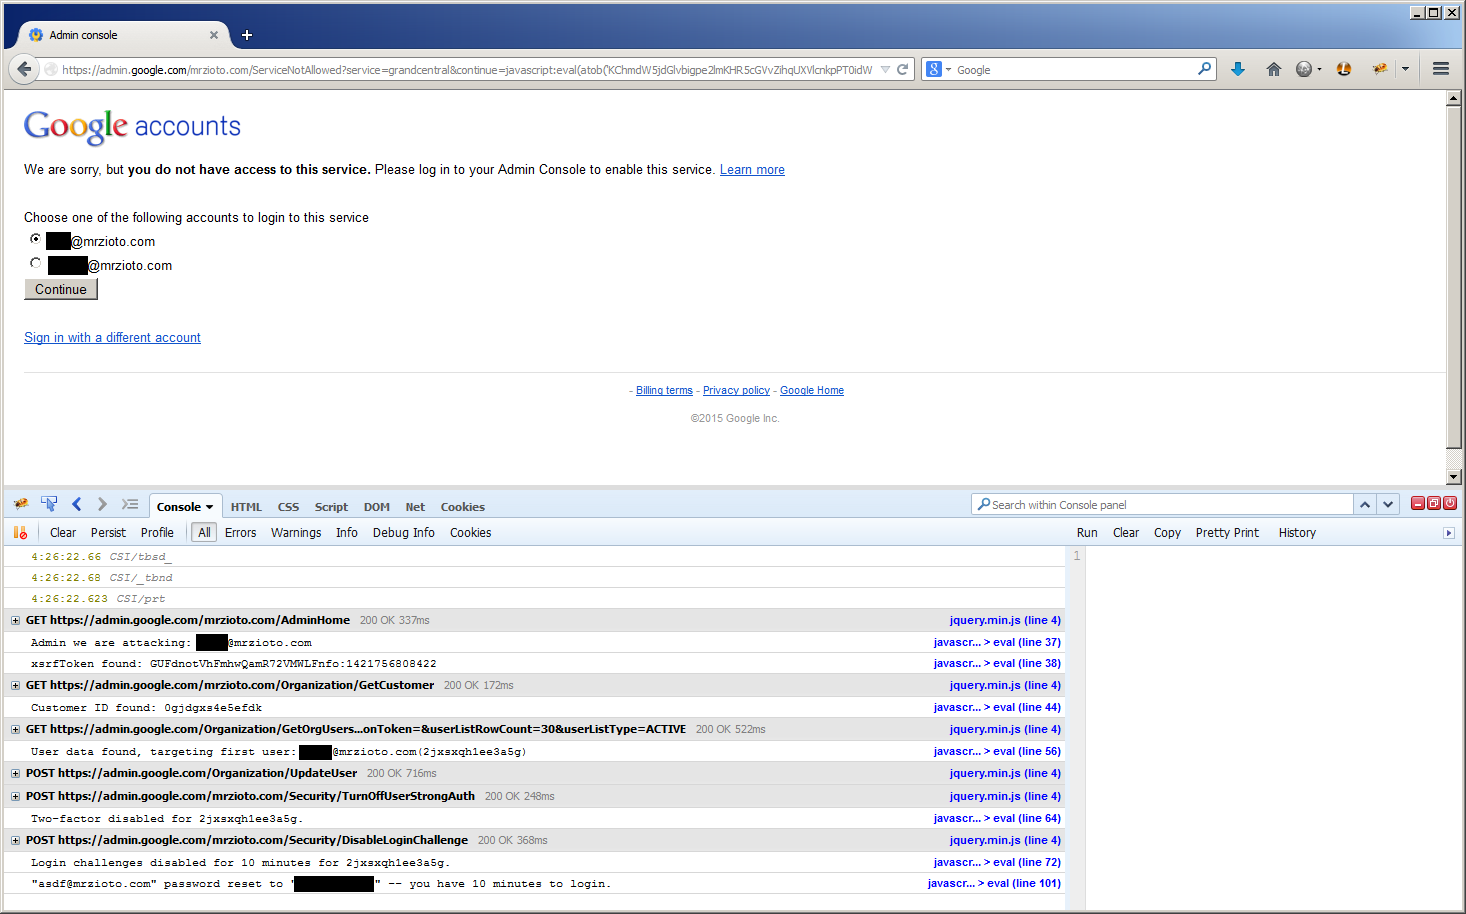
Security Expert Brett Buerhaus has discovered a critical flaw on admin.google.com, which could be exploited by to Hijack an account and disable 2FA Authentication. Even the giants have their Achilles heel, the Google Apps administrator console is affected by a critical cross-site scripting (XSS) vulnerability that could be exploited by attackers to force a Google Apps admins […]


Security / November 06, 2026