 Pierluigi Paganini
 December 02, 2014
FIN4 hacking team has targeted over 100 organizations since 2013, all of which are either publicly traded companies or advisory firms. Researchers at FireEye issued a report on a hacking crew dubbed FIN4 which is specialized in hacking of publicly traded companies with the intent to steal sensitive data, including mergers and acquisitions intelligence. ” FIN4 has pursued targets at more than […]
 Pierluigi Paganini
November 26, 2014
FireEye discovered that the Group of hackers dubbed APT3 that managed the Op Clandestine Fox is now running a new campaign dubbed Operation Double Tap. Researchers at FireEye have uncovered a new advanced persistent threat crew dubbed APT3, which is using exploits targeting recently disclosed vulnerabilities in Windows. The experts at FireEye believe that APT3 is the same […]
 Pierluigi Paganini
November 17, 2014
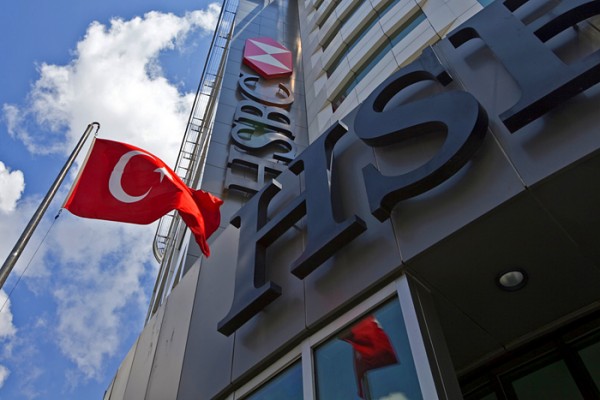
The International bank Hong Kong and Shanghai Banking Corporation (HSBC) announced that its systems suffered a major data breach. Last week the International bank Hong Kong and Shanghai Banking Corporation (HSBC) has announced that its computer networks in Turkey were breached by unknowns. The data breach has exposed the personal data of about 2.7 million customers of the HSBC bank, […]
 Pierluigi Paganini
November 12, 2014
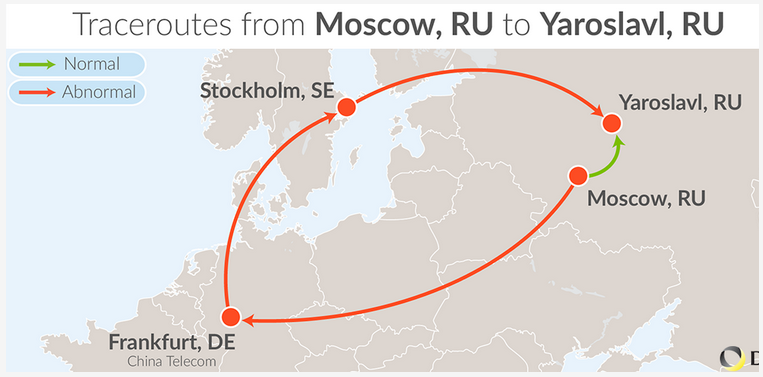
Russian Internet Traffic redirected by a Chinese operator due to routing errors caused by a weakness in the Border gateway protocol (BGP). The Russian Internet traffic in several circumstances has been re-routed outside the country, the incidents seem to be caused by routing errors made by China Telecom. The news has been published by the Internet monitoring service Dyn in a blog […]
 Pierluigi Paganini
November 11, 2014
Happy BirthDay Security Affairs! Three years together, it all began the 11/11/2011, a dream that becomes more and more real every day with your loving support. And it is just the beginning! I’m very happy and proud to be here with you for the third year of SecurityAffairs. We are a growing community that has tens of […]
 Pierluigi Paganini
November 10, 2014
A study published by Google demonstrates that manual phishing attacks are the simplest and most effective method for hacking email accounts. A study recently published by Google demonstrates that so-called manual phishing attacks are the simplest and most effective method for hijacking users’ email address. Let’s consider that the manual phishing attacks, as suggested by the name, doesn’t use […]
 Pierluigi Paganini
November 03, 2014
The ISIS has released a manual for its militants, titled “How to Tweet Safely Without Giving out Your Location to NSA”, that explain how avoid surveillance. Security and media consider the ISIS a group with great cyber capabilities, last news of the IS is related to the diffusion of a Training Guide for its members to prevent the NSA spying. The […]
 Pierluigi Paganini
October 26, 2014
The security firm AdaptiveMobile has discovered a new variant of Koler ransomware is capable of self-replication via SMS messages. A new strain of the Koler Android ransomware is threatening the mobile industry, the new variant spreads itself via SMSs and holds the victim’s device phone hostage until a ransom is paid. The Koler ransomware were detected by experts […]
 Pierluigi Paganini
October 22, 2014
Security experts at Google and McAfee have discovered a new Zero-day vulnerability in Microsoft OLE being exploited in targeted attacks. Early this week, Microsoft issued the security advisory 3010060 to warn its customer of a new Zero-Day vulnerability that affects all supported versions of Windows OS except, Windows Server 2003. The OLE Packager is the component that is affected by the zero-day, […]
 Pierluigi Paganini
October 16, 2014
Principal security firms united in a joint effort dubbed Operation SMN against the cyber espionage group known as Hidden Lynx and its arsenal. The Hidden Lynx APT is a China-based group of hackers that conducted numerous cyber espionage campaign against U.S. defense contractors and other foreign organizations. The name Hidden Lynx was assigned to the APT by experts at […]


Security / November 06, 2026