


 Pierluigi Paganini
 September 11, 2022
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs free for you in your email box. If you want to also receive for free the newsletter with the international press subscribe here. IHG suffered a cyberattack that severely impacted its booking process China-Linked BRONZE PRESIDENT APT targets Government […]
 Pierluigi Paganini
September 11, 2022
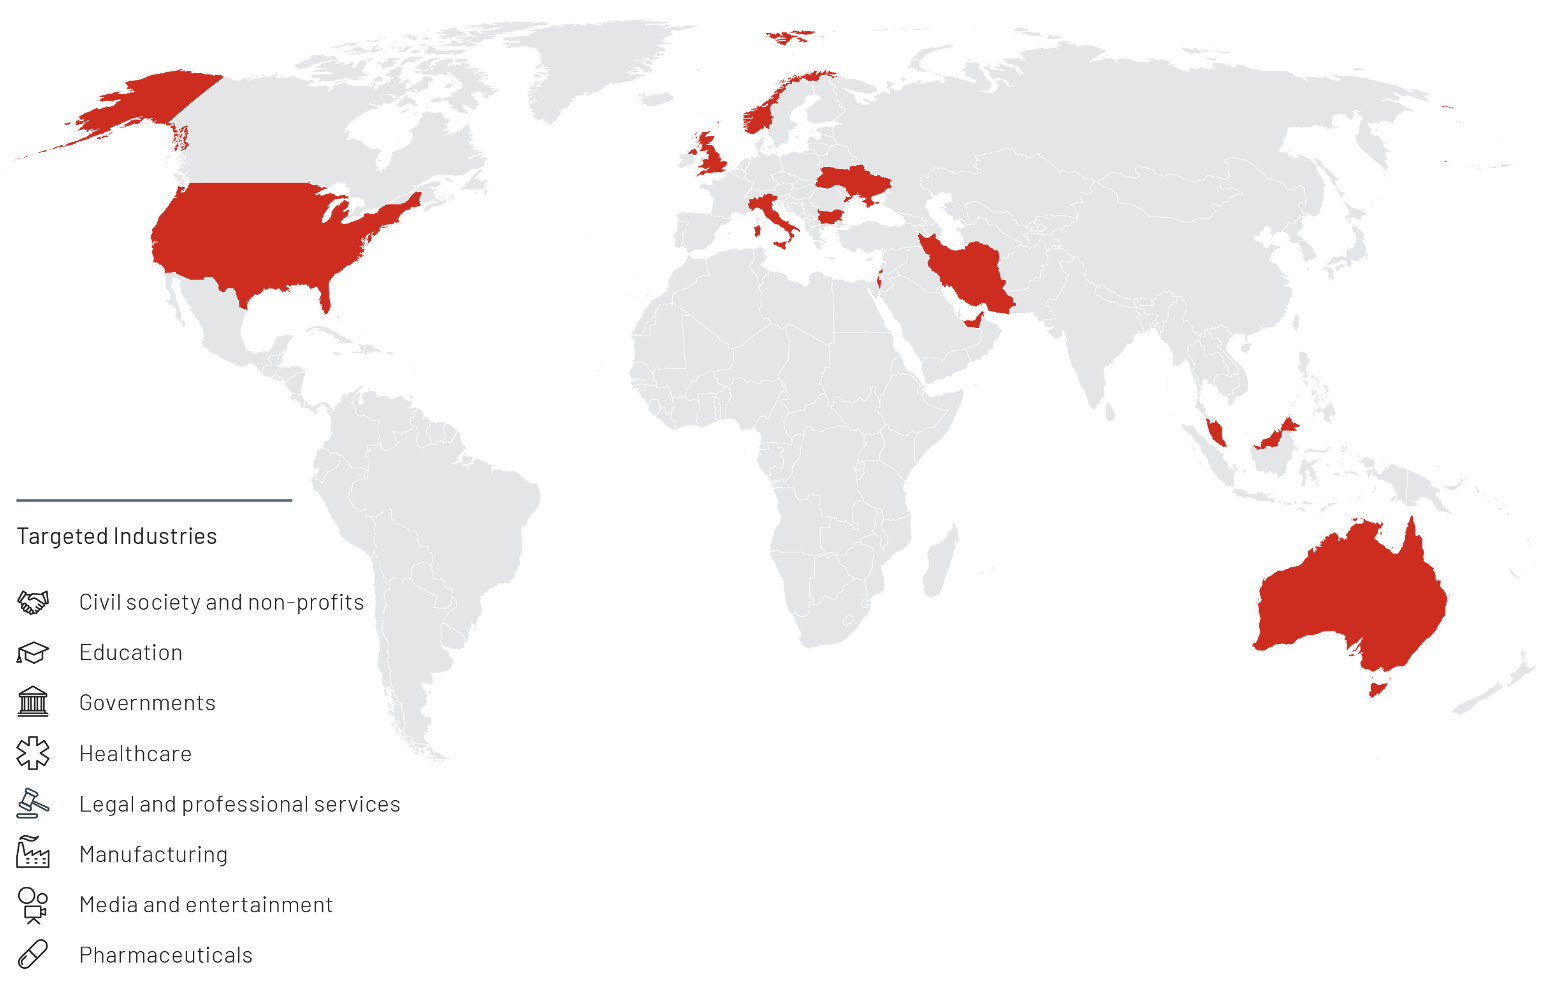
Iran-linked APT42 (formerly UNC788) is suspected to be the actor behind over 30 cyber espionage attacks against activists and dissidents. Experts attribute over 30 cyber espionage attacks against activists and dissidents to the Iran-linked APT42 (formerly UNC788). The campaigns have been conducted since 2015 and are aimed at conducting information collection and surveillance operations against […]
 Pierluigi Paganini
September 10, 2022
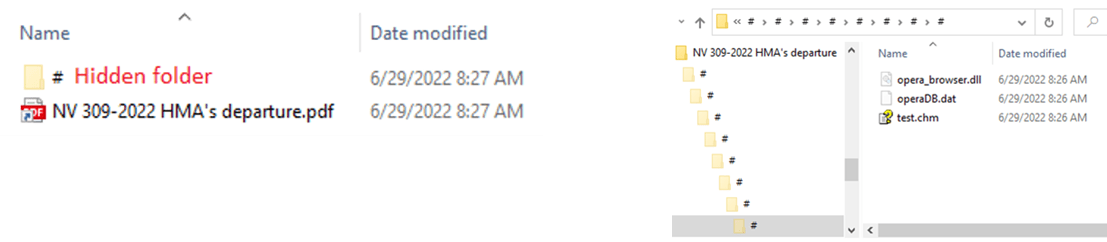
China-linked BRONZE PRESIDENT group is targeting government officials in Europe, the Middle East, and South America with PlugX malware. Secureworks researchers reported that China-linked APT group BRONZE PRESIDENT conducted a new campaign aimed at government officials in Europe, the Middle East, and South America with the PlugX malware. Attacks part of this campaign were spotted […]
 Pierluigi Paganini
September 10, 2022
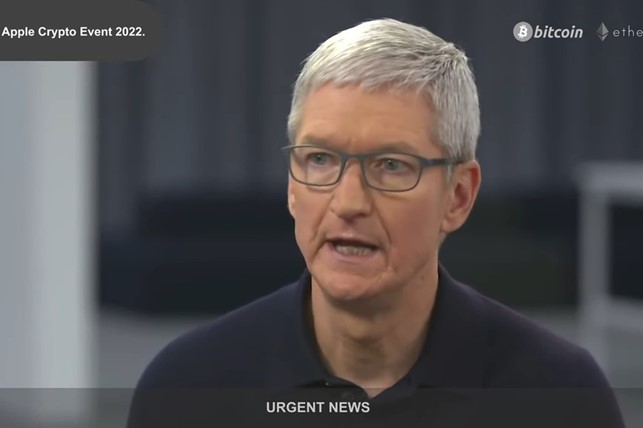
Scammers live-streamed on YouTube an old interview with Tim Cook as part of a fake Apple crypto event, and tens of thousands of users viewed it. Cybercriminals were live-streaming on YouTube an old interview with Tim Cook as part of a fake Apple crypto event, and tens of thousands of users viewed it. The interview […]
 Pierluigi Paganini
September 09, 2022
The U.S. Treasury Department sanctioned Iran ‘s Ministry of Intelligence and Security (MOIS) and its Minister of Intelligence over the Albania cyberattack. The U.S. Treasury Department announced sanctions against Iran ‘s Ministry of Intelligence and Security (MOIS) and its Minister of Intelligence over the cyber attack that hit Albania in July. MOIS is the primary intelligence […]
 Pierluigi Paganini
September 09, 2022
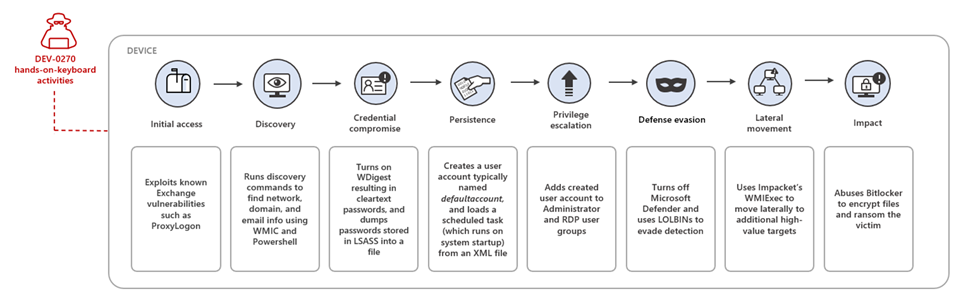
Iran-linked APT group DEV-0270 (aka Nemesis Kitten) is abusing the BitLocker Windows feature to encrypt victims’ devices. Microsoft Security Threat Intelligence researchers reported that Iran-linked APT group DEV-0270 (Nemesis Kitten) has been abusing the BitLocker Windows feature to encrypt victims’ devices. The researchers tracked multiple ransomware attacks conducted by the DEV-0270 group, which is a […]
 Pierluigi Paganini
September 08, 2022
CISA added 12 more security flaws to its Known Exploited Vulnerabilities Catalog including four D-Link vulnerabilities. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added 12 new vulnerabilities to its Known Exploited Vulnerabilities Catalog, including four vulnerabilities in D-Link routers, two Chrome zero-day issues, and a recently disclosed flaw in the QNAP Photo Station. According to Binding Operational […]
 Pierluigi Paganini
September 08, 2022
Threat actors claimed to have stolen classified NATO documents from the Armed Forces General Staff agency of Portugal (EMGFA). After discovering that Classified NATO documents belonging to the Armed Forces General Staff agency of Portugal (EMGFA) were offered for sale on the darkweb, the Portuguese agency discovered it has suffered a cyberattack. The Armed Forces […]
 Pierluigi Paganini
September 08, 2022
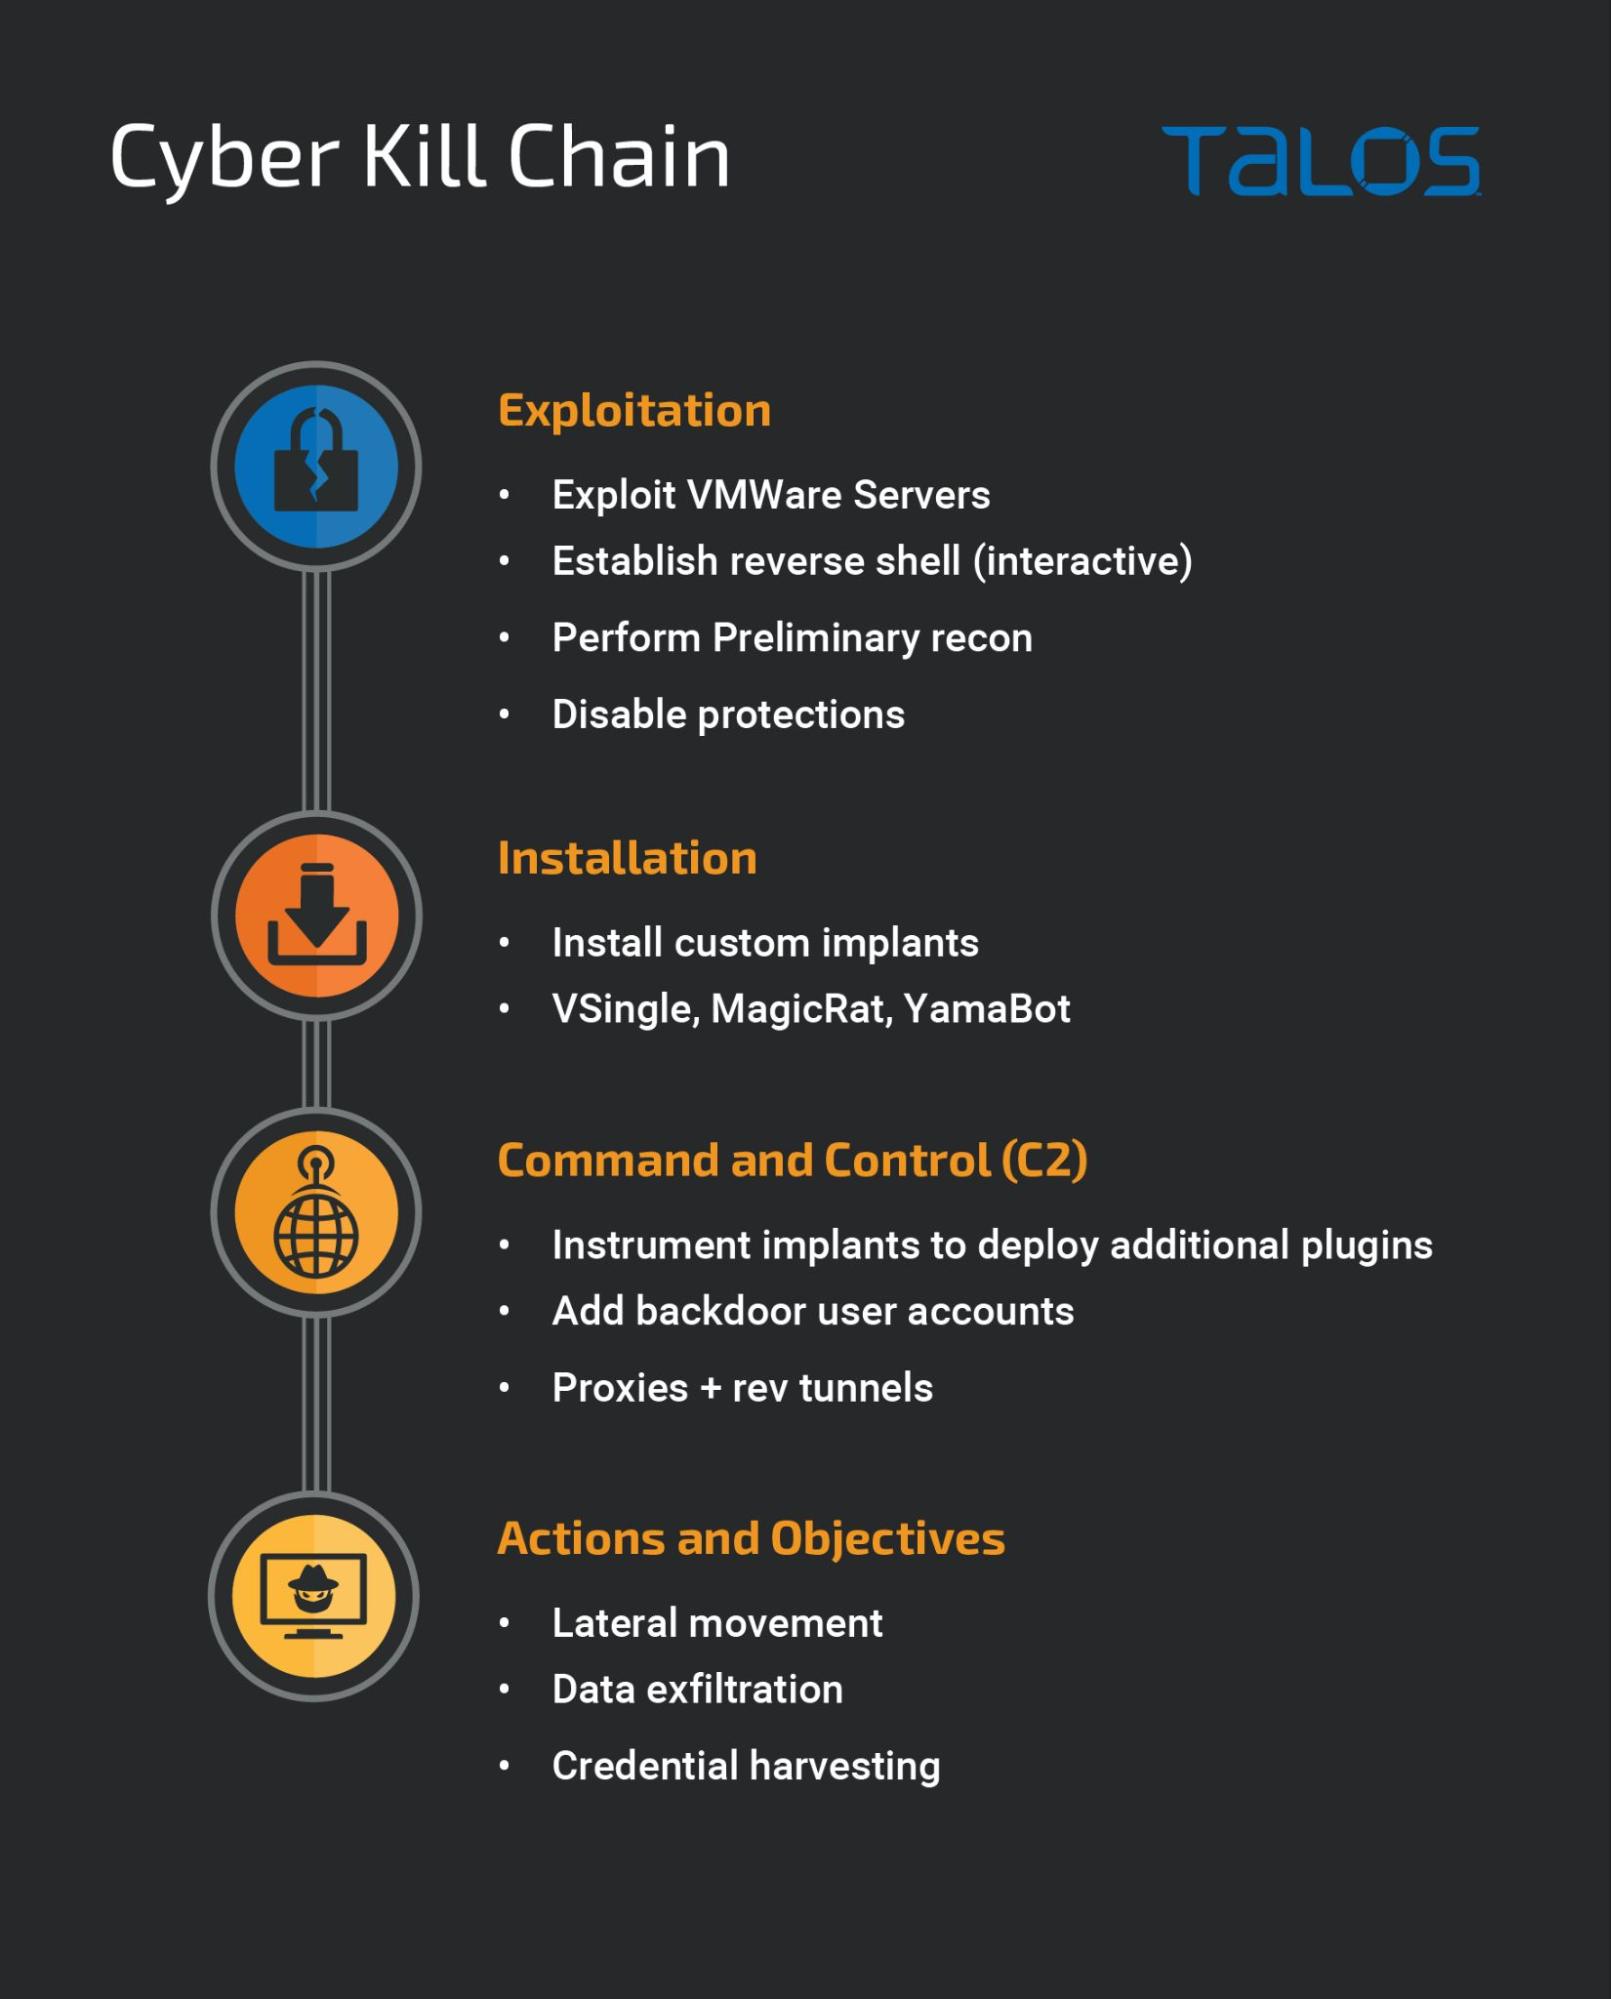
North Korea-linked Lazarus APT group is targeting energy providers around the world, including organizations in the US, Canada, and Japan. Talos researchers tracked a campaign, orchestrated by North Korea-linked Lazarus APT group, aimed at energy providers around the world, including organizations in the US, Canada, and Japan. The campaign was observed between February and July 2022. The attacks […]
 Pierluigi Paganini
September 08, 2022
Cisco fixed new security flaws affecting its products, including a recently disclosed high-severity issue in NVIDIA Data Plane Development Kit. The most severe issues fixed by Cisco are an unauthenticated Access to Messaging Services Vulnerability affecting Cisco SD-WAN vManage software and a vulnerability in NVIDIA Data Plane Development Kit. The two issues have been tracked as CVE-2022-20696 […]
Security / November 04, 2026

Malware / November 03, 2026


