 Pierluigi Paganini
 August 29, 2019
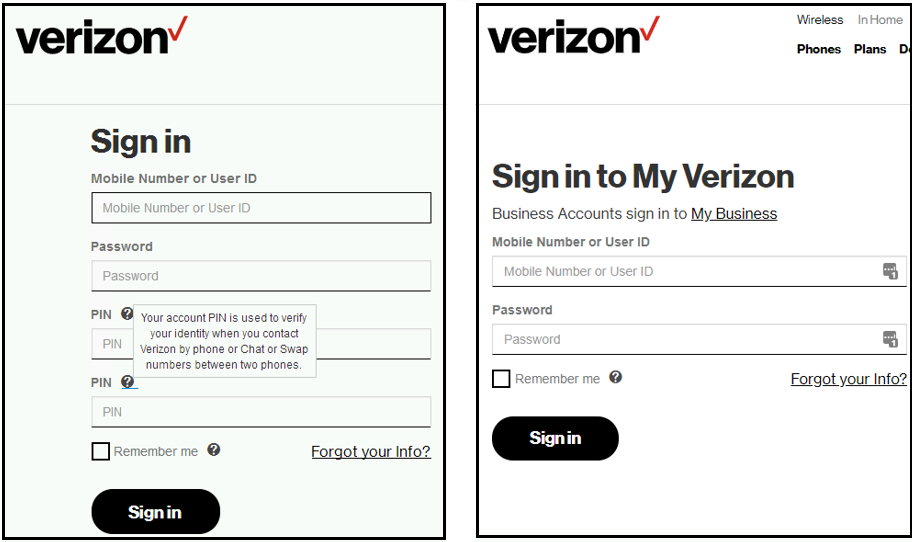
A new Trickbot Trojan variant is targeting Verizon Wireless, T-Mobile, and Sprint users, confirming the evolution of the threat. TrickBot is a popular banking Trojan that has been around since October 2016, its authors has continuously upgraded it by implementing new features. For example, in February Trend Micro detected a variant that includes a new module […]
 Pierluigi Paganini
August 29, 2019
An expert published technical details of recently disclosed Cisco Unified Computing System (UCS) flaws that can be exploited to take complete control of vulnerable systems. Security researcher Pedro Ribeiro, aka “bashis,” has released the details of three the recently addressed vulnerabilities in the Cisco Unified Computing System (UCS) products along with Metasploit modules for their exploitation. […]
 Pierluigi Paganini
August 28, 2019
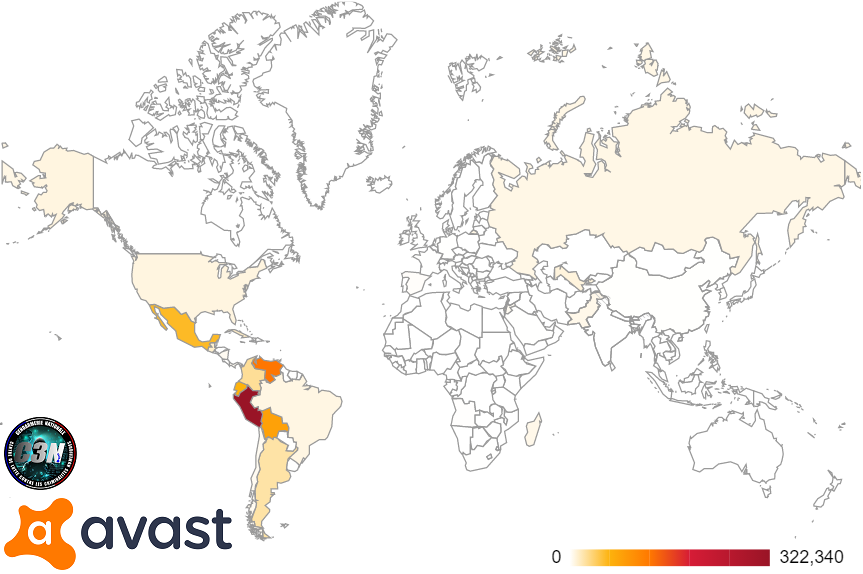
The French police force, National Gendarmerie, announced to have neutralized the Retadup malware on over 850,000 computers taking over its C2 server. The French police force, National Gendarmerie, announced the successful takedown of a huge RETADUP botnet after it has taken the control of its command and control (C2) server. The operation allowed the France law enforcement […]
 Pierluigi Paganini
August 28, 2019
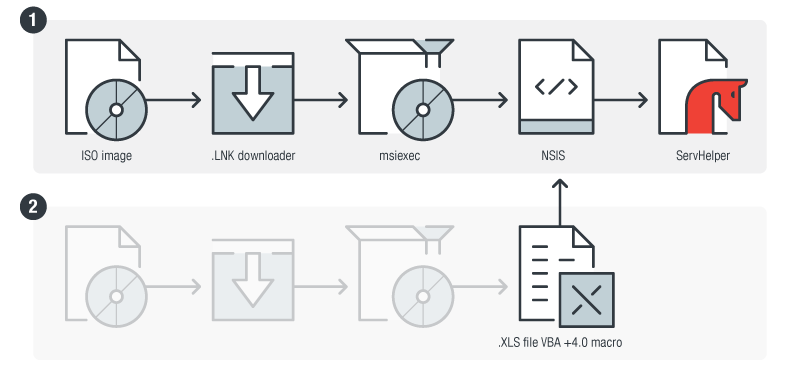
Recent campaigns show threat actors behind the Dridex and Locky malware families, the TA505 group, have updated tactics and expanded its target list. Trend Micro revealed that the TA505 group that is behind the Dridex and Locky malware families continue to make small changes to its operations. TA505 hacking group has been active since 2014 […]
 Pierluigi Paganini
August 27, 2019
Security firm Imperva revealed it has suffered a data breach that affecting some customers of its Cloud Web Application Firewall (WAF) product. Cybersecurity firm Imperva disclosed a data breach that has exposed sensitive information for some customers of its Cloud Web Application Firewall (WAF) product, formerly known as Incapsula. Incapsula, is a CDN service designed […]
 Pierluigi Paganini
August 27, 2019
Security experts from Kaspersky spotted a malware in the free version of the popular PDF creator application CamScanner app. CamScanner is a very popular Phone PDF creator app with more than 100 million downloads on Google Play Store. Experts from Kaspersky have discovered malware in the free Android version of the CamScanner app that could […]
 Pierluigi Paganini
August 27, 2019
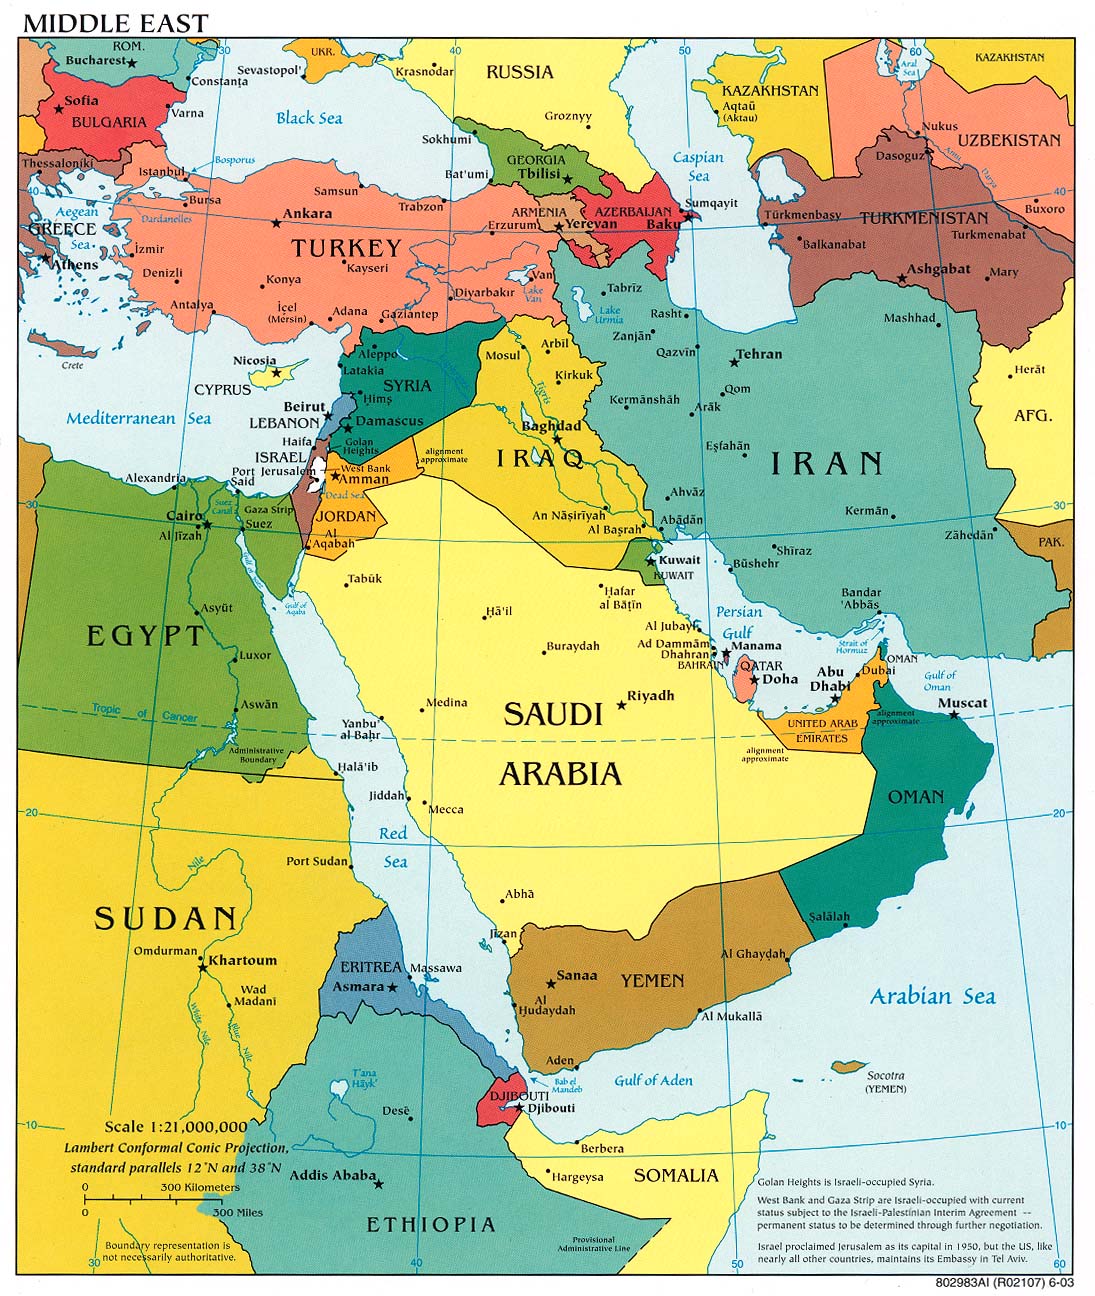
A recently reported APT group dubbed Lyceum group targets Oil and Gas organizations in the Middle East with simple techniques. The activity of the Lyceum APT group was first documented earlier in August by researchers at ICS security firm Dragos that tracked it as Hexane. Security experts at Dragos Inc. reported that Hexane is targeting organizations […]
 Pierluigi Paganini
August 27, 2019
A researcher was awarded $10,000 by Facebook for the discovery of a critical vulnerability that could have been exploited to hack Instagram accounts. The white-hat hacker Laxman Muthiyah has discovered a critical vulnerability that could have been exploited to hack Instagram accounts. The process affected Instagram’s password recovery process for mobile devices that leverages on […]
 Pierluigi Paganini
August 26, 2019
Apple has released an emergency patch in iOS 12.4.1 that addresses the CVE-2019-8605 use-after-free vulnerability that allowed iPhone jailbreak. Recently, Apple accidentally unpatched a vulnerability it had already fixed, making current versions of iOS vulnerable to hackers and allowing the jailbreak of the devices. Experts discovered that the iOS version 12.4 released in June has reintroduced a security […]
 Pierluigi Paganini
August 26, 2019
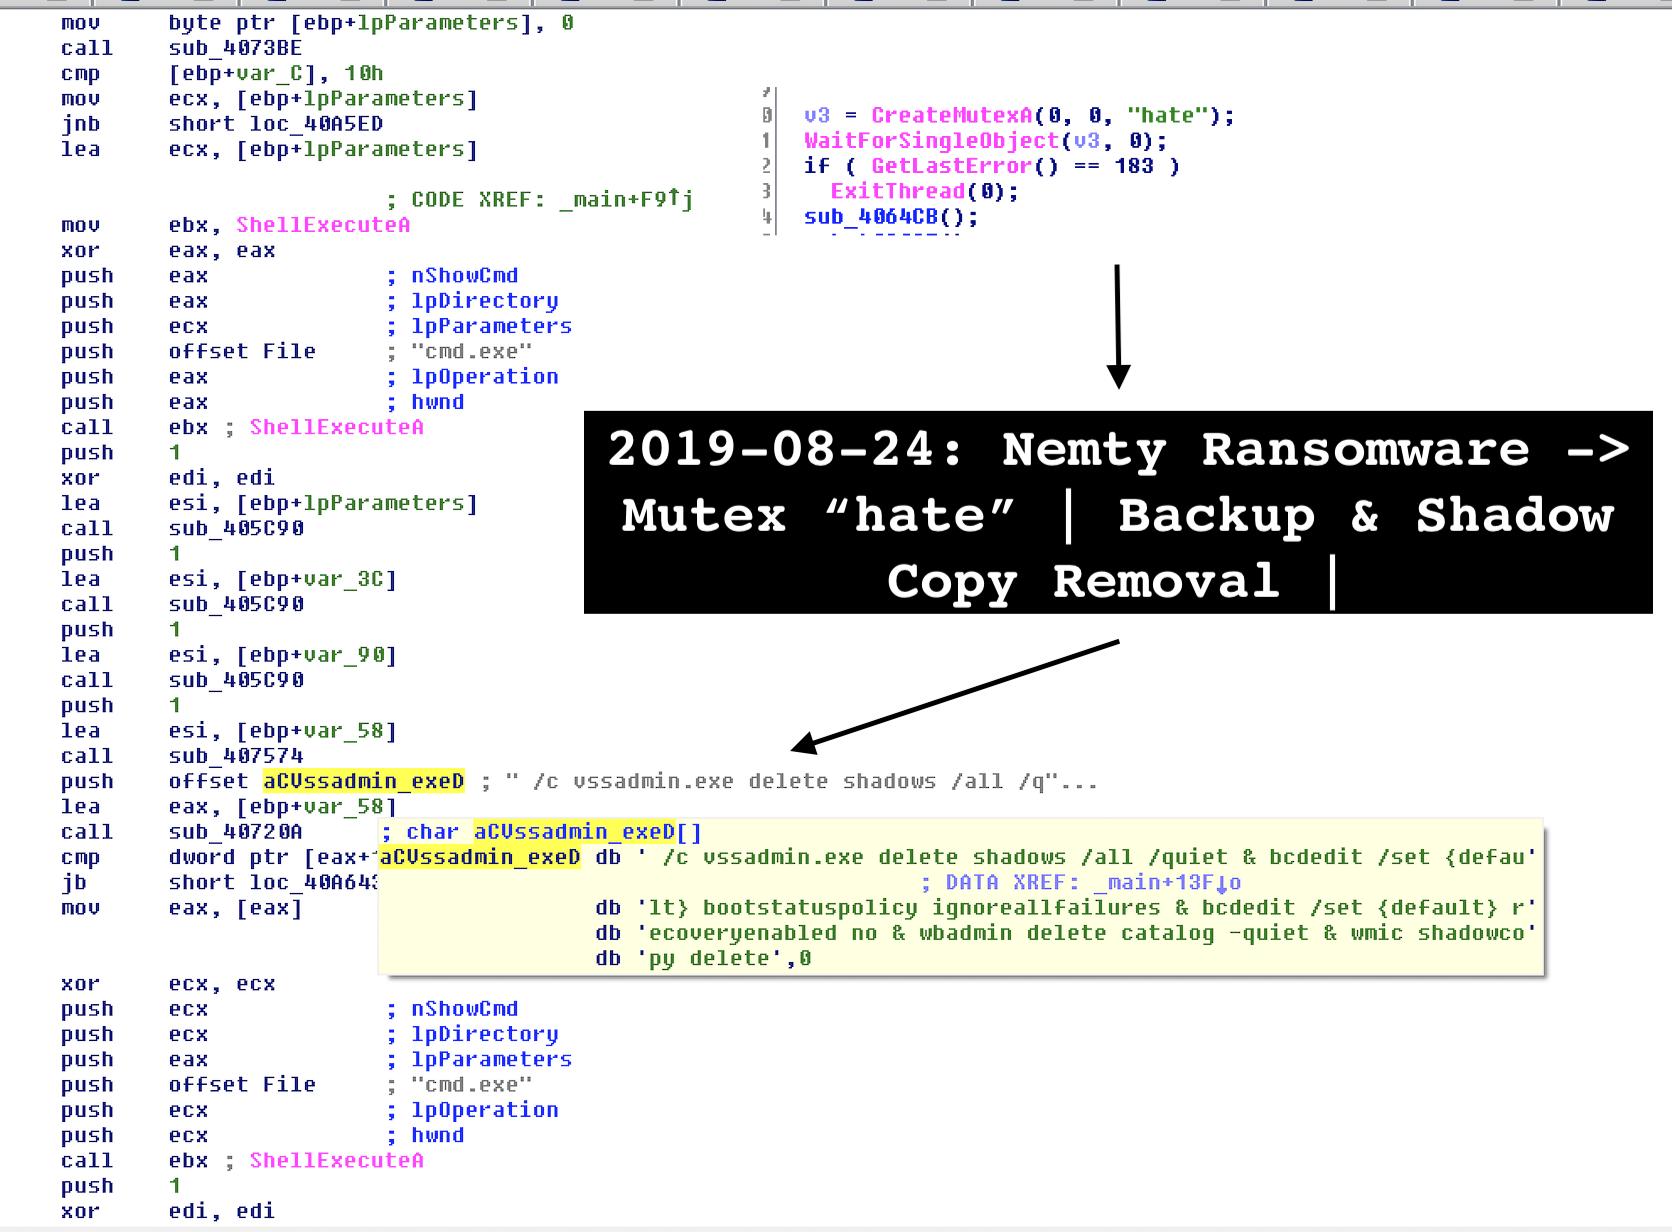
A new ransomware, dubbed Nemty, appeared in the threat landscape over the weekend, it spreads via compromised RDP connections. A new ransomware, called Nemty ransomware, has been discovered over the weekend by malware researchers. The name of the ransomware comes after the extension it adds to the encrypted file names, the malicious code also deletes […]