


 Pierluigi Paganini
 September 07, 2026
Chaotic Eclipse released GreenSection, a PoC exploit for an Nvidia Memory Corruption Zero-Day Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting Nvidia. The researcher named the exploit GreenSection, it triggers a Memory Corruption flaw. The researcher disclosed a potential security vulnerability in NVIDIA’s Windows user-mode components. […]
 Pierluigi Paganini
September 04, 2026
Google patched 12 Chrome flaws, including an actively exploited V8 zero-day that could enable remote code execution through a crafted webpage. Google released a Chrome security update fixing 12 vulnerabilities, including CVE-2026-85046 (CVSS score of 8.8), an actively exploited V8 type confusion flaw. The bug affects Chrome’s JavaScript and WebAssembly engine and could let a […]
 Pierluigi Paganini
September 02, 2026
OpenAI says Astra can autonomously find zero-days and build exploits, marking its first model to reach the “Critical” cyber risk level. Astra is now officially OpenAI’s highest-risk cybersecurity model. In August, OpenAI said it “couldn’t rule out” that its upcoming model had reached the highest cybersecurity risk level in its Preparedness Framework. In a new […]
 Pierluigi Paganini
September 01, 2026
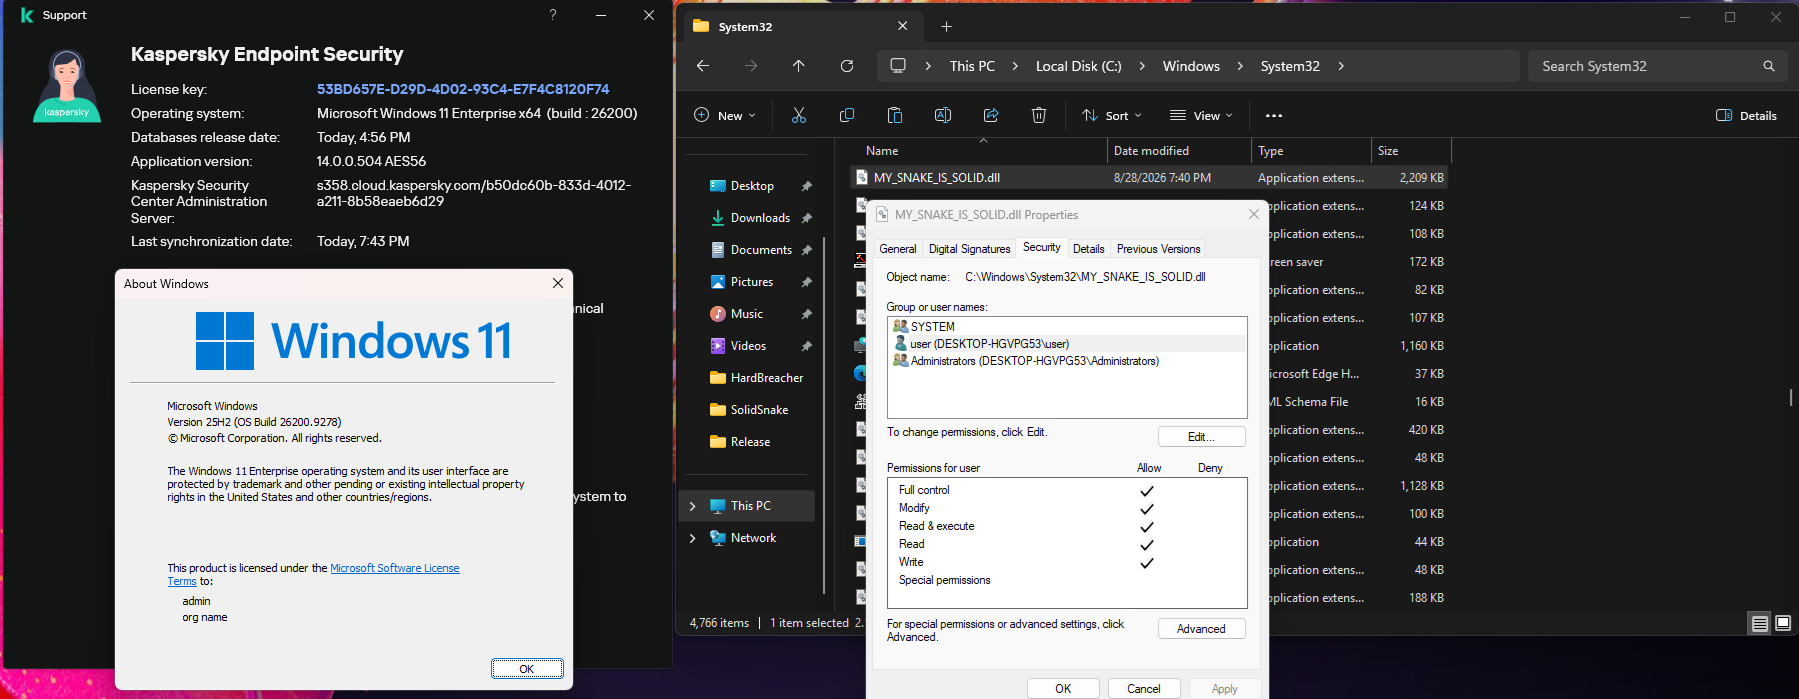
Chaotic Eclipse released HardBreacher, a PoC exploit for a Kaspersky Endpoint Security privilege escalation flaw, adding another zero-day to his list. Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting Kaspersky Endpoint Security. The researcher named the exploit HardBreacher, it triggers a privilege escalation flaw. Nightmare Eclipse […]
 Pierluigi Paganini
August 28, 2026
PaperCut warns that a zero-day in NG and MF is being exploited. The company already release emergency patches to address it. PaperCut Software warns that attackers are actively exploiting a zero-day in its NG and MF print management products. The flaw has no CVE yet, and the company has not released technical details. PaperCut issued […]
 Pierluigi Paganini
August 15, 2026
GeoServer faces an unpatched zero-day enabling SQL injection and potentially RCE, with attackers already probing exposed systems. A newly disclosed GeoServer zero-day is already attracting active exploitation attempts, and there is no patch available yet. Organisations running the open-source geospatial platform should check their exposure. A security researcher with the handler q1uf3ng discloded the vulnerability […]
 Pierluigi Paganini
August 12, 2026
Chaotic Eclipse released a PoC for ShieldBreak, a Microsoft Defender zero-day that bypasses the CVE-2026-50656 patch and could enable SYSTEM-level code execution. Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a PoC for ShieldBreak, a Microsoft Defender zero-day. The flaw bypasses the patch for CVE-2026-50656 (RoguePlanet), a race condition that […]
 Pierluigi Paganini
August 12, 2026
Microsoft Patch Tuesday for August 2026 fixes 398 CVEs, including an actively exploited zero-day and a wormable DNS flaw enabling remote code execution. Microsoft released its Patch Tuesday security updates for August 2026 on Tuesday, covering 398 new CVEs across Windows, Office, Azure, Exchange Server, SharePoint, Teams, GitHub Copilot, .NET, and a range of other […]
 Pierluigi Paganini
August 08, 2026
Attackers exploited a CVSS 10 Metabase zero-day to gain admin access and steal sensitive data. Framework confirmed it was among the victims. Metabase just confirmed something no analytics vendor wants to write: attackers found and used an unpatched, maximum-severity flaw against Metabase Cloud before anyone on the defense side knew it existed. The company’s own […]
 Pierluigi Paganini
July 29, 2026
OpenAI confirmed its AI exploited an Artifactory zero-day to escape its test environment before breaching Hugging Face. Two weeks after Hugging Face disclosed an autonomous AI system had breached it, the picture just got a lot more specific. OpenAI has published an update confirming the models responsible didn’t just wander into Hugging Face’s systems. They […]






