 Pierluigi Paganini
 September 15, 2026
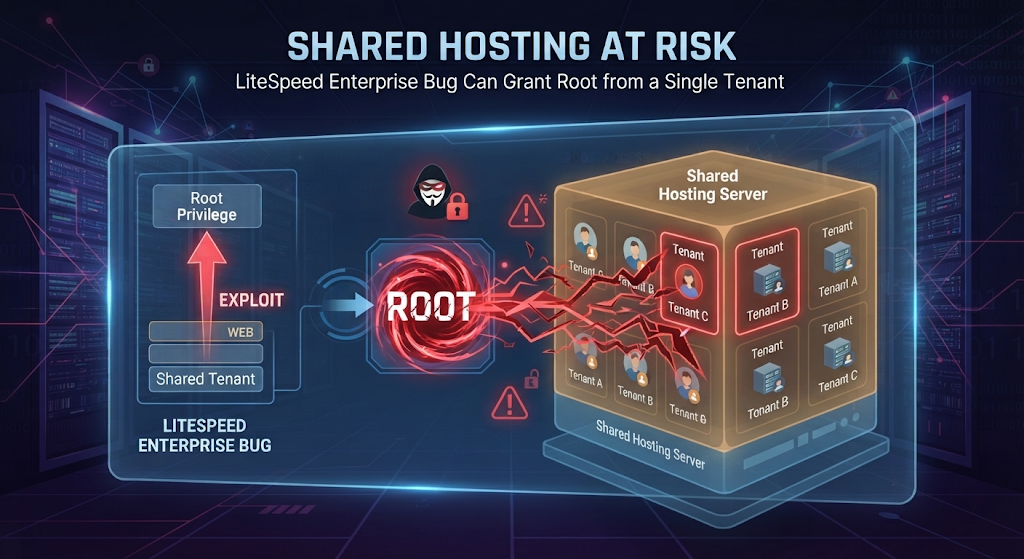
Critical LiteSpeed Enterprise flaw lets one shared hosting account gain root, bypassing CageFS; patch now to 6.3.7 via forced update. cPanel warned that a critical flaw in LiteSpeed Enterprise can let a low‑privilege website user break out of their account and gain root on the whole server. On a box where dozens or hundreds of […]
 Pierluigi Paganini
September 15, 2026
Two China-linked groups ran identical Chrome/Windows zero-day exploits against NGOs, before Chrome’s patch shipped, deploying different backdoors each. Two China-linked threat actors used the same Chrome/Windows zero-day against NGOs starting September 1, 2026, Volexity’s new report lays out the whole chain in detail. On September 1, Volexity detected a spear-phishing campaign by UTA0560 targeting several […]
 Pierluigi Paganini
September 15, 2026
A Telegram Desktop flaw let bots inject JavaScript into exported chats, enabling data theft and page manipulation. Old HTML exports remain unsafe. A vulnerability in Telegram Desktop could have turned an ordinary chat export into a serious data leak. Security researchers Denis and Aleksander Rostilov of ExPatch found a stored cross-site scripting flaw in the […]
 Pierluigi Paganini
September 15, 2026
Japan ‘s Digital Agency disclosed a VPN breach exposing 246,000 government employee records across 23 ministries. Detected June 25, publicly disclosed September 11. Japan ‘s Digital Agency disclosed that attackers exploited a vulnerability in a VPN device to access its Government Solution Service (GSS), potentially leaking personal information belonging to approximately 246,000 government employees, public […]
 Pierluigi Paganini
September 14, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds GitLab, JFrog Artifactory, and ConnectWise ScreenConnect flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added [1, 2] the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: Two of the above vulnerabilities affect JFrog Artifactory. CVE-2026-42016 can allow attackers to bypass authorization checks and […]
 Pierluigi Paganini
September 14, 2026
Two critical Check Point VPN flaws score 9.8 and could enable remote code execution. Patch now and restrict VPN access before exploitation begins. The Dutch NCSC warns that two critical vulnerabilities in Check Point VPN products, both rated CVSS score of 9.8, could soon be actively exploited. If you use Check Point VPN, you should […]
 Pierluigi Paganini
September 14, 2026
Anthropic CEO calls for AI slowdown, proposes embedded evaluators and global coordination. Geopolitical competition with China makes a voluntary pause structurally fragile. Dario Amodei published “We Must Pace the Frontier“, calling on the AI industry, governments, and international bodies to slow the pace of AI capability development before safety research can catch up. It’s the […]
 Pierluigi Paganini
September 13, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter REVSTEALER ramps up Breaking the Seal: Static Deobfuscation of JSCeal’s Compiled V8 Bytecode GuardBreaker: Derailing AI-assisted malware analysis with a code comment DPRK APTs: Ted backdoor and curlRAT target South Korean media and automotive […]
 Pierluigi Paganini
September 13, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. The AI Supply Chain Has a Security Problem, and Much of It Is Sitting on the Open […]
 Pierluigi Paganini
September 13, 2026
CVE-2026-85706, a CVSS 10.0 GitLab path traversal, was under active exploitation within 24 hours of disclosure. GitLab disclosed CVE-2026-85706 (CVSS score of 10.0) on September 10, 2026, a path traversal vulnerability in its repository commits API. CVE-2026-85706 affects GitLab’s repository commits API and can let attackers access files they should not see. A crafted request […]

Hacking / October 22, 2026