


 Pierluigi Paganini
 October 06, 2026
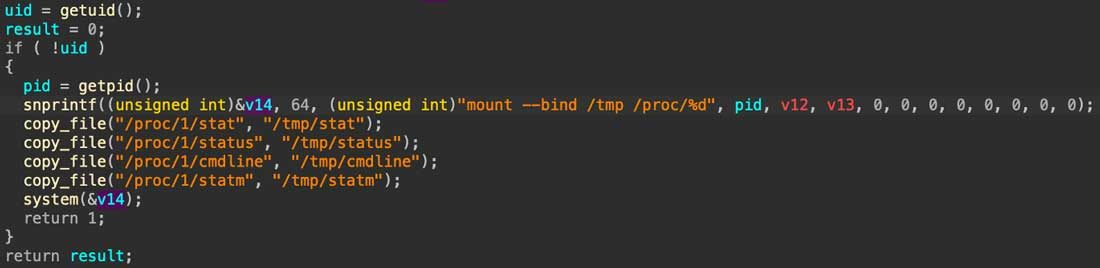
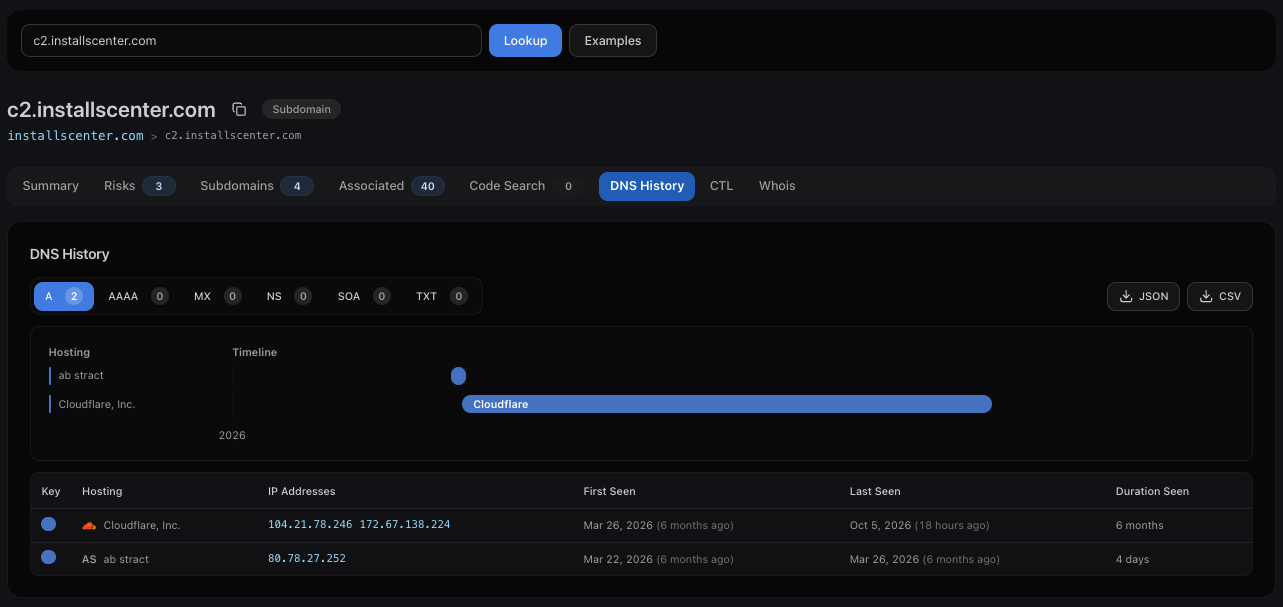
Fortinet details ClingSTUN, a Linux backdoor exploiting unpatched IoT devices and abusing public STUN servers to route traffic past NAT. FortiGuard Labs researchers spotted a Linux malware family they call ClingSTUN, and the name gives away its trick immediately. Instead of relying on a dedicated command server, the malicious code leans on STUN, the protocol […]
 Pierluigi Paganini
September 29, 2026
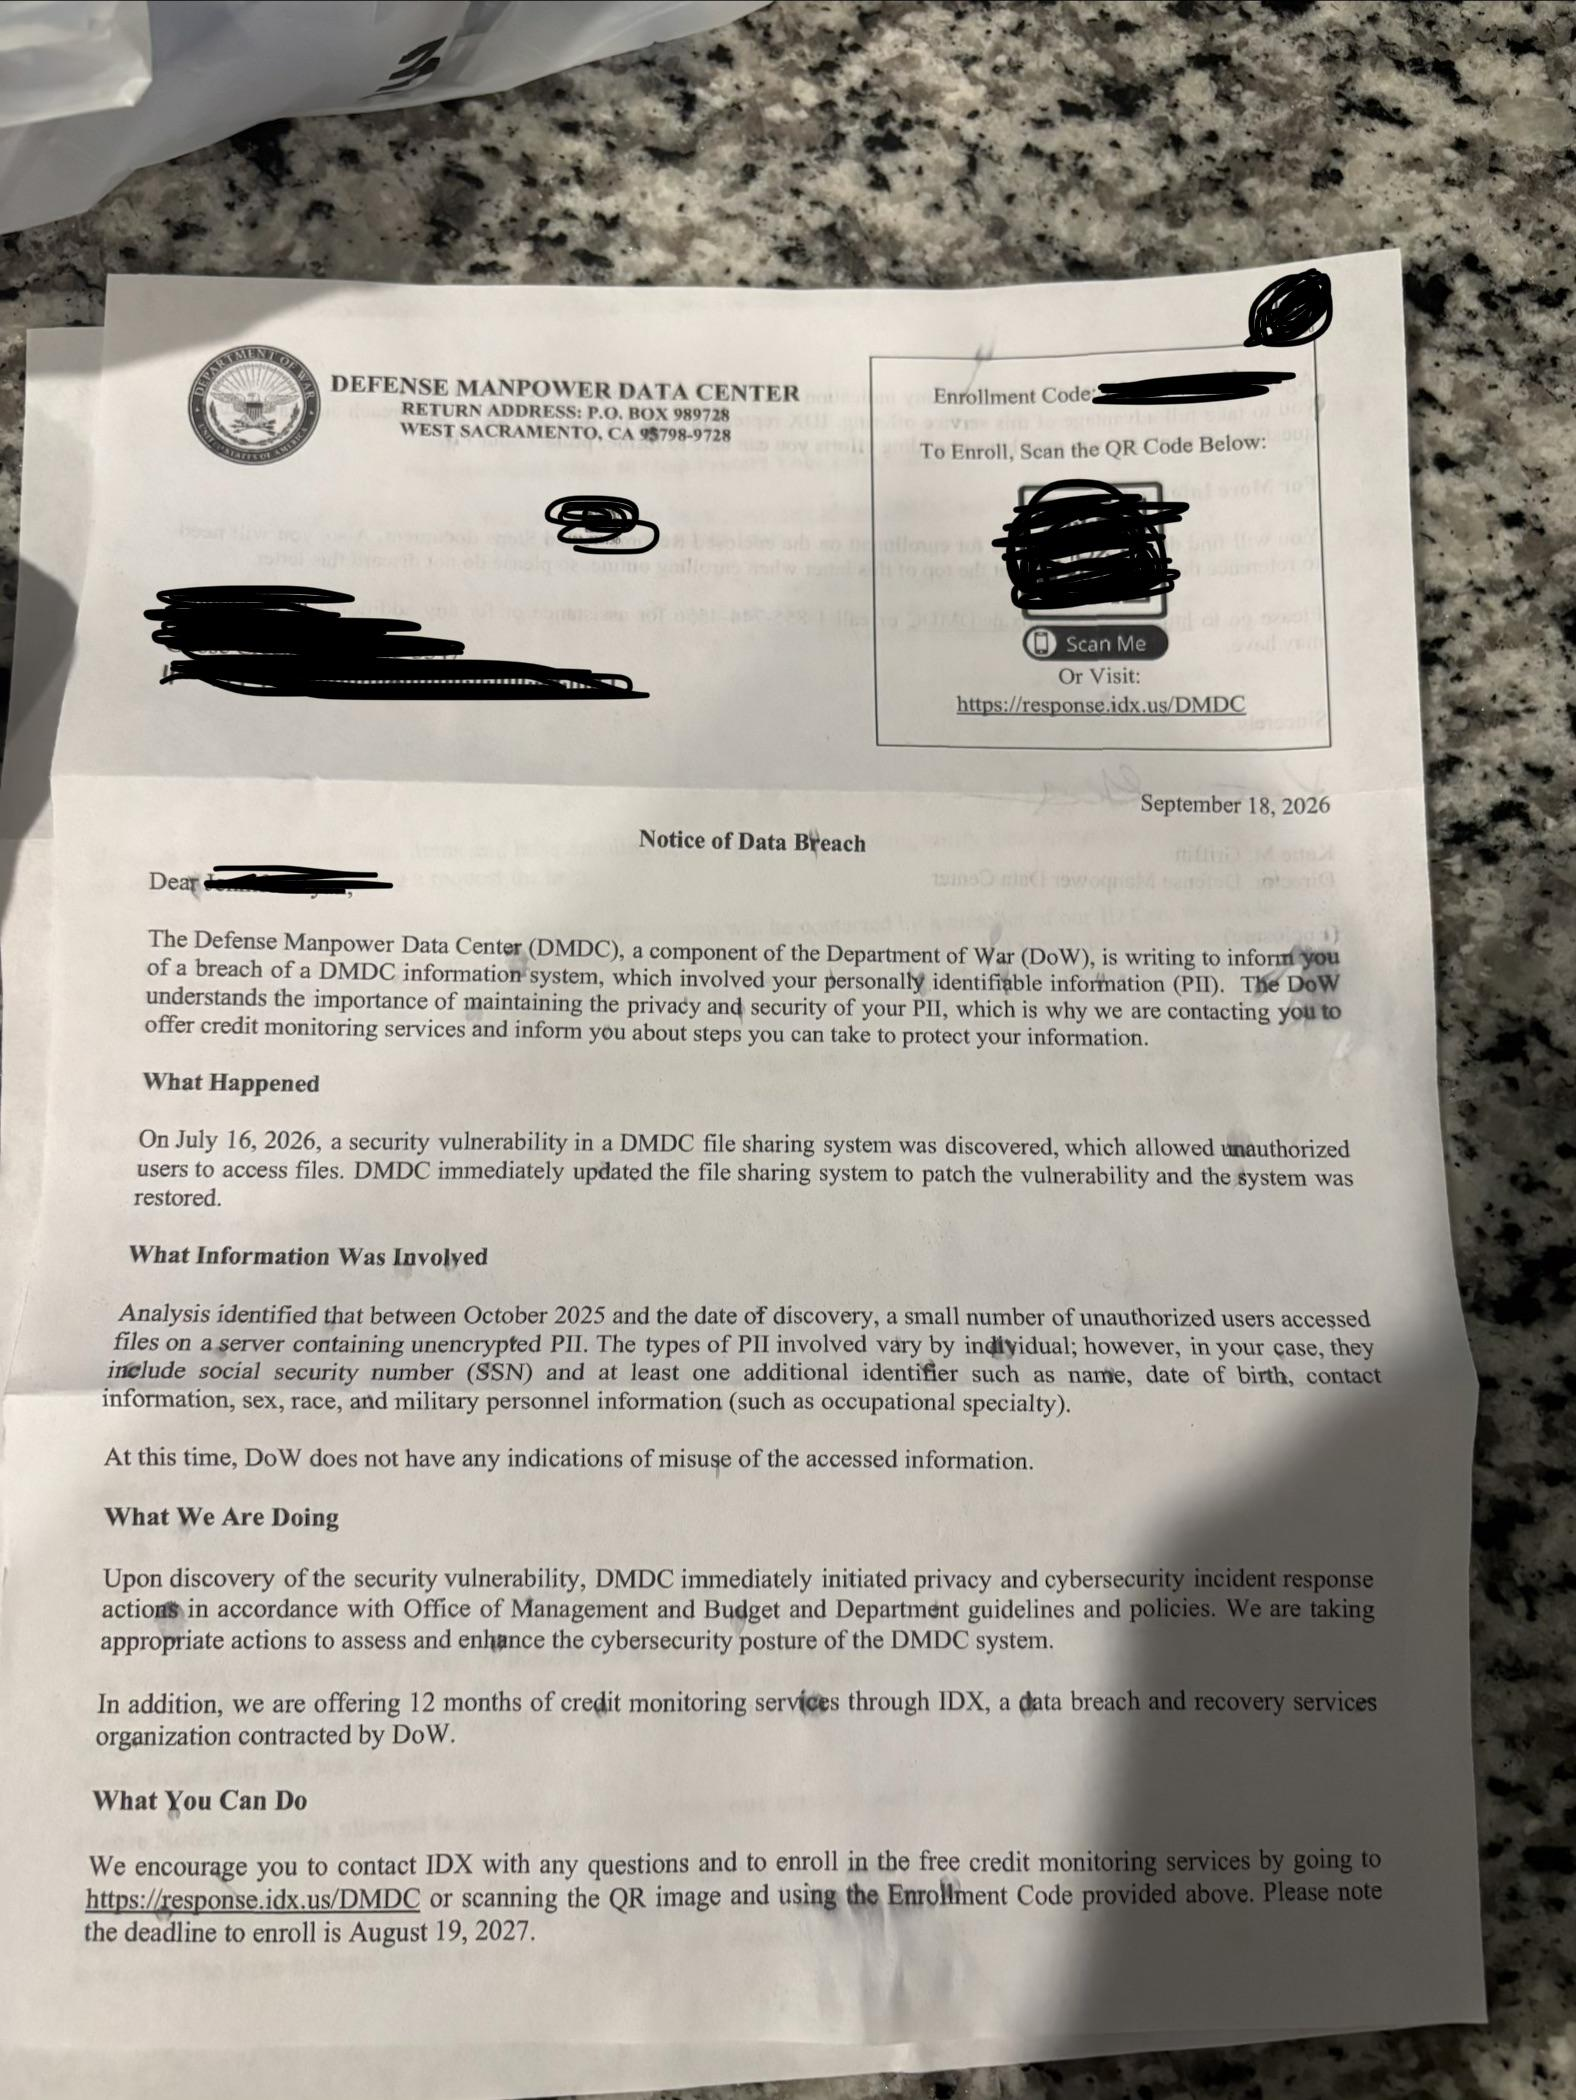
Pentagon personnel agency breach exposed data of 3 million people after attackers accessed a file-sharing server for about nine months. The U.S. Defense Manpower Data Center (DMDC), which maintains personnel records for the Department of Defense, is notifying people that their personal information was exposed in a data breach. According to the agency, unauthorized users […]
 Pierluigi Paganini
September 27, 2026
Kosovo national Ardit Kutleshi pleaded guilty to running Rydox, a cybercrime marketplace that sold stolen identities and credentials for years. Ardit Kutleshi, 28 years old and a citizen of Kosovo, pleaded guilty last week to building and running the cybercrime marketplace Rydox. The Rydox marketplace has been active since February 2016; it facilitated over 7,600 […]
 Pierluigi Paganini
September 22, 2026
North Korea-linked WaterPlum runs the Contagious Interview campaign, infecting over 30,000 devices using a fake job interview. On September 18, Japan’s National Police Agency, the FBI, the US Department of Defense’s Cyber Crime Center, and intelligence agencies from Australia and Germany published a joint advisory about a group called WaterPlum, better known as Contagious Interview. […]
 Pierluigi Paganini
September 14, 2026
China rejects Amodei’s AI slowdown proposal, calling it fearmongering and a US attempt to contain China’s technology sector. The debate over whether the world should slow down the development of advanced AI has quickly turned into something bigger than a technology argument. Dario Amodei, CEO of Anthropic, has called for a slower pace of development, […]
 Pierluigi Paganini
September 07, 2026
StyleSmuggler Magento zero-day is under active attack, letting unauthenticated attackers execute code and install backdoors on stores that may already be patched. A new zero-day flaw, dubbed StyleSmuggler, in Magento and Adobe Commerce is under active attack, giving unauthenticated attackers a path to run code on vulnerable online stores. Sansec researchers say it affects current […]
 Pierluigi Paganini
August 15, 2026
Hackers are exploiting a macOS Screen Sharing flaw to gain root access and install Monero miners on Macs with port 5900 exposed online. The Dutch National Cyber Security Centre confirmed active exploitation of a critical macOS authentication flaw, tracked as CVE-2026-65400 (CVSS score of 9.8), less than two weeks after Apple shipped the fix. The […]
 Pierluigi Paganini
August 13, 2026
Lazarus targets defense professionals with fake Lockheed Martin jobs, exploiting a Windows zero-day to deploy backdoors and evade security controls. Check Point Research has uncovered a new wave of Operation Dream Job, the long-running North Korean campaign that lures defense and aerospace professionals with convincing fake job offers. This iteration is more dangerous than previous […]
 Pierluigi Paganini
August 05, 2026
Brown Health Medical Group-MA breach exposed personal, medical, and financial data of over 311,000 individuals after hackers accessed its servers. Brown Health Medical Group-MA data breach exposed personal, medical, and financial data of over 311,000 individuals after hackers accessed its servers. The healthcare group identified a data security breach involving a legacy file server on […]
Pierluigi Paganini
July 12, 2026
An alleged Ryuk ransomware member pleaded guilty in the U.S. for helping deploy attacks on American companies and faces up to 15 years in prison. Armenian national Karen Serobovich Vardanyan (34) pleaded guilty in the U.S. for his role in Ryuk ransomware attacks targeting American organizations between 2019 and 2020. Extradited from Ukraine after his […]
Security / October 08, 2026

