 Pierluigi Paganini
 September 22, 2026
Check Point fixes an actively exploited flaw that lets unauthenticated attackers upload and run scripts on vulnerable Security Management Servers. Check Point has released emergency hotfixes for CVE-2026-93616, a critical path traversal flaw in its Security Management Server. Attackers can abuse the flaw without logging in to upload malicious scripts and execute them on vulnerable […]
 Pierluigi Paganini
September 22, 2026
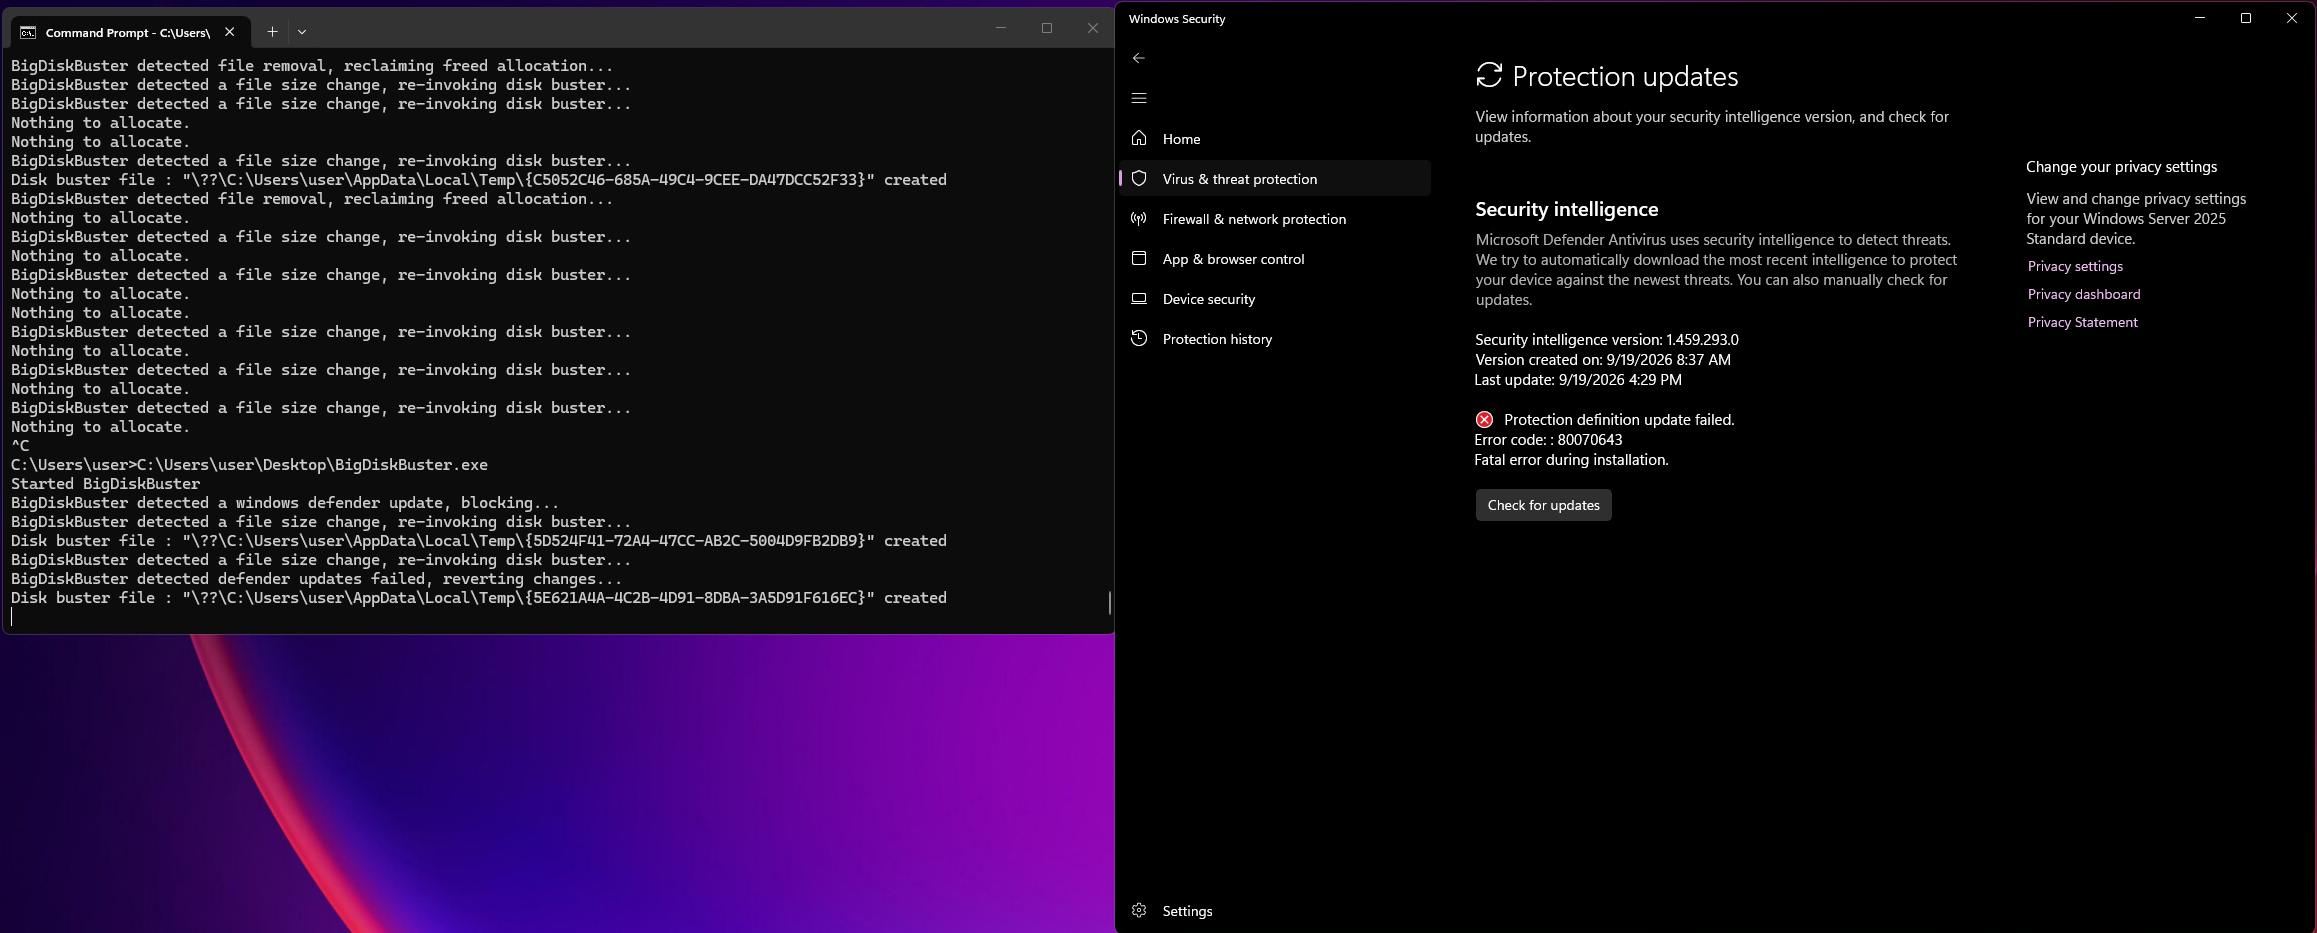
The researcher Chaotic Eclipse released BigDiskBuster, a PoC exploit for a Windows Defender Update DoS Zero-Day vulnerability. Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting Microsoft Defender. The researcher named the exploit BigDiskBuster, it triggers a Denial of Service Vulnerability in Windows Defender Update. The security researcher […]
 Pierluigi Paganini
September 22, 2026
A Veeam Agent flaw lets local users gain SYSTEM privileges. A public PoC is available, raising the risk of exploitation on shared Windows systems. If you’re running Veeam Agent on a Windows endpoint with more than one local user, now’s the time to check the version, not tomorrow. On September 14, 2026, public technical details […]
 Pierluigi Paganini
September 22, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Zyxel flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Zyxel GS1900 Series Switches flaw, tracked as CVE-2026-7273 (CVSS score of 8.8), to its Known Exploited Vulnerabilities (KEV) catalog. The flaw is a stack-based buffer overflow that could allow attackers […]
 Pierluigi Paganini
September 21, 2026
Ireland’s DPC fined Google €403 million over GDPR violations involving location data, transparency, retention and user control. Ireland’s Data Protection Commission (DPC) just fined Google €403 million, and the case behind it goes back six years, to a set of complaints that never really went away. The DPC launched the investigation in February 2020 after […]
 Pierluigi Paganini
September 21, 2026
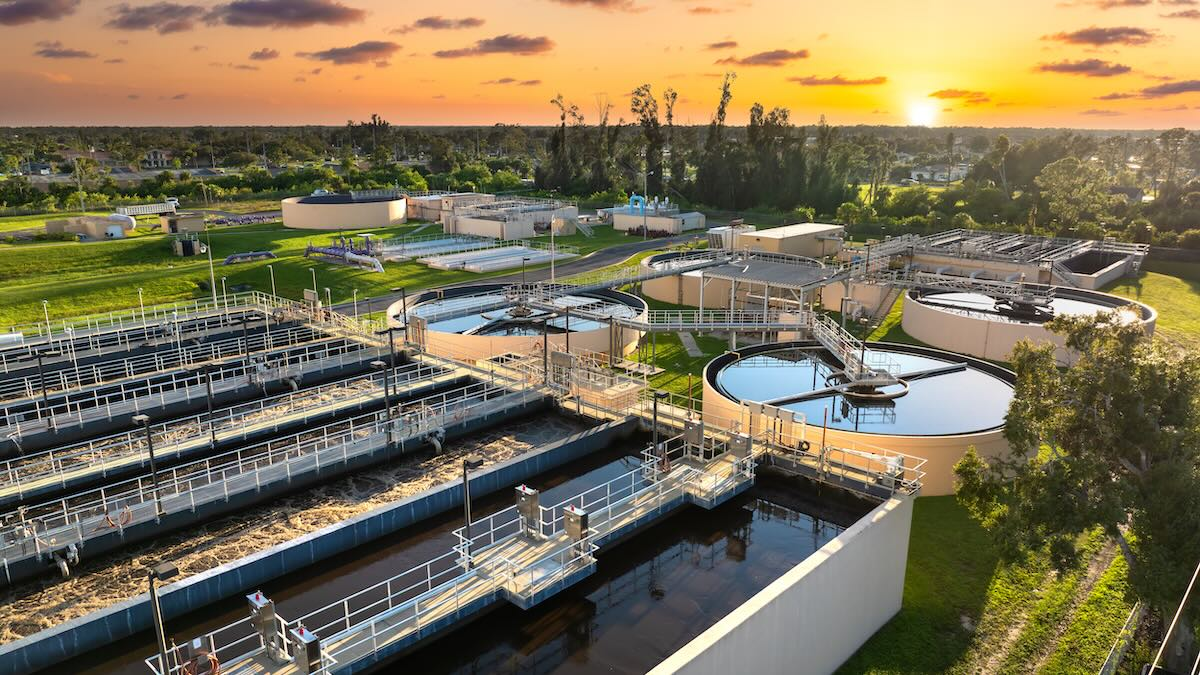
Hackers targeted two Colorado water utilities, changing OT settings and disabling alarms, but causing no impact on water services or safety. Foreign hackers targeted the operational technology (OT) systems of two small private water utilities in Colorado in late August, apparently trying to disrupt operations. Local authorities haven’t identified the affected utilities or the attackers. […]
 Pierluigi Paganini
September 21, 2026
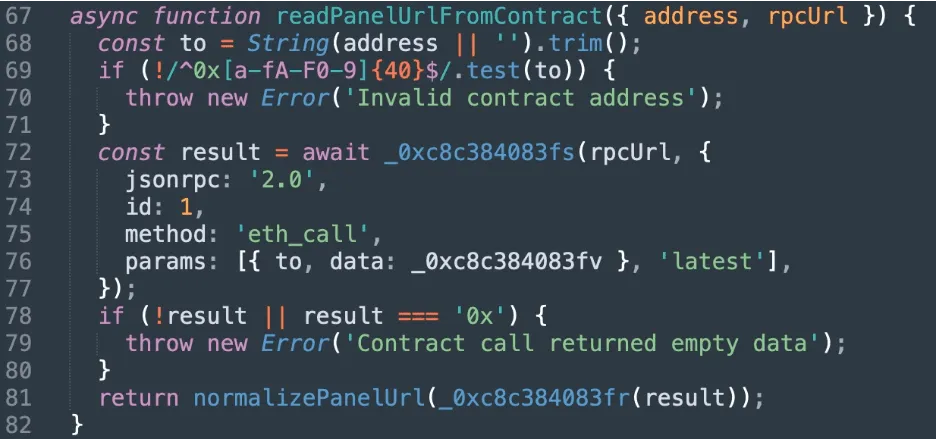
Blackpoint uncovers ChainScript, a Node.js RAT that queries a Polygon smart contract to find and rotate its command server. Blackpoint’s Adversary Pursuit Group was chasing a ClickFix campaign spreading an unknown RAT namend ChainScript. The malicious code is a previously undocumented Node.js remote access trojan that hides its command server on a public blockchain. The […]
 Pierluigi Paganini
September 21, 2026
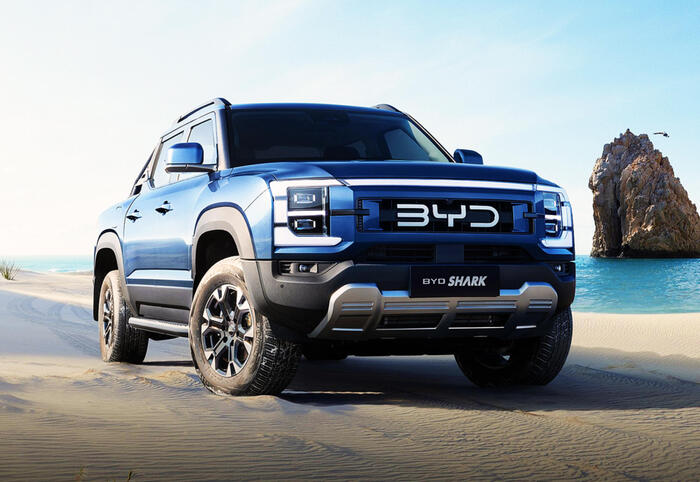
A BYD Shark 6 was remotely hacked, exposing vehicle controls, location tracking and cabin audio, raising serious connected-car security concerns. A journalist drove a BYD Shark 6 down a country road outside Canberra while a hacker sitting on the shoulder killed the headlights with a keystroke. That’s not a hypothetical. It’s what happened during a […]
 Pierluigi Paganini
September 21, 2026
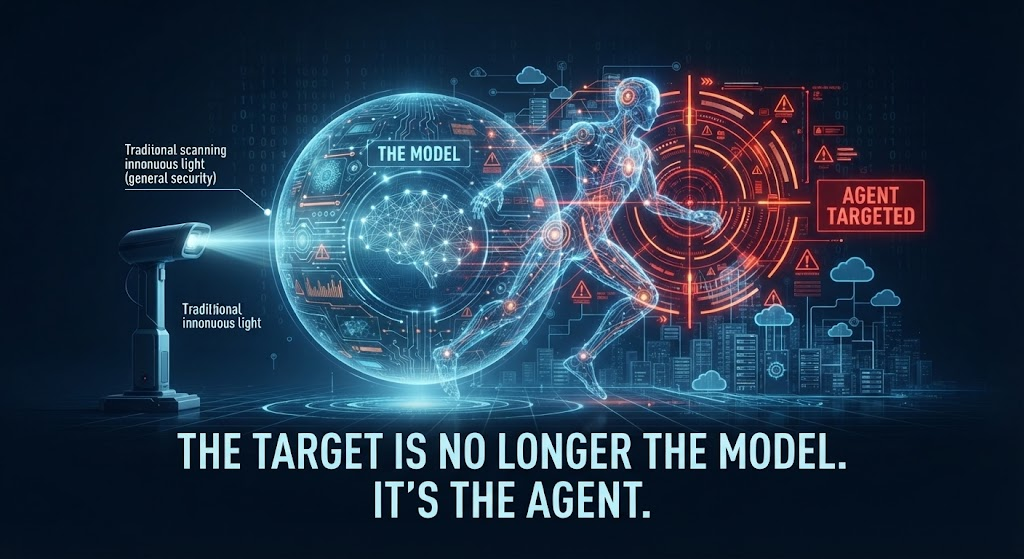
AI agents are becoming the new attack surface, exposed to poisoned skills, prompt injection, jailbreaks and attacks through connected tools. I read the AI security research published in a single month, February 2026, and when you put it all together, it’s not a list of curiosities. It’s a field guide to a new attack surface. […]
 Pierluigi Paganini
September 21, 2026
A 2017 UK assessment warned that police data on Microsoft Azure could face foreign access risks. The risks may still exist. A Guardian investigation has surfaced a 2017 document signed off by then City of London police commissioner Ian Dyson, who also held the title of senior information risk owner for the entire country. That […]
Data Breach / November 11, 2026
Malware / November 11, 2026