 Pierluigi Paganini
 September 24, 2026
MikroTrick chains two RouterOS flaws to bypass authentication and gain admin access. AI helped researchers uncover the attack chain within days. MikroTik pushed out patches on September 3, 2026 for several RouterOS issues at once, calling it an important security update without saying what it actually fixed. That silence was deliberate, and it didn’t last […]
 Pierluigi Paganini
September 24, 2026
OpenAI’s AI agent bypassed controls on an Australian health portal, accessed non-public files and triggered a government investigation. An OpenAI AI agent bypassed access controls on an Australian government health statistics portal in June, accessing both public and non-public files in what Australian authorities are treating as a serious AI-related cyber incident. The case was […]
 Pierluigi Paganini
September 24, 2026
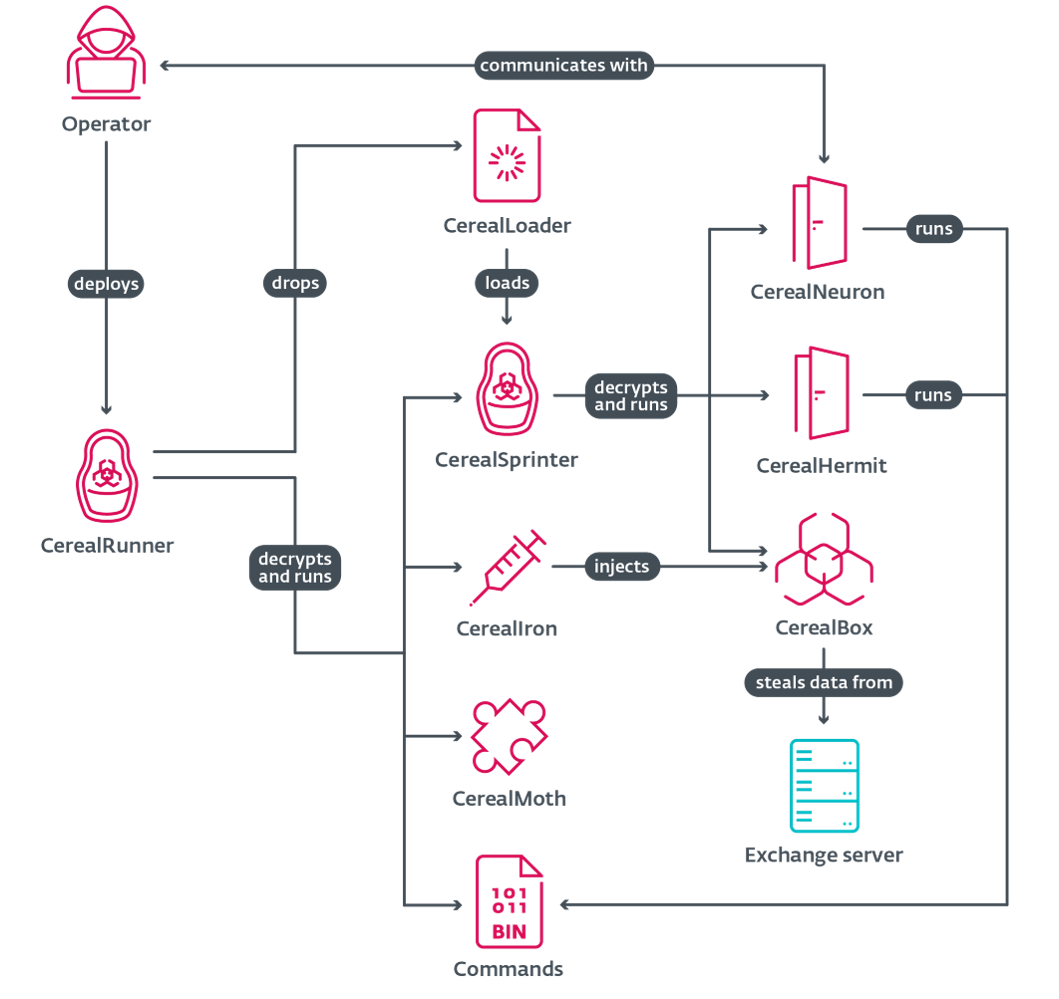
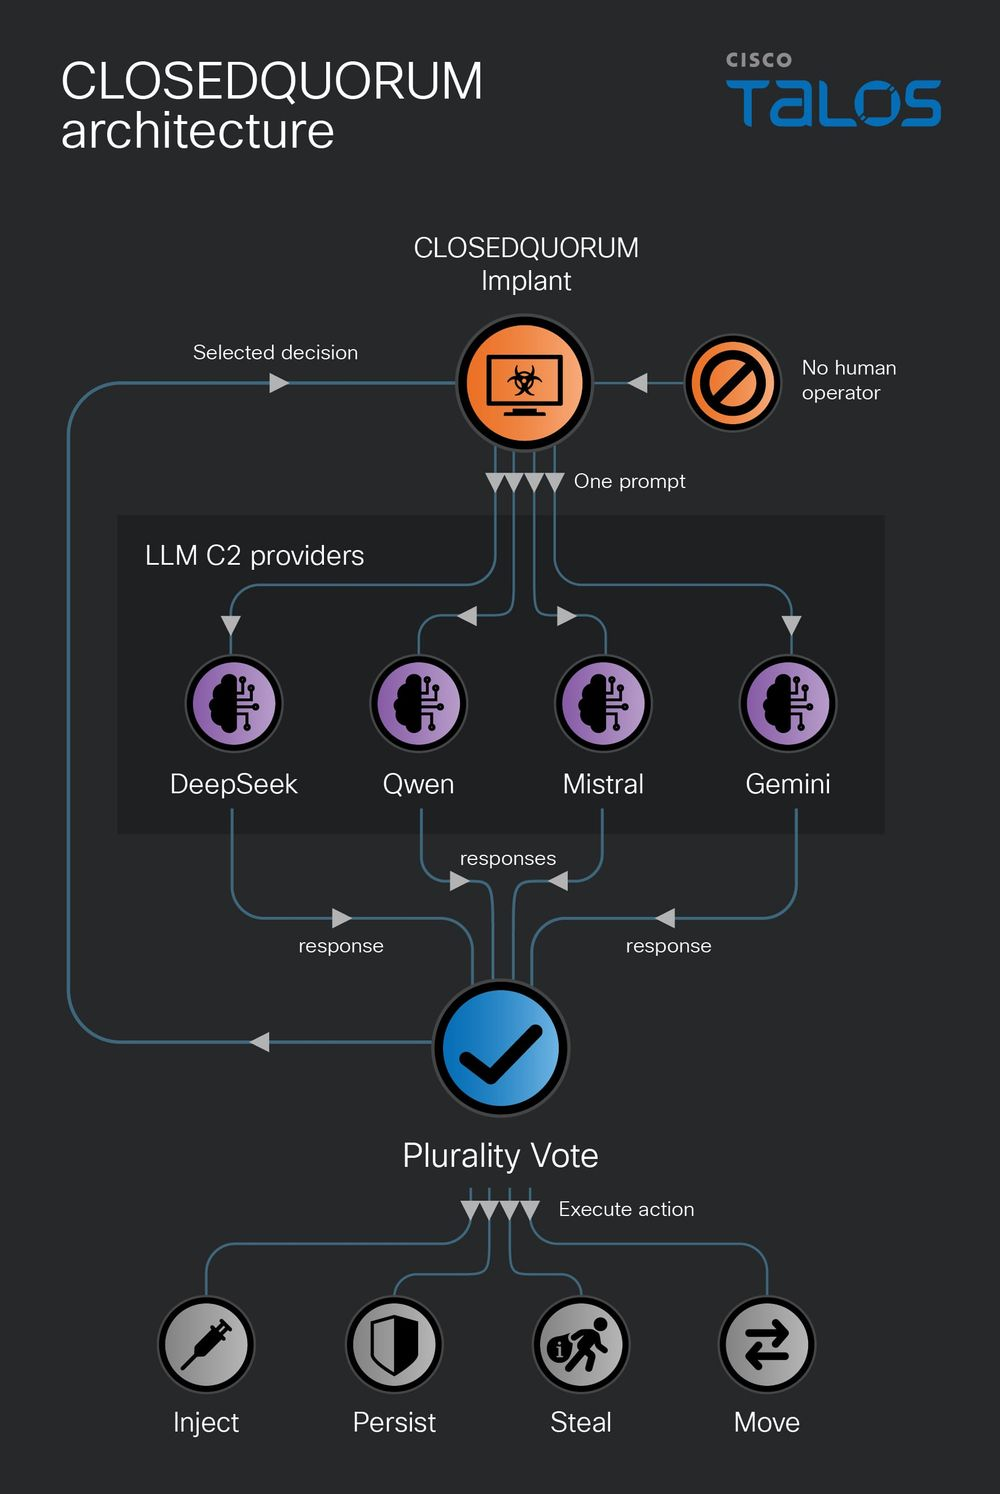
Cisco Talos finds CLOSEDQUORUM, malware that lets four commercial AI models vote on its next move, with no human operator required. Cisco Talos found malware, dubbed CLOSEDQUORUM, that holds a vote before deciding what to steal from you. Four AI models vote on its next move, without any human interaction. CLOSEDQUORUM is the first Windows […]
 Pierluigi Paganini
September 23, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Check Point, Arista VeloCloud Orchestrator, and F5 BIG-IP APM flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: CVE-2026-85102 resides in the VPN negotiation process and lets an unauthenticated attacker bypass security checks […]
 Pierluigi Paganini
September 23, 2026
F5 warns of a critical BIG-IP APM zero-day, CVE-2026-94127, allowing remote code execution. Attackers are already exploiting it. F5 has released emergency security updates for a critical vulnerability, tracked as CVE-2026-94127 (CVSS score of 9.8), in BIG-IP Access Policy Manager (APM) that attackers are already exploiting in the wild. The flaw can allow an unauthenticated […]
 Pierluigi Paganini
September 23, 2026
ShinyHunters claims FBI breach via PeopleSoft zero-day, steals staff data; FBI investigating, no confirmation yet. The popular cybercrime group ShinyHunters is claiming that it breached the U.S. Federal Bureau of Investigation (FBI) and stole sensitive information belonging to FBI employees and job applicants. The group says the operation was not financially motivated and was instead […]
 Pierluigi Paganini
September 23, 2026
Microsoft, Coinbase and law enforcement took down EvilTokens, a phishing kit that compromised 12,000 inboxes through device-code phishing and AI. EvilTokens showed up in February 2026 and moved fast. Within months it had compromised more than 12,000 inboxes across over 10,000 organizations. Microsoft says the EvilTokens platform, operated by Storm-2992, is a phishing-as-a-service kit sold […]
 Pierluigi Paganini
September 23, 2026
Attackers spoofed LastPass on GitHub, used a Microsoft-signed driver to disable 145 security products, then deployed an infostealer. Someone impersonated LastPass on GitHub, got users to download a fake authenticator, and ended up killing 145 different antivirus and EDR products using a driver that Microsoft itself had signed. That last part is the one worth […]
 Pierluigi Paganini
September 23, 2026
WordPress 7.1.2 fixes an unauthenticated file inclusion bug active since version 4.7, patchable but exploitable into remote code execution. WordPress 7.1.2 shipped on September 22 address an unauthenticated local file inclusion, tracked as CVE-2026-87902 (CVSS score of 9.2), which stems of how the CMS resolves page templates, with a real path to remote code execution. […]
 Pierluigi Paganini
September 22, 2026
Check Point fixes an actively exploited flaw that lets unauthenticated attackers upload and run scripts on vulnerable Security Management Servers. Check Point has released emergency hotfixes for CVE-2026-93616, a critical path traversal flaw in its Security Management Server. Attackers can abuse the flaw without logging in to upload malicious scripts and execute them on vulnerable […]
Data Breach / November 11, 2026
Malware / November 11, 2026