


 Pierluigi Paganini
 July 28, 2026
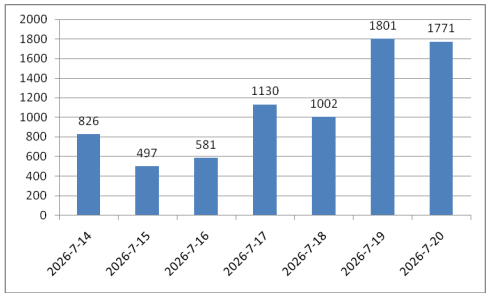
Researchers uncovered the 200,000-device Dysphoria botnet, which uses Ethereum and Solana domains to hide its command servers. QiAnXin XLab, jointly with China’s CNCERT, disclosed Dysphoria, a botnet that has compromised roughly 200,000 devices worldwide and uses Ethereum and Solana blockchain domain names to hide its command infrastructure. The botnet evolved from jackskid and fbot malware […]
 Pierluigi Paganini
July 28, 2026
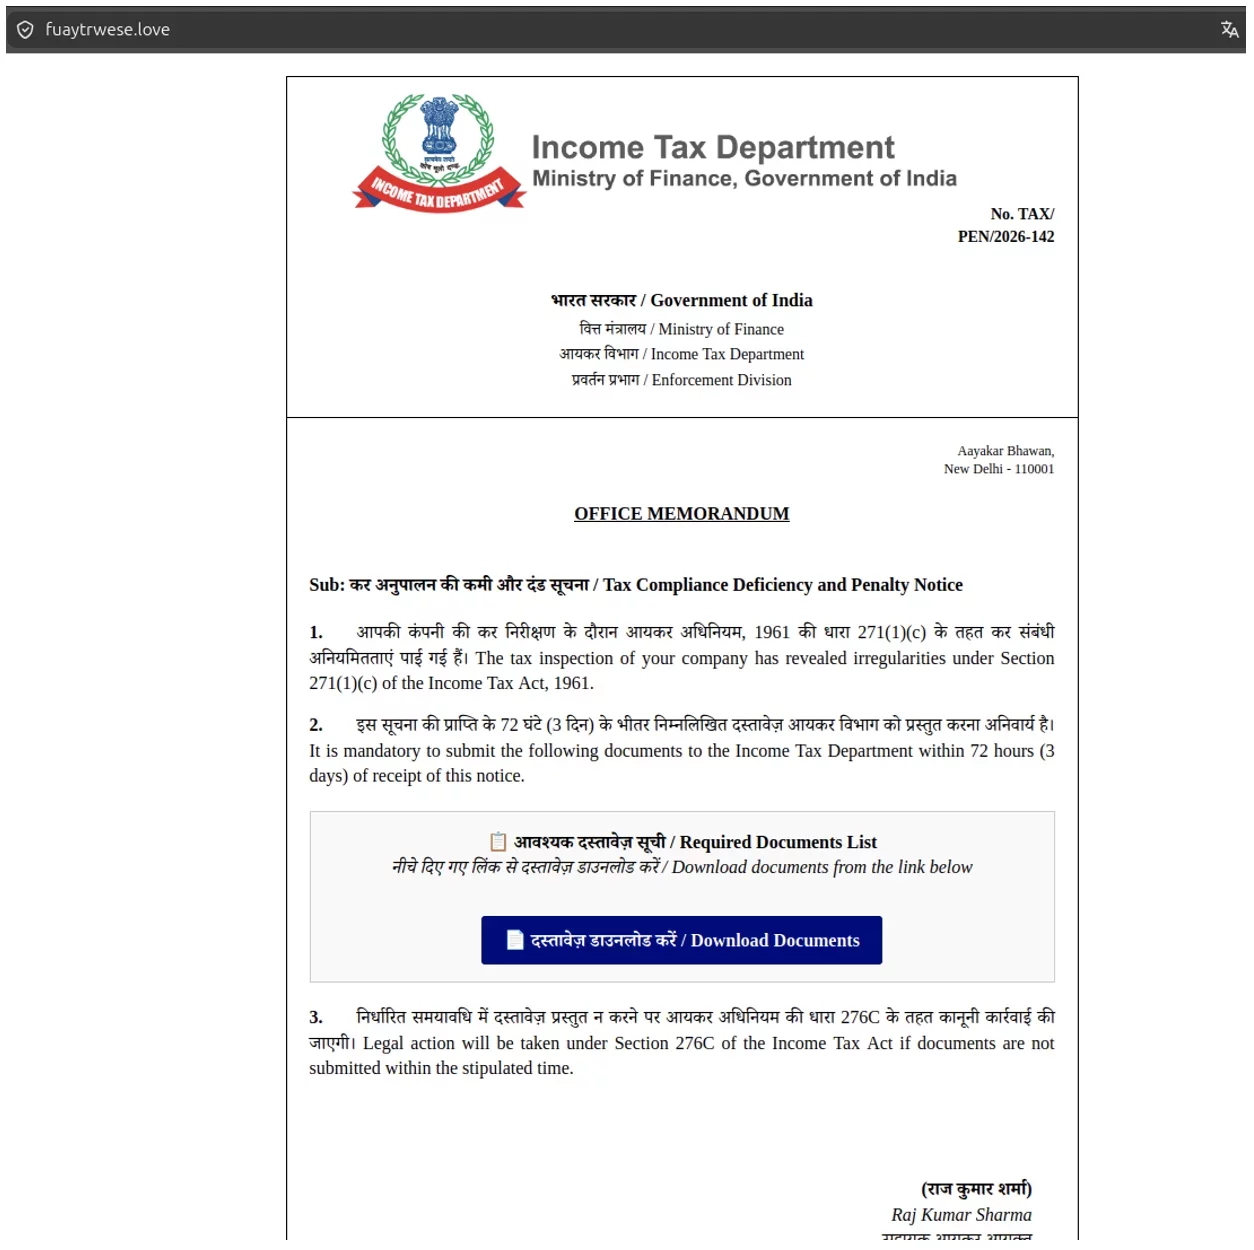
Proofpoint uncovered Cruciferra, a crypter-as-a-service that helps hackers evade antivirus and deliver malware in multiple campaigns. Proofpoint’s research team traced a wave of income-tax-themed lures targeting Indian taxpayers, tax professionals, and corporate finance teams back to a crypter service called Cruciferra, and the tool turns out to be shared infrastructure used across multiple unrelated criminal […]
 Pierluigi Paganini
July 27, 2026
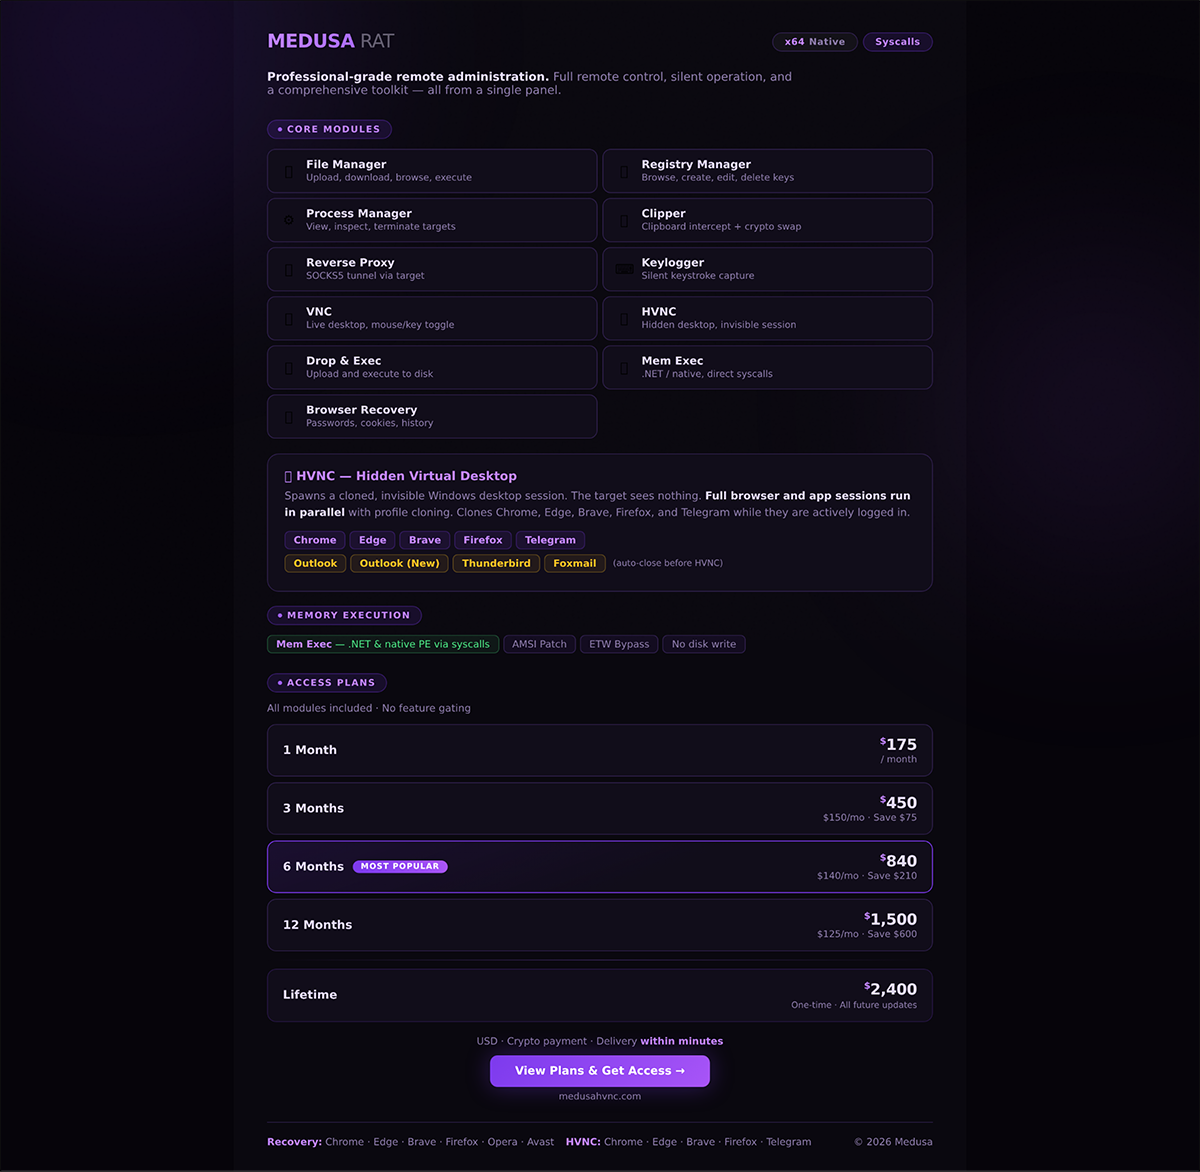
MedusaHVNC RAT uses hidden Windows desktops to remotely control browsers, steal data, and evade detection through legitimate system features. Windows has always supported hidden desktops as a legitimate feature, useful for specialized software that needs a workspace the user never touches. It’s a niche capability most people never think about, buried deep in how the […]
 Pierluigi Paganini
July 27, 2026
DentaQuest disclosed a data breach that may have exposed the personal and dental health information of more than 23 million people. DentaQuest is notifying more than 23 million people of a data breach after hackers accessed its network in May 2026. The incident may have exposed customers’ personal information and dental health data. DentaQuest, part […]
 Pierluigi Paganini
July 27, 2026
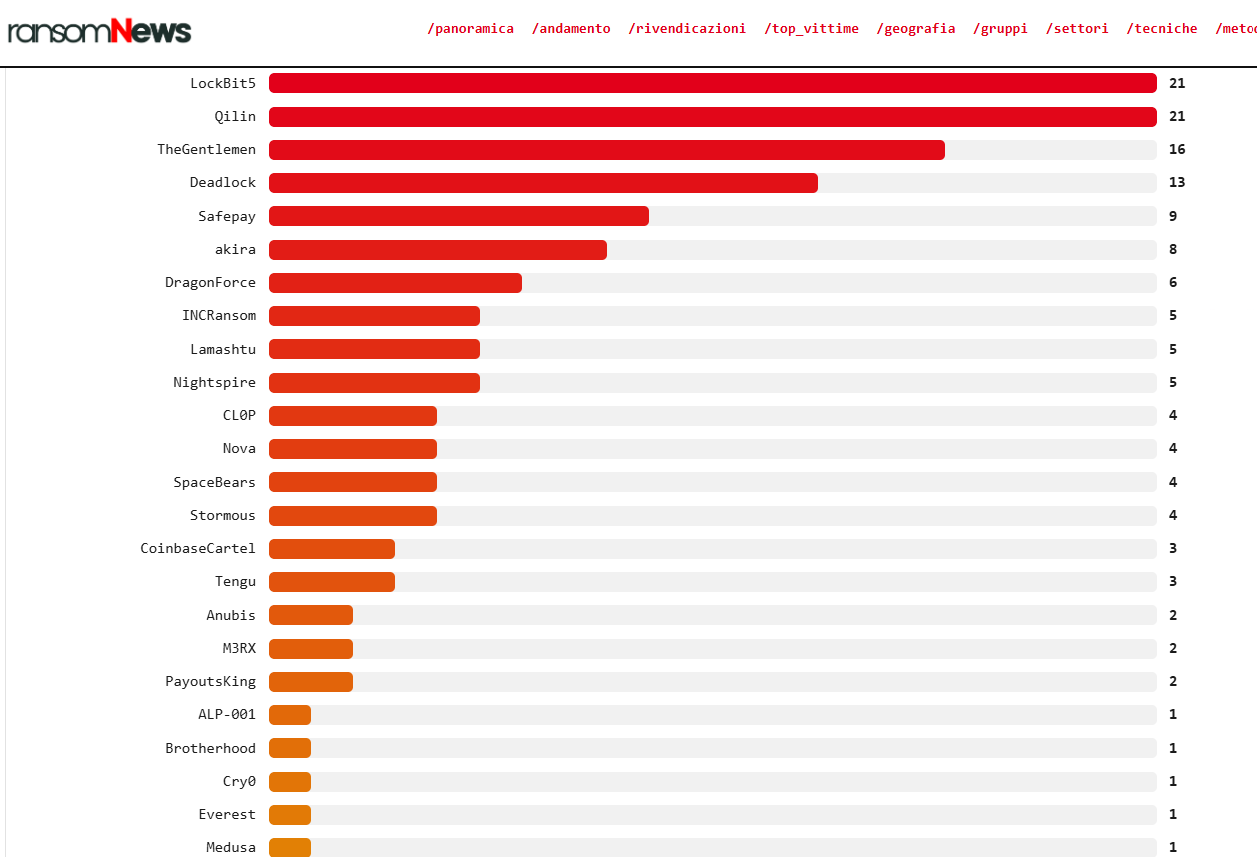
A new report links 148 ransomware attacks to Italian organizations in H1 2026, with manufacturing the most targeted sector. Six months, 148 confirmed ransomware claims against Italian targets, and one sector taking the brunt of it. That’s the headline number from a new semi-annual tracker compiled by ransomNews under its RedACT project, which pulls together […]
 Pierluigi Paganini
July 25, 2026
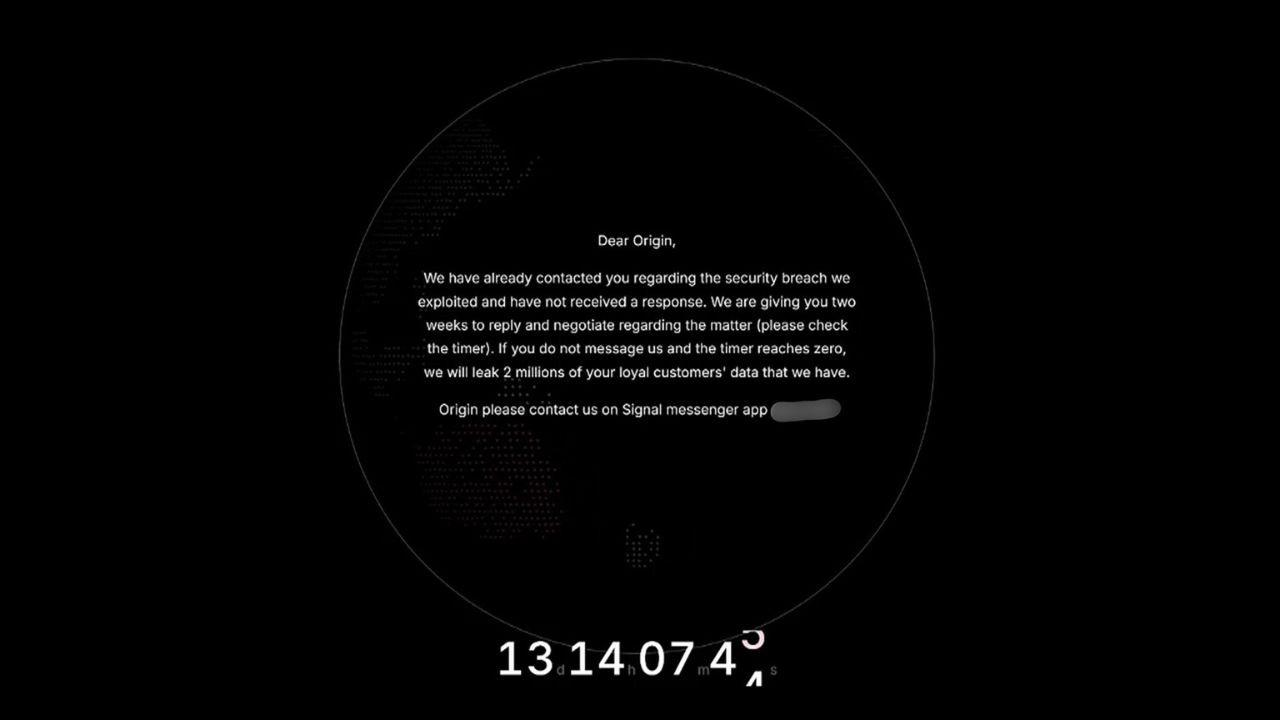
Origin Energy confirmed a data breach after a hacker claimed to have stolen data from 2 million customers and threatened to leak it. Origin Energy disclosed a cyberattack that exposed customer data after a hacker claimed to have stolen records belonging to 2 million customers and threatened to publish them. An alleged hacker calling themselves […]
 Pierluigi Paganini
July 23, 2026
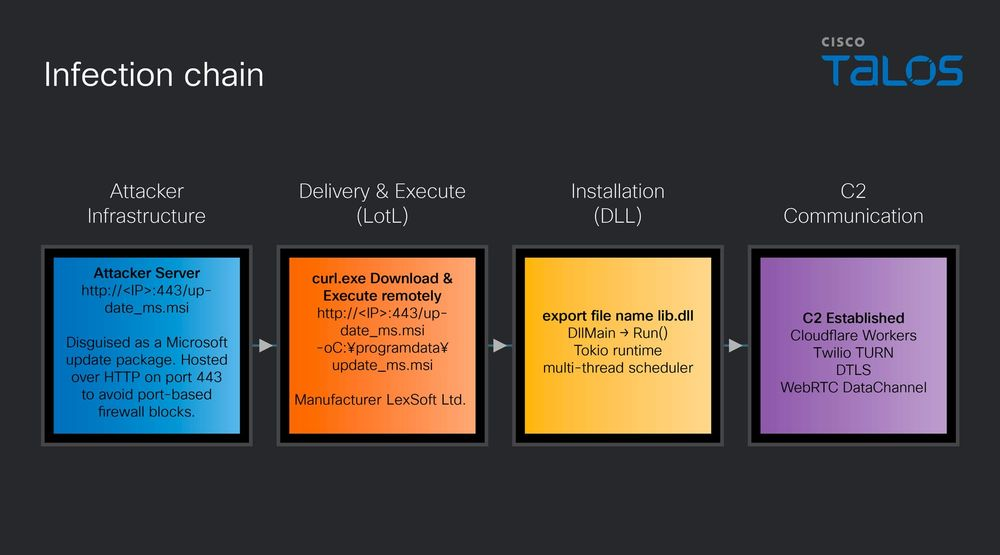
Cisco Talos uncovered msaRAT, a Chaos ransomware RAT that hides C2 traffic by routing it through Chrome or Edge using the Chrome DevTools Protocol. Cisco Talos disclosed msaRAT, a Rust-based remote access trojan attributed to the Chaos ransomware group that routes its entire command-and-control channel through the victim’s own Chrome or Edge browser. The malware […]
 Pierluigi Paganini
July 21, 2026
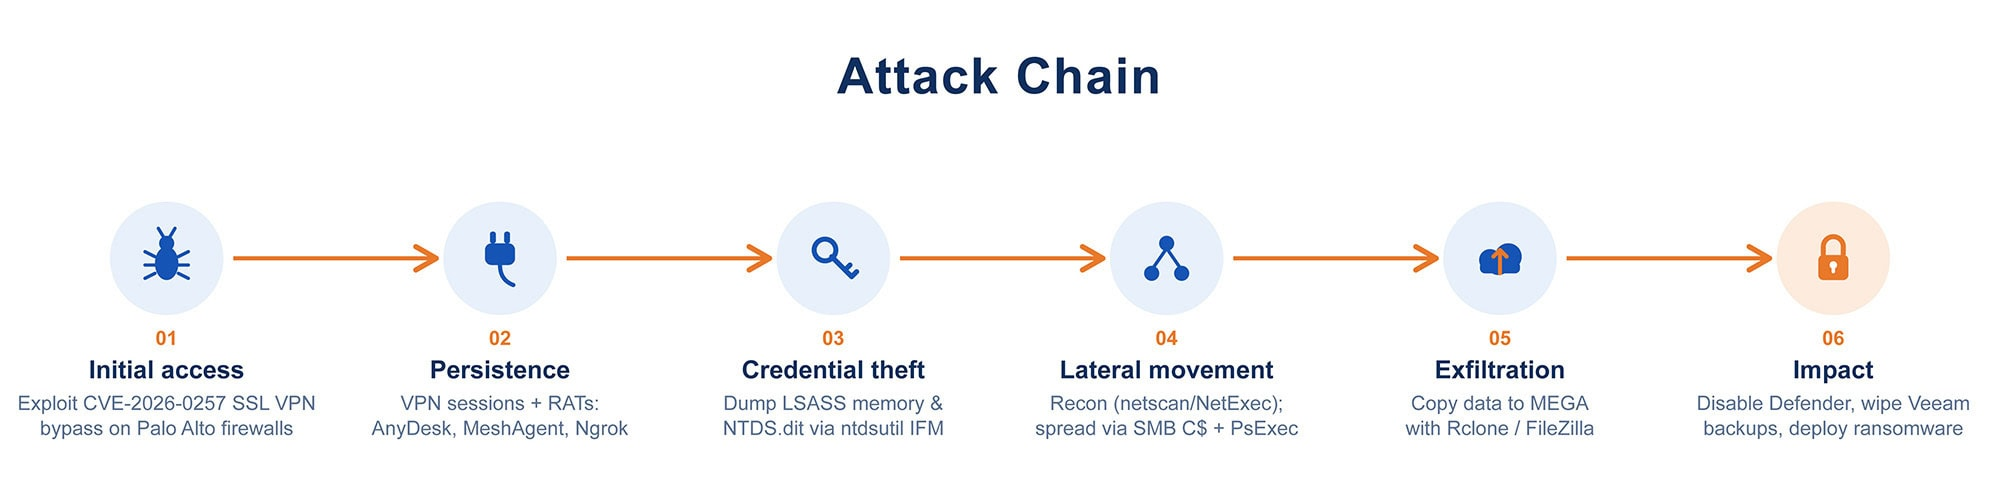
Qilin ransomware exploits the PAN-OS GlobalProtect flaw CVE-2026-0257 to gain unauthorized VPN access to unpatched networks. Arctic Wolf researchers warn that the Qilin ransomware gang is exploiting the critical PAN-OS GlobalProtect vulnerability CVE-2026-0257 to compromise corporate networks. CVE-2026-0257 is a PAN-OS authentication bypass vulnerability affecting GlobalProtect portals and gateways. Palo Alto Networks addressed the vulnerability on May […]
 Pierluigi Paganini
July 19, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter CrashStealer: C++ macOS infostealer posing as crash reporter Lucide Proxy: Turning Student Web Proxies into DDoS Bots AsyncAPI npm organization compromised, 2M weekly downloads affected OkoBot: new sophisticated malware framework targets cryptocurrency users […]
 Pierluigi Paganini
July 17, 2026
Ernst & Young (EY) disclosed a data breach after attackers compromised a third-party IT support system containing client documents and tax information. Ernst & Young (EY) is disclosed a data breach linked to a compromised third-party support ticket system used by its IT teams. The platform stored support requests that may have included documents containing […]






