


 Pierluigi Paganini
 July 17, 2026
A cyberattack hit one of Japan’s largest food companies, Nichirei, disrupting logistics and shipments. The company is gradually restoring operations. Nichirei is one of Japan’s largest food companies, best known for its frozen food business. Founded in 1942 and headquartered in Tokyo, it operates globally through dozens of subsidiaries. The food giant confirmed that the […]
 Pierluigi Paganini
July 17, 2026
Russian-speaking UAT-11795 spreads trojanized Zoom, Webex, and MobaXterm installers to deliver Starland RAT and the WLDR memory-only implant. Cisco Talos researchers published a detailed technical report on July 16 disclosing UAT-11795, a financially motivated, Russian-speaking threat actor that has been running a malware campaign against users in the United States and Europe since at least […]
 Pierluigi Paganini
July 16, 2026
Two members of the Scattered Spider cybercrime group received jail sentences in the UK for the 2024 cyberattack on Transport for London. A UK court sentenced two Scattered Spider members, Thalha Jubair (20) and Owen Flowers (18), for their role in the 2024 cyberattack on Transport for London (TfL). Transport for London (TfL) is a local […]
 Pierluigi Paganini
July 15, 2026
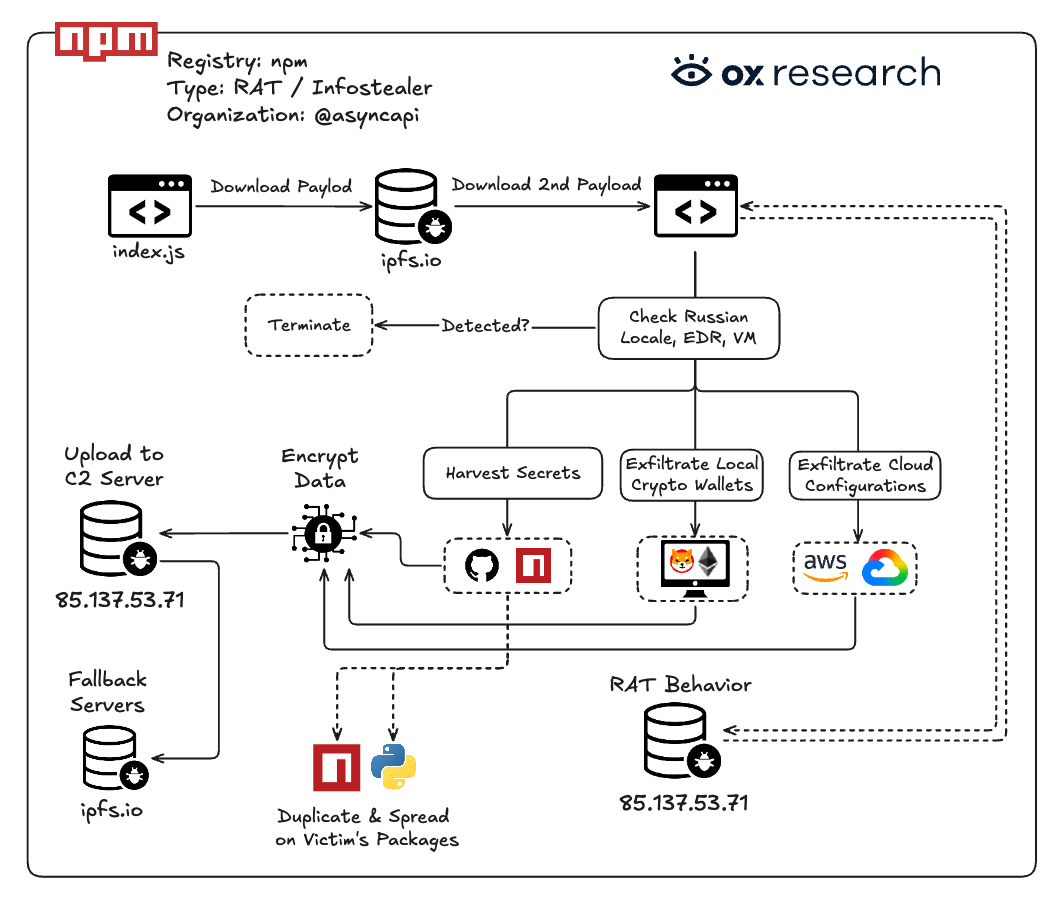
AsyncAPI npm packages with 2M weekly downloads were compromised, spreading malware with info-stealing, crypto-theft and RAT capabilities. OX Security researchers disclosed on July 14 that the AsyncAPI npm organization was compromised, with malicious code injected into four packages that together account for over 2 million weekly downloads. The affected versions are @asyncapi/generator 3.3.1, @asyncapi/generator-components 0.7.1, […]
 Pierluigi Paganini
July 14, 2026
Japan’s largest taxi operator Nihon Kotsu shut down systems after a malware attack, disrupting dispatch and bookings. Nihon Kotsu, Japan’s largest taxi company, disclosed on July 13, 2026 that its internal systems suffered an unauthorized external access involving malware infection in the early morning hours of Saturday, July 11. The company immediately shut down systems […]
 Pierluigi Paganini
July 14, 2026
New macOS infostealer CrashStealer uses a signed app to bypass Gatekeeper, steals credentials and wallets, then AES-encrypts stolen data. Jamf Threat Labs first spotted CrashStealer in early May 2026 as a suspicious macOS sample uploaded to VirusTotal. By early July, in-the-wild detections confirmed the malware had moved from development into active deployment. The malware is […]
 Pierluigi Paganini
July 13, 2026
Lidl disclosed a third-party data breach affecting online shop customers in Germany, Belgium, and the Netherlands. Payment data was not exposed. Lidl contacted customers of its online shop in Germany, Belgium, and the Netherlands last week to inform them that their personal data had been stolen in an attack on an external IT service provider. […]
 Pierluigi Paganini
July 13, 2026
Dutch police suspect local hackers behind the Odido breach that exposed 6M customers after a phishing attack and seek public help identifying them. Dutch police have identified strong indications that Dutch nationals were involved in the February 2026 cyberattack on telecom provider Odido, which resulted in data from more than six million customers being stolen […]
 Pierluigi Paganini
July 13, 2026
Australia warns of a global campaign exploiting CMS flaws to deploy webshells on WordPress, Joomla, and other websites. Australia’s Signals Directorate has issued an alert about a large-scale exploitation campaign actively targeting content management systems (CMS) worldwide, with many small and medium-sized Australian businesses already hit. Attackers are scanning websites for known vulnerabilities, deploying webshells […]
 Pierluigi Paganini
July 10, 2026
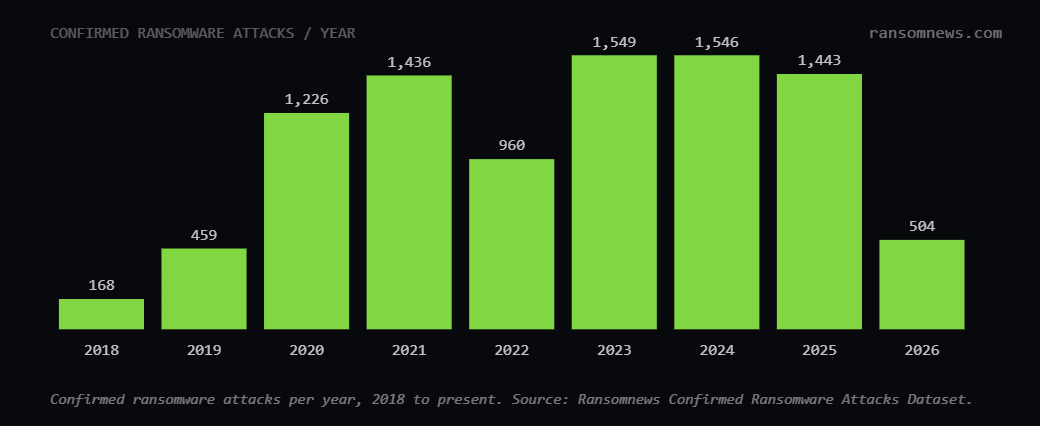
Ransomware remains above 1,400 attacks yearly since 2023. Qilin leads in 2026, while the U.S. remains the main target. Ransomnews has independently confirmed 9,291 ransomware attacks worldwide between January 2018 and July 2026, tracking incidents only when verified through victim disclosures, regulatory filings, official statements, or credible press reporting. Leak-site listings alone don’t qualify, operators […]






