 Pierluigi Paganini
 August 15, 2023
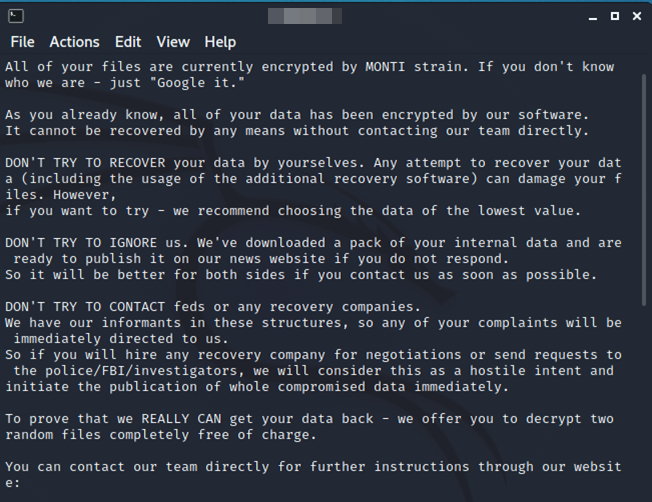
Monti Ransomware operators returned, after a two-month pause, with a new Linux variant of their encryptor. The Monti ransomware operators returned, after a two-month break, with a new Linux version of the encryptor. The variant was employed in attacks aimed at organizations in government and legal sectors. The Monti group has been active since June 2022, […]
 Pierluigi Paganini
August 15, 2023
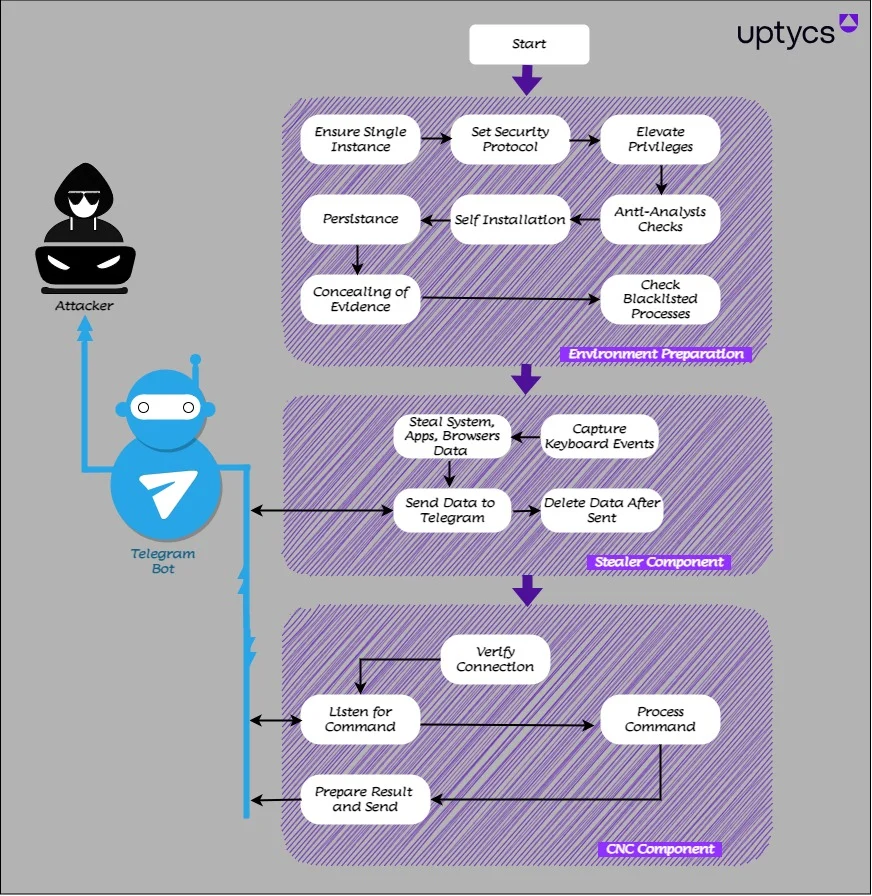
QwixxRAT is a new Windows remote access trojan (RAT) that is offered for sale through Telegram and Discord platforms. The Uptycs Threat Research team discovered the QwixxRAT (aka Telegram RAT) in early August 2023 while it was advertised through Telegram and Discord platforms. The RAT is able to collect sensitive data and exfiltrate them by […]
 Pierluigi Paganini
August 14, 2023
Experts warn of ongoing attacks, dubbed Xurum, targeting e-commerce websites using Adobe’s Magento 2 CMS. Akamai researchers warn of ongoing attacks, dubbed Xurum, targeting e-commerce websites running the Magento 2 CMS. The attackers are actively exploiting a server-side template injection issue, tracked as CVE-2022-24086, (CVSS score: 9.8), in Adobe Commerce and Magento Open Source. The […]
 Pierluigi Paganini
August 12, 2023
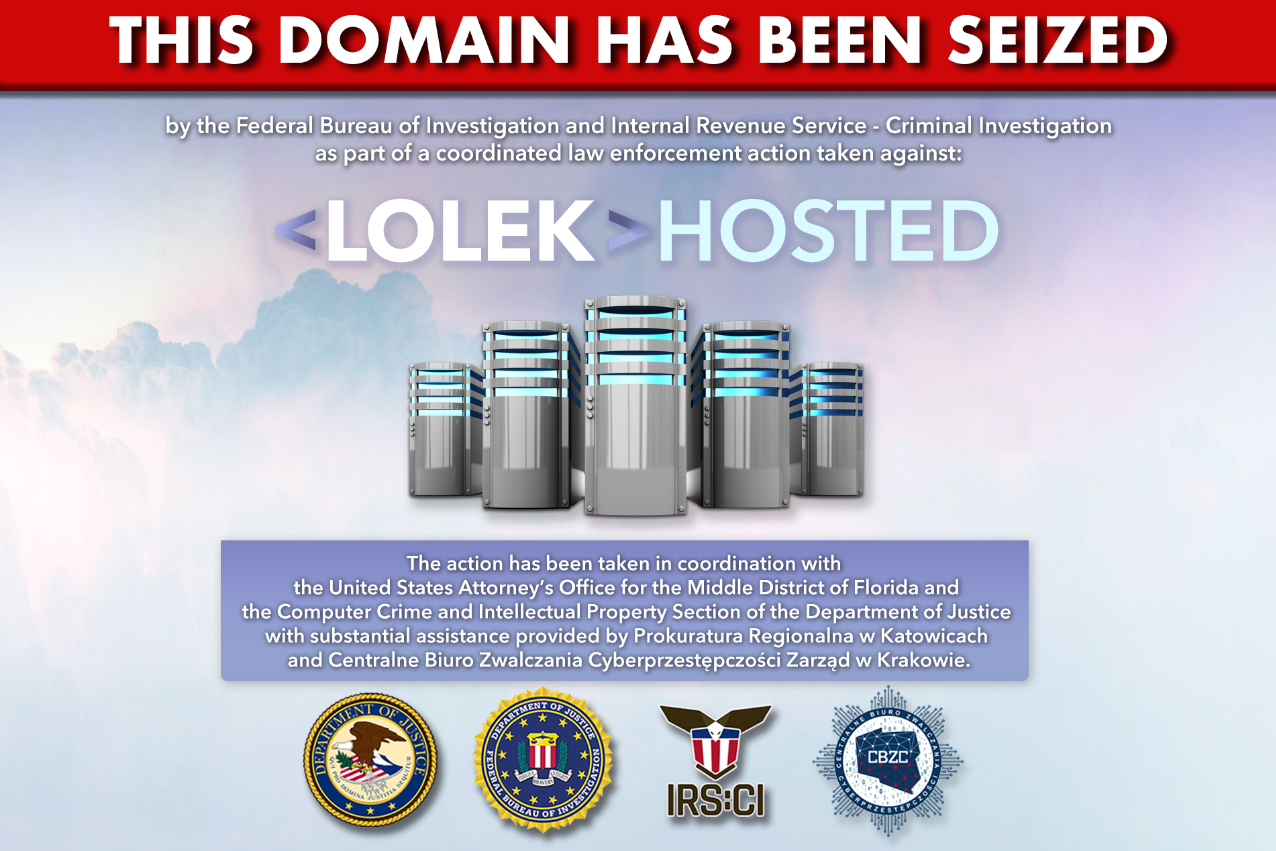
A joint operation conducted by European and U.S. law enforcement agencies dismantled the bulletproof hosting service provider Lolek Hosted. Lolek Hosted is a bulletproof hosting service provider used to facilitate the distribution of information-stealing malware, and also to launch DDoS (distributed denial of service) attacks, manage fictitious online shops, manage botnet servers and distribute spam messages […]
 Pierluigi Paganini
August 12, 2023
Threat actors employed a new variant of the SystemBC malware, named DroxiDat, in attacks aimed at African critical infrastructure. Researchers from Kaspersky’s Global Research and Analysis Team (GReAT) reported that an unknown threat actor used a new variant of the SystemBC proxy malware, named DroxiDat, in an attack against a power generation company in southern Africa. SystemBC was […]
 Pierluigi Paganini
August 11, 2023
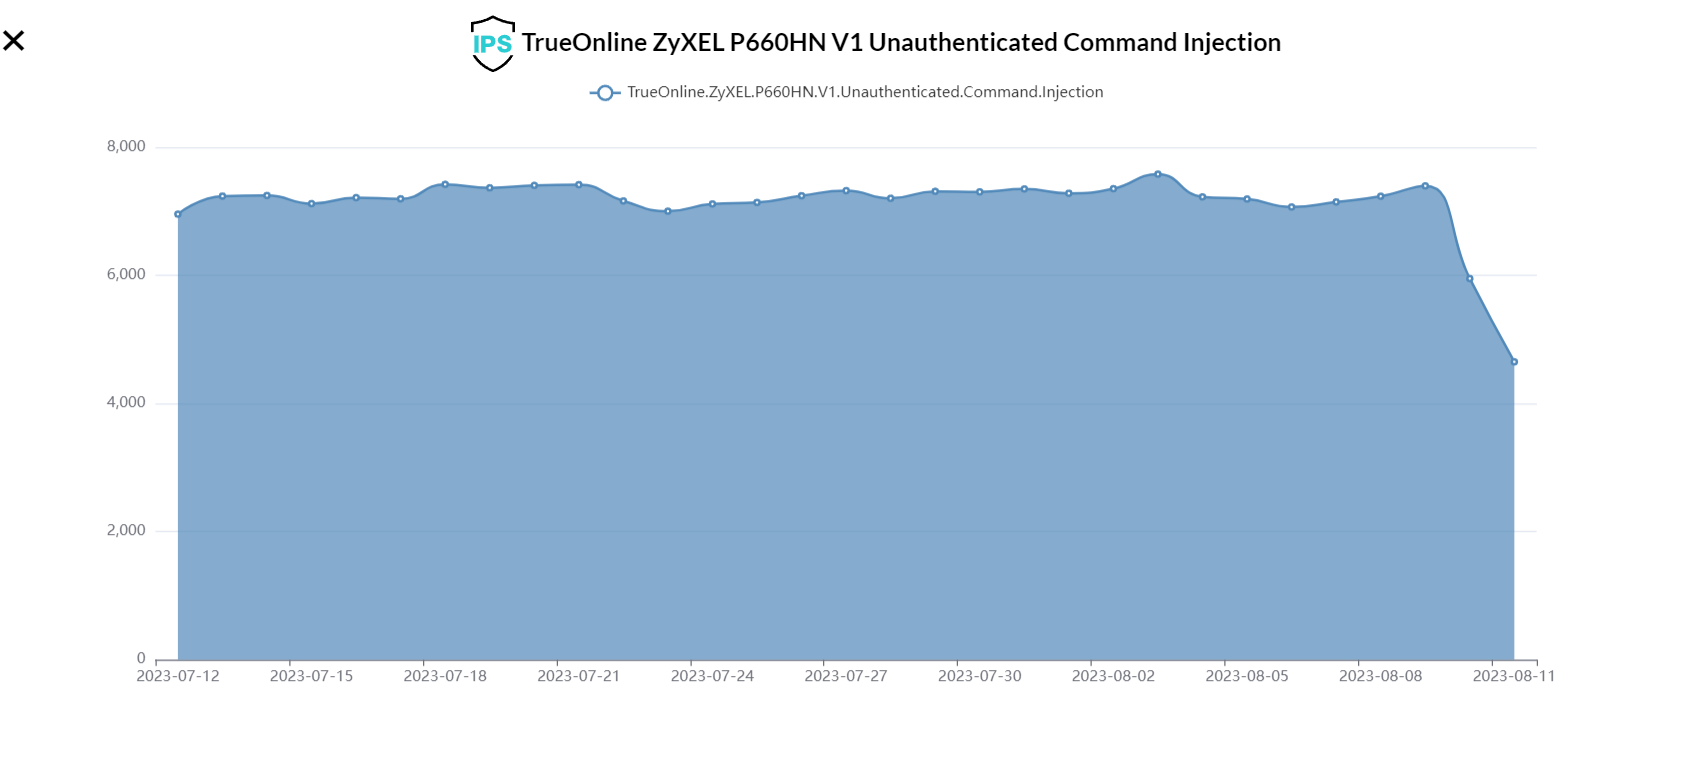
Researchers warn that the Gafgyt botnet is actively exploiting a vulnerability impacting the end-of-life Zyxel P660HN-T1A router. A variant of the Gafgyt botnet is actively attempting to exploit a vulnerability, tracked as CVE-2017-18368 (CVSS v3: 9.8), impacting the end-of-life Zyxel P660HN-T1A router. The flaw is a command injection vulnerability that resides in the Remote System Log […]
 Pierluigi Paganini
August 09, 2023
The Balada Injector is still at large and still evading security software by utilizing new domain names and using new obfuscation. During a routine web monitoring operation, we discovered an address that led us down a rabbit hole of WordPress-orientated “hack waves” caused by the Balada Injector malware. This evidence suggests that the malware is […]
 Pierluigi Paganini
August 09, 2023
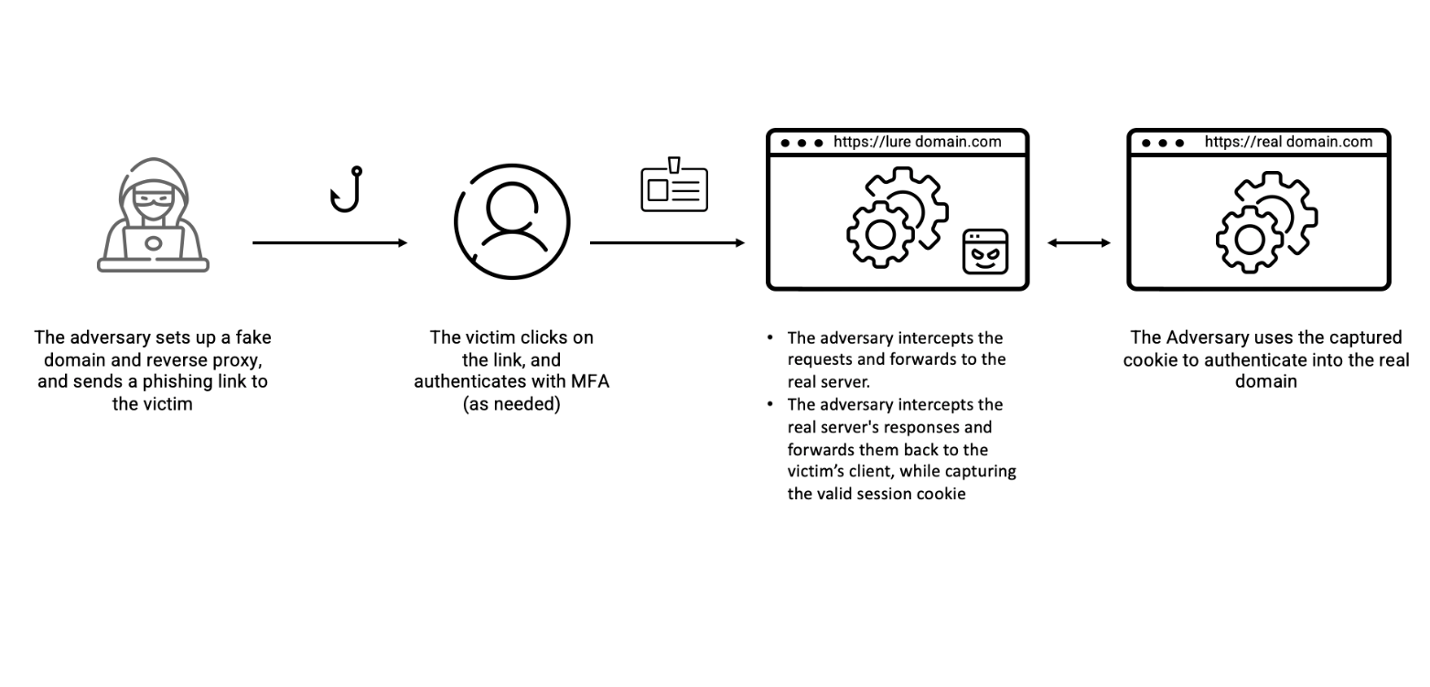
Cloud account takeover scheme utilizing EvilProxy hit over 100 top-level executives of global organizations EvilProxy was observed sending 120,000 phishing emails to over a hundred organizations to steal Microsoft 365 accounts. Proofpoint noticed a worrisome surge of successful cloud account compromises in the past five months. Most of the attacks targeted high-ranking executives. The researchers estimated […]
 Pierluigi Paganini
August 09, 2023
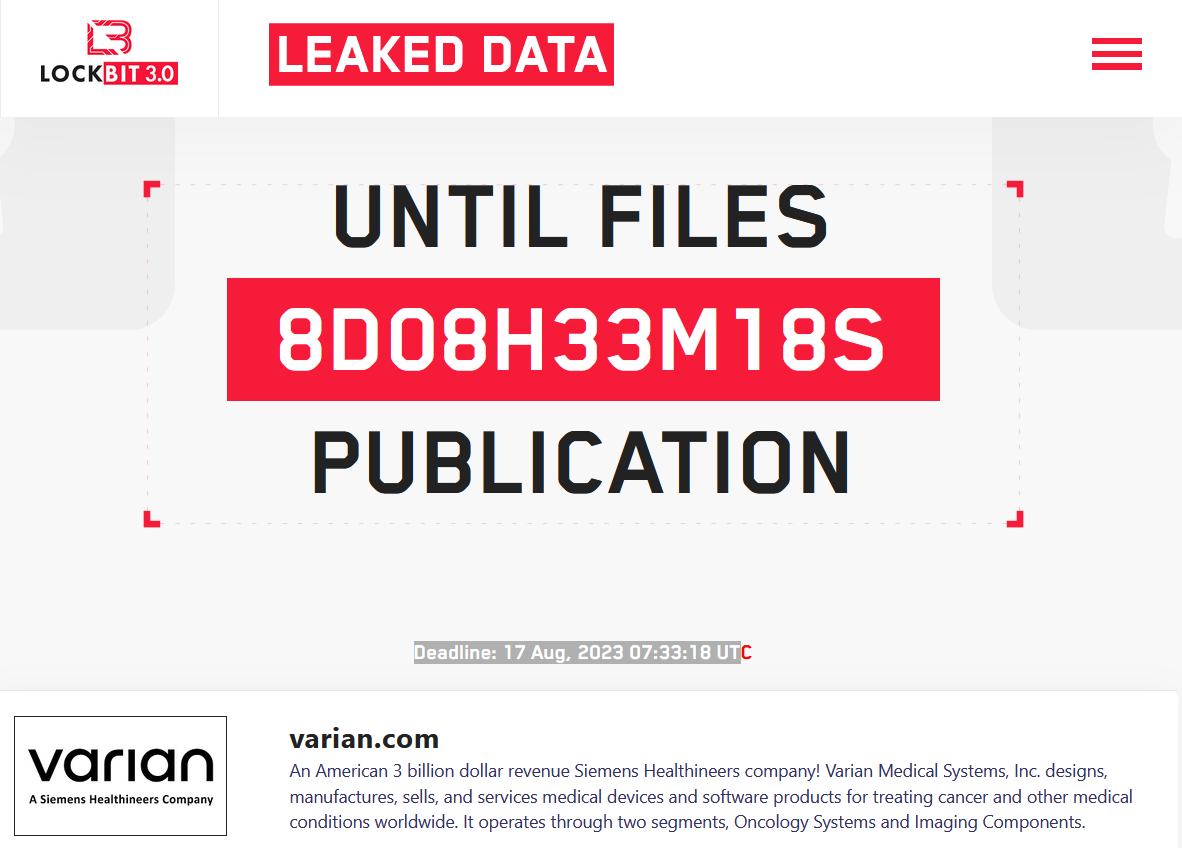
The LockBit ransomware group threatens to leak medical data of cancer patients stolen from Varian Medical Systems. The LockBit ransomware group claims to have hacked the healthcare company Varian Medical Systems and threatens to leak the medical data of cancer patients. Varian Medical Systems, Inc. designs, manufactures, sells, and services medical devices and software products […]
 Pierluigi Paganini
August 07, 2023
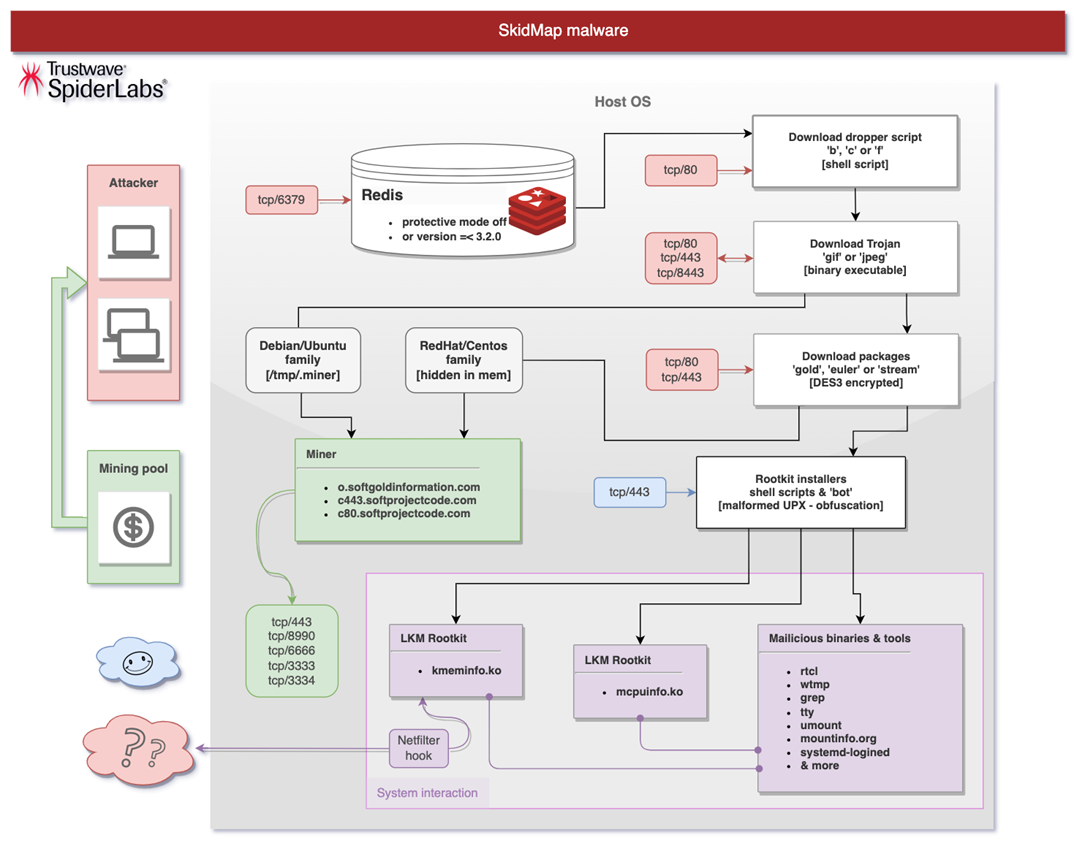
A new campaign targets Redis servers, this time the malware employed in the attacks is a new variant of the SkidMap malware. Skidmap is a piece of crypto-miner detected by Trend Micro in September 2019 while it was targeting Linux machines. The malicious code used kernel-mode rootkits to evade detection, it differs from similar miners because […]