 Pierluigi Paganini
 October 24, 2020
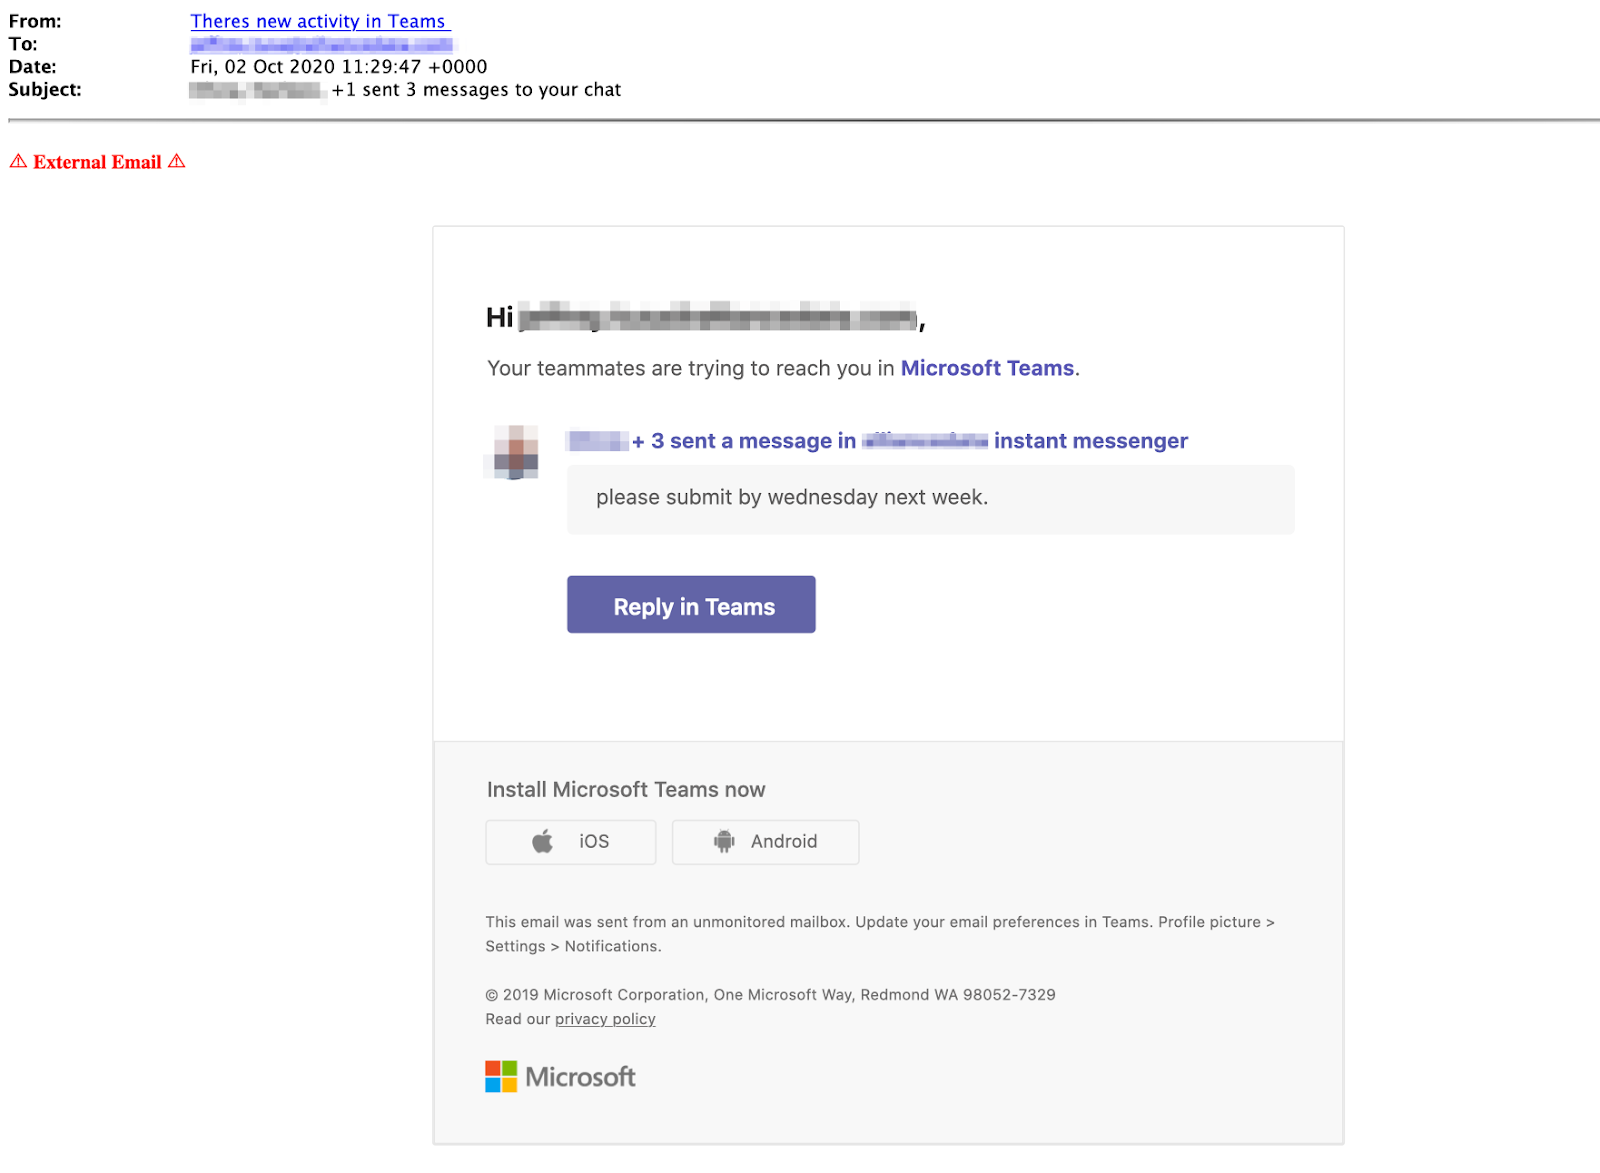
Experts warn of a phishing campaign that already targeted up to 50,000 Office 365 users with a fake automated message from Microsoft Teams. Secruity researchers reported that up to 50,000 Office 365 users have been targeted by a phishing campaign that pretends to be automated message from Microsoft Teams. The bait message uses fake notifications […]
 Pierluigi Paganini
October 24, 2020
The systems at the US-based ski and golf resort operator were infected with the WastedLocker ransomware, the incident impacted reservation systems. Boyne Resorts is a collection of mountain and lakeside resorts, ski areas, and attractions spanning from British Columbia to Maine. The company owns and operates eleven properties and an outdoor lifestyle equipment/apparel retail division […]
Pierluigi Paganini
October 23, 2020
French IT outsourcer Sopra Steria hit by ‘cyberattack’, Ryuk ransomware suspected French IT outsourcer Sopra Steria has been hit by a ransomware attack, while the company did not reveal the family of malware that infected its systems, local media speculate the involvement of the Ryuk ransomware. “A cyber attack was detected on the Sopra Steria […]
 Pierluigi Paganini
October 22, 2020
According to the ENISA Threat Landscape Report 2020, cyberattacks are becoming more sophisticated, targeted, and in many cases undetected. I’m proud to present the ENISA Threat Landscape Report 2020, the annual report published by the ENISA that provides insights on the evolution of cyber threats for the period January 2019-April 2020. The 8th annual ENISA Threat Landscape […]
 Pierluigi Paganini
October 21, 2020
Sweden is banning Chinese tech giant Huawei and ZTE from building new 5G wireless networks due to national security concerns. Another state, Sweden, announced the ban of Chinese tech companies Huawei and ZTE from building its 5G network infrastructure. The Swedish Post and Telecom Authority announced this week that four wireless carriers bidding for frequencies […]
 Pierluigi Paganini
October 21, 2020
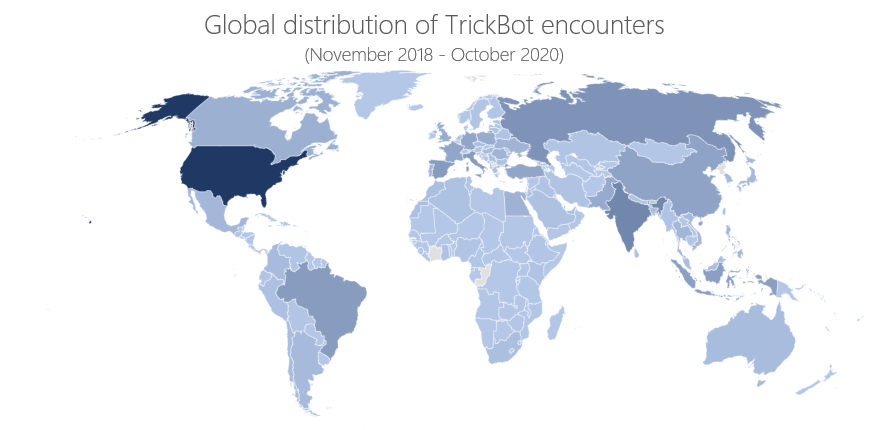
Microsoft brought down TrickBot infrastructure last week, but a few days later the botmasters set up a new command and control (C&C) servers. Microsoft’s Defender team, FS-ISAC, ESET, Lumen’s Black Lotus Labs, NTT, and Broadcom’s cyber-security division Symantec joined the forces and announced last week a coordinated effort to take down the command and control infrastructure of the infamous TrickBot botnet. Even if […]
 Pierluigi Paganini
October 20, 2020
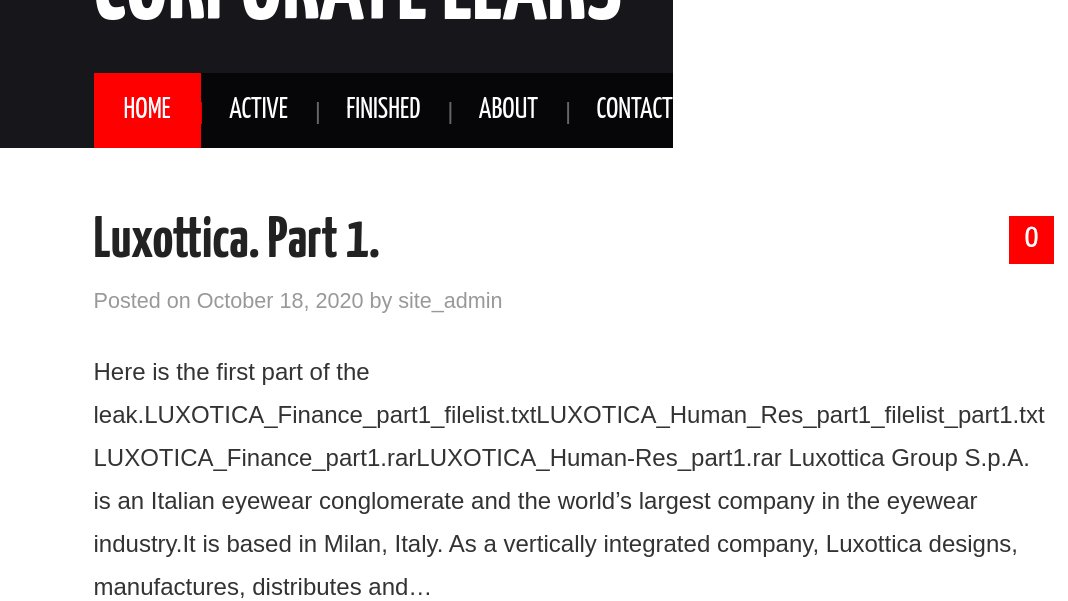
The Nefilim ransomware operators have posted a long list of files that appear to belong to Italian eyewear and eyecare giant Luxottica. Luxottica Group S.p.A. is an Italian eyewear conglomerate and the world’s largest company in the eyewear industry. As a vertically integrated company, Luxottica designs, manufactures, distributes and retails its eyewear brands, including LensCrafters, Sunglass […]
 Pierluigi Paganini
October 20, 2020
Group-IB assisted Paxful, an international peer-to-peer cryptocurrency marketplace, in countering web-bot and social engineering attacks Group-IB, a global threat hunting and intelligence company headquartered in Singapore, has assisted Paxful, an international peer-to-peer cryptocurrency marketplace, in countering a wave of web-bot and social engineering attacks, and customer account takeovers. Powered with Group-IB’s solution for online fraud prevention Secure […]
 Pierluigi Paganini
October 19, 2020
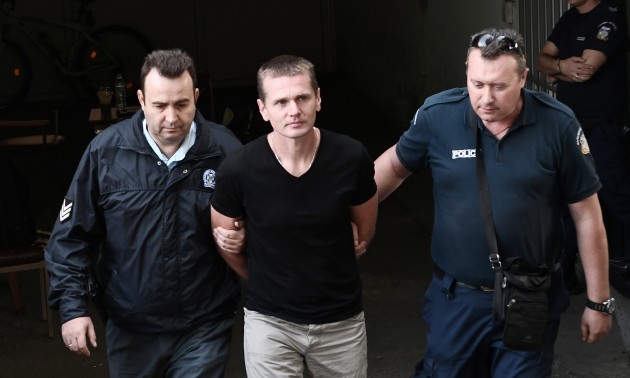
The Russian citizen Alexander Vinnik goes on trial in Paris for having defrauded nearly 200 victims across the world of 135 million euros using ransomware. The Russian man Alexander Vinnik goes on trial in Paris for having defrauded nearly 200 victims across the world of 135M euros using ransomware. Alexander Vinnik allegedly headed the Bitcoin exchange BTC-e, he is charged […]
 Pierluigi Paganini
October 19, 2020
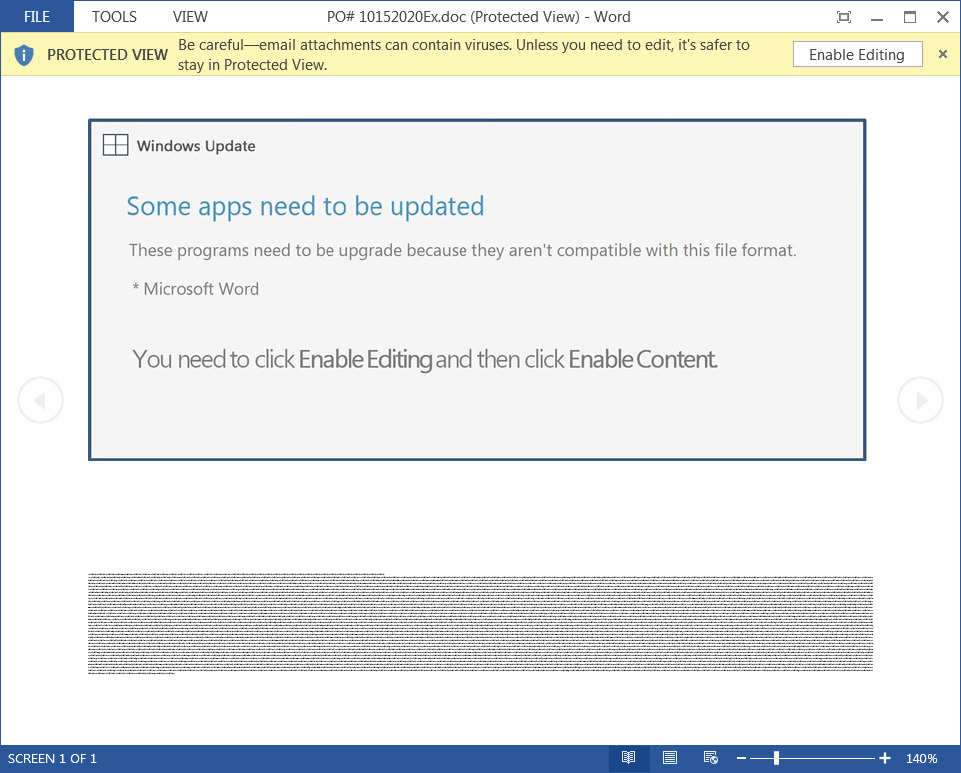
After a short pause, a new Emotet malware campaign was spotted by the experts on October 14th, crooks began using a new ‘Windows Update’ attachment. After a short interruption, a new Emotet malware campaign was spotted by the experts in October. Threat actors began using new Windows Update attachments in a spam campaign aimed at […]
Uncategorized / September 22, 2026
Malware / September 21, 2026