


 Pierluigi Paganini
 August 25, 2026
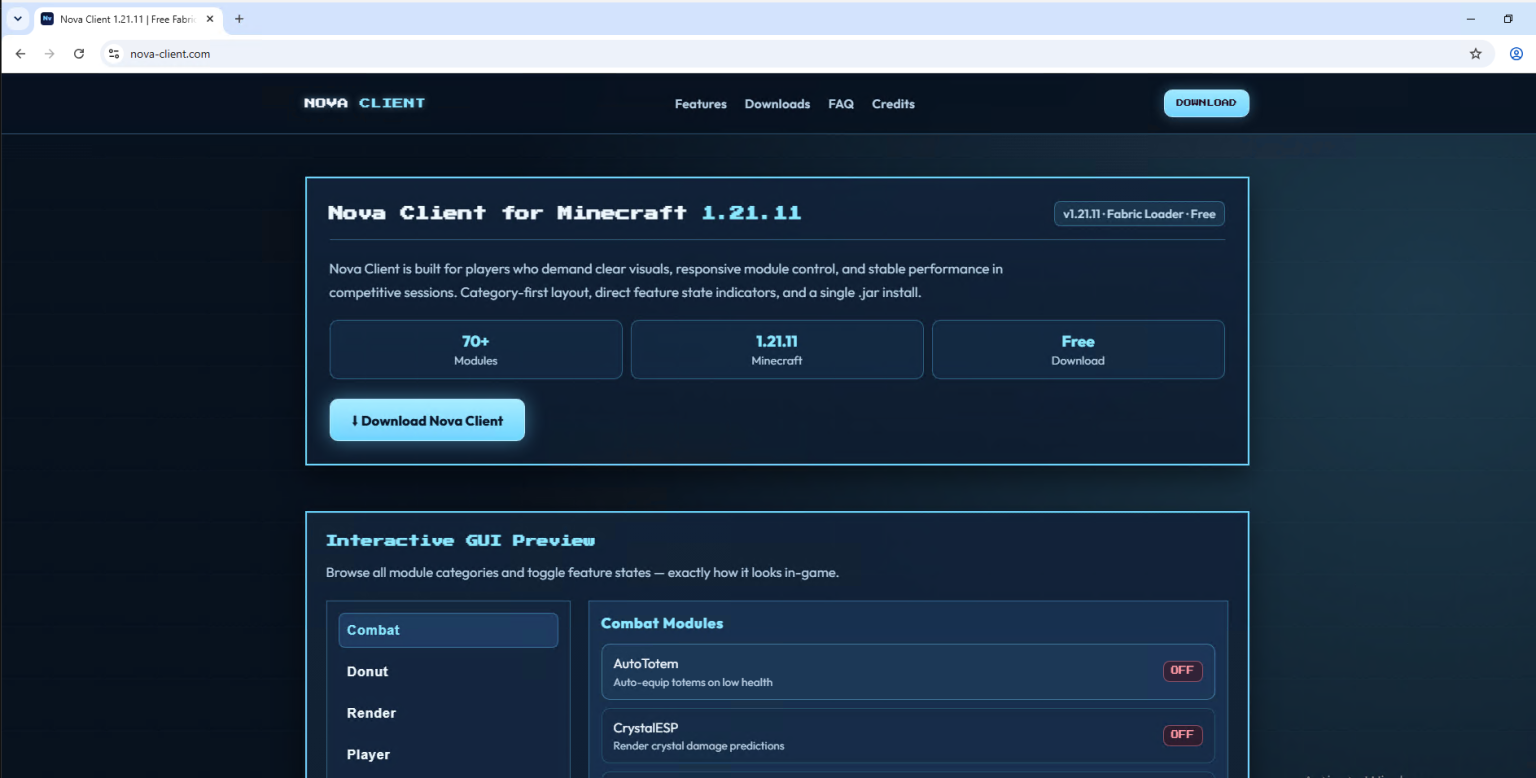
WeedHack Minecraft Malware Survives C2 Takedown: Fake Client Sites Still Active, SEO Poisoning Puts Malicious Downloads at the Top of Google McAfee Labs published a follow-up report on the WeedHack Malware-as-a-Service campaign this week, documenting ten active malicious sites and multiple file-hosting accounts that are still spreading the infostealer despite a disruption to its command-and-control […]
 Pierluigi Paganini
August 24, 2026
A fake 113GB GTA VI build is packed with malware, using massive empty files to hide a tiny malicious payload. GTA VI hype has reached the point where people are volunteering to infect their own computers just to check if a leak is real. Someone on X asked their followers to “take one for the […]
 Pierluigi Paganini
August 24, 2026
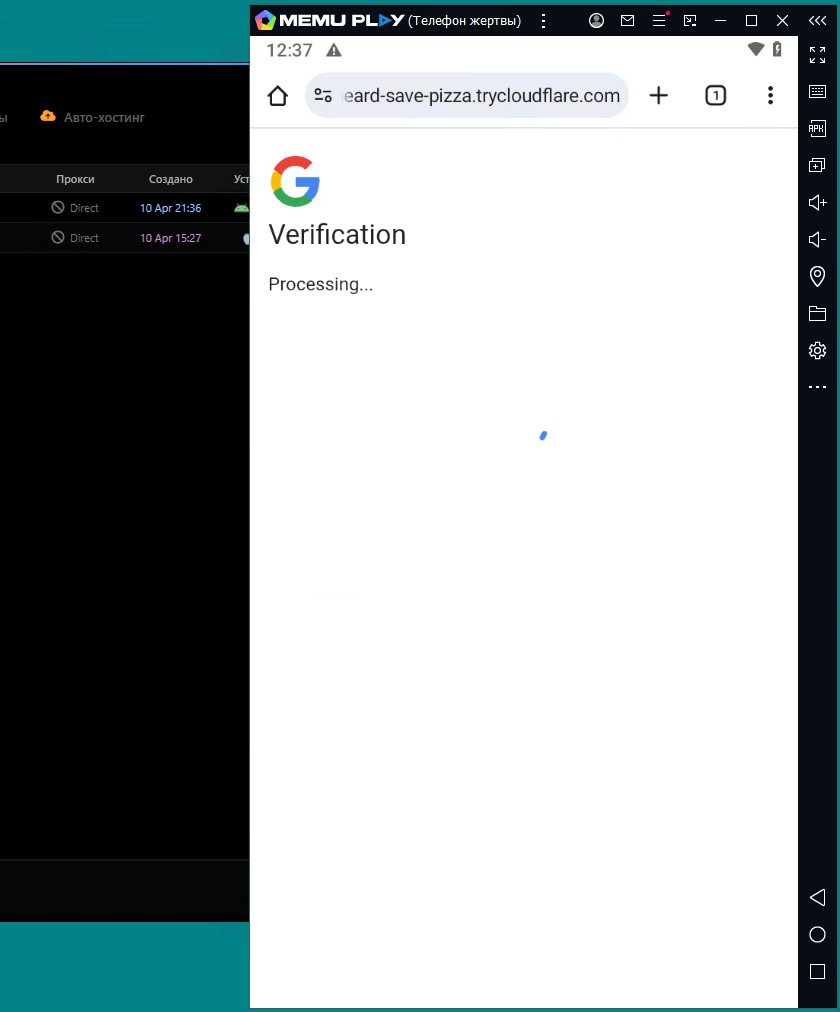
iAuthFlow v2 phishing toolkit uses a phished Google session to enroll an attacker-controlled passkey that survives password resets. Abnormal Security researchers have published an analysis of iAuthFlow v2, a phishing toolkit sold on a Russian-language cybercrime forum for $10,000 base price. The author also offers for sale additional capability modules separately. The headline feature is […]
 Pierluigi Paganini
August 22, 2026
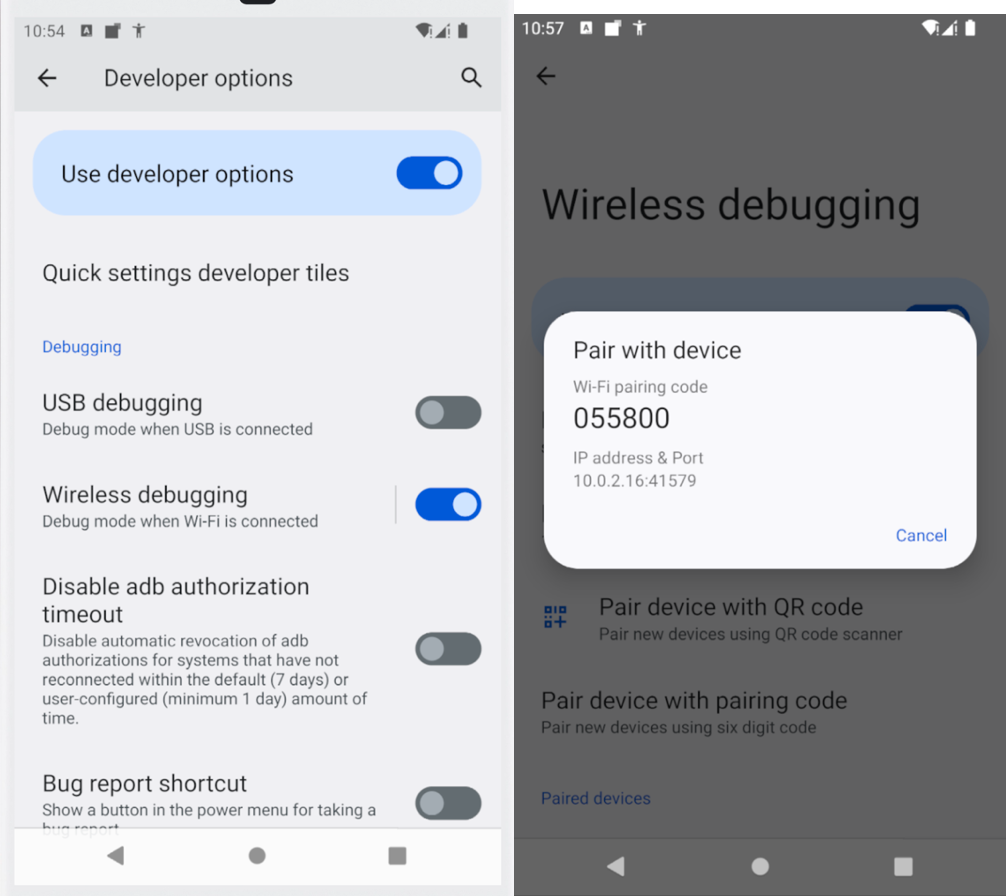
ToxicPanda 2.0 targets 349 financial apps and abuses Android Wireless Debugging to gain deeper device access and steal banking credentials. ToxicPanda used to be a Europe-focused nuisance targeting a manageable list of banks. That version is gone. Zimperium’s zLabs team just documented ToxicPanda 2.0, and the numbers alone tell the story: 349 targeted financial institutions […]
 Pierluigi Paganini
August 21, 2026
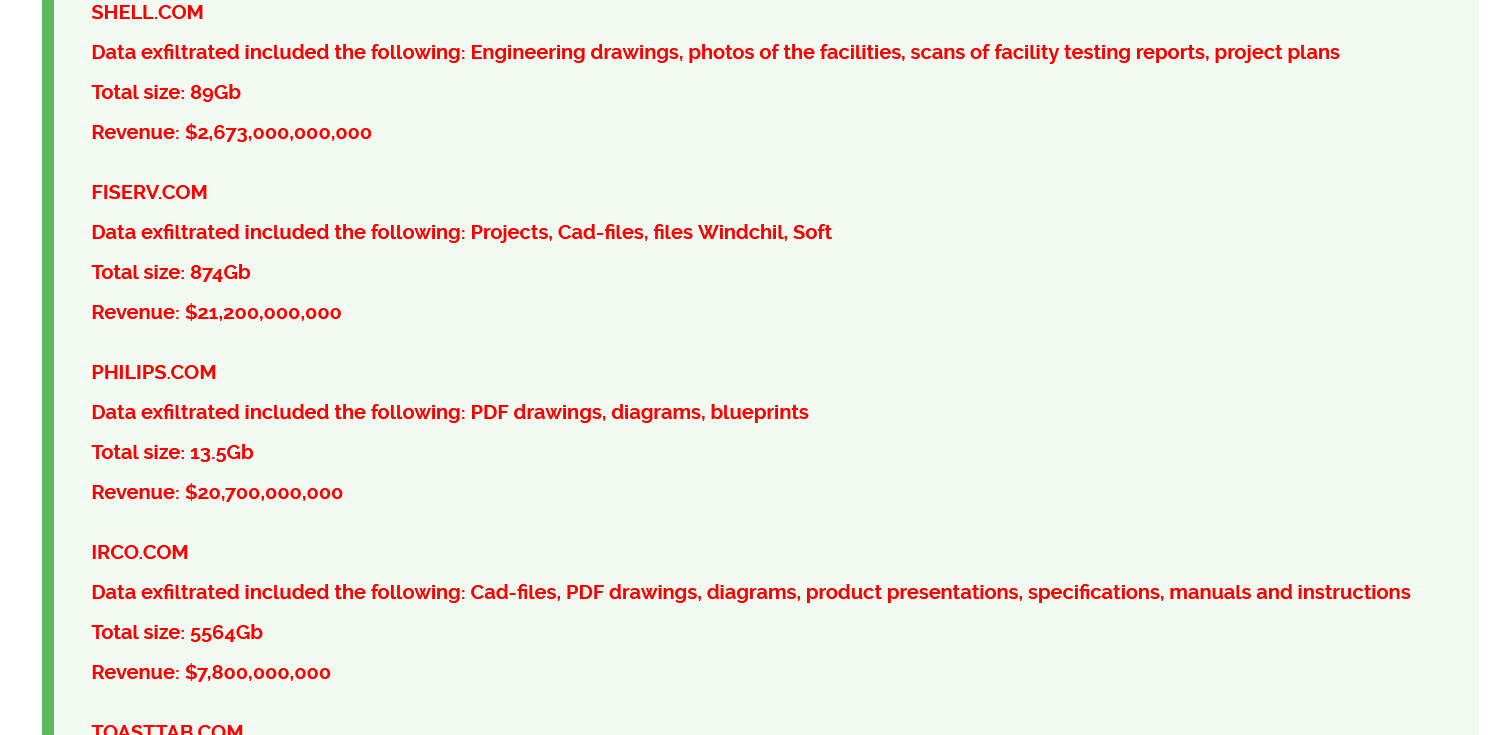
Cl0p claims over 40 organizations fell victim to attacks exploiting a PTC Windchill and FlexPLM vulnerability. Cl0p is using a familiar strategy again: exploit one flaw in enterprise software to attack many companies, then publish the victims’ names if they refuse to pay. The group claims it has targeted more than 40 organizations through a […]
 Pierluigi Paganini
August 20, 2026
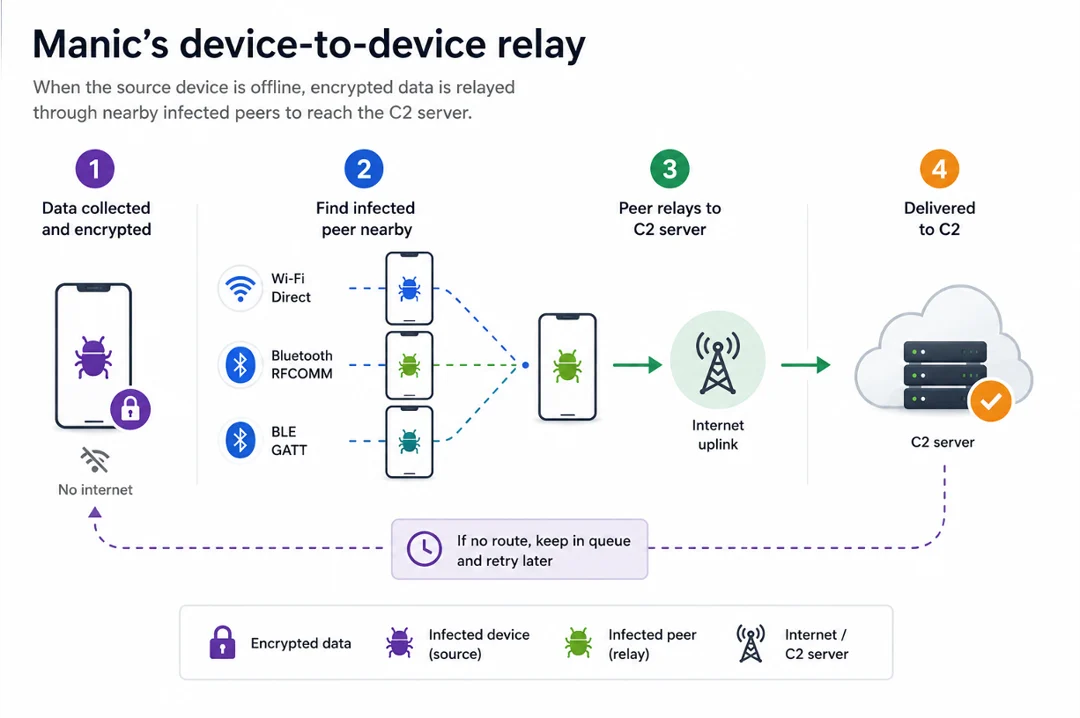
Manic Android malware combines banking fraud and spyware, using a Bluetooth relay to steal data even when devices are offline. ThreatFabric’s Mobile Threat Intelligence team has identified a new Android malware, dubbed Manic, which has been active in the wild since at least February 2026. The researchers state that the malware is still under development […]
 Pierluigi Paganini
August 20, 2026
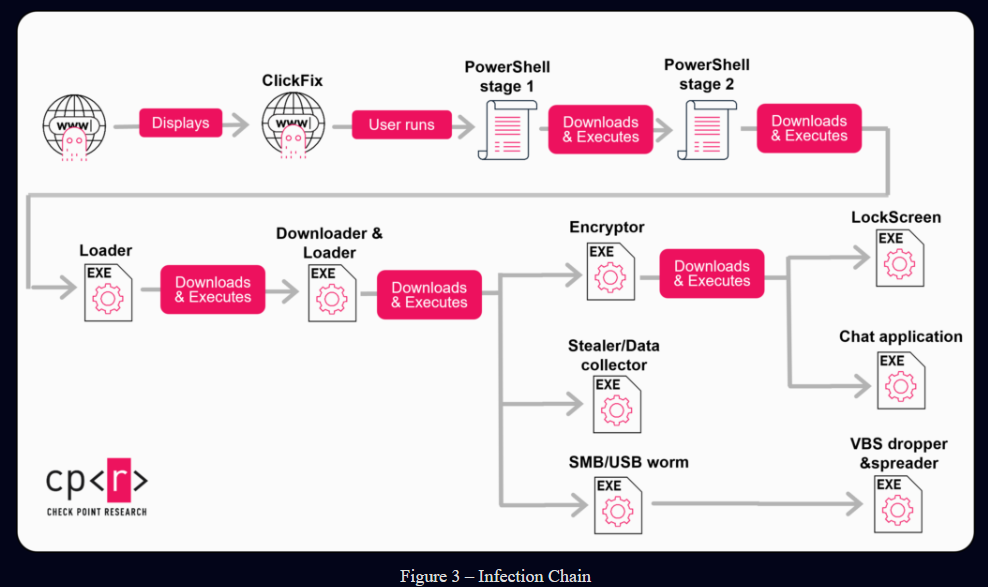
StopAndProtect turned nearly 2,000 hacked WordPress sites into a criminal network for malware delivery, data theft, surveillance and ransomware. Check Point Research uncovered a cybercrime operation, dubbed StopAndProtect, that has turned thousands of hacked WordPress websites into a shared platform for malware delivery, data theft, surveillance and ransomware. The operation is a good reminder that […]
 Pierluigi Paganini
August 19, 2026
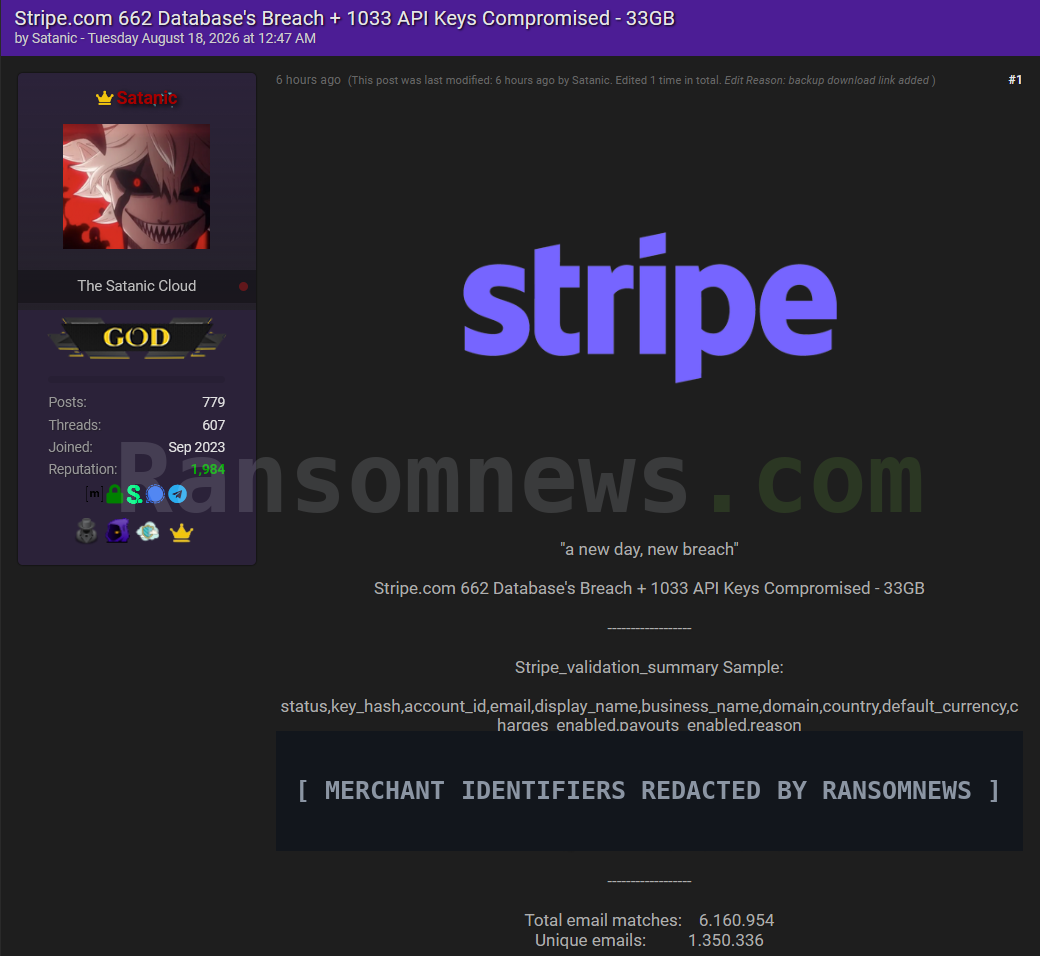
Over 50,000 exposed Stripe API keys show how leaked secrets can enable fraud, data access and account abuse within hours. Ransomnews researchers have documented a large-scale leak of Stripe merchant API keys found exposed in public code repositories, GitHub Actions logs, and misconfigured web servers, with over 50,000 unique keys identified in total. The research […]
 Pierluigi Paganini
August 18, 2026
A Heights Finance breach exposed personal and financial data of over 1.2 million people after hackers compromised a third-party cloud platform. Heights Finance is a U.S. consumer finance company that provides personal loans and related lending services, mainly to customers who may have limited access to traditional bank credit. It is part of Heights Finance […]
 Pierluigi Paganini
August 18, 2026
Evooo1Bot is a Mirai-based Linux botnet that hijacks routers and IoT devices for DDoS attacks, credential theft and criminal proxy services. Fortinet’s FortiGuard Labs disclosed Evooo1Bot in mid-August, a previously undocumented Linux botnet that’s been active since July 2026. The bot borrows Mirai‘s DDoS engine but adds encrypted command-and-control communications, an SSH brute-force scanner, a […]





