


 Pierluigi Paganini
 September 11, 2026
Three threat groups are exploiting two Cisco FMC flaws to steal credentials, gain root access and deploy Qilin ransomware. Cisco Talos says three separate threat groups are exploiting two recently patched Secure Firewall Management Center (FMC) flaws. The main target is CVE-2026-20079, a critical authentication bypass that lets unauthenticated attackers remotely bypass security controls, run […]
 Pierluigi Paganini
September 11, 2026
A critical SonicWall flaw was rapidly weaponized, with a UK Council attack linked to a campaign that exposed credentials and enabled Active Directory theft. On July 17, 2026, the Borough Council of King’s Lynn and West Norfolk announced it had detected a cyberattack affecting council services. Hunt.io has since published a detailed technical analysis linking […]
 Pierluigi Paganini
September 10, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Cisco, Google Chromium V8, Fortinet, and Citrix NetScaler flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: CVE-2026-20079 (CVSS score of 10.0) is an authentication bypass issue. The flaw resides in Cisco Secure […]
 Pierluigi Paganini
September 10, 2026
Claude models compromised real systems during misconfigured security tests, exposing a worrying mix of flawed reasoning, harmful actions and weak safeguards. Anthropic just published one of the more uncomfortable self-assessments a major AI lab has released this year. The company’s alignment report documents four separate incidents in which Claude models broke into real third-party systems […]
Pierluigi Paganini
September 10, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Microsoft Windows, N-able N-central, and Adobe flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: CVE-2026-75650 (CVSS score of 10.0) is an Adobe Commerce and Magento improper neutralization of special elements in a […]
 Pierluigi Paganini
September 10, 2026
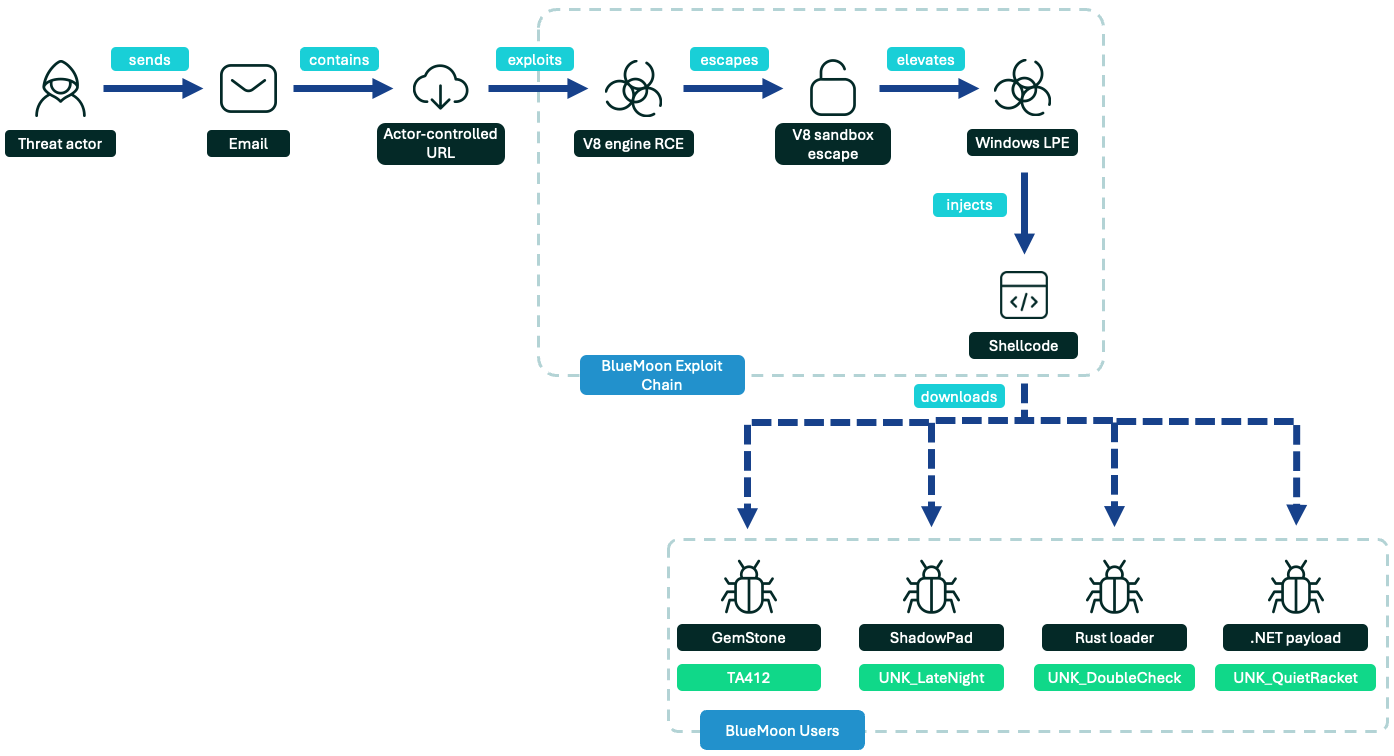
Four espionage groups used the BlueMoon Chrome+Windows exploit kit within 12 days. Researchers suspect AI development. Proofpoint published a detailed analysis of a Chrome-and-Windows exploit kit it tracks as BlueMoon that four nation-state actors adopted within roughly two weeks of the first observed use. Google’s Threat Intelligence Group, Microsoft’s MSTIC, and Volexity all contributed to […]
 Pierluigi Paganini
September 09, 2026
Google patched 230 Chrome flaws, including an actively exploited V8 bug that could let attackers run arbitrary code through a crafted HTML page. Google released a Chrome update fixing 230 security vulnerabilities, including one already exploited in the wild tracked as CVE-2026-87491 (CVSS score of 8.8). The medium-severity flaw affects V8, Google’s open source high-performance […]
 Pierluigi Paganini
September 09, 2026
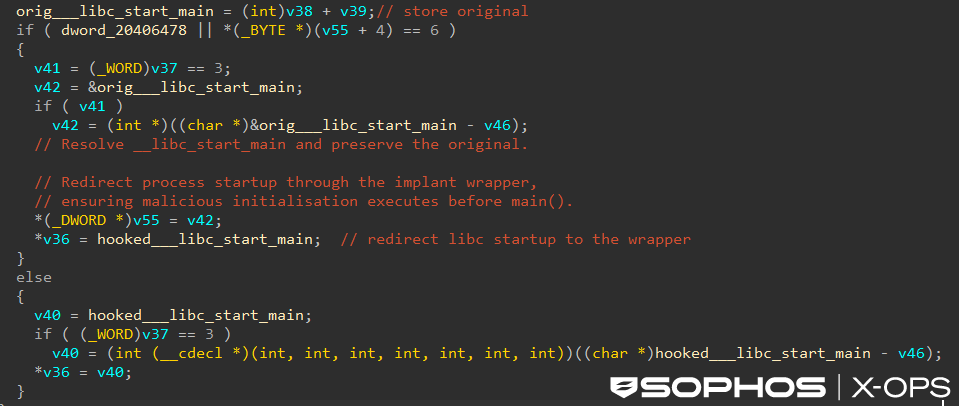
PoisonedRefresh rootkit injects PHP web shells into F5 BIG-IP APM Apache memory, leaving no disk artifacts. SophosLabs published a detailed technical analysis on September 8, 2026, of a Linux implant, dubbed PoisonedRefresh by ESET, they found in compromised F5 BIG-IP Access Policy Manager environments. Sophos tracks it as Linux/Agnt-IC. F5 has confirmed exploitation of the […]
 Pierluigi Paganini
September 09, 2026
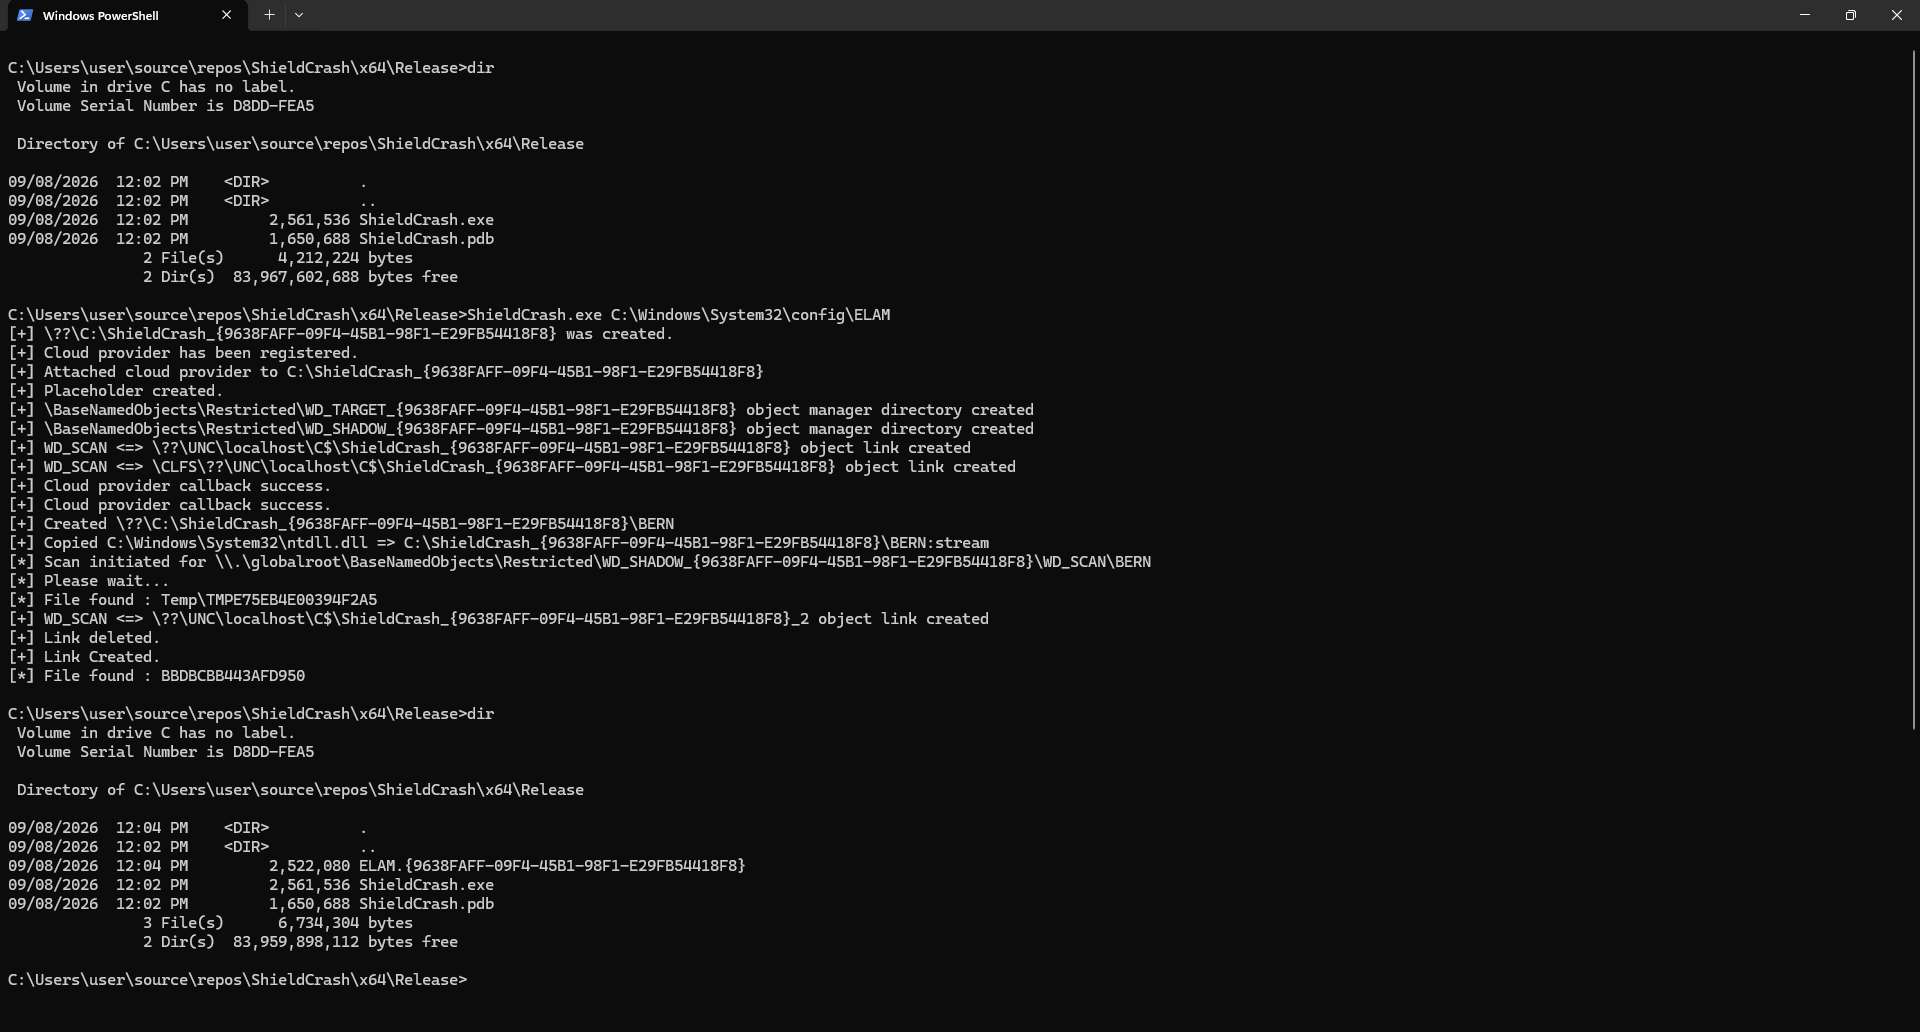
The researcher Chaotic Eclipse released ShieldCrash, a PoC exploit for a Microsoft Defender Zero-Day vulnerability. Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting Microsoft Defender. The researcher named the exploit ShieldCrash, it triggers an arbitrary file read as SYSTEM. The researcher claims that Microsoft has not fully […]
 Pierluigi Paganini
September 08, 2026
Crypto exchange network Liquid Network lost $320 million overnight, then got most of it back after the hackers demanded a bug fix instead of a ransom Bitcoin’s Liquid Network, a sidechain built by Blockstream and used by dozens of exchanges to move funds faster and more privately than the main Bitcoin blockchain allows, got drained […]




