 Pierluigi Paganini
 November 09, 2022
Google Project Zero researchers reported that a surveillance vendor is using three Samsung phone zero-day exploits. Google Project Zero disclosed three Samsung phone vulnerabilities, tracked as CVE-2021-25337, CVE-2021-25369 and CVE-2021-25370, that have been exploited by a surveillance company. The three issues are: The researchers pointed out that the surveillance firm included in its spyware the […]
 Pierluigi Paganini
November 09, 2022
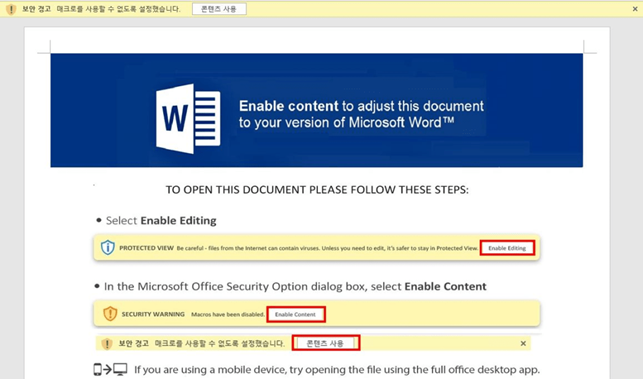
Experts noticed that the Amadey malware is being used to deploy LockBit 3.0 ransomware on compromised systems. Researchers from AhnLab Security Emergency Response Center (ASEC) reported that the Amadey malware is being used to deploy LockBit 3.0 ransomware on compromised systems, researchers have warned. Amadey Bot is a data-stealing malware that was first spotted in 2018, it also allows […]
 Pierluigi Paganini
November 08, 2022
The U.S. Department of Justice condemned James Zhong, a hacker who stole 50,000 bitcoins from the Silk Road dark net marketplace. The US Department of Justice announced that a man from Georgia, James Zhong, has pleaded guilty to wire fraud after stealing more than 50,000 bitcoins from the Silk Road. Zhong pled guilty to money […]
 Pierluigi Paganini
November 07, 2022
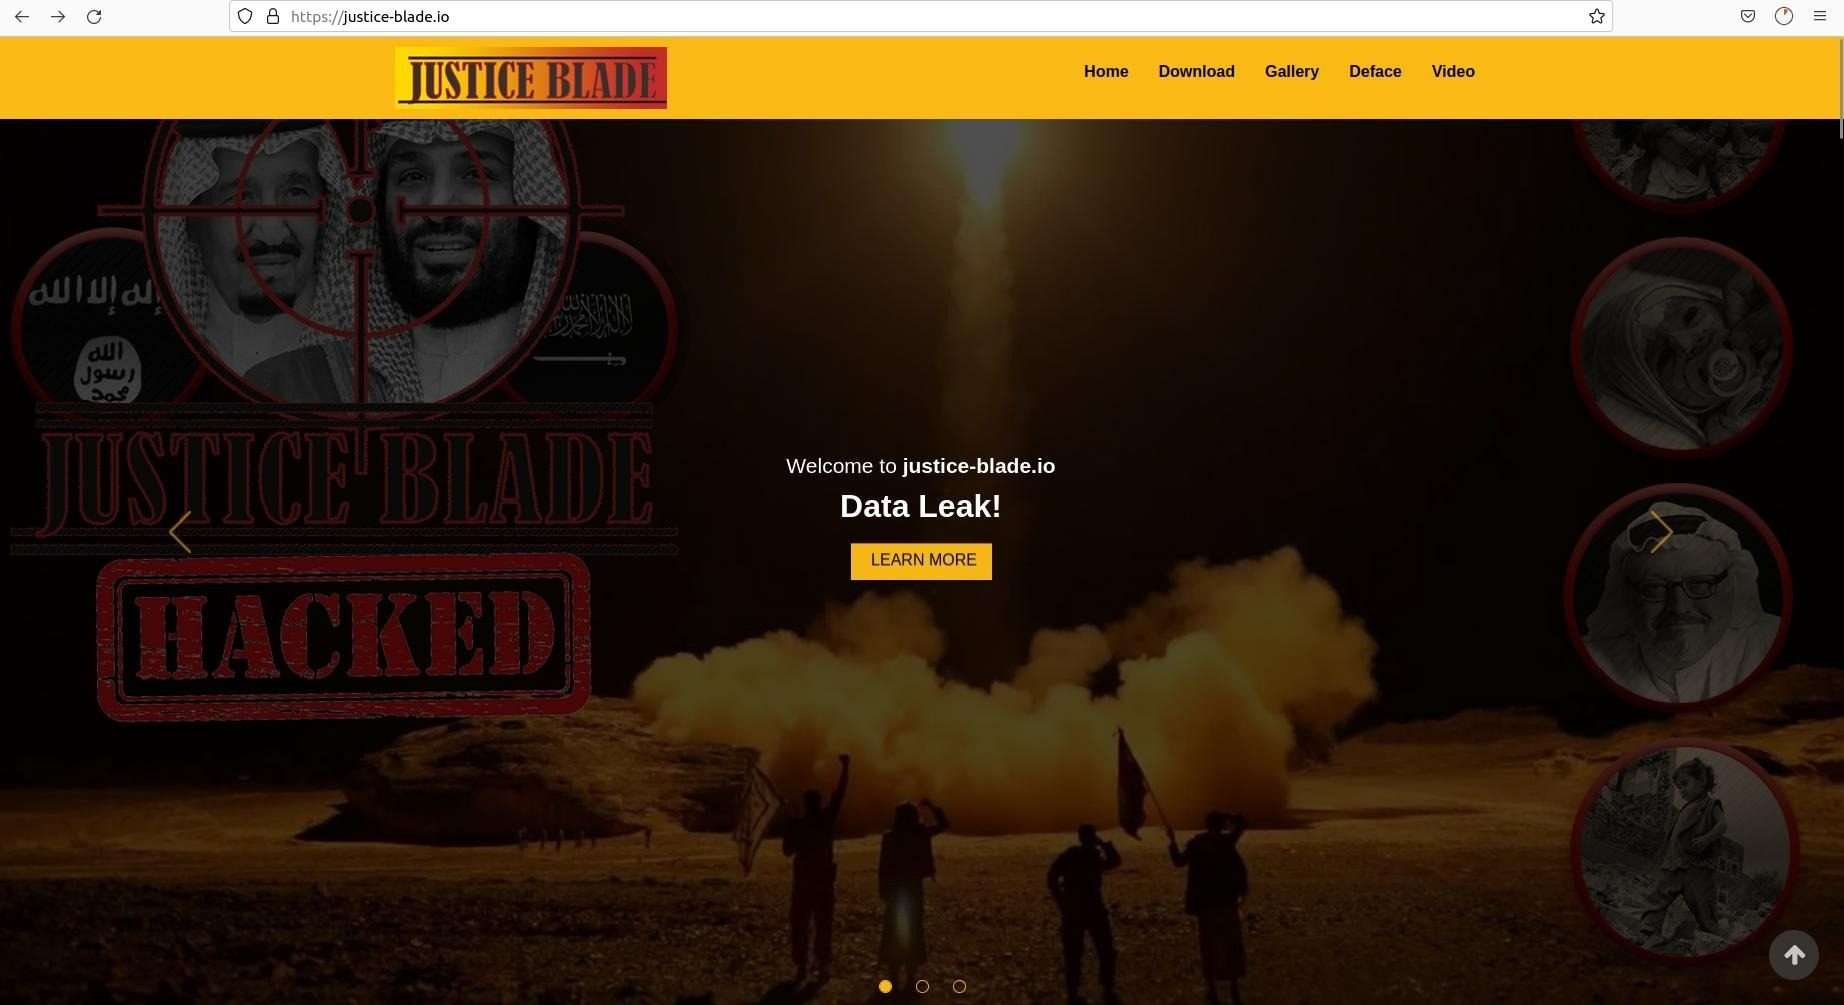
Threats actors calling themselves “Justice Blade” published leaked data from an outsourcing IT vendor. The group of threat actors calling themselves ‘Justice Blade’ published leaked data from Smart Link BPO Solutions, an outsourcing IT vendor working with major enterprises and government agencies in the Kingdom of Saudi Arabia and other countries in the GCC. The […]
 Pierluigi Paganini
November 07, 2022
The phishing-as-a-service (PhaaS) platform Robin Banks migrated its infrastructure to DDoS-Guard, a Russian bulletproof hosting service. The phishing-as-a-service (PhaaS) platform Robin Banks was originally hosted by Cloudflare provider, but the company in July disassociated Robin Banks phishing infrastructure from its services after being informed. The move caused a multi-day disruption to PhaaS operations, then the administrators […]
 Pierluigi Paganini
November 07, 2022
Expert warns that the US and Israel are still unprepared to defeat a cyber attack against organizations in the water sector. Ariel Stern, a former Israeli Air Force captain, warns that the US and Israel are still unprepared to defeat a cyber attack against the water sector that could be orchestrated by enemy states like […]
 Pierluigi Paganini
November 07, 2022
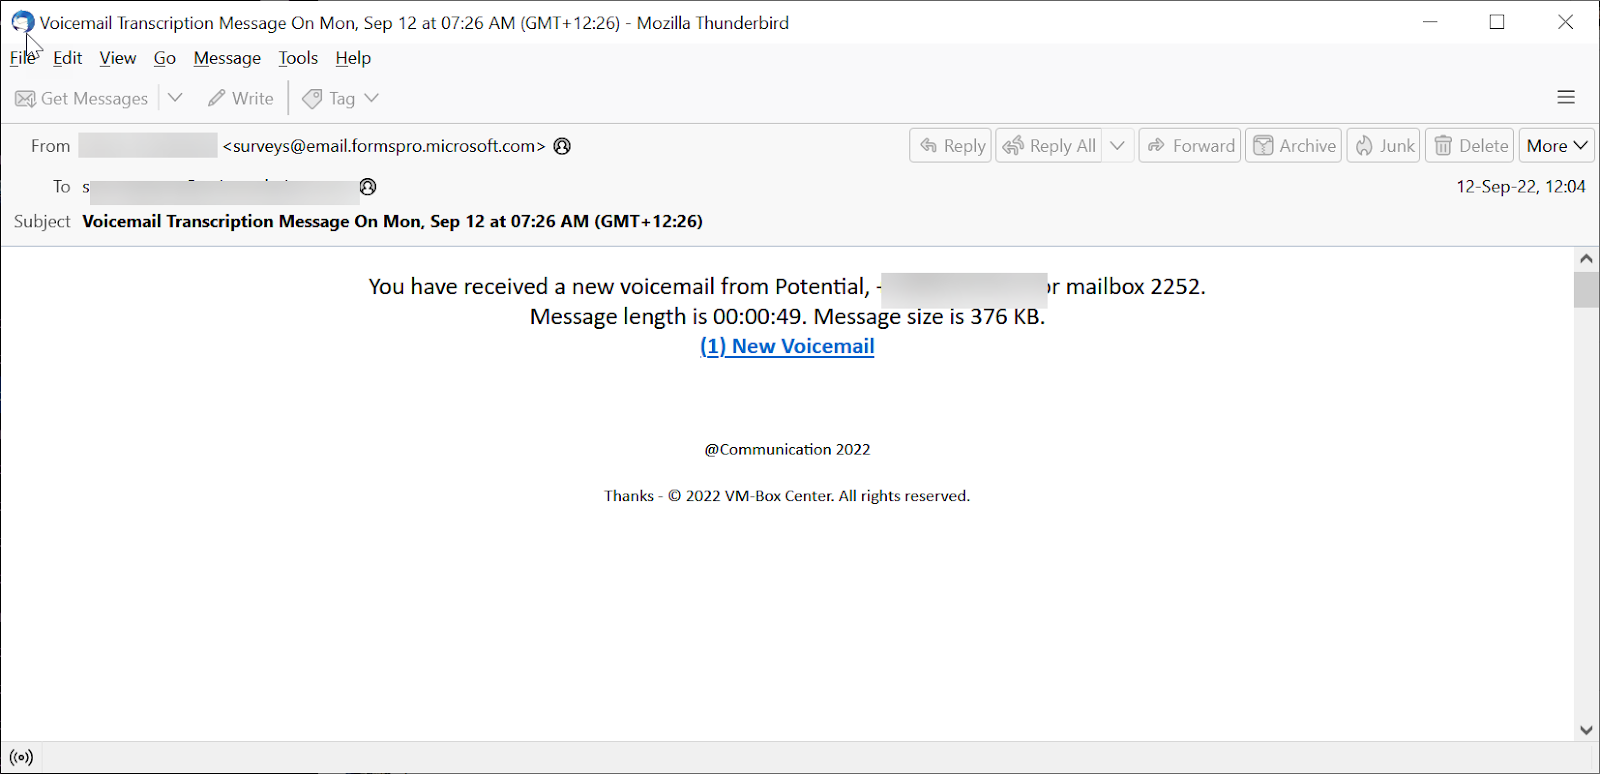
Researchers uncovered a campaign abusing Microsoft Dynamics 365 customer voice to steal credentials from the victims. Microsoft’s Dynamics 365 Customer Voice product allows organizations to gain customer feedback, it is used to conduct customer satisfaction surveys. Researchers from cybersecurity firm Avanan, uncovered a campaign abusing Microsoft Dynamics 365 customer voice to steal credentials from the […]
 Pierluigi Paganini
November 06, 2022
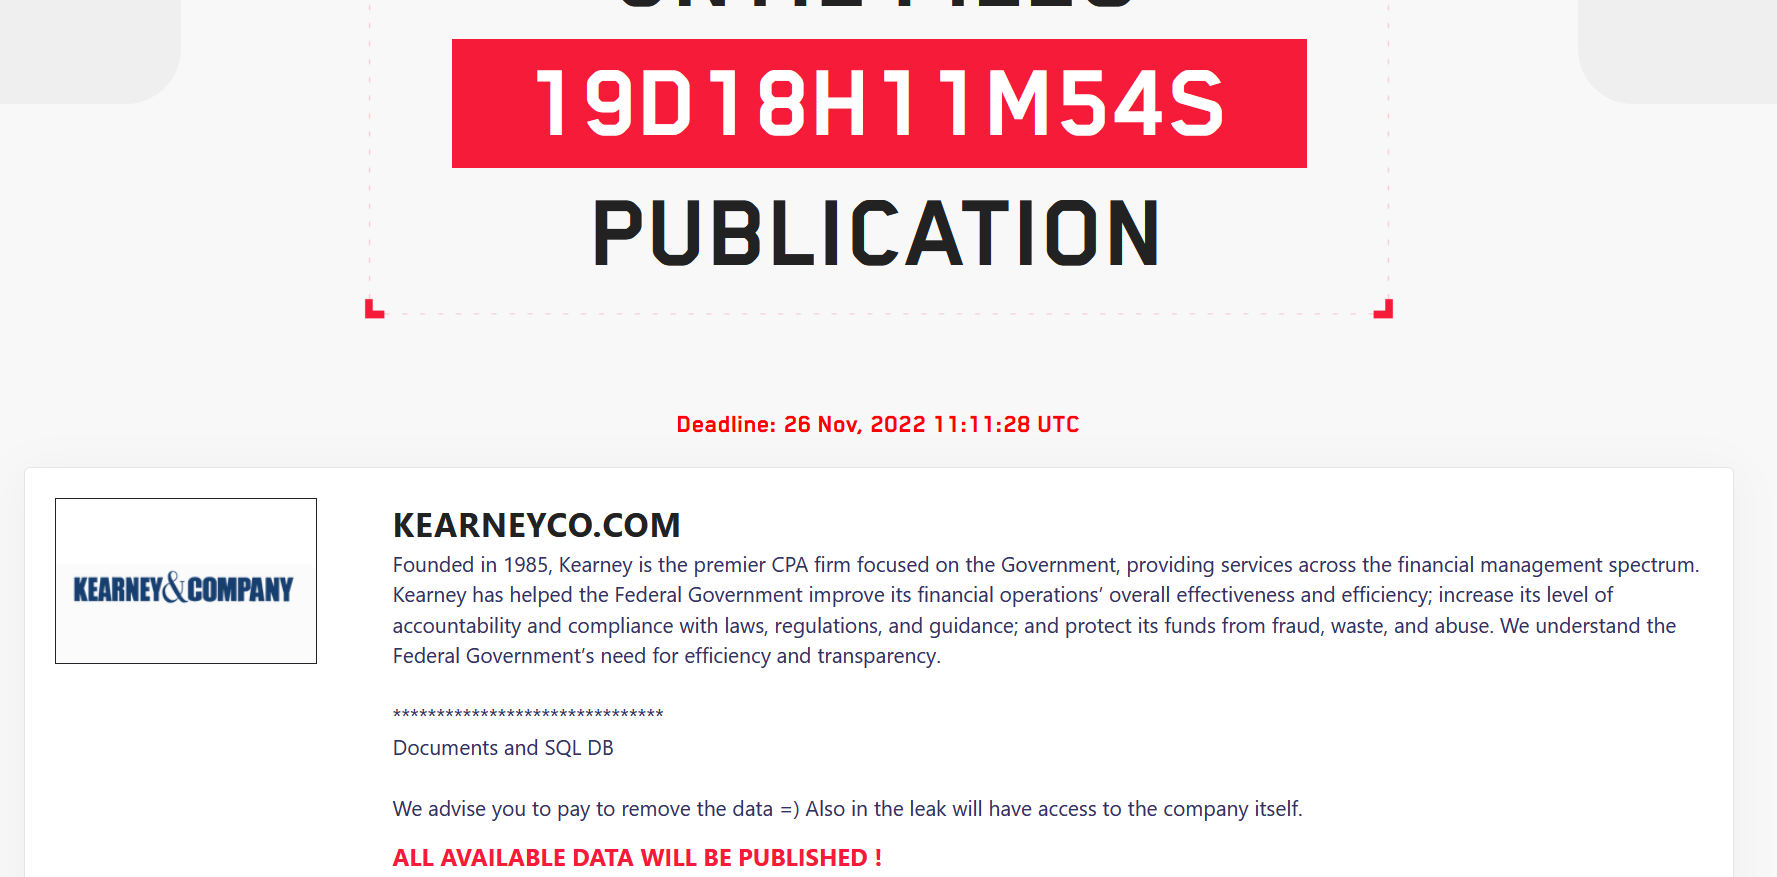
The ransomware group LockBit claimed to have stolen data from consulting and IT services provider Kearney & Company. Kearney is the premier CPA firm that services across the financial management spectrum to government entities. The company provides audit, consulting and IT services to the United States government. It has helped the Federal Government improve its […]
 Pierluigi Paganini
November 06, 2022
At the end of October, a cyberattack caused trains in Denmark to stop; it hit a third-party IT service provider. A cyber attack caused the trains operated by DSB to stop in Denmark during the last weekend; threat actors hit a third-party IT service provider. The attack hit the Danish company Supeo, which provides enterprise […]
 Pierluigi Paganini
November 05, 2022
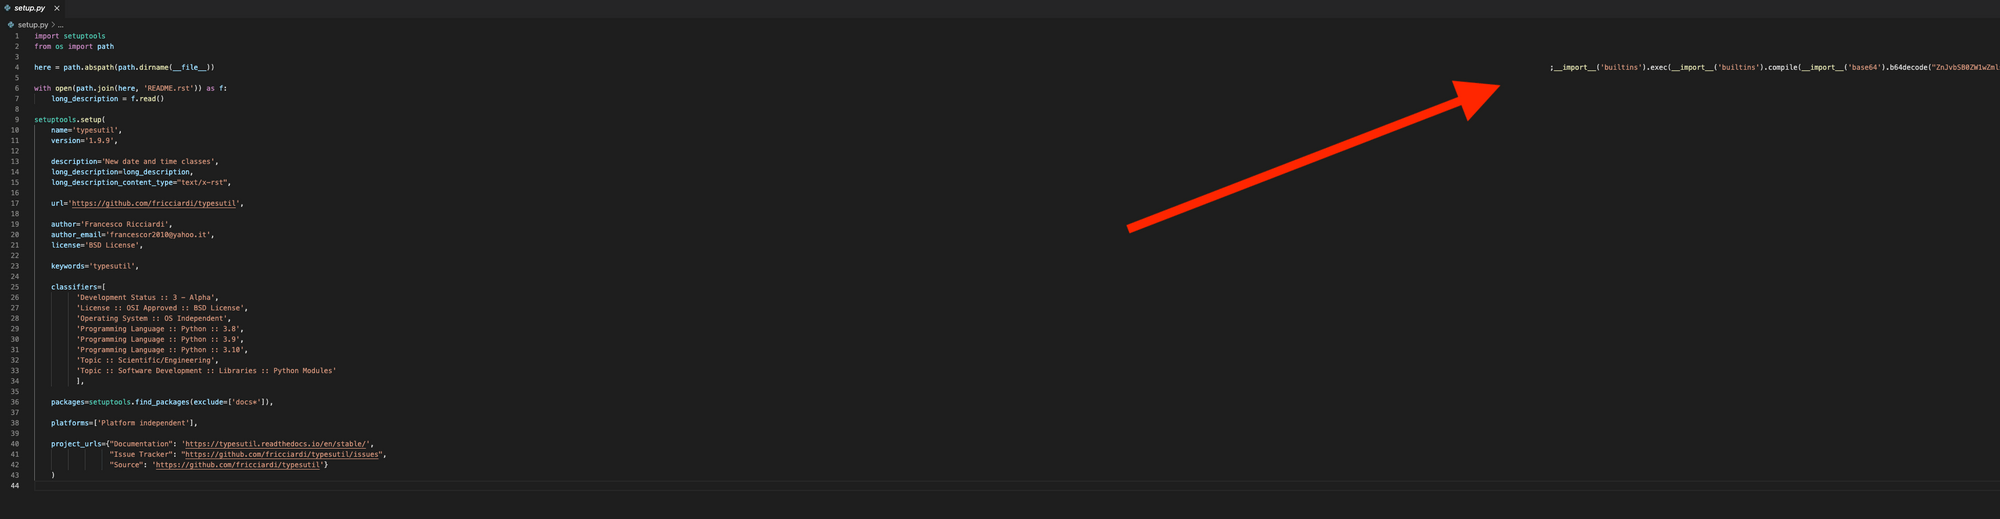
Cybersecurity researchers discovered 29 malicious PyPI packages delivering the W4SP stealer to developers’ systems. Cybersecurity researchers have discovered 29 packages in the official Python Package Index (PyPI) repository designed to infect developers’ systems with an info-stealing malware dubbed W4SP Stealer. “It appears that these packages are a more sophisticated attempt to deliver the W4SP Stealer on […]